






Cybercriminals are using fake artificial intelligence (AI) tools to target software developers in a coordinated supply chain attack on the JetBrains Marketplace. The compromise was first discovered by the Code security firm Aikido Security, which found 15 published plugins designed as AI coding assistants built on large language models (LLMs) like DeepSeek.
The first fake plugins came out at the end of October 2025, and new ones dropped as recently as June 2026. Scammers used seven different seller accounts to publish them. Collectively, people downloaded these malicious plugins nearly 70,000 times. Some of the most downloaded plugins are called CodeGPT AI Assistant and DeepSeek AI Assist. The hackers also added fake five-star reviews to make the tools look safe.
Like similar campaigns, this one’s modus operandi includes installing extensions and exfiltrating the user’s private AI authentication credentials to a static, hard-coded server controlled by attackers.
The malicious code was structured into otherwise fully functional software offering genuine features like code reviews, automated git commit messages, and unit tests. The infiltration is designed so that it seems like a routine setup process where developers paste an OpenAI, SiliconFlow, or DeepSeek API key into the settings interface.
According to researchers, the software hooks into the save function of the Integrated Development Environments (IDEs), which are the main software applications where developers write code. The exact moment a user applies their changes, the extension transmits the authentication data in plaintext over an unencrypted HTTP connection later sent to the attackers’ C2 server. This transmission happens silently in the background with no permission prompts or visual indicators.
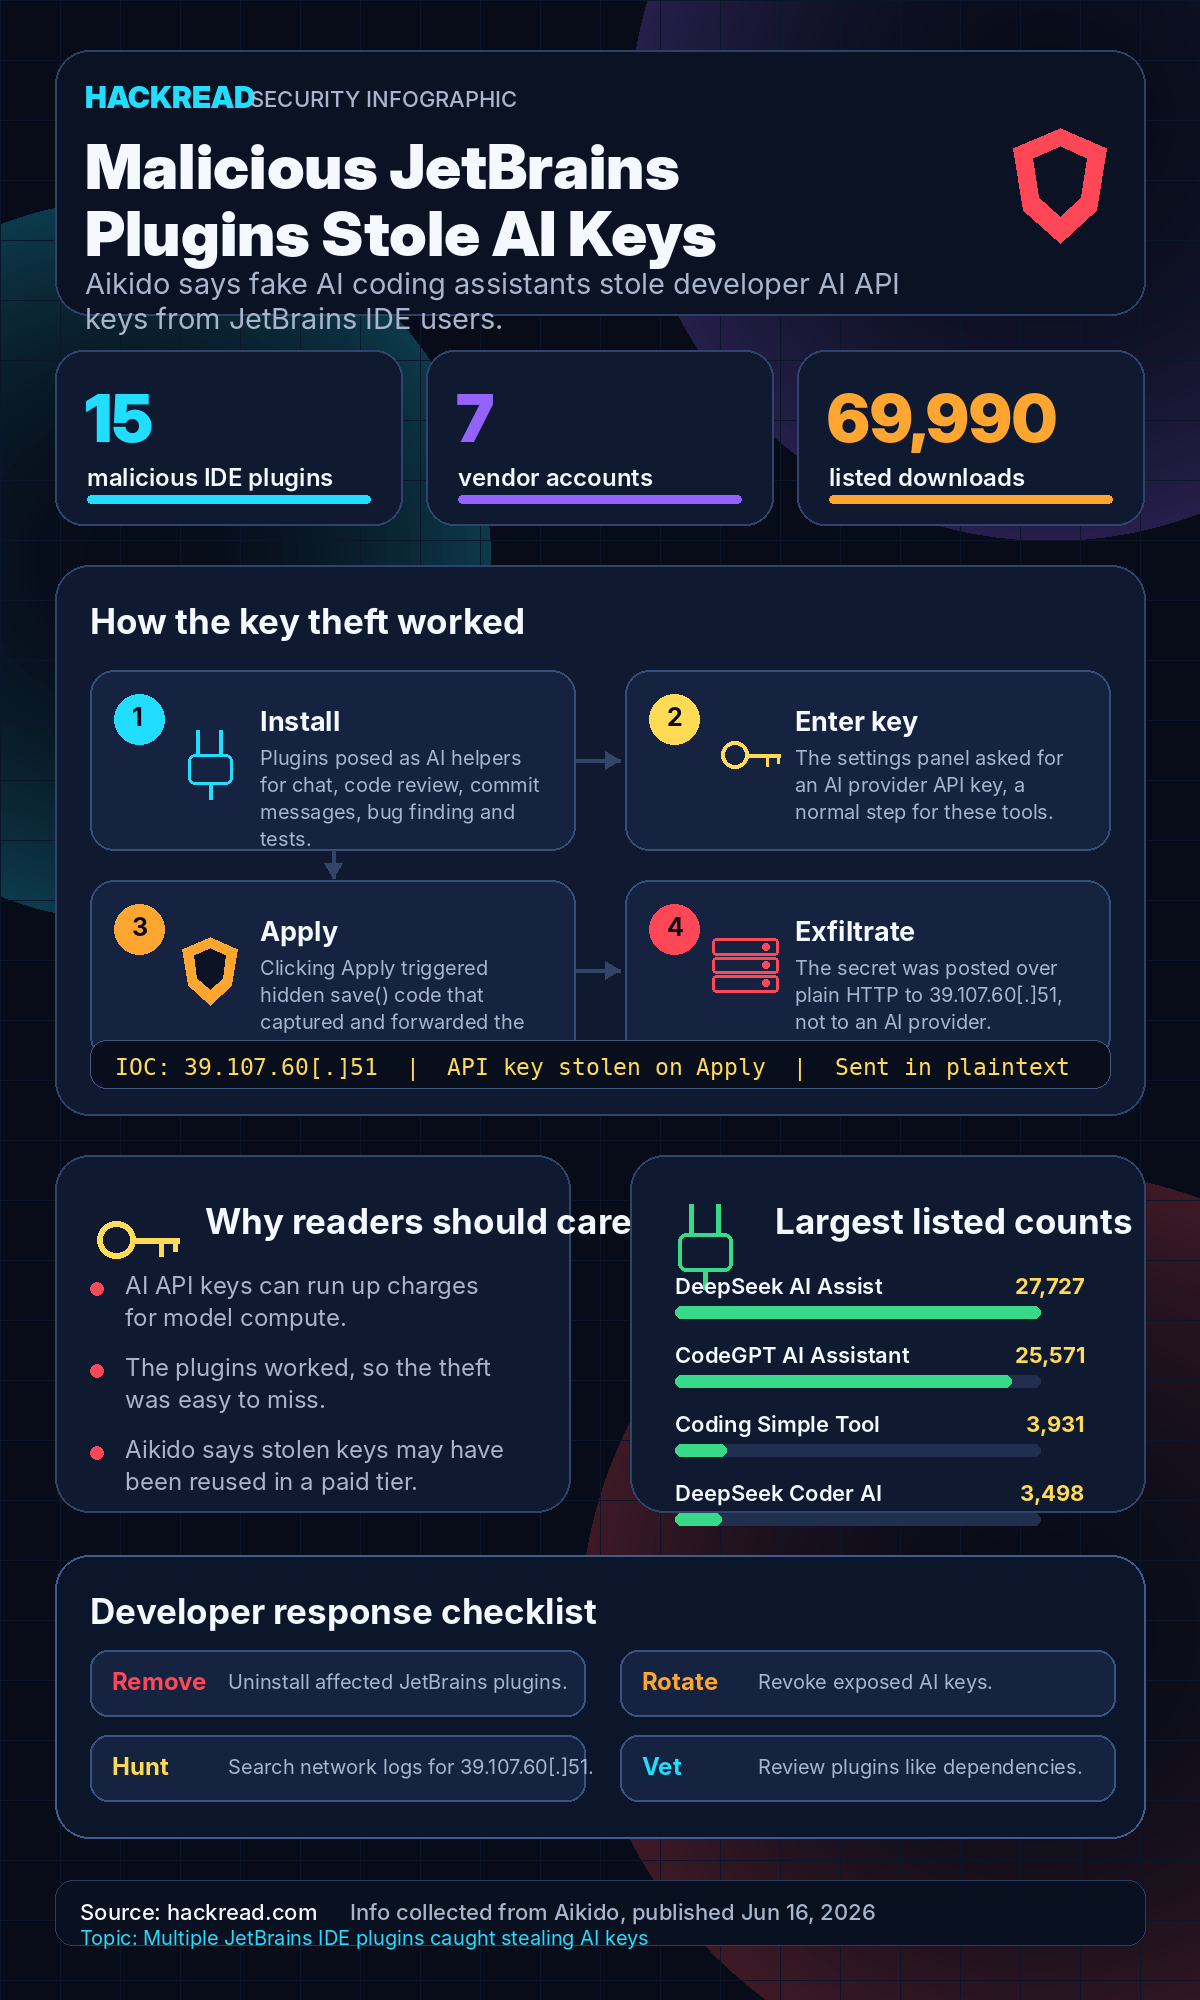
Aikido researchers explained in the blog post shared with Hackread.com that the threat actors also integrated a monetized secondary tier. Users who chose to pay a small fee through an in-app donation prompt received a functional, unrestricted AI key sent back from the malicious server.
“The keys handed to paying users may well be the keys stolen from everyone else, turning the campaign into a service that resells other people’s stolen API access.”
This architectural model allows the operators to steal free developer credentials on one side while generating direct revenue on the other, leaving the original credential owners to fund the unauthorised compute usage.
This research highlights a key fact that hackers nowadays like targeting IDEs. IDE plugins possess high privileges and lack sandbox restrictions on developer workstations, which is why they become a high-value entry point for stealing source code, cloud credentials, and API access. Similar techniques were observed in late 2025 during the GlassWorm malware campaign, which successfully compromised the Visual Studio Code system.
Since IDE plugins run directly on sensitive engineering workstations, researchers advise developers to treat marketplace extensions with the same level of caution as any third-party code dependency.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。