



Cybercriminals linked to the DragonForce ransomware group recently compromised a US services firm and concealed their malicious traffic by abusing Microsoft Teams’ relay infrastructure.
According to research from Broadcom’s Symantec and Carbon Black threat hunter teams, the attackers used a newly identified, custom-built backdoor to keep their activity hidden inside trusted business traffic.
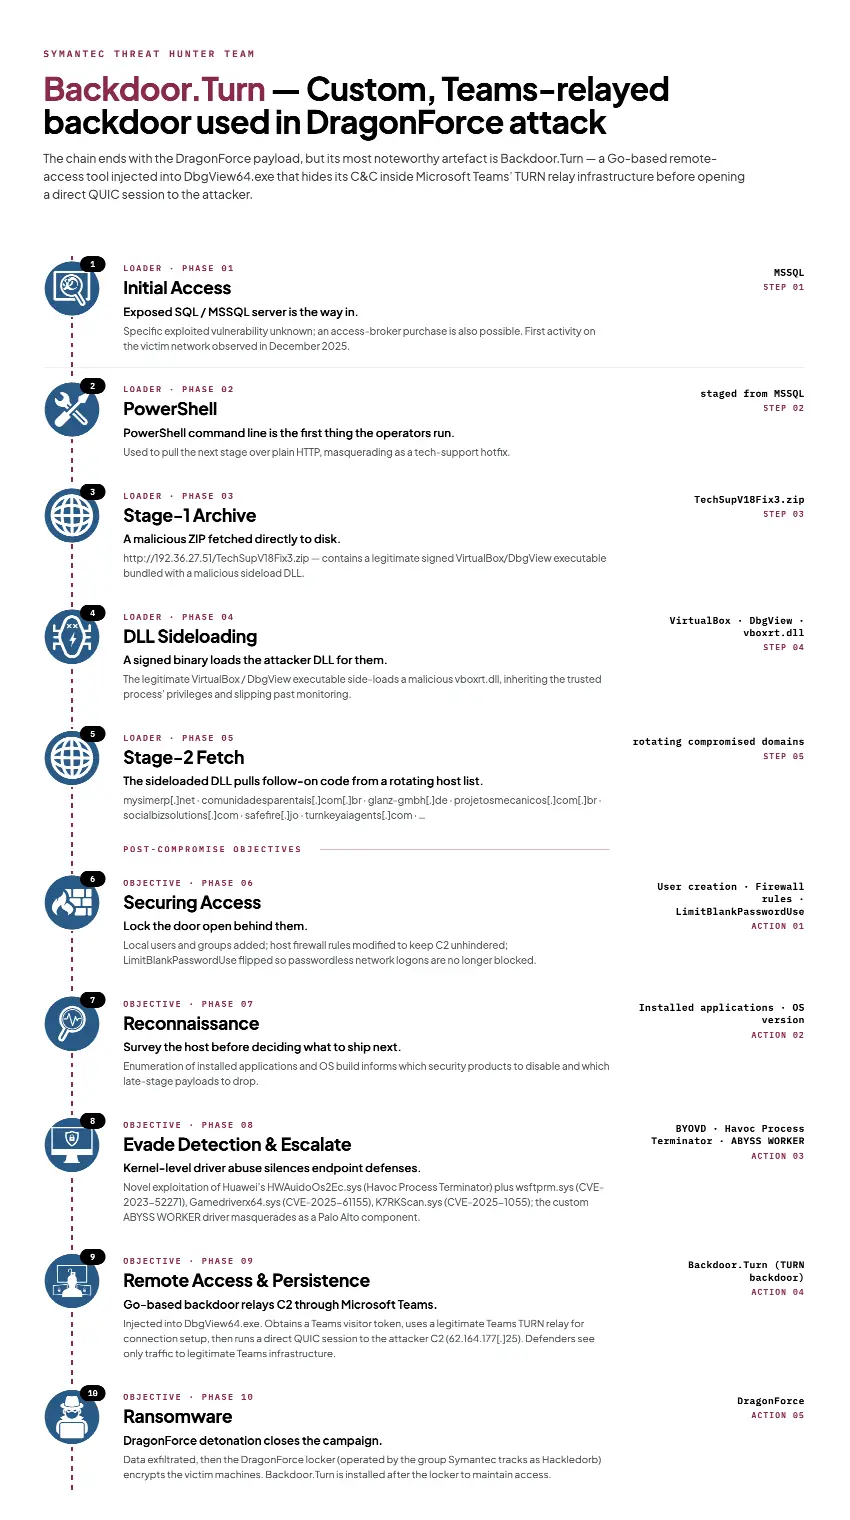
The custom tool used in the attack has been identified as Backdoor.Turn, a Go-based backdoor designed to hide command-and-control traffic inside trusted Microsoft Teams relay connections.
According to Symantec and Carbon Black researchers, Backdoor.Turn first obtains an anonymous Microsoft Teams visitor token, then uses Microsoft’s TURN relay infrastructure to route traffic through legitimate Microsoft servers before connecting to the attackers’ command-and-control server.
That makes the activity difficult to spot. To network administrators, the traffic may appear to be ordinary Microsoft Teams communication rather than a connection to attacker-controlled infrastructure. The researchers said this “appears to be the first malware family to abuse the TURN relay infrastructure in this way.”
The attackers gained an initial foothold in the US company’s network in December 2025. Researchers said the intrusion most likely began with the exploitation of an unknown vulnerability in an SQL or MSSQL server, although they also noted that access may have been purchased from an initial access broker.
After gaining access, the attackers used DLL sideloading to execute malicious code. In this case, they abused a legitimate VirtualBox executable to load a malicious DLL, allowing the malware to run through a trusted process and avoid immediate detection.
The attackers remained inside the company’s network for one to two months before deploying ransomware. During that period, they modified firewall rules and system settings to maintain access and prepare the environment for later stages of the attack.
To disable security tools, the attackers used bring-your-own-vulnerable-driver (BYOVD) techniques, a method in which legitimate but vulnerable drivers are installed and abused to gain high-level system access.
Researchers said the attackers used a new tool called Havoc Process Terminator to exploit a Huawei audio driver, tracked as HWAudioOs2Ec.sys. They also exploited three documented driver vulnerabilities CVE-2023-52271 in Topaz Antifraud, CVE-2025-61155 in Tower of Fantasy, and CVE-2025-1055 in K7 Security Anti-Malware. In addition, they used Abyss Worker, a malicious driver that masqueraded as a Palo Alto Networks security component.
The next step, as per the company’s blog post, the attackers stole confidential files and encrypted systems using DragonForce ransomware. They also deployed Backdoor.Turn, which could allow them to retain access, steal browser credentials, or resell access to the compromised network.
Symantec and Carbon Black researchers assessed that the custom backdoor, combined with the group’s advanced evasion methods, shows DragonForce has “transitioned from a standard ransomware-as-a-service (RaaS) model to a highly organised, formalised cartel structure.” The researchers also described the group as one of the most capable and persistent ransomware operations active today.
In comments shared with hackread.com, cybersecurity experts offered additional context on how this infrastructure abuse affects corporate security.
Jason Soroko, Senior Fellow at Sectigo, explained how the mechanism works. “The Backdoor.Turn malware exploits this infrastructure by routing command and control communications through Microsoft servers. This method masks the activities of the attacker as business traffic. Firewalls and security systems trust traffic flowing to and from Microsoft domains, which allows the data to bypass filters.”
Robert Coles, Senior Manager of Threat Intelligence Security at Black Duck, noted the changing nature of these extortion groups, stating: “They’re investing in more advanced tradecraft, custom tooling, BYOVD for defense evasion, and now leveraging trusted cloud services to stay persistent and operate under the radar. That’s not typical “smash-and-grab” ransomware anymore; it’s much closer to what we historically associated with more advanced threat actors.”
Shane Barney, Chief Information Security Officer at Keeper Security, emphasised the danger of implicit corporate trust. Barney commented, “Backdoor.Turn works because organizations extend implicit trust to the collaboration infrastructure that they would never extend to other systems. TURN servers are the relay layer that platforms like Microsoft Teams use to route traffic when direct connections fail, and security tools generally treat that traffic as benign by design.”
(Photo by Jack B on Unsplash)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。