








Operation Endgame has expanded its reach by dismantling the network infrastructure of TA569, a major cybercriminal syndicate.
On 18 June 2026, international law enforcement agencies, including the Netherlands National High-Tech Crime Unit (NHCTU), the Royal Canadian Mounted Police (RCMP), the US Federal Bureau of Investigation (FBI), and Germany’s Federal Criminal Police Office (BKA), with operational support from Europol, announced the successful disruption of the group responsible for the SocGholish malware framework.
This joint action marks the latest phase of the ongoing global campaign targeting initial access brokers and botnets that feed ransomware networks. This development follows threat intelligence provided by Proofpoint, which was shared with Hackread.com.
Proofpoint research reveals that this group uses the web injection method to deploy malware on legitimate, high-traffic websites. They can target any website for this purpose- from retail to news platforms. The next step involves gaining privileged access to content management systems (CMS) like WordPress either by using stolen credentials or exploiting vulnerabilities in unpatched plugins.
The SocGholish framework operates via a multi-stage attack chain. First, a script profiles the visitor’s environment to verify the visitor is a real person and not an automated security sandbox. It does this by tracking at least ten mouse movements. It also checks that the user does not have developer tools open.
If everything matches, the script uses a traffic distribution system like ParrotTDS or a Keitaro service run by TA2726 to route the user. The victim then sees a FakeUpdates screen that impersonates a normal browser update alert. Clicking this button runs a hidden iframe that downloads GhoLoader, a first-stage JScript downloader.
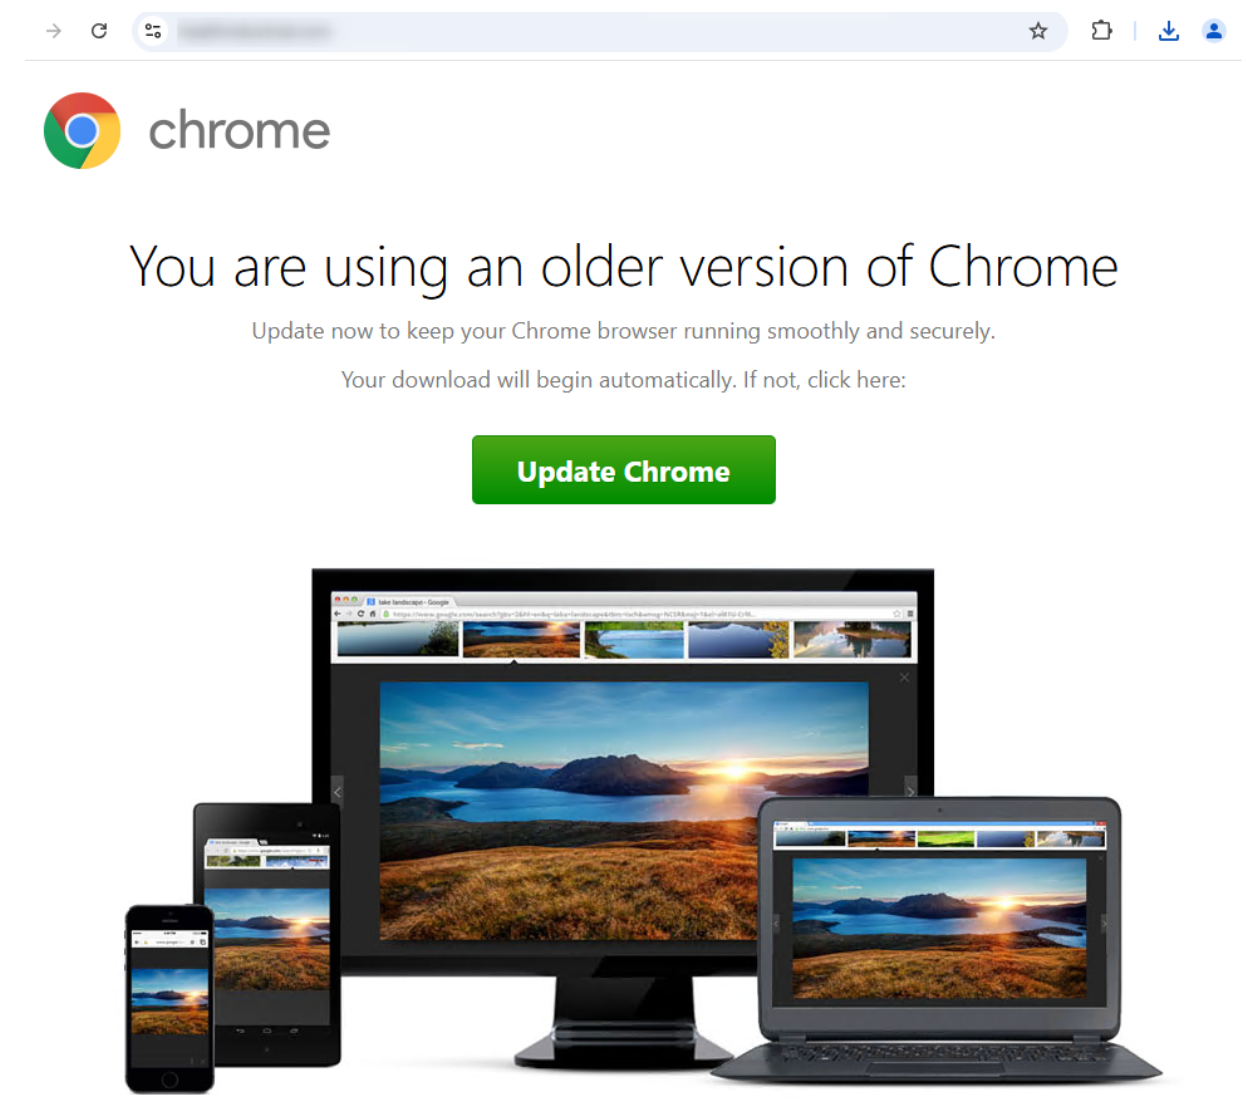
TA569 then tries to ensure persistence on the site. This is achieved by installing fake plugins and PHP backdoors. These are the same initial access points that allowed ransomware groups like Evil Corp, LockBit, RansomHub, and WastedLocker to obtain deeper access to corporate networks in the past.
According to Dutch Police’s press release, to break this specific ransomware pipeline, the global coalition behind Operation Endgame aimed its recent enforcement actions directly at these access points. By taking down the core infrastructure feeding these networks, officials seized over 100 command-and-control (C2) servers and remediated 14,971 such compromised websites.
This latest crackdown is one of the many past achievements made through Operation Endgame. Hackread.com has covered Operation Endgame over the last couple of years.
In May 2024, the operation resulted in seizing around 100 servers belonging to dropper networks, including IcedID, SystemBC, Smokeloader, Trickbot, Pikabot, and Bumblebee, and by May 2025, the DanaBot network was dismantled, leading to charges against 16 people.
Later in November 2025, police shut down over 1,025 servers used by three other malware groups, terminating the core infrastructure of the Rhadamanthys infostealer, the VenomRAT remote control tool, and the Elysium botnet.
Most recently, in January 2026, Dutch police arrested the 33-year-old mastermind behind a hacker testing site at Amsterdam’s airport. Nevetheless, experts believe this latest hit on SocGholish will cause severe financial and reputational damage to the TA569 group, making the internet safer for everyone.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。