


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

腾讯CDC
IT之家
IT之家
有赞技术团队
有赞技术团队
WordPress大学
WordPress大学
Apple Machine Learning Research
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
人人都是产品经理
人人都是产品经理
The Cloudflare Blog
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
博客园 - 【当耐特】
V
V2EX
Last Week in AI
Last Week in AI
H
Help Net Security
The GitHub Blog
The GitHub Blog
S
SegmentFault 最新的问题
F
Fortinet All Blogs
I
InfoQ
宝玉的分享
宝玉的分享
A
About on SuperTechFans
MongoDB | Blog
MongoDB | Blog
Microsoft Azure Blog
Blog — PlanetScale
Blog — PlanetScale
B
Blog

Hackread – Cybersecurity News, Data Breaches, AI and More

Operation Endgame Disrupts StealC, Amadey and SocGholish Malware Networks New GhostShell Hacking Group Targets Ukraine’s Drone Defense Sector Fake npm Packages Impersonate PostCSS Tool to Steal Chrome Passwords Best Crypto Payment Solutions for E-Commerce Businesses Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity LastPass Confirms Customer Data Breach After Klue OAuth Token Theft ‘Cordyceps’ CI/CD Flaw Exposes Microsoft, Google, Apache Repos to Pipeline Hijacking The Rise of AI-Powered Academic Fraud: Beyond Traditional Plagiarism New CryptoBandits Malware Uses USB Drives and Tor to Steal Crypto The Evolution of iGaming Fraud: What Security Teams Should Expect in 2027 2 Scattered Spider-Linked Hackers Plead Guilty Over £39M TfL Cyberattack Beats Studio Buds Flaw Could Let Nearby Attackers Eavesdrop on Users Texas Parks and Wildlife Data Breach Affects Over 3M License Customers Threat Hunting Beyond Alerts: Finding the Activity Detection Misses Scammers Use Fake GitHub Stars, VirusTotal Reviews to Spread Crypto Clipper Salesforce Disables Klue Integration After OAuth Token Theft Hits Customer Data MDR Provider Comparison: Time to Discover and Respond to Threats Meteor 3.0 Migration Helped Rocket.Chat Move Off End-of-Life Node.js Runtime Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections Nintendo America Employee Data Exposed After Shadowbyt3$ Targets TinyPulse eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks FIFA World Cup 2026: Hackers Target Football Fans With Fake Tickets Sites MacBook Neo vs Windows Laptops for Cybersecurity Tasks Operation Endgame Disrupts SocGholish Malware Infrastructure What Businesses Should Know Before Migrating Their CMS DragonForce Ransomware Abused Microsoft Teams to Hide Malware Activity Agentjacking: Researchers Show How One Fake Bug Report Can Hijack AI Coding Agents FortiBleed Attack Exposes Fortinet Firewall Credentials in 194 Countries SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Fake Search Clicks
Hackers Hide New Argamal Malware Inside Working Hentai Games
Deeba Ahmed · 2026-06-15 · via Hackread – Cybersecurity News, Data Breaches, AI and More

Cybersecurity firm Kaspersky has discovered a new campaign delivering malware to people downloading adult video games. Detected in April 2026, Kaspersky’s investigation suggests that this malware is named Argamal, and it is hidden inside hentai game installers. Argamal is a remote access Trojan (RAT) that allows hackers to remotely control a person’s computer.

Researchers note that Normal internet scams usually give you a broken file that will not open. These infected downloads actually include fully working games built on common systems like RenPy or RPG Maker. The game runs exactly as you want it to, so you never realise your machine is under someone’s control.

How the Attack Works

These malicious files are distributed via different platforms such as adult game sites, file-sharing platforms like PixelDrain, and torrent trackers such as AniRena. The game archive, when downloaded, launches a rigged version of a standard library file called FFmpeg DLL and another file named natives2_blob.bin right after the game starts.

This rigged library loads into the computer memory without any warning screens popping up, and immediately runs a PowerShell script. To avoid detection, the script first checks the system for monitoring tools like Sandboxie or Procmon64.
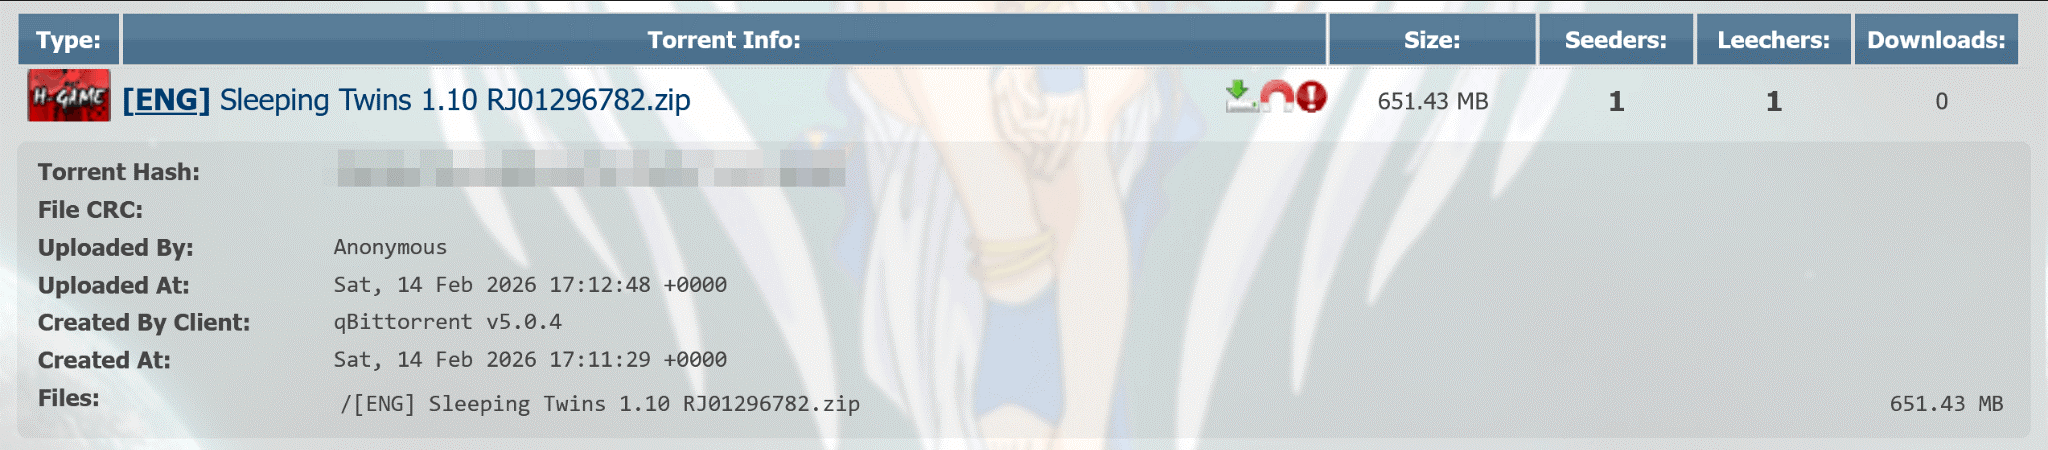
Malicious game torrent in AniRena (Source: Kaspersky Securelist)

If the computer seems safe, the malware waits. Three days later, a scheduled task opens and uses a tool called bitsadmin.exe to download an encrypted file (zaesdl.dat) from GitHub, and decrypts it using AES-CBC encryption to create the main Trojan module.

To ensure persistence on the device, the malware uses COM hijacking. It alters the registry entries for a real Windows feature called the Windows Color System Calibration Loader. This feature runs every time a user logs into their PC, meaning the malware automatically starts up during every new user session.

What Hackers Can Do

Argamal malware immediately sends UDP heartbeats (updates) to attackers’ servers once active on the device. These servers are hosted on domains such as asper1.freeddns.org and Winst0.kozow.com.

This allows the attackers full control over the system. They can now perform malicious activities of all sorts, ranging from stealing files, reading private chats, and gathering financial data to taking screenshots, swapping crypto-wallet addresses, and streaming live videos.
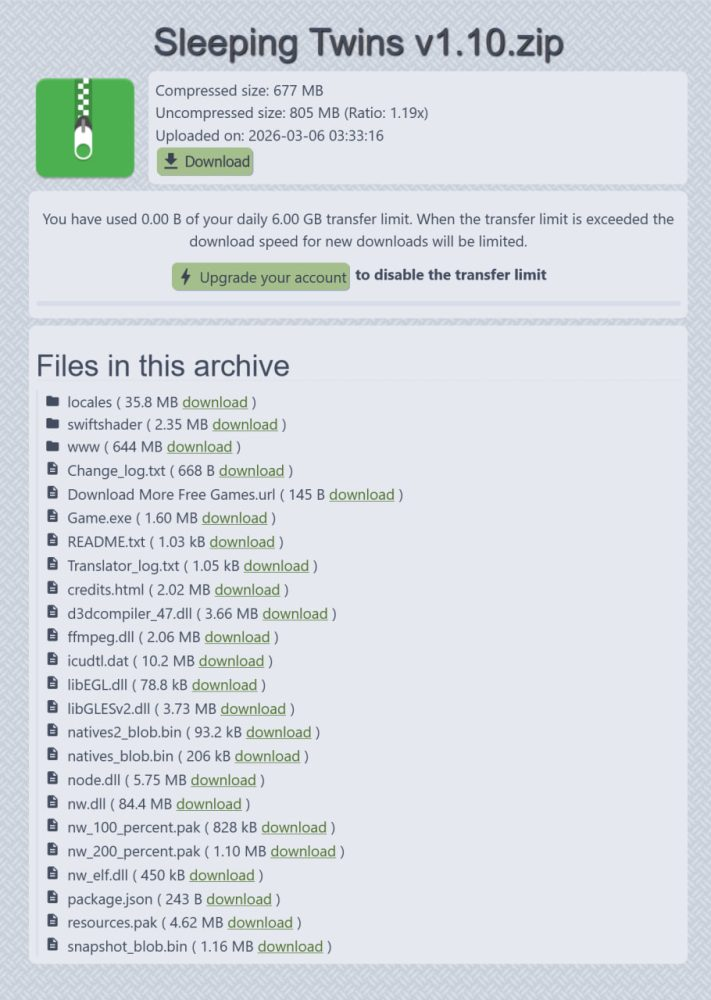
Game archive contents (Source: Kaspersky Securelist)

Kaspersky has detected hundreds of users infected so far, mostly in Russia, Brazil, Germany, and Vietnam. Code analysis suggests that the attackers speak Spanish. A crucial finding is that the malware purposefully avoids targeting users in China. Nevertheless, all users of Hentai games must avoid unverified adult sites and use real-time security software.

(Photo by Urim Pormeia on Unsplash)