








The zLabs research team at mobile security firm Zimperium has identified a new Android banking trojan named Rokarolla. This highly invasive malware is named after its command-and-control infrastructure (the server network that threat actors use to send instructions to infected phones).
According to zLabs researchers, this trojan is unusual in that it combines financial fraud with total device surveillance and can target 217 different cryptocurrency and banking programs.
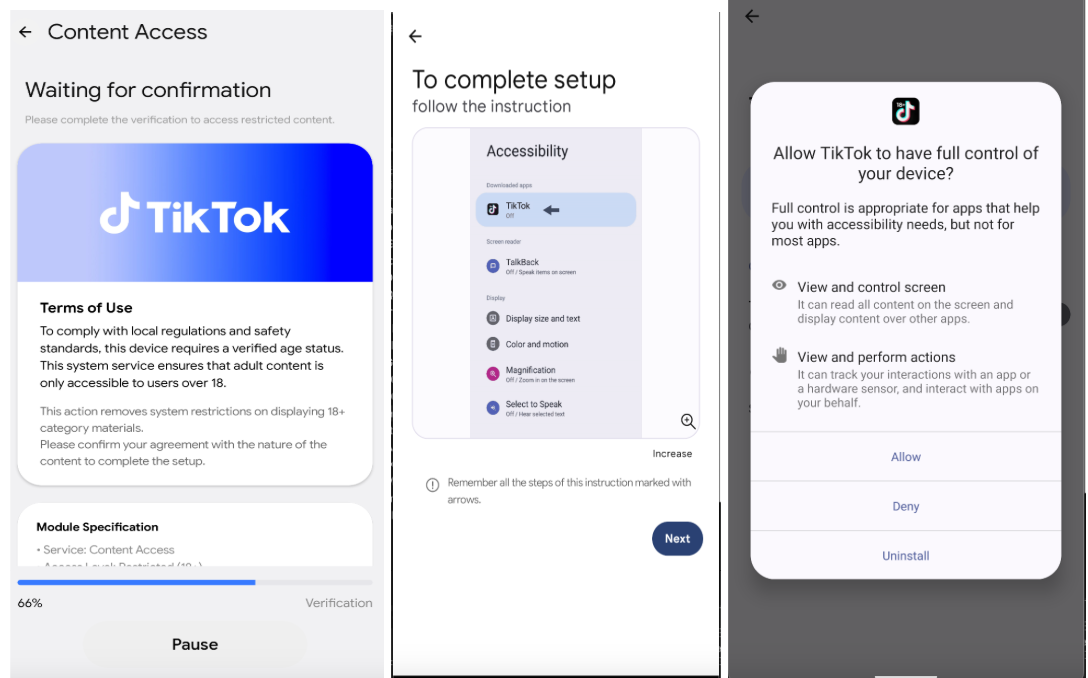
The attack chain begins when a user visits a malicious website like infocontablidades.it.com. These pages actually contain the malware, hidden inside files that look like popular programs such as TikTok or Google Chrome.
When a victim downloads this file, a secondary dropper (secondary malware) runs first, disguised as a Google Play Protect security tool. It is this dropper that tricks the user into installing the final malicious payload.
Once installed, the malware asks for permission to use Android Accessibility Services. Then, it takes over these services to monitor the phone screen and track coordinates without user intervention. It requests to become the phone’s default SMS handler and default Call handler for uninterrupted data interception.
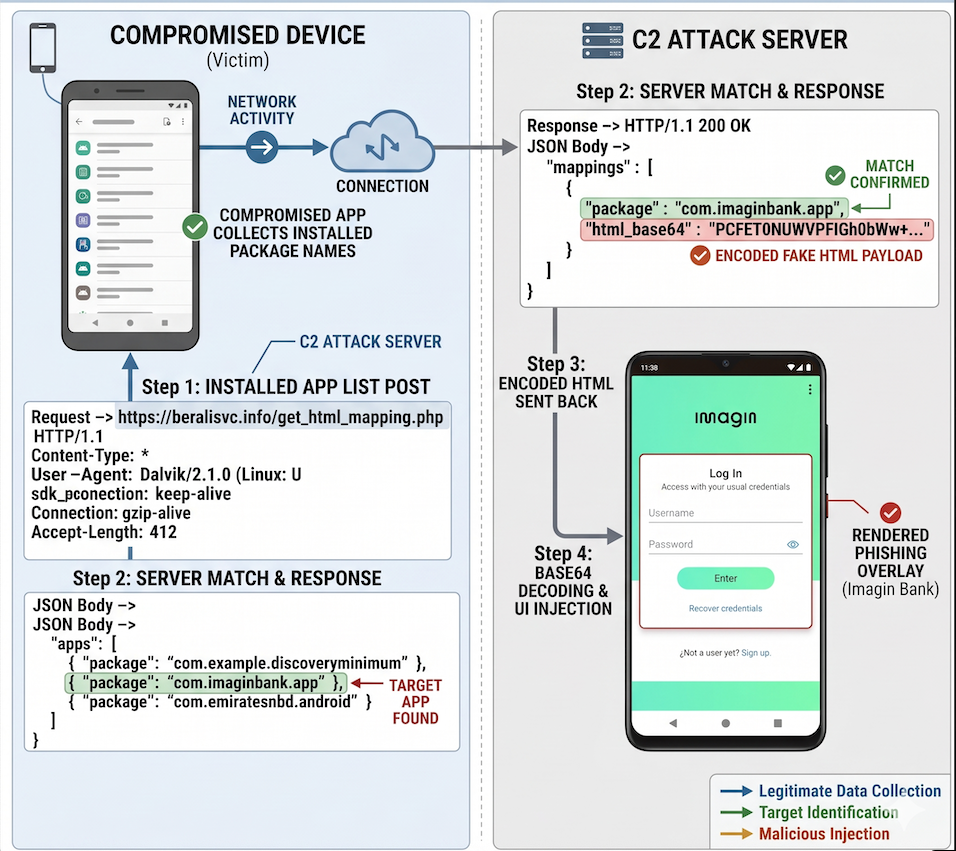
Further investigation revealed that Rokarolla uses fake screen overlays. When a victim opens an authentic financial application, it queries the server’s endpoint to fetch fake HTML-based phishing pages. It then displays these fake login screens right on top of the legitimate apps. It even puts a fake PIN prompt over the phone’s regular lock screen to steal passwords.
Researchers noted that the malware has 137 commands available to control the phone, and it uses specific background code terms, such as and , to trigger these actions. Through an automated keylogger and UI logger, the malware can read text messages, steal WhatsApp lists, track keystrokes, and take screenshots.
Using a snapshot-based surveillance mechanism called Pseudo-VNC, it monitors screens secretly. Also, it performs clipboard hijacking to modify text copied by the user, switching cryptocurrency wallet addresses during transfers without the victim noticing
To keep the attack hidden, Rokarolla stops incoming phone calls using commands like and mutes all sounds. This step stops victims from hearing warning alerts or receiving fraud prevention calls from their banks. It also actively disables real Google Play Protect security scans and forces the device screen to stay on permanently so its background actions are never cut off.
The research shows the changing trends in mobile threats as cybercriminals don’t focus entirely on data theft and aim for full device takeover. This is a worrying trend because controlling a phone’s audio/text messages makes security features like multi-factor authentication completely useless.
Commenting on this, Randolph Barr, Chief Information Security Officer at Cequence Security, a San Francisco, Calif.-based API security and bot management provider, stated that:
“The threat landscape continues to surge, in particular, the mobile threat landscape. Back in 2024 alone, more than 4 million social engineering attacks targeted mobile devices, over 33 million mobile malware/adware incidents were blocked, and phishing attacks rose significantly. Android continues to face banking trojans and data-leaking SDKs, while insecure app practices plague both Android and iOS platforms. Most of these attacks are aimed at PII, credentials, and financial data.”
“Employers and service providers add a third risk layer. Each validation request is a new integration point, creating an additional attack surface. Bad actors could compromise employer systems, abuse verification APIs, or phish organizations into over-collecting and mishandling sensitive data. Since employers often lack the same level of cybersecurity maturity as, say, government systems, they may become the weakest link in the chain,” he warned.
Nevertheless, the best protection against these threats is avoiding third-party links or pop-up ads for downloading files, denying accessibility service requests from unverified apps, and closely monitoring unusual screen behaviour like a device refusing to turn off.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。