






Modern enterprises aren’t just adding employees; they’re adding subsidiaries, multiple teams, contractors, AI builders, temporary projects, and new SaaS tools every week.
And every new addition to a company’s ecosystem also brings more credentials to manage. Unfortunately, not all of those credentials can be managed by solutions like single-sign-on (SSO) or privileged access management (PAM). Many of them might be stored in shared spreadsheets, developer environments, browser sessions, and automation workflows that traditional identity security systems were never designed to govern.
This results in identity sprawl, operational drag, and an overall widening of the Access-Trust Gap. In the face of this ever-expanding attack surface, security leaders are left struggling to deploy credential security across every team and workflow, without having to build more infrastructure just to manage their infrastructure.
In light of these issues, today we’re introducing a new evolution for 1Password Enterprise Password Manager (EPM): enterprise-grade provisioning, structure, governance, and security automation built directly into the platform.
This launch includes:
Automated Provisioning hosted by 1Password
Enterprise multi-tenancy
Verified emails from 1Password
OAuth-based Users API and new Security Automation integrations
Together, these capabilities make EPM easier to deploy, easier to scale, and easier to operate as the foundational tool of modern identity security.
Automated Provisioning hosted by 1Password is our next-generation provisioning solution, built directly into 1Password. Automated Provisioning requires no servers to deploy, no bridge to maintain, and no ongoing infrastructure burden.
In early testing, the response from admins was immediate.
“We were done in about five minutes. We set everything up from scratch, added the integration in Okta, and it worked immediately. Adding and removing users was seamless. This is 100% a better experience than trying to set up the SCIM bridge on GCP. This is exactly what a best-in-class provisioning experience should look like: URL, token, test API, and SCIM is up and running. Thanks for making it so easy.”
By hosting provisioning inside 1Password’s secure infrastructure, powered by confidential computing, we removed the operational tax that slows teams down without compromising our zero-knowledge security model.
Most provisioning solutions start from the same assumption: the service managing users can also see the data it manages.
That assumption does not work for 1Password.
From day one, 1Password has operated on a zero-knowledge, end-to-end encrypted architecture. At no point can anyone at 1Password see customers' encryption keys or vaults. Even our own infrastructure cannot read your data. That privacy model is core to 1Password, but it also makes automation significantly more difficult. For years, that tradeoff forced a choice: teams could have automation, or they could have zero-knowledge security, but they couldn’t have both without adding significant complexity by running their own infrastructure.
Automated Provisioning hosted by 1Password completely changes that dichotomy. Instead of asking customers to trust a hosted service with sensitive cryptographic operations, we designed provisioning to run inside of an isolated secure enclave. Encryption keys are generated, used, and protected inside that enclave, meaning that they stay isolated not just from 1Password operators, but even from the underlying cloud provider.
In practical terms, that means:
1Password can automate user creation and access without ever seeing client secrets
Cryptographic operations are isolated, attested, and inaccessible to operators
Every provisioning action is recorded in a verifiable trust log that clients can independently validate
Rather than a hosted version of a SCIM integration, this is a fundamentally different approach to automation in a zero-knowledge system.
The result is something rare in identity infrastructure: automation that scales without compromising privacy or trust.
Still, automating users is table stakes. The next challenge is organizing access at enterprise scale, and it’s significantly harder.
As companies grow, many start with a single 1Password account, which they quickly outgrow. Over time, different teams need different policies. For instance, acquisitions often require some degree of autonomy without losing oversight.
1Password Enterprise now supports multi-tenancy, enabling parent and child account structures with:
Delegated administration
Consistent policy enforcement
Centralized visibility
And more
This new way of structuring 1Password gets away from the “one size fits all” model and allows you to create a more personalized structure that maps to the way your team actually operates.
Automated Provisioning support for multi-tenant environments is coming soon after launch for teams that want to add automated assignment workflows.
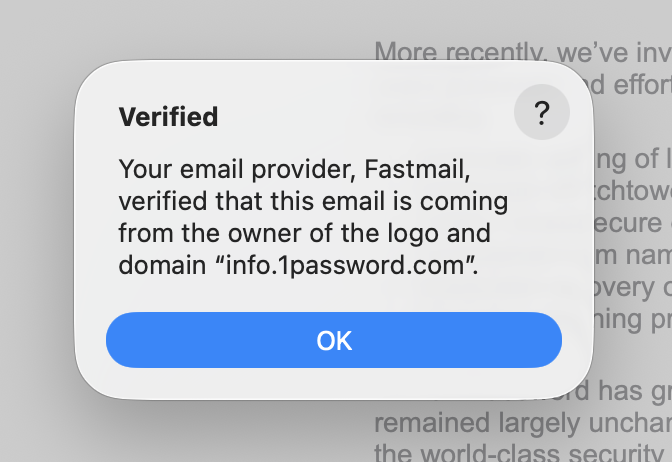
Trust at the moment of access matters, especially when identity decisions are happening in real time. That’s why emails sent from 1Password now display our verified logo and authentication indicator across supported inboxes, including Gmail, Apple Mail, Yahoo (and more).
By meeting the strict verification requirements reserved for highly trusted senders, every message from 1password.com, 1password.ca, 1password.eu, and agilebits.com now carries built-in proof of authenticity that attackers can’t replicate. For customers onboarding users, verifying accounts, or recovering access, this removes hesitation at a critical moment. It reduces false phishing reports, accelerates self-service flows, and reinforces 1Password as a trusted foundation for identity security — not just in the browser or vault, but everywhere our customers interact with us.
Modern security teams increasingly rely on integrated security operations center (SOC) workflows that correlate signals and alerts, while orchestrating detection responses in real time. Behind every alert is an identity: a person, a service account, an API key, or an AI agent. However, when remediation requires manual steps, investigation and response slows, increasing security risks.
We’re launching the Users API for Partners (in public preview), our first API using OAuth 2.0-based authentication designed for secure, enterprise-grade security. Enabling ecosystem partners to build integrations for 1Password Enterprise Password Manager and use delegated, scoped authorization to list users, suspend access when risk is detected, and restore access after remediation.
We’ve worked with strategic partners over the past few months to build new security automation integrations using the Users API. With these integrations, customers can use EPM events activity logs and SIEM insights, alongside security automations, to trigger automated SOC workflows to suspend or restore users in 1Password Enterprise Password Manager when risk is detected.
Joint customers of 1Password Enterprise Password Manager and CrowdStrike, as well as BlinkOps, Elastic, Sumo Logic, Tines, and Torq can configure their OAuth integration within the Integrations page of EPM starting today.
For customers, this helps SOC teams reduce exposure time and act on risk with greater speed and consistency. For partners, this enables joint value solutions built on OAuth designed for secure, enterprise-grade extensibility.
Automated Provisioning hosted by 1Password, multi-tenancy, and the Users API for Partners, were all made to serve the same goal; they make it easier than ever to deploy 1Password EPM wall to wall. Simplified provisioning, scalable structure, and predictable governance all help enterprises secure every team and workflow, while preserving the usability and zero-knowledge security model that 1Password is known for.
These capabilities mark another step toward what modern enterprises need most: security that scales with the business instead of slowing it down.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。