







Chris Sullo, General InfoSec Tips & Tricks, Web App Burp Suite, Copy For
Chris has been working in security for 30 years, mainly doing penetration testing in both consulting and corporate environments. Chris is the author of the Nikto web scanner, founder of the RVAsec conference, and has been involved in many OSS projects and community efforts.
If you’ve ever had to take a request from Burp and turn it into a command line, especially for jwt_tool.py, you know it can be painful—but no more! The “Copy For” extension is here to save valuable time.
This simple extension allows you to quickly generate command-line syntax for security tools directly from Burp Suite’s context menu.
What is Copy For?
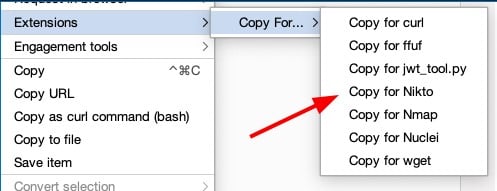
Copy For is a Burp Suite extension that enables pentesters to effortlessly copy formatted commands for popular security tools. It integrates into Burp’s UI by adding new options to the Extensions context menu when you right-click on a request.
Why Use Copy For?
As a pentester, you often need to switch between Burp Suite and other command-line tools during your assessments. Manually crafting commands for these tools can be time-consuming and error prone. Copy For eliminates this hassle by automatically generating properly formatted commands based on the selected request in Burp.
Key Features
Built-in Commands: Copy For comes with built-in support for several popular tools, including:
- curl – command line tool and library for transferring data with URLs
- ffuf – Fuzz Faster U Fool
- jwt_tool.py – The JSON Web Token Toolkit v2
- Nikto – Web scanner
- Nmap – The Network Mapper
- Nuclei – Vulnerability Scanner
- Wget – Retrieves files via the most widely used Internet protocols
You can also add your own custom commands, allowing you to extend the functionality to suit your specific needs.
Variable Substitution: The extension uses a variable substitution system, automatically populating commands with relevant information from the selected request. The substitutions are:
- {baseurl} – Base URL (protocol , user/pass, port, domain)
- {body} – Request body (if present)
- {directory} – Path-safe directory name based on base URL
- {url} – Full URL
- {filename} – Path-safe filename based on hostname
- {headers} – Request headers
- {hostname} – Hostname header value
- {method} – HTTP method
- {port} – Port number
- {ua} – User Agent (default is Firefox)
For the built-in commands, some items like {headers} will be formatted into the proper command-line switches (such as “-h” or “-H” depending on the tool).
Configurable Flags: Each tool’s command flags can be customized through the extension’s configuration panel, giving you full control over the generated commands.
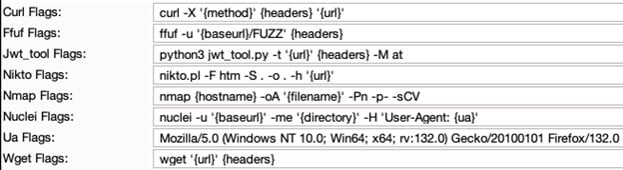
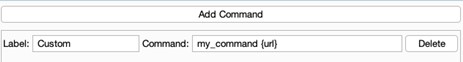
Custom Commands: An arbitrary number of custom commands can be added via the configuration panel, allowing you to add what you need without source code changes!
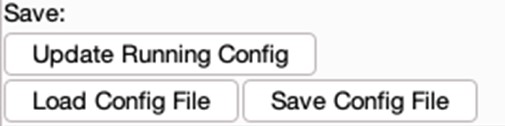
Save Configuration: The extension can save the current configuration in the Burp Project by pressing Update Running Config (which will keep the settings for the current project only), or in a JSON configuration file that can be loaded into any Burp Project.
How Copy For Works
When you right-click on a request in Burp Suite, Copy For adds menu items for each tool. Upon selecting a tool from the menu, Copy For analyzes the request and extracts relevant information, and replaces placeholders with actual values.
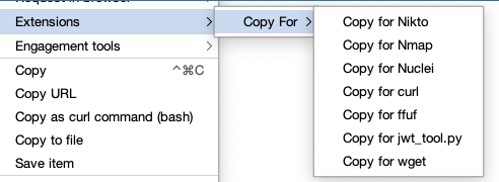
The fully formed command is automatically copied to the clipboard.
Installation
Until the extension makes it to the BApp Store, simply download the python file directly or via git and tell Burp how to find it. You will also need to install Jython if you do not already have it.
- Clone the extension using git (or download the file directly):
git clone https://github.com/sullo/copy-for.git
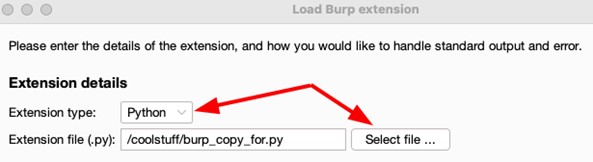
- Press the Add button in Burp’s Extensions tab.
- Set the extension type to Python.
- Press the “Select file…” button and navigate to the location you saved the extension’s code.
- Press the Next button to complete the process.
Summary & Acknowledgements
Copy For is a handy addition to any pentester’s toolkit. By automating the tedious task of command generation, it allows you to focus on what really matters – finding and exploiting vulnerabilities. Whether you’re a seasoned professional or just starting out in the field, Copy For will help you work more efficiently and effectively in Burp Suite.
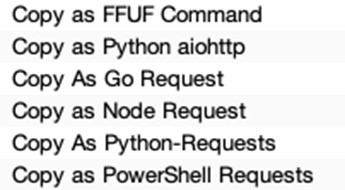
This extension builds on the idea of these other fine “Copy As” tools available in the BApp store:
Ready to learn more?
Level up your skills with affordable classes from Antisyphon!
Available live/virtual and on-demand
