







General InfoSec Tips & Tricks, , InfoSec 101 burnout, Infosec for Beginners, InfoSec Survival Guide, Mental health
by Amanda Berlin of Mental Health Hackers
This article was originally published in the second edition of the InfoSec Survival Guide. Find it free online HERE or order your $1 physical copy on the Spearphish General Store.
Cybersecurity is a rapidly growing field, and with it, comes a number of mental health challenges above and beyond our normal day-to-day living. We are all often under a great deal of stress, as we are responsible for protecting data, environments, and more from attackers, no matter what role we are in. This can lead to burnout, imposter syndrome, high levels of anxiety, and more.
Common Mental Health Issues in Cybersecurity
- Burnout is a state of physical, emotional, and mental exhaustion caused by prolonged stress. One of the reasons we are at risk of burnout is because of the constant bombardment of new threats, attacks, and vulnerabilities. We sometimes feel that we “always have to be on,” even to the detriment of our own health.
- High stress and anxiety are common in the cybersecurity field. Our bodies aren’t built to be in a constant “fight or flight” mode.
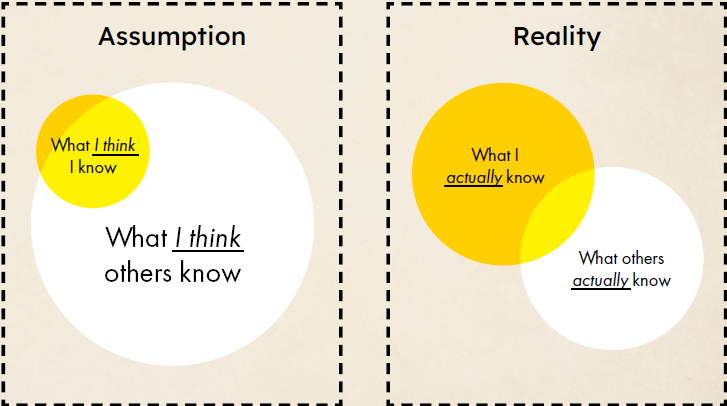
- Imposter syndrome is a feeling of inadequacy and insecurity, despite evidence to the contrary. We are often surrounded by highly skilled and knowledgeable people; it’s one of the amazing aspects of our community, but can also be an indirect source of stress.
Tips for Prevention
- Take breaks; try not to stare at your screen constantly. Work/life balance is difficult. Overwhelmed or stressed? Go do something else to switch your brain off from work.
- Exercise is a powerful way to reduce stress and anxiety. It’s not just about getting fit, it’s also about reconnecting your mind and your body. You don’t have to hit the gym — even a simple, short walk can do wonders. If it’s too difficult, start smaller… just start somewhere.
- Take care of yourself by speaking to yourself as you would a friend, eating healthy, getting enough sleep, and exercising. This is easier said than done. Start small and work towards achievable goals to establish health habits. (Be kind to yourself. Build trust with yourself that you’ll take care of you.)
- Talk to someone you trust. It could be a friend or a professional. It may take some patience and persistence to find the right fit, but therapists are professionals that can give you tools to succeed. (Professional therapy isn’t the only option. Help can take other forms. Keep seeking out what helps you.)
Places to Talk With Fellow Peers
- Online forums: Discord and Slack groups are available in all different areas of security. Many of these have dedicated mental health channels. If you community doesn’t have a mental health channel, try asking for one.
- Scheduled chats with friends: Text, phone, or video, scheduling friend time is sometimes needed amongst our busy daily scheduled.
Mental health is an important issue for everyone. Everyone struggles, you’re not alone. By being aware of the signs and taking steps to prevent mental health struggles, we all improve our mental health and well-being.
Lastly, and most importantly, it’s never too late. You can find healing after burnout. You can recover from workplace trauma. Reach out and ask for help.
More Help
The National Alliance on Mental Illness (NAMI): nami.org
The American Foundation for Suicide Prevention (AFSP): afsp.org
Mental Health Hackers: mentalhealthhackers.org/resources-and-links/
American Psychiatric Association’s Resources for Employers: workplacementalhealth.org
Mental Health First Aid: mentalhealthfirstaid.org
Sober in Cyber: soberincyber.org/about
If you find yourself or someone you love in a crisis, you can call 988 for the National Suicide & Crisis Prevention Line. The Lifeline provides 24/7 free and confidential support for people in distress, as well as prevention resources for you and your loved ones.
Read more in our “Infosec for Beginners” blog series:
- How to Get a Job in Cybersecurity
- John Strand’s 5 Phase Plan For Starting in Computer Security
- From High School to Cyber Ninja—For Free (Almost)!
- Blue Team, Red Team, and Purple Team: An Overview
- Pentesting, Threat Hunting, and SOC: An Overview
- What Is Penetration Testing?
- How to Perform and Combat Social Engineering
- The Human Element in Cybersecurity: Understanding Trust and Social Engineering
- Build a Home Lab: Equipment, Tools, and Tips
- Questions From a Beginner Threat Hunter
- Shenetworks Recommends: 9 Must Watch BHIS YouTube Videos
- Mental Health – An Infosec Challenge