







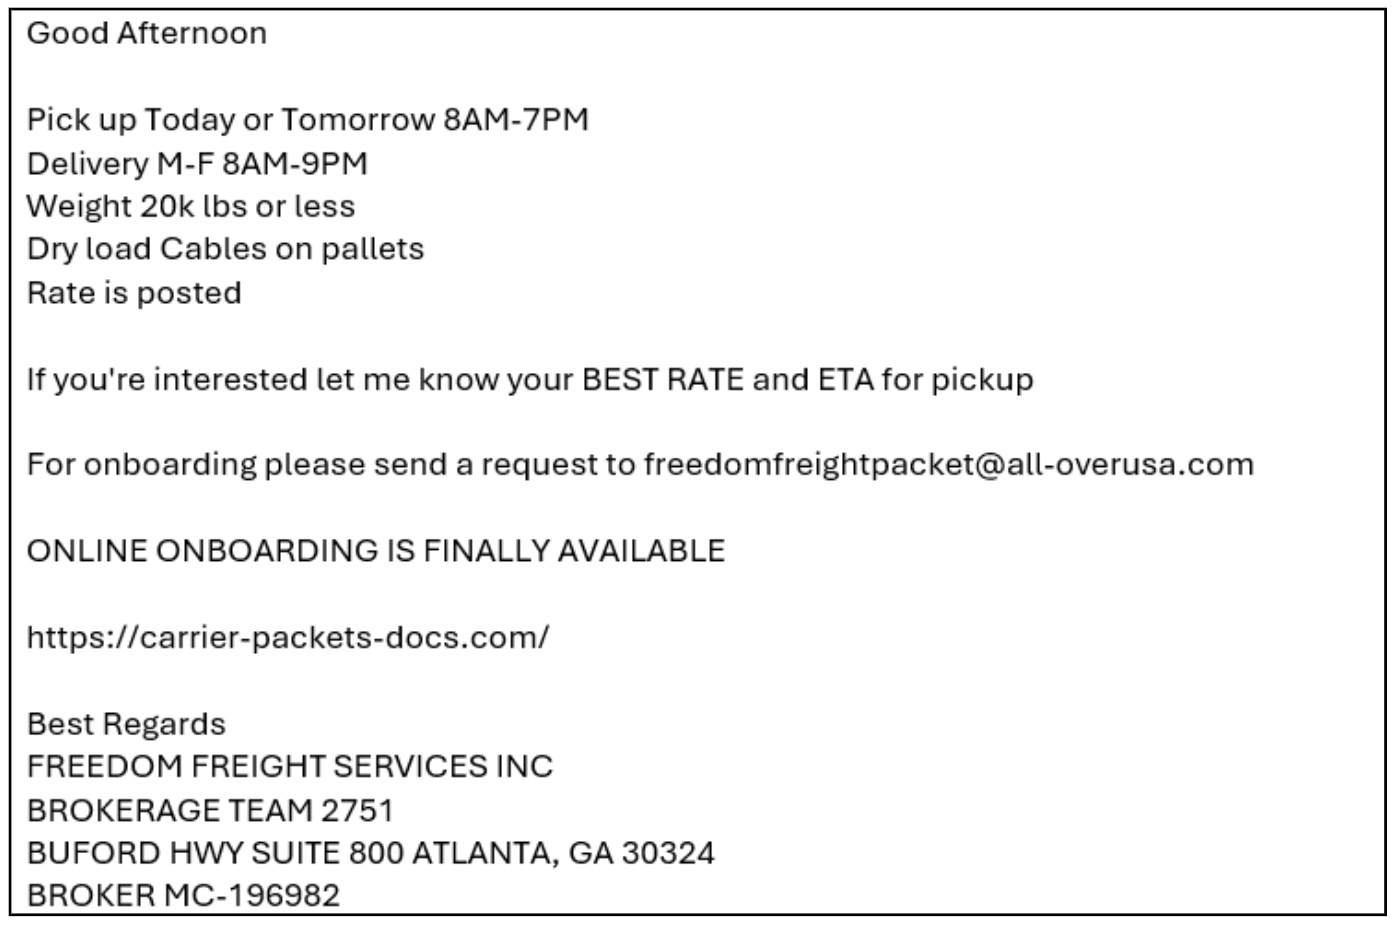
Proofpoint researchers observed crooks targeting trucking and logistics companies, running coordinated remote access campaigns to steal cargo and divert payments. These attacks appear to be linked to organized crime.
The findings highlight a growing trend of cyber-enabled cargo theft, where digital intrusions directly support real-world crime. This threat is expanding rapidly, with losses in North America reaching $6.6 billion in 2025, showing how cyberattacks are increasingly used to disrupt supply chains and generate profit.
“In late February 2026, Proofpoint researchers executed a malicious payload from a threat actor targeting transportation organizations inside a controlled decoy environment operated by our partners at Deception.pro.” reads the report published by Proofpoint. “While the environment did not represent a transportation carrier, it remained compromised for more than a month—offering rare, extended visibility into post‑compromise operations, tooling, and decision‑making.”
In November 2025, Proofpoint first reported cybercriminals were targeting trucking and logistics firms with RMM tools (remote monitoring and management software) to steal freight. Active since June 2025, the group works with organized crime to loot goods, mainly food and beverages.
Crooks infiltrate logistics firms, hijack cargo bids, and steal goods, fueling the rise of cyber-enabled freight theft.
On February 27, 2026, attackers breached a load board platform and sent emails to carriers about fake shipping jobs.

The message delivered a malicious VBS file that launched a PowerShell script, installed ScreenConnect for remote access, and showed a fake agreement to hide the attack.
After gaining access, they focused on persistence by installing multiple remote management tools. Over a month, they deployed several ScreenConnect instances along with Pulseway and SimpleHelp, ensuring continued access even if one tool was detected or removed.
The researchers reported the attackers used a new “signing-as-a-service” method to deploy a stealthy ScreenConnect instance. A PowerShell chain bypassed controls, downloaded the installer, had it re-signed with a fraudulent but valid certificate, then installed it silently. It also replaced original components with signed versions to avoid detection, bypass revoked certificates, and maintain persistent, trusted remote access.
After gaining stable access, the attacker moved to hands-on activity. They manually checked accounts like PayPal and ran a custom tool to find and steal cryptocurrency wallet data, sending results to Telegram.
They used over a dozen PowerShell scripts to profile victims, collecting user data, browser history, and signs of access to banking, payments, logistics, and accounting platforms. The scripts copied locked files, searched for valuable services, stored data in hidden folders, and ran with SYSTEM privileges.
The attacker consistently scanned browser databases, matched patterns, and reported findings via Telegram, sometimes using delayed tasks to evade controls. Targets included banks, money transfer services, fleet payment systems, and freight platforms—showing a clear focus on financial fraud and cargo theft.
In a final step, another script quietly gathered system details, checked security tools and financial apps, and sent results back through the existing remote session without raising alerts.
The intrusion shows that financially motivated attackers go far beyond initial access. They focus on staying hidden, gathering intelligence, and stealing credentials to exploit payment systems and logistics platforms—behavior that also aligns with freight theft and cargo diversion preparation.
“Notably, the use of a signing‑as‑a‑service capability underscores a growing trend toward attacker use of legitimate trust mechanisms to evade detection.” concludes the report. “For transportation, logistics, and freight organizations, these findings reinforce the importance of monitoring for unauthorized remote management tools, suspicious PowerShell activity, and abnormal browser telemetry associated with financial platform access. “
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, cargo)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。