









WP Maps Pro plugin allows WordPress site owners to embed Google Maps and OpenStreetMap with markers, listings, and location search. It’s a store locator tool. Unremarkable. The plugin is installed on over 15,000 websites, according to sale data of Envato Market. And right now, attackers are actively exploiting a critical flaw in it that lets anyone on the internet create a full administrator account on an affected site without logging in first.
The vulnerability is tracked as CVE-2026-8732 and received a CVSS score of 9.8. The root cause is a “temporary access” feature built to let plugin support staff log into a customer’s site during troubleshooting. That feature registered an AJAX action called wpgmp_temp_access_ajax using WordPress’s wp_ajax_nopriv_ hook, which means unauthenticated users can call it. The only protection was a nonce check, but the nonce itself was embedded publicly into every frontend page of the site via wp_localize_script.
“This makes it possible for unauthenticated attackers to invoke the wpgmp_temp_access_support handler with check_temp=false, which unconditionally creates a new WordPress user with the hardcoded role of administrator via wp_insert_user() and returns a magic login URL that, when visited, calls wp_set_auth_cookie() to fully authenticate the attacker as the newly created administrator, resulting in complete site takeover.” reads the report published by WordPress security firm WordPress.
The design is almost impressive in how thoroughly it fails. A nonce is meant to prevent cross-site request forgery, not control access. Using it as an authentication gate for a publicly accessible endpoint is like locking a door with a key you’ve taped to the outside.
“This is due to the wpgmp_temp_access_ajax AJAX action being registered with wp_ajax_nopriv_ and protected only by a nonce check using the fc-call-nonce nonce, which is publicly embedded into every frontend page via wp_localize_script as the nonce field of the wpgmp_local JavaScript object, rendering the check ineffective as an access control mechanism.” states the report.
Security researcher David Brown discovered and reported the vulnerability through the Wordfence Bug Bounty Program. He earned a bounty of $1,950.00 for his submission.
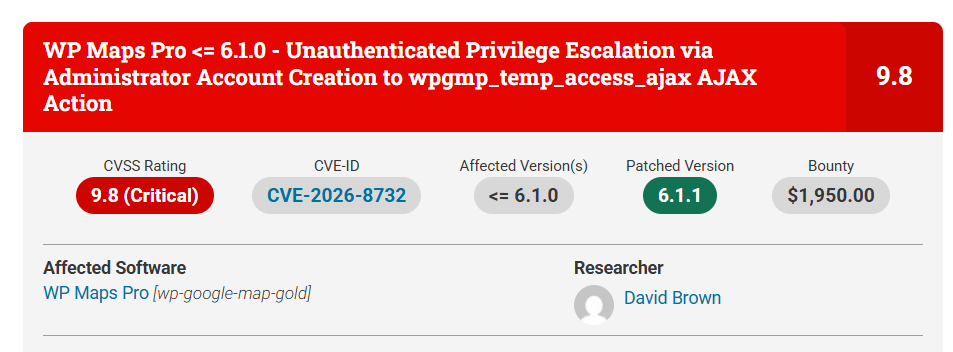
The plugin maintainers addressed the issue on May 20, 2026, with the release of version 6.1.1. The fix is straightforward: the endpoint now requires the requesting user to already be an authenticated administrator before it’ll do anything. All versions up to and including 6.1.0 remain vulnerable.
However, Wordfence researchers observed that the active exploitation started before most site owners had time to patch.
“Wordfence blocked 2,003 attacks targeting this vulnerability in the past 24 hours.” reports the cybersecurity firm.
That’s a fast ramp from disclosure to mass exploitation, which is consistent with how WordPress plugin vulnerabilities tend to move once a working proof-of-concept circulates. The attack surface is wide: 15,000 sales on Envato Market, and many WordPress site owners don’t update plugins on any predictable schedule.
If you’re running WP Maps Pro, update to 6.1.1 immediately. If you can’t update right now, deactivate the plugin entirely until you can. An attacker who’s already created an admin account on your site has full control: they can install backdoors, redirect traffic, inject malware into your pages, or simply exfiltrate whatever data the site holds. The update takes thirty seconds. The cleanup after a full site takeover does not.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, WordPress)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。