


In July 2026, Kaspersky experts detected a new attack by the Head Mare group. Previously, we classified them as hacktivists, but now we define them as an APT group due to the sophistication of their TTPs and the absence of destructive activity (encryption, wiping) in the targeted infrastructures. In this latest campaign, the attackers exploited a chain of vulnerabilities in the TrueConf video conferencing server and replaced the original TrueConf client installers with infected versions that installed the PhantomCore malware on the system.
An investigation of the compromised server revealed that the attackers used a combination of two new vulnerabilities (assigned internal identifiers KLCERT-26-057 and KLCERT-26-058), allowing them to execute arbitrary code with the highest privileges.
The attack occurs in several stages:
…\public\js\locale.php with a web shell, which can be used for subsequent remote control of the compromised server.This web shell was used for the following activities:
The vulnerabilities exploited by the attackers were patched by the vendor in the latest TrueConf Server updates (versions 5.3.9, 5.4.9, and 5.5.5). These updates were released on June 18, 2026.
The PhantomCore backdoor was successfully detected by Kaspersky solutions.
To automatically launch the malware after the system boots, a registry key is created: HKEY_CURRENT_USER\Software\Classes\CLSID\{0340F119-A598-4ed9-B0AC-6F6A12D3E755}\InprocServer32, with the value set to the path to the malicious program’s file.
Using a web shell, in addition to PhantomCore, the attackers load a backdoor that we have named PhantomGraph, consisting of two modules:
SysExcSvc.dll is responsible for receiving commands from the attackers and transmitting the results of their execution. The attackers used an account on Microsoft OneDrive cloud storage as their command-and-control (C2) server.SysReadSvc.dll reads the command transmitted by the first module, executes it, and saves the execution result.To establish persistence on the system, the attackers execute a Base64-encoded PowerShell command that installs SysExcSvc.dll and SysReadSvc.dll as Windows services. We believe the attackers deliberately split this malicious command into two components to make it harder to detect using EDR tools. Additionally, the program’s code partially matches that of PhantomCore, indicating that it belongs to the Head Mare group’s arsenal.
We also managed to identify the commands executed by the attackers when connecting to the backdoor. The SysReadSvc module executes commands using a BATCH file. Example of execution:
$system32\cmd.exe /c cmd /c ""$temp\cmd_cmd_4488.bat"" 2>&1 |
Commands detected:
lsass.exe process:
hostname whoami "$system32\WindowsPowerShell\v1.0\powershell.exe" -noexit -command Set-Location -literalPath '$system32\inetsrv' |

In addition, we discovered several commands that did not work due to the attackers’ typos and encoding issues.
We are observing several active Head Mare campaigns targeting Russian organizations across various industries: instrument manufacturing, electronics, transportation, energy,
IT, and software development. The attackers distribute their backdoors using various methods, including phishing, exploiting public web servers, or through a subcontractor.
We recommend that all organizations using TrueConf software install the latest server version (versions 5.3.9, 5.4.9, and 5.5.5) in accordance with the vendor’s recommendations.
We also recommend verifying that the client distributions downloaded from the TrueConf server used by your organization have a valid TrueConf digital signature and have not been tampered with. The malicious distributions we detected do not have a valid digital signature. You can also verify authenticity on the vendor’s website.
Important: Even if your organization does not use a TrueConf server, your employees may connect to compromised TrueConf servers belonging to business partners to participate in online meetings and download infected installation packages.
The attack mechanism and the vulnerabilities exploited will be described in more detail on the Kaspersky ICS CERT website.
Kaspersky security solutions successfully detect malicious activity associated with the attacks described above.
The malware used in this attack is detected by our solutions with the following detection names:
Let’s take a closer look using Kaspersky Endpoint Detection and Response Expert (KEDR Expert) as an example.
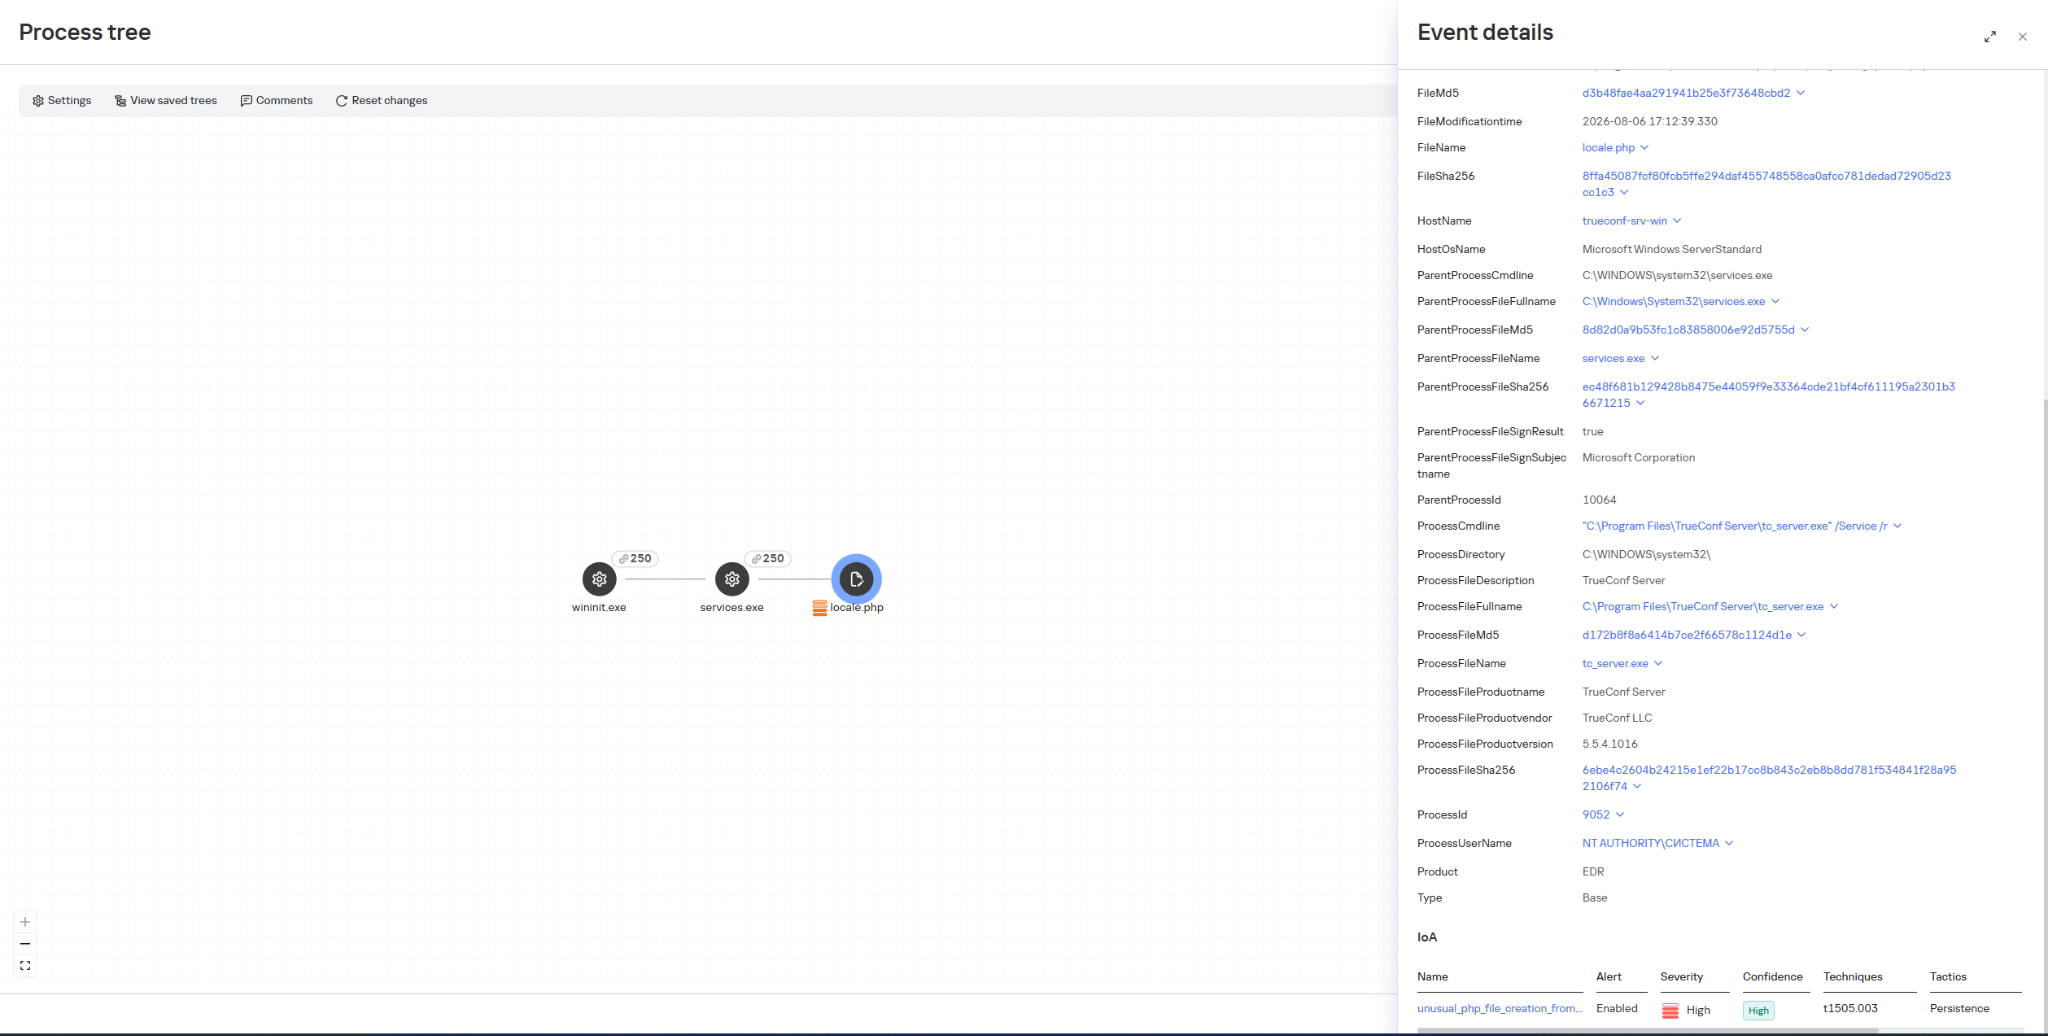
Specifically, activity involving the replacement of the legitimate file …\public\js\locale.php with a web shell, as well as the deletion of entries from TrueConf event logs, is detected by the rule unusual_php_file_creation_from_trueconf_process.
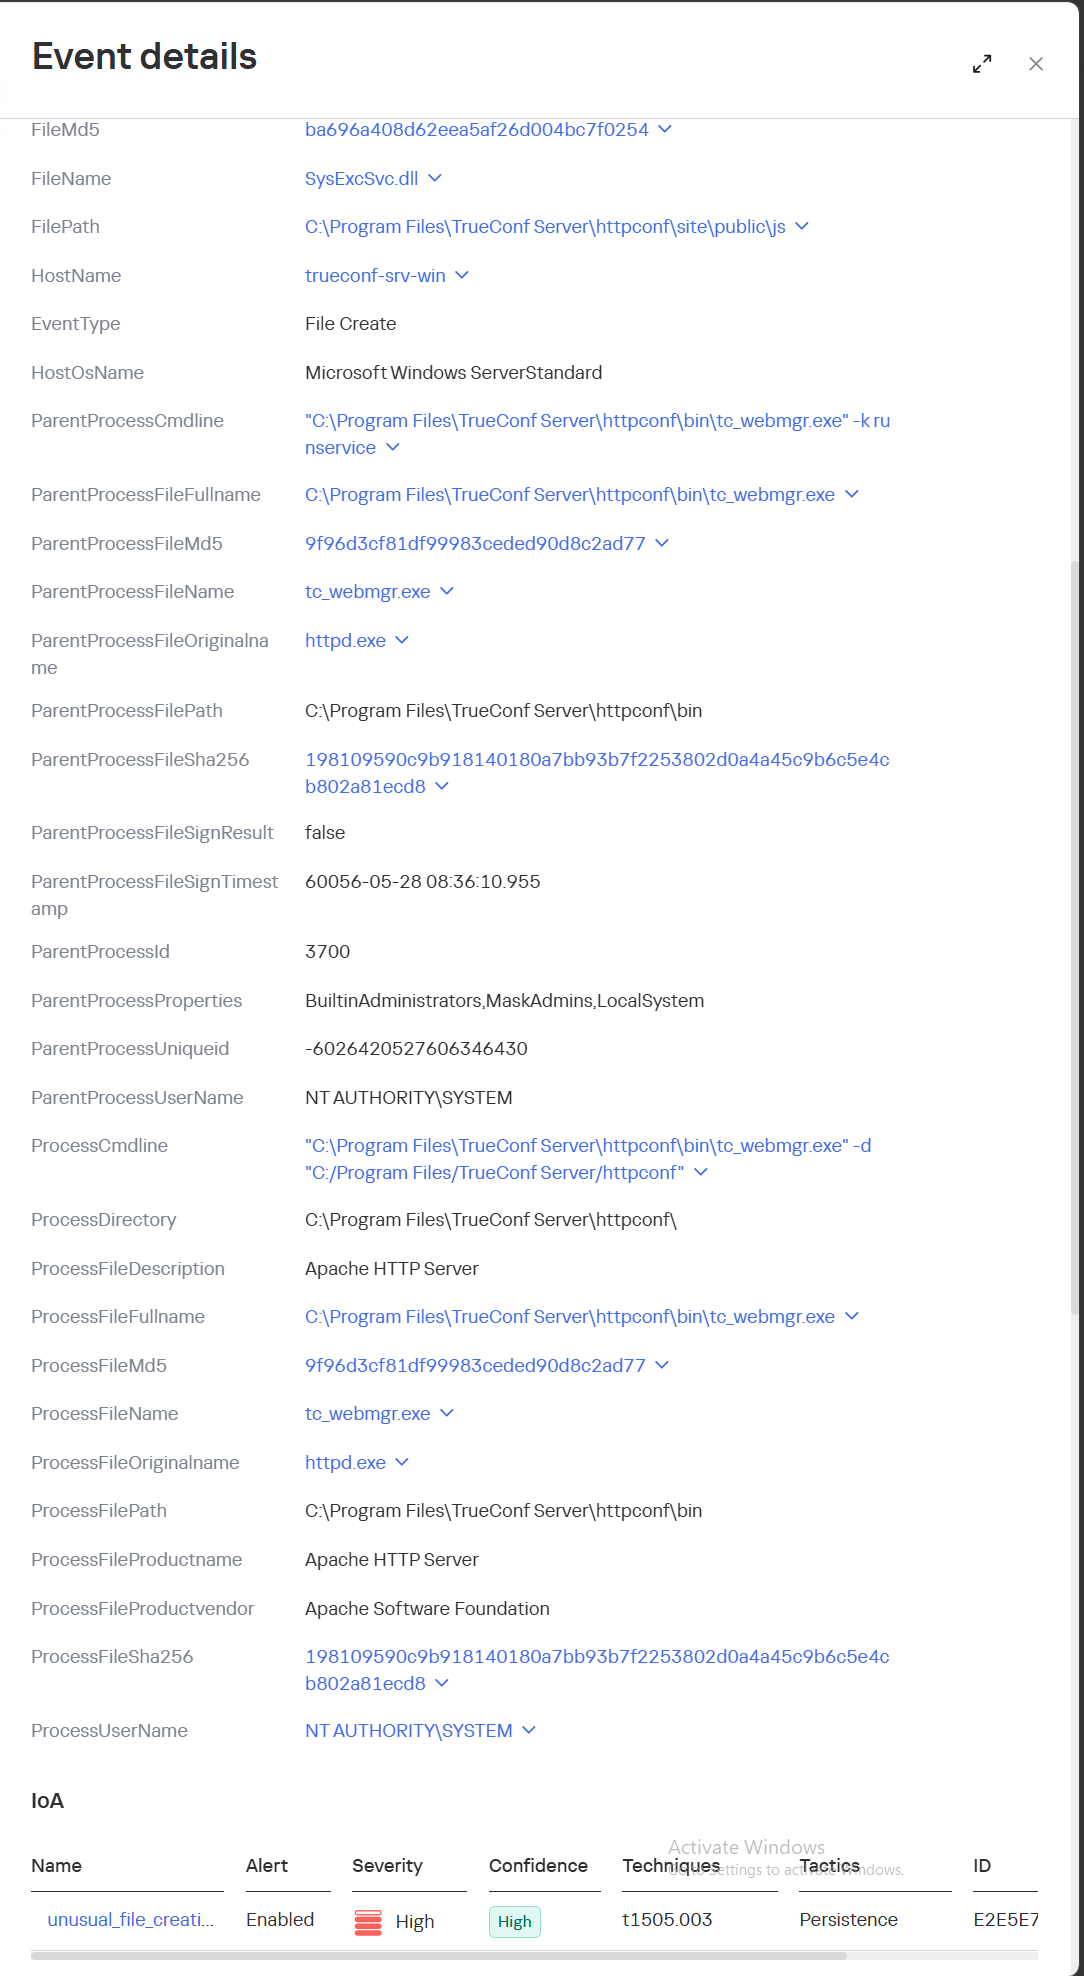
Downloading a file containing the PhantomCore backdoor via the replaced legitimate file …\public\js\locale.php is detected by KEDR Expert with the rule unusual_file_creation_from_trueconf.
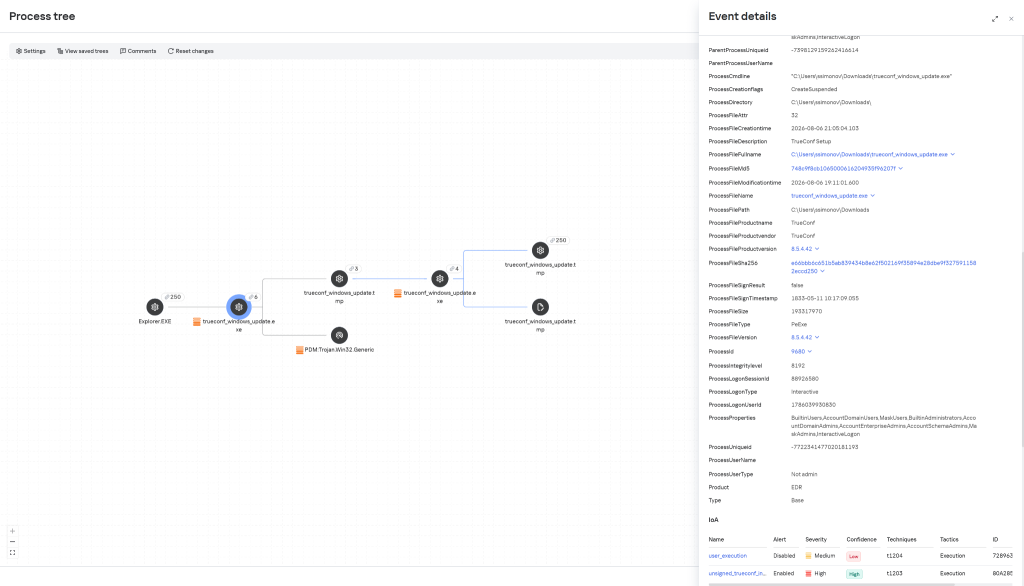
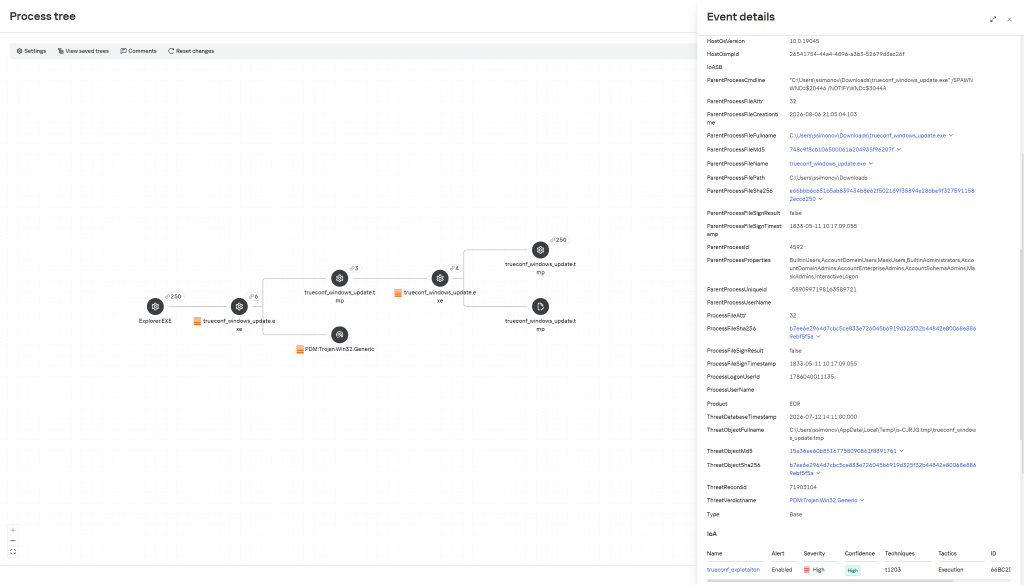
Activity related to the installation of an infected TrueConf client installer containing the PhantomCore backdoor is detected by KEDR Expert using the unsigned_trueconf_installer rule.
The Kaspersky Managed Detection and Response service detects the described attack by monitoring the following actions:
lsass.exe process.lsass.exe process using the comsvcs.dll library.lsass.exe process.To protect companies using our Kaspersky SIEM system, a general set of rules is available in the product repository that allows detection of the following techniques:
lsass.exe process using the comsvcs.dll library:lsass.exe process:We also recommend paying attention to the following events when developing your own detection rules or conducting threat hunting:
(DeviceEventClassID = '4657' OR DeviceEventClassID = '13') AND FileName like '%\Software\Classes\CLSID\{0340F119-A598-4ed9-B0AC-6F6A12D3E755}%' AND DeviceCustomString6 = 'InprocServer32' |
SysExcSvc and SysReadSvc services to run executables from temporary directories in the background via cmd:DeviceEventClassID = '4697' AND (DestinationServiceName = 'SysExcSvc' OR DestinationServiceName = 'SysReadSvc') AND match (FileName, '.*cmd\s+\/c.*temp\\cmd_cmd_.*\.bat.*') |
(DeviceEventClassID = '4688' OR DeviceEventClassID = '1') AND SourceProcessName LIKE '%\trueconf_windows_update.exe' |
For the detection rules to work correctly, ensure that events from Windows systems are received in full, including Security events 4688, 4663, 4657, 4697 and Sysmon events 1, 7, 11, 13.
Web shell
4d27b4eb1c5dbb3d8160f29b8119523e locale.php
Infected installer
748c9f8cb1065000616204935f96207f trueconf_windows_update.exe
PhantomCore DLL
c5a460e4e68a088f6e51b2c6474642ec
129462164a7d52e9ea8560b60f0412c5 doc.txt
ec0bf4a2186a88874e9f26f07cfeb532 usocacheddata.txt
b348642146ea34771e5785c5857950f5
c915cb6c2aeb863ee8479238e1644217 doc.txt
0e79996d9483d1e44fea32b0a48c2c19 doc.txt
2bb75c20e778eb5c416965bd4d4259b1 trueconf_windows_client_x64_[redacted].exe
b3a6fee3307f1c26841fd5c603e2b013 usocacheddata.txt
8fcc3e4ccbf1725d9989fb464abf3561 usocacheddata.txt
PhantomGraph
489f43be558b2679284ceabed7adc4f3 sysexcsvc.dll
dd1fd2b459b97b7d59375cb8383cd19a sysreadsvc.dll
0e4541c3153ec5ed01497f19cf4f63d0 sysexcsvc.dll
12d4e8f5295f2ef7e0f9bfc0f4830939 sysexcsvc.dll
7f267006cac10f341c356b62fe493527 sysexcsvc.dll
ee2861d5965e8730708cd1da8a93fa4c sysexcsvc.dll
Backdoor (ELF)
c3a2abe8756910f42582b04a44ea3514
43f435c3c437bc879a2d7d4634f43494
Rootkit
aee9642b45b099cb7f3053b9b680b425
81.177.32[.]12
194.87.239[.]71 ssh
194.87.93[.]153 ssh
38.244.205[.]244
31.59.102[.]61
penzadogshelter[.]site
trendy-market[.]site
bright-deals[.]site
nova-stream[.]site
rinomobile[.]ink
urbanpixel[.]store
flexish[.]shop
media-hub[.]today
cosmetic-deals[.]store
vks.gossopka[.]forum
SysExcSvc
SysReadSvc
C:\Windows\System32\inetsrv\SysExcSvc.dll
C:\Windows\System32\inetsrv\SysReadSvc.dll
C:\Windows\System32\inetsrv\graphi-refresh.dat
C:\Windows\System32\inetsrv\share\input_*.txt
C:\Windows\System32\inetsrv\share\output_*.txt
%TEMP%\cmd_cmd_*.bat
%LOCALAPPDATA%\TrueConf\Client\api-ms-win-crt-time-l1-1-0-2.dll
/etc/systemd/system/omicluster.service
/etc/systemd/system/schedul2-bin.service
/opt/acronis/bin/schedul2-bin
/omi/bin/omicluster
/usr/lib64/libzvbi-tchain.so.2
/var/tmp/cx2
HKEY_CURRENT_USER\Software\Classes\CLSID\{0340F119-A598-4ed9-B0AC-6F6A12D3E755}\InprocServer32
Backdoor.PHP.WebShell.abi
Backdoor.Win64.PhantomCore.dt
Trojan.Win64.Agent.smgvnc
Trojan.Win64.Agent.smgvnb
HEUR:Backdoor.Win64.PhantomCore.gen
HEUR:Backdoor.Linux.Agent.fb
HEUR:Backdoor.Linux.PhantomHook.a
HEUR:Backdoor.Linux.PhantomReact.a
Trojan.Win64.PhantomGraph.gen
UDS:Backdoor.Win64.PhantomCore.a
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 |
import "pe" rule apt_HeadMare_PhantomCore { meta: description = "Rule to detect PhantomCore used by HeadMare" author = "Kaspersky ICS CERT" copyright = "Kaspersky ICS CERT" version = "1.0" last_modified = "2026-08-02" hash = "c5a460e4e68a088f6e51b2c6474642ec" strings: $a1 = "lying.dll" ascii $a2 = { 2D 7F 95 4C 2D F4 51 58 } $a3 = { 4F 81 67 F7 7E 7B 05 14 } condition: (uint16(0) == 0x5A4D) and (filesize > 4MB) and (filesize 20MB) and (all of them) and (pe.number_of_signatures == 0) } |
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 |
rule apt_HeadMare_FakeConf_installer { meta: description = "Rule to detect any unsigned TrueConf installers" author = "Kaspersky" copyright = "Kaspersky" version = "1.0" last_modified = "2026-08-02" hash = "748c9f8cb1065000616204935f96207f" strings: $a1 = "TrueConf Setup" wide $a2 = "This installation was built with Inno Setup." wide condition: (uint16(0) == 0x5A4D) and (filesize > 20MB) and (all of them) and (pe.number_of_signatures == 0) } |
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 |
rule apt_HeadMare_PhantomCore_exchange { meta: description = "Rule to detect PhantomCore exchange module used by HeadMare" author = "Kaspersky ICS CERT" copyright = "Kaspersky ICS CERT" version = "1.0" last_modified = "2026-08-02" hash = "489f43be558b2679284ceabed7adc4f3" strings: $a1 = "graphi_exchange.dll" ascii $a2 = "graphi-client/1.0" ascii $b1 = "https://graph.microsoft.com/v1.0/me/drive/root:/" ascii $b2 = ":/children?$select=name,id&$top=200" ascii $b3 = "offline_access Files.ReadWrite" ascii $b4 = "GRAPHI_INSECURE" ascii $b5 = "\"@microsoft.graph.conflictBehavior\":\"replace\"}" ascii $b6 = "https://login.microsoftonline.com/" ascii condition: (uint16(0) == 0x5A4D) and (any of ($a*)) and (3 of ($b*)) } |
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 |
rule apt_HeadMare_PhantomCore_executor { meta: description = "Rule to detect PhantomCore executor module used by HeadMare" author = "Kaspersky ICS CERT" copyright = "Kaspersky ICS CERT" version = "1.0" last_modified = "2026-08-02" hash = "dd1fd2b459b97b7d59375cb8383cd19a" strings: $a1 = "graphi_reader.dll" ascii $a2 = "^input_(.+)\\.txt$" ascii $b1 = "output_" ascii $b2 = "cmd_cmd_" ascii $b3 = "cmd /c \"\"" ascii $b4 = "error: failed to start cmd process" ascii $b5 = "share" ascii $b6 = "SysReadSvc" ascii condition: (uint16(0) == 0x5A4D) and (filesize < 4MB) and (any of ($a*)) and (4 of ($b*)) } |
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 |
rule apt_HeadMare_FakeLocale_webshell { meta: description = "Rule to detect the HeadMare TrueConf web shell" author = "Kaspersky" copyright = "Kaspersky" version = "1.0" last_modified = "2026-08-04" hash = "4d27b4eb1c5dbb3d8160f29b8119523e" strings: $a1 = "X-Redirect-Bit" ascii wide nocase $a2 = "tc_vcs_web_db_conn" ascii wide $a3 = "user=postgres" ascii wide $b1 = "UPL ok::" ascii wide $b2 = "DWN fail nexs" ascii wide $b3 = "DWN fail inv" ascii wide condition: (2 of ($a*)) or (2 of ($b*)) } |
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 |
rule apt_HeadMare_TrueConf_Rootkit { meta: description = "Rule to detect the HeadMare rootkit installed on TrueConf servers" author = "Kaspersky" copyright = "Kaspersky" version = "1.0" last_modified = "2026-08-06" hash = "aee9642b45b099cb7f3053b9b680b425" strings: $a1 = "PQconnectdb" $a2 = "obfuscated_data" $a3 = "install_hook" condition: (uint32(0) == 0x464c457f) and (filesize < 400000) and (all of them) } |
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 |
rule apt_HeadMare_Github_Backdoor { meta: description = "Rule to detect the HeadMare backdoor with Github C2" author = "Kaspersky" copyright = "Kaspersky" version = "1.0" last_modified = "2026-08-06" hash = "43f435c3c437bc879a2d7d4634f43494" hash = "c3a2abe8756910f42582b04a44ea3514" strings: $a1 = "cryptor5crypt" $a2 = "execraw_task" $a3 = "jitter_task" $a4 = "upload_task" $a5 = "exec_task" $a6 = "react_comment" condition: (uint32(0) == 0x464c457f) and (filesize > 5000000) and (filesize < 10000000) and (4 of them) } |
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。