





Organizations evaluating Managed Detection and Response (MDR) are now looking well beyond the table stakes of 24x7 detection and response. They are increasingly asking new questions of service providers, and they go something like this:
These questions reflect a fundamental shift in what organizations expect from MDR.
Recent research about digital sovereignty reveals how significant the issue has become. In the 2026 Bitdefender Cybersecurity Assessment, 77% of IT and cybersecurity professionals said data sovereignty is becoming increasingly important in cybersecurity purchasing decisions, and a nearly identical number (76%) said they would consider switching cybersecurity vendors because of concerns about data sovereignty, jurisdiction, or foreign government access to their data.
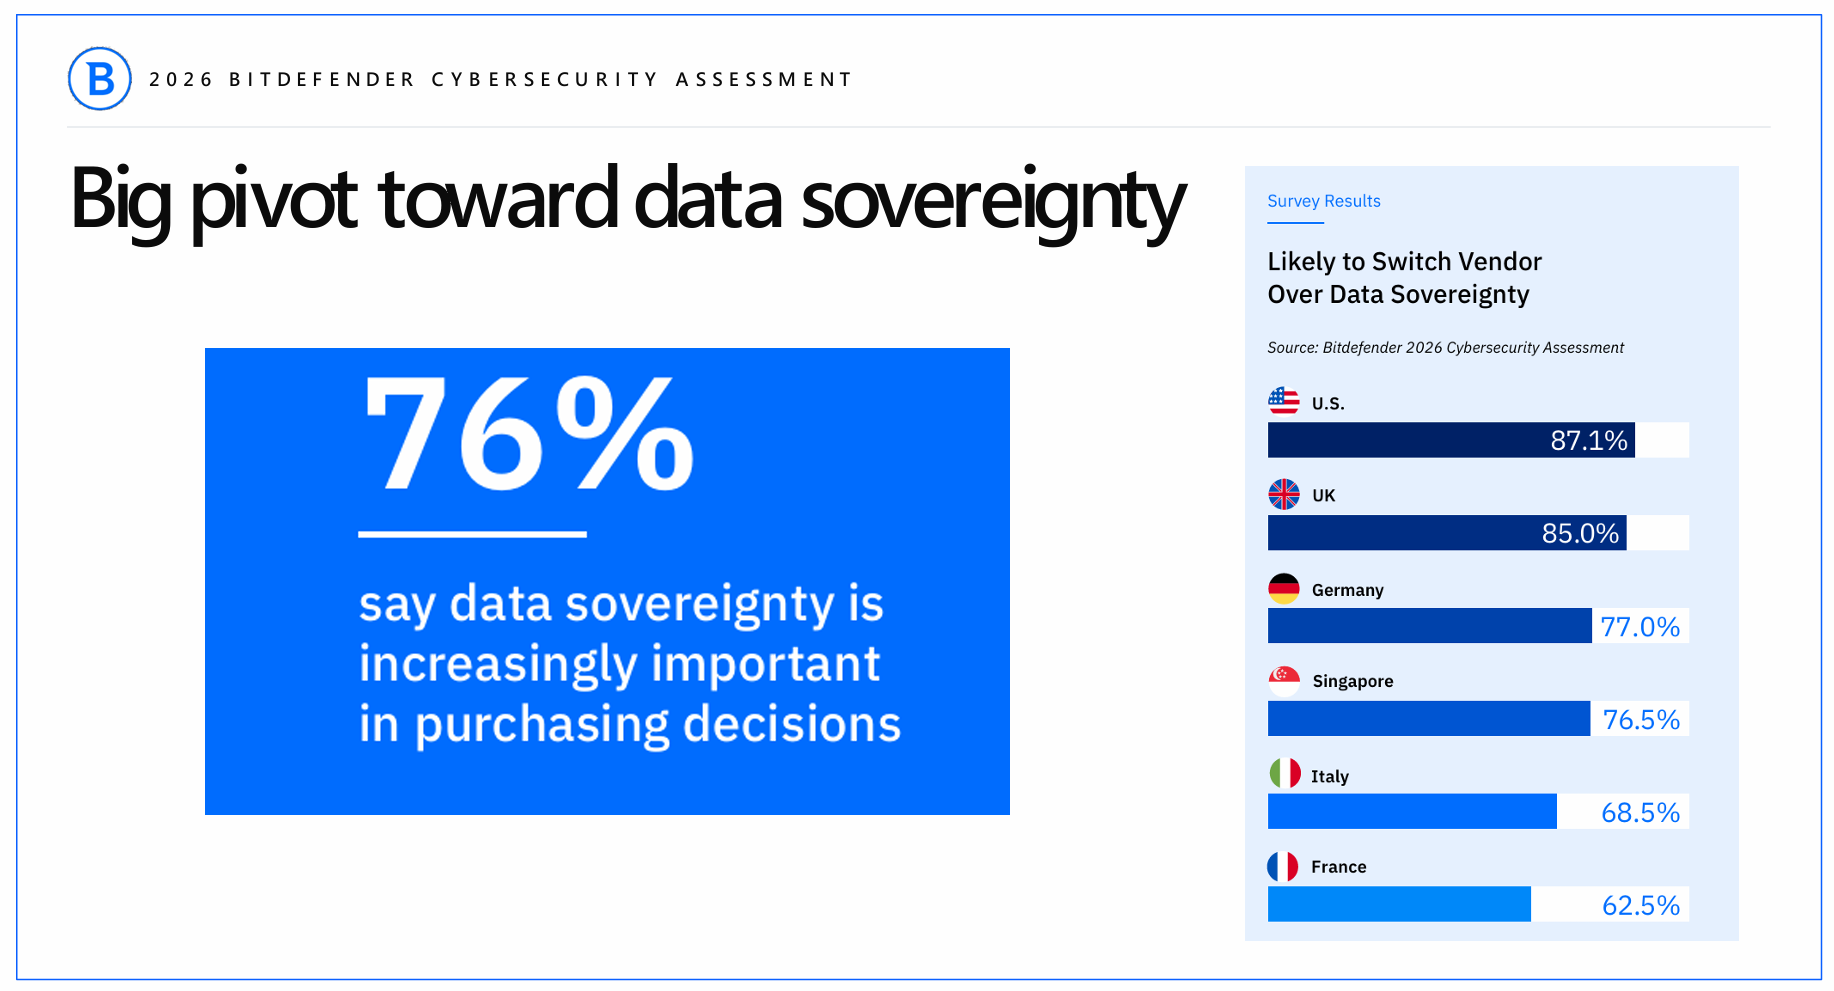
Sovereignty is now a deciding factor.
The evolution of digital sovereignty extends well beyond where a platform is hosted and is redefining trust in cybersecurity.
As an IDC Market Note recently observed:
"Questions have moved from 'Where is the platform hosted?' to 'Who governs it, and from where, and which foreign government can legally impose its will on providers of our critical technology?'"
Organizations increasingly want assurance that the people investigating incidents, the systems processing telemetry, and the engineering teams building detections all operate within the legal and operational framework they must trust.
As a European cybersecurity company founded and headquartered in Romania, Bitdefender has spent more than two decades helping organizations protect critical environments across Europe and around the world.
Now, with digital sovereignty a strategic priority, we believe sovereignty cannot stop at where customer data is stored. It must extend across the entire security operation, and that thinking is reflected in the Bitdefender EU Sovereign MDR operating model for European organizations.
Every stage of service delivery—from continuous monitoring and threat investigation to malware analysis, detection engineering, platform engineering, and incident response—remains within the European Union.
For organizations balancing security, compliance, and trust, this represents a fundamentally different approach to MDR.
Sovereignty alone, however, is not enough. Your MDR provider must also be able to respond on your behalf, to stop attacks before they become large-scale breaches or deploy ransomware.
That requires more than keeping operations within a sovereign environment. It requires experienced analysts, proven operational processes, integrated technology, and years of real-world incident response expertise.
The Bitdefender MDR team has been protecting organizations across Europe for years, continuously refining its capabilities. Our new EU Sovereign MDR service builds on that operational foundation, delivering the same mature 24×7 detection and response capabilities within a fully sovereign operating model designed to meet the evolving needs of organizations across the European Union.
Bitdefender was recently positioned as a Major Player in the IDC MarketScape for Worldwide Managed Detection and Response Service for Midmarket 2026 Vendor Assessment.
The IDC MarketScape highlighted an architectural strength that we believe increasingly differentiates modern MDR:
"Bitdefender's MDR offering is built natively on the GravityZone EDR/XDR platform, a vertically integrated security architecture that unifies prevention, detection, response, and risk visibility within a single technology stack."
We believe this reflects an important evolution in how MDR should operate. Rather than treating detection, response, threat research, engineering, and prevention as separate functions, they operate together as one continuously improving system integrating both AI and human expertise.
Today, AI-enabled attacks operate at machine speed. Living-off-the-Land (LOTL) techniques abuse legitimate tools already present inside environments. Attackers increasingly move across endpoints, cloud workloads, identities, and collaboration platforms without relying on traditional malware.
Responding effectively now requires far more than watching alerts. It requires contextual visibility, integrated threat intelligence, machine-speed analysis, and experienced analysts who can make complex decisions under pressure.
Organizations increasingly expect AI to accelerate investigations—but not replace human judgment. While machine speed is valuable, human accountability remains essential. The strongest MDR services combine both to create a continuous feedback loop you can trust.
The cybersecurity industry is approaching another inflection point. Yesterday's question was whether your MDR provider could respond around the clock.
Today's questions are about who operates that response, under whose laws it is governed, and how AI and human expertise work together in the MDR SOC.
If your organization is evaluating how to strengthen security operations without sacrificing governance or compliance, now is the time to explore what sovereign MDR can deliver—and why trusted operations are becoming as important as continuous protection itself.
IDC Market Note: Bitdefender and OVHcloud Join Forces with European Sovereign Cybersecurity Platform Offering (Doc #EUR254251926, February 2026)
IDC MarketScape: Worldwide Managed Detection and Response Service for Midmarket 2026 Vendor Assessment (Doc #US52992326, July 2026).
About IDC MarketScape: IDC MarketScape vendor assessment model is designed to provide an overview of the competitive fitness of technology and service suppliers in a given market. The research utilizes a rigorous scoring methodology based on both qualitative and quantitative criteria that results in a single graphical illustration of each supplier's position within a given market. IDC MarketScape provides a clear framework in which the product and service offerings, capabilities and strategies, and current and future market success factors of technology suppliers can be meaningfully compared. The framework also provides technology buyers with a 360-degree assessment of the strengths and weaknesses of current and prospective suppliers.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。