



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

I
InfoQ
博客园_首页
美团技术团队
M
MIT News - Artificial intelligence
人人都是产品经理
人人都是产品经理
Blog — PlanetScale
Blog — PlanetScale
H
Help Net Security
J
Java Code Geeks
T
Tailwind CSS Blog
Jina AI
Jina AI
量子位
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
G
Google Developers Blog
爱范儿
爱范儿
Cyber Security Advisories - MS-ISAC
宝玉的分享
宝玉的分享
小众软件
小众软件
MongoDB | Blog
MongoDB | Blog
博客园 - 三生石上(FineUI控件)
L
LangChain Blog
酷 壳 – CoolShell
酷 壳 – CoolShell
V
Visual Studio Blog
博客园 - Franky
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知

Hackread – Cybersecurity News, Data Breaches, AI and More

Suspected Cyberattack Sends Fake Emergency Alert to Phones Across Brazil Operation Endgame Disrupts StealC, Amadey and SocGholish Malware Networks New GhostShell Hacking Group Targets Ukraine’s Drone Defense Sector Fake npm Packages Impersonate PostCSS Tool to Steal Chrome Passwords Best Crypto Payment Solutions for E-Commerce Businesses Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity LastPass Confirms Customer Data Breach After Klue OAuth Token Theft ‘Cordyceps’ CI/CD Flaw Exposes Microsoft, Google, Apache Repos to Pipeline Hijacking The Rise of AI-Powered Academic Fraud: Beyond Traditional Plagiarism New CryptoBandits Malware Uses USB Drives and Tor to Steal Crypto The Evolution of iGaming Fraud: What Security Teams Should Expect in 2027 2 Scattered Spider-Linked Hackers Plead Guilty Over £39M TfL Cyberattack Beats Studio Buds Flaw Could Let Nearby Attackers Eavesdrop on Users Threat Hunting Beyond Alerts: Finding the Activity Detection Misses Scammers Use Fake GitHub Stars, VirusTotal Reviews to Spread Crypto Clipper Salesforce Disables Klue Integration After OAuth Token Theft Hits Customer Data MDR Provider Comparison: Time to Discover and Respond to Threats Meteor 3.0 Migration Helped Rocket.Chat Move Off End-of-Life Node.js Runtime Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections Nintendo America Employee Data Exposed After Shadowbyt3$ Targets TinyPulse eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks FIFA World Cup 2026: Hackers Target Football Fans With Fake Tickets Sites MacBook Neo vs Windows Laptops for Cybersecurity Tasks Operation Endgame Disrupts SocGholish Malware Infrastructure What Businesses Should Know Before Migrating Their CMS DragonForce Ransomware Abused Microsoft Teams to Hide Malware Activity Agentjacking: Researchers Show How One Fake Bug Report Can Hijack AI Coding Agents FortiBleed Attack Exposes Fortinet Firewall Credentials in 194 Countries SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Fake Search Clicks
Texas Parks and Wildlife Data Breach Affects Over 3M Lice...
Deeba Ahmed · 2026-06-22 · via Hackread – Cybersecurity News, Data Breaches, AI and More

More than three million people who bought hunting and fishing licenses in Texas are facing a range of risks due to a data breach, which is being dubbed one of the biggest cyberattacks reported in the state this year.

According to an official data security incident notification released by the department, on June 18, hackers targeted the computer systems of a third-party vendor that sells these licenses for the Texas Parks and Wildlife Department (TPWD). The incident is currently being investigated by a state security team called the Texas Cyber Command.

What Data Was Taken?

Reportedly, an unauthorised actor managed to infiltrate the vendor’s private network, and could’ve gotten away with personal details like email addresses, phone numbers, home addresses, driver’s licence details, and passport numbers.

However, the TPWD has confirmed that the hackers didn’t manage to steal highly sensitive data. This means Social Security numbers, birthdays, and banking details like credit cards are completely safe.

Also, there is no evidence that children under 18 years old were involved. This could be because the hackers didn’t seem to focus on any specific group of people. Even some of the department’s own workers had their details stolen because they hunt and fish too.

“We recognise the seriousness of this issue and have identified and implemented additional security options to better protect customer information,” TPWD officials stated.

The Hacker Behind the Breach

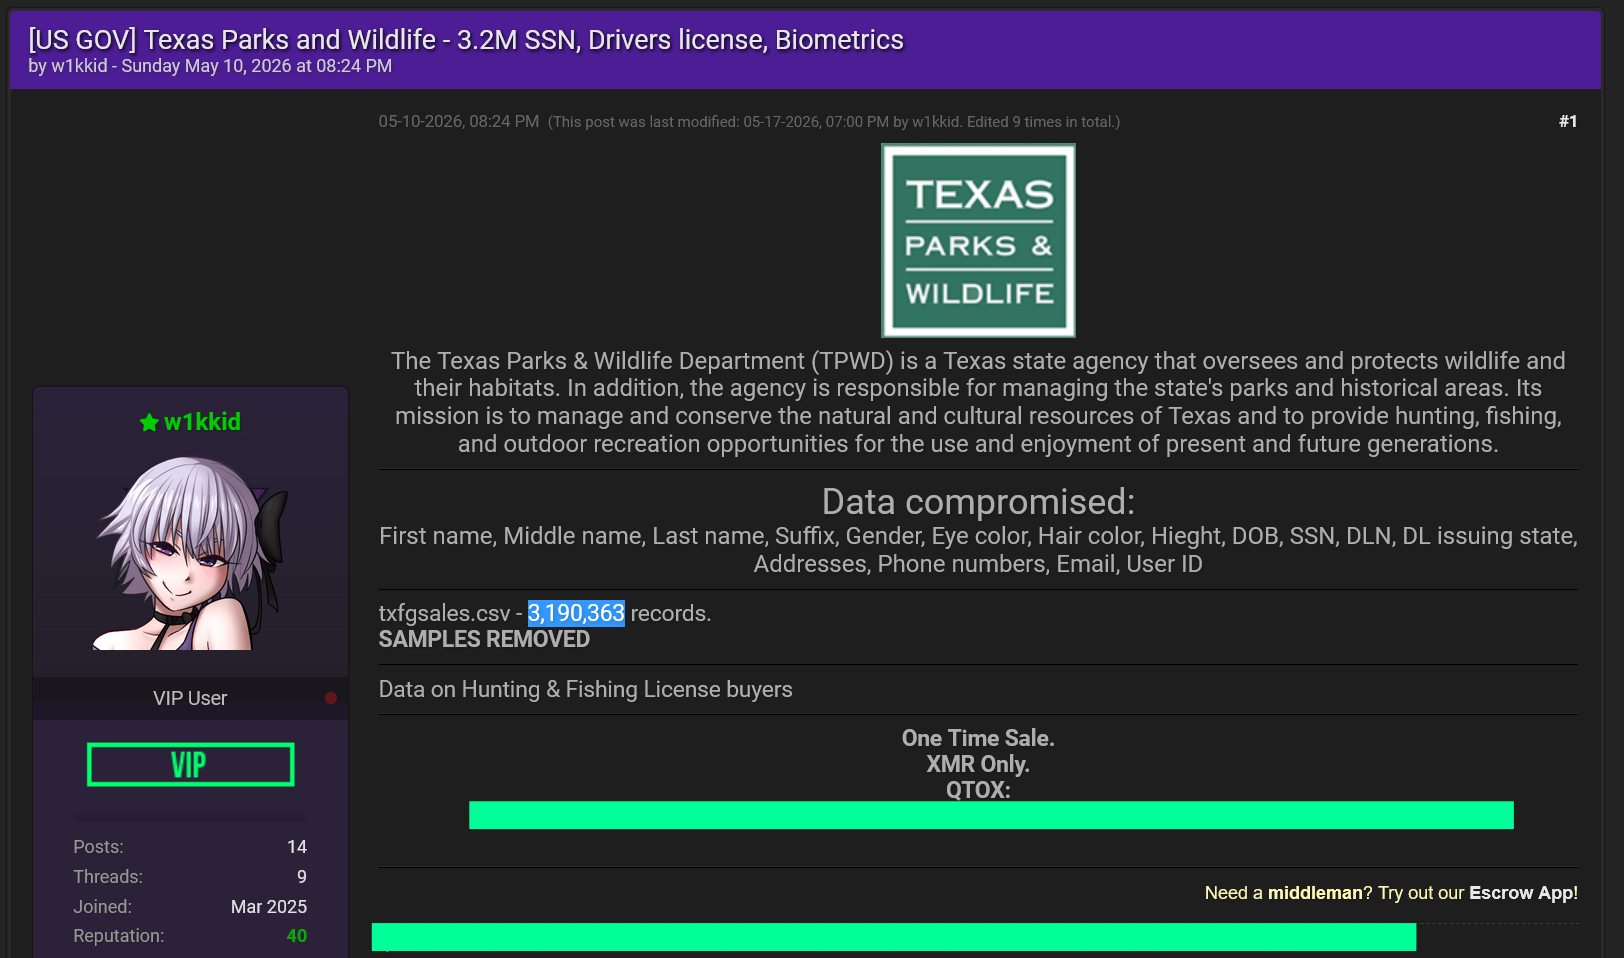
Hackread.com also found a listing on a cybercrime forum where a user using the handle w1kkid claimed responsibility for the Texas Parks and Wildlife data breach and offered the alleged database for sale in Monero (XMR).

The post claimed the dataset contained 3,190,363 records linked to hunting and fishing license buyers and listed fields such as names, addresses, phone numbers, email addresses, driver’s license details, and other personal attributes.

The listing was later updated to indicate that the data had been sold, though TPWD’s official notice says Social Security numbers, dates of birth, and financial information were not obtained in the incident.
Texas Parks and Wildlife Data Breach Affects Over 3M License Customers
Image credit: Hackread.com)

Changing the Security Systems

The state agency hasn’t yet shared the hacked third-party vendor’s name or exactly who hacked it, or the specific attack method used in the breach.

However, the agency is changing how its data is viewed to make things safer. They are improving access control measures on customer profiles and will monitor their computer networks much more closely. People can still buy their hunting and fishing licences as usual. The next sales are due to start this August.

How to Protect Yourself

The department is working with a security firm called Kroll to help the affected people and is offering Texas residents a full year of free credit monitoring to help them monitor their financial records for suspicious changes. Interested individuals need to sign up by September 14, 2026.

For staying safe, a good option is freezing your credit with the main credit agencies like Equifax, Experian, and TransUnion. It is free and can stop scammers from opening new bank accounts using your name. Lastly, always check your bank statements and never click on strange links in emails.