





Meta has disclosed a security incident involving an Instagram account recovery tool after attackers used a flaw to send password reset links to email addresses that were not connected to the targeted accounts.
According to a data breach notice filed with the Maine Attorney General’s Office, Meta Platforms said the issue affected 20,225 people in total, including 30 Maine residents. The incident occurred on April 17, 2026, and was discovered by Meta on May 31, 2026.
The problem involved Instagram’s “High Touch Support” system, an AI-assisted account recovery tool built to help users regain access when locked out of their accounts. As part of that process, users could request a password reset link by providing an email address.
Meta said the support tool itself functioned as designed, but a bug in a separate code path caused a serious validation failure. The system did not properly confirm that the email address entered during the recovery process matched the email address already linked to the Instagram account.
Because of that error, an unauthorized person could request a password reset for someone else’s Instagram account and have the reset link sent to an email address they controlled. If the targeted account did not have two-factor authentication enabled, the attacker could reset the password and access the account.
Meta said it is not aware of exactly what personal information was viewed. Still, the company listed several categories of account data that may have been accessible, including email addresses, phone numbers, dates of birth, profile information, posts, photos, videos, stories, direct messages, account activity, interaction history, and connected accounts or linked services.
The 30 Maine users identified in the filing were described as people whose passwords were reset through the support tool, who did not have two-factor authentication enabled, and whose Instagram accounts were likely accessed by an unauthorized party. Meta also said that the number is an upper limit because some of the account activity may have been carried out by legitimate account owners.
After finding the flaw, Meta said it disabled the AI-assisted support tool on the same day and invalidated all existing password reset links generated through the vulnerable path. The company also placed affected accounts behind a mandatory security checkpoint, requiring users to authenticate before regaining access.
Meta also said impacted users are being instructed to reset their passwords and re-authenticate through secure channels. The company also plans to notify affected users electronically on June 19, 2026, and recommend that they review account security settings and turn on two-factor authentication.
Before the tool is brought back, Meta said it will fix the authentication check in the Instagram recovery flow so that password reset requests are verified against existing account information. The company also said it is reviewing similar recovery flows on Meta platforms to look for related issues.
The Maine filing gives May 31, 2026, as the date Meta discovered the Instagram recovery tool vulnerability. Yet the disclosure arrives during a difficult week for Instagram’s account recovery systems.
On June 1, hackers abused Meta’s AI support bot to hijack major Instagram accounts, including the archived Barack Obama White House account, Sephora, and John Bentivegna, the Chief Master Sergeant of the U.S. Space Force. Those reports described attackers using Meta’s support automation to push through account recovery requests on accounts they did not own.
A few days later, another password reset problem was reported. On June 6, an Instagram glitch exposed full contact details for high-profile users through the password reset flow, including email addresses and a phone number linked to Meta CEO Mark Zuckerberg.
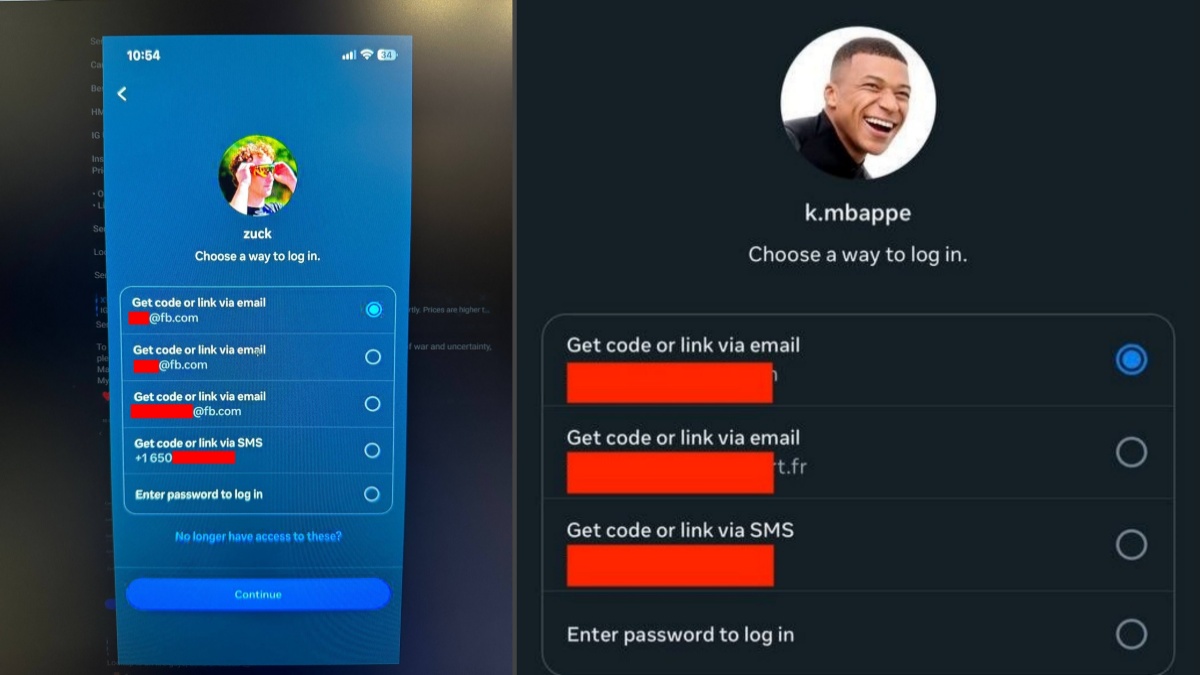
Meta’s Maine notice does not say these later reports were part of the same incident. The filing is limited to the AI-assisted High Touch Support recovery tool and the 20,225 users whose accounts may have been affected through that path.
Nevertheless, Instagram users concerned about account security should review recent login activity, remove unfamiliar linked accounts, update their password, and enable two-factor authentication using an authenticator app or security key where available.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。