










A new attack discovered by the cybersecurity firm Check Point shows how far hackers will go to make their malware look popular and safe. According to researchers, a single threat actor operating under the handle @JoseCmanXD has successfully manipulated multiple online platforms to promote a dangerous clipper designed to steal cryptocurrency.
A clipper is malware that hijacks the clipboard. When someone copies a cryptocurrency wallet address, the malware swaps it with the attacker’s wallet address before the victim pastes it. If the victim does not notice the change, their crypto payment goes to the hacker instead.
The operation targets crypto owners and gamblers seeking quick profits through fake utilities such as Solana sniper bots, crash-game predictors, and an “Aviator Predictor.” Instead of hiding, the hacker acted like a marketer to build a fake reputation.
Further investigation revealed the attacker used ghost networks of fake accounts to inflate metrics. On GitHub, linked developer accounts like Decryptor-j and crash-predictor1 gave repositories over 140 stars, pushing downloads past 5,000.
On SourceForge, a web service that provides a centralized software discovery platform, the download counter was pumped over 44,000. To maximize credibility, the scammers used a YouTube channel with realistic desktop tutorials, pairing computer-generated AI narrators with fake views and coordinated positive comments.
The most worrying part of this campaign is how it abused trusted security platforms. Researchers said the threat actor used fake VirusTotal accounts to post positive votes and comments claiming the files were clean. VirusTotal is widely used by security teams to check suspicious files and links. Combined with malware that antivirus tools failed to detect, those fake signals created a false sense of safety.
The scammers even managed to get promotional articles published on legitimate news websites on 27 April, alongside posts on popular crypto forums like BitcoinTalk, giving their trap ultimate credibility.
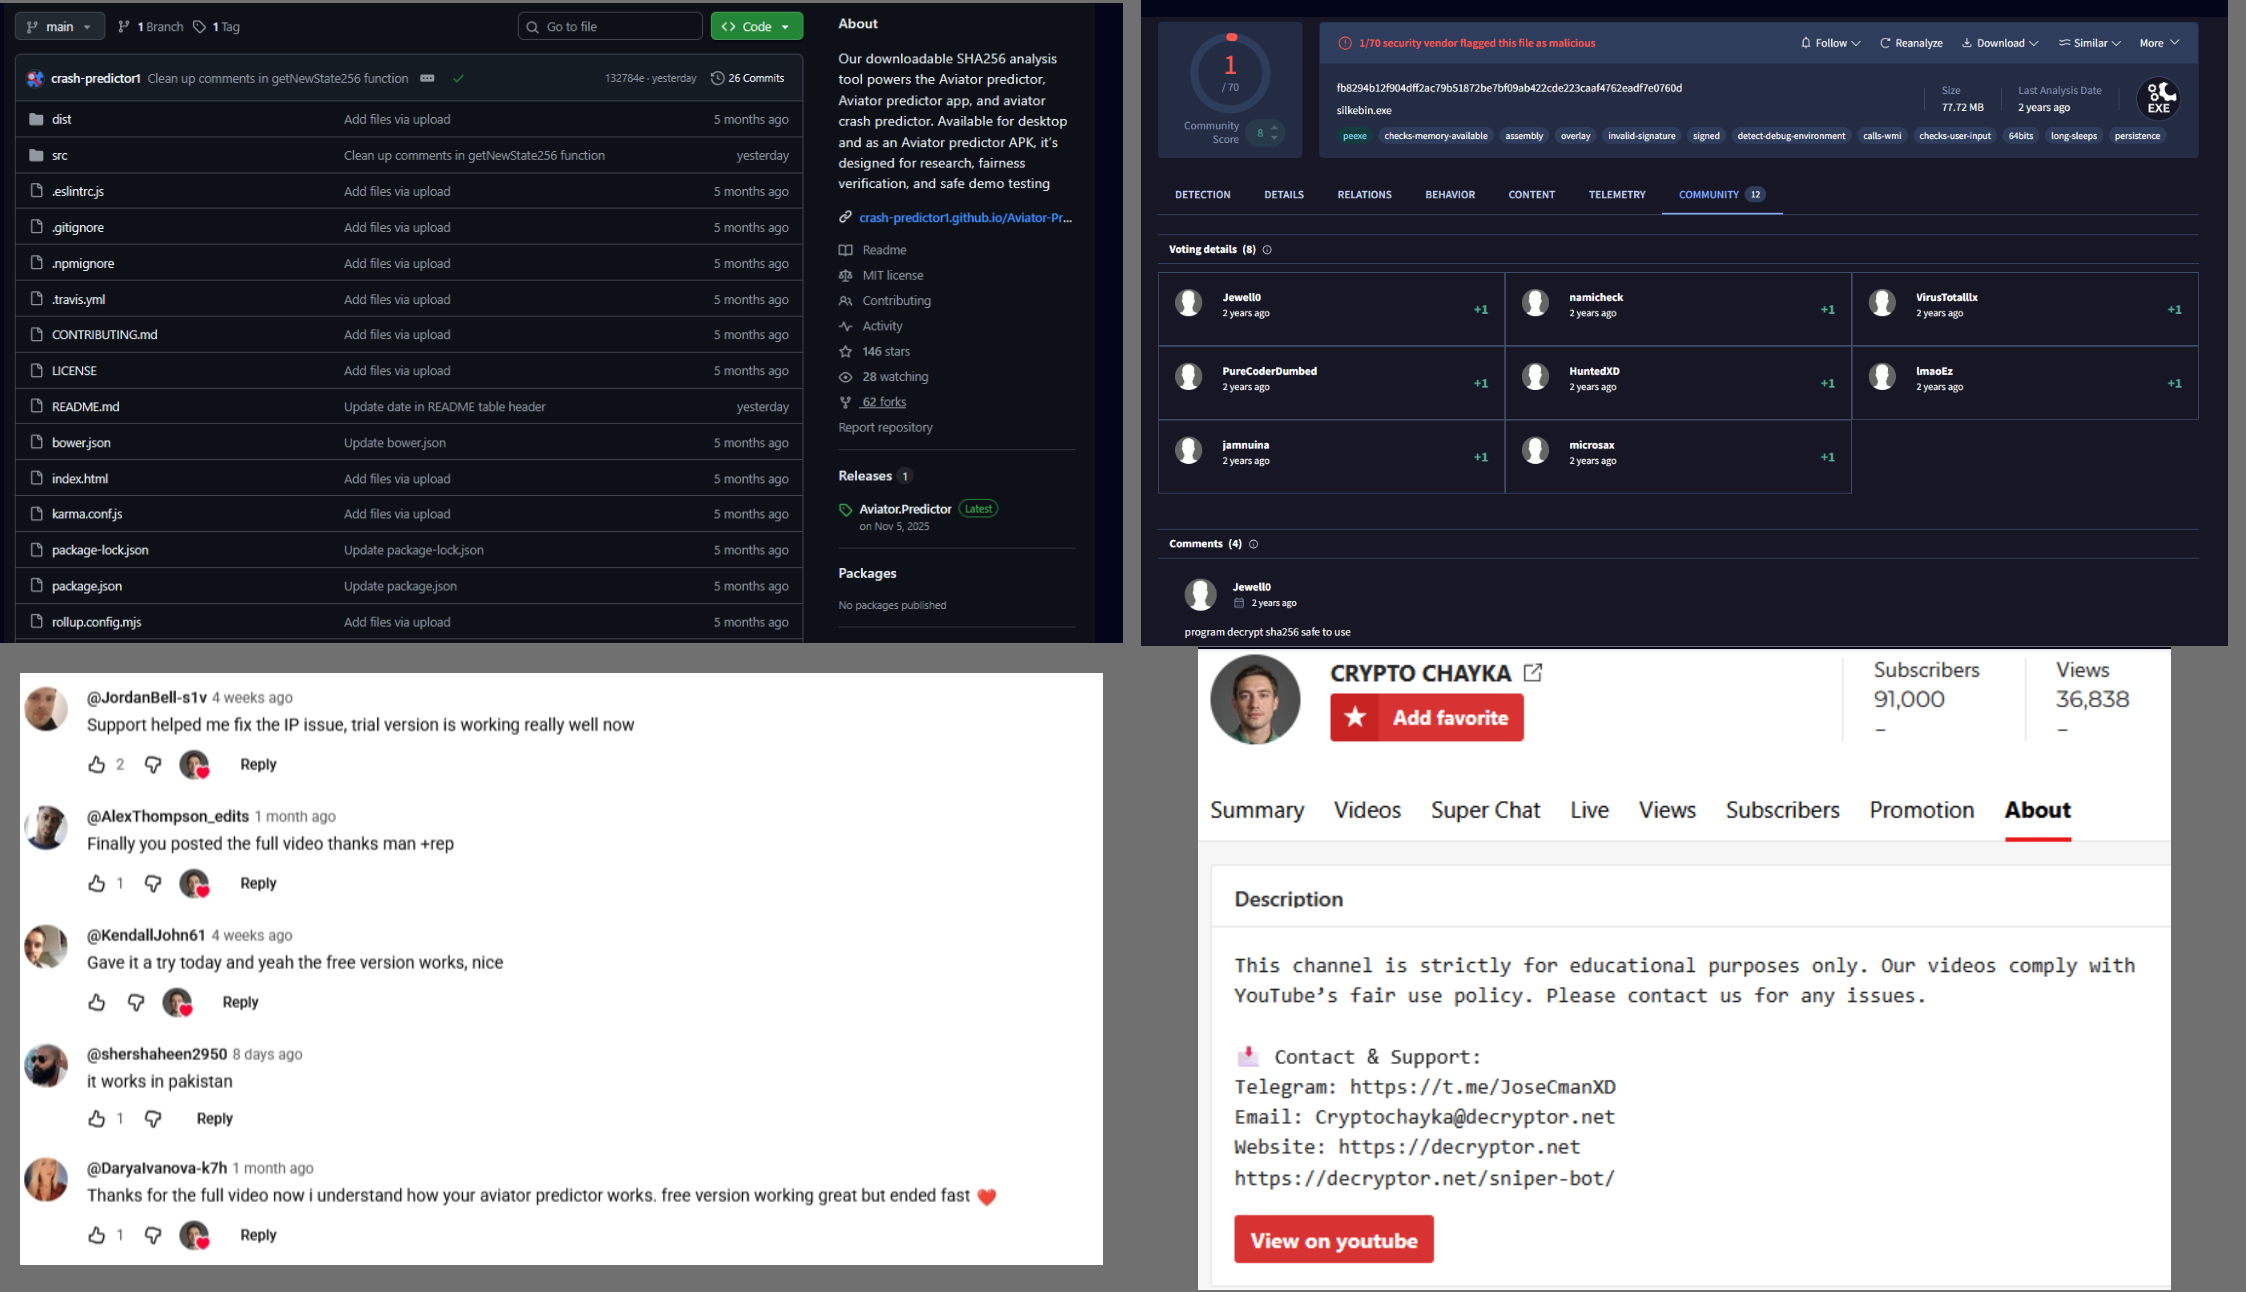
Behind all the fake praise, the actual payload is a dangerous Rust-based malware known as a clipboard hijacker. When a victim downloads the ZIP archive onto a Windows computer, a .NET loader named SniperBot_Premium(Free).exe launches the main file, silkebin.exe.
On macOS systems, a script called unlocker.command forces the device to bypass native Gatekeeper protections so that the malware can run. Once active, it quietly runs in the background and monitors the pasteboard.
The clipper waits until the user copies a long string of characters that looks like a cryptocurrency wallet address. It then quickly and silently swaps it with one of the 15,500 attacker-controlled wallets already embedded in its code. If the user doesn’t double-check the address before hitting send, their funds go straight to the scammers.
Check Point researchers warn that engagement metrics such as likes, stars, and positive comments can be easily bought or faked, and that popularity should never be conflated with safety.
“From a user’s perspective, the ability to manipulate sentiment and reputation on platforms like VirusTotal marks an important evolution in how threat actors shape trust. Even if this campaign is not primarily aimed at large enterprises, it shows that attackers no longer rely only on classic malware distribution techniques to reach victims. Instead, they can manipulate reputation systems, crowd‑sourced feedback, and cross‑platform promotion to lower suspicion and attract more users,” the report concludes.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。