









Threat Response
Threat Response
MiniPlasma: detecting exploitation of a critical unpatched Windows vulnerability
Related Kaspersky Products & Services
posted
minute read
Over the past two months, the anonymous researcher Nightmare Eclipse (also known as Chaotic Eclipse) has publicly released six Windows vulnerabilities complete with ready-to-use exploits, without prior coordination with Microsoft. The most critical of these is MiniPlasma, a zero-day local privilege escalation exploit that grants attackers SYSTEM-level access.
In short
The exploit leverages an old flaw, CVE-2020-17103, which was believed to have been patched back in 2020. Fully updated systems running Windows 11, as well as Windows Server 2022 and 2025, are vulnerable to this attack vector.
Similar to CVE-2020-17103, the MiniPlasma issue is rooted in the Cloud Filter driver and the HsmOsBlockPlaceholderAccess routine.
According to Huntress Labs, attacks exploiting the initial vulnerabilities from the same list as MiniPlasma have been ongoing in the wild since April 10. Microsoft has promised to release a patch for MiniPlasma only on June 9.
Detection by Kaspersky solutions
Kaspersky Managed Detection and Response service detects the exploitation of this vulnerability using the following indicators of attack:
- Creation of SymbolLinks in the registry key:
HKU\\.DEFAULT\\Software\\Policies\\Microsoft\\CloudFiles\\BlockedApps:
category: registry_set
product: windows
detection:
selection:
TargetObject|contains: 'Policies\\Microsoft\\CloudFiles\\BlockedApps'
Details: 'SymbolicLinkValue'
condition: selection
- Tracking the appearance of
wermgr.exeoutside standard paths:
category: process_creation
product: windows
detection:
selection:
TargetFilename|endswith: '\\wermgr.exe'
filter_system_locations:
TargetFilename|startswith:
- 'C:\\Windows\\System32\\'
- 'C:\\Windows\\SysWOW64\\'
- 'C:\\Windows\\WinSxS\\'
- 'C:\\Windows\\servicing\\'
- 'C:\\$WINDOWS.~BT\\'
- 'C:\\Windows\\SoftwareDistribution\\'
condition: selection and not filter_system_locations
- Execution of system binaries or their imitations from non-standard directories.
- The analyzed PoC uses the
.NETlibrary NtApiDotNet by researcher James Forshaw to interact with registry Native APIs. The presence of artifacts or traces of this library’s usage is also an indicator of compromise.
To protect companies using our Kaspersky SIEM system or Kaspersky Extended Detection and Response, we have prepared a correlation rules package designed to detect such malicious activity. The rules are available for download from the products repository. For those developing custom detection rules or conducting threat hunting in the SIEM using Windows events, we recommend monitoring the following activities:
- Modification of the
HKU\.DEFAULT\Software\Policies\Microsoft\CloudFiles\BlockedAppsregistry key by creating a symbolic link toHKU\.DEFAULT\Volatile Environment. To hunt for this, registry auditing (SACL) must be configured. KUMA query:
DeviceEventClassID = '4657' AND FileName like '%Policies\Microsoft\CloudFiles\BlockedApps%' AND DeviceCustomString6 = 'SymbolicLinkValue'
- Execution of the scheduled task
\Microsoft\Windows\Windows Error Reporting\QueueReporting. To trackEvent ID 110, monitoring of theMicrosoft-Windows-TaskScheduler/Operationallog must be configured. KUMA query:
DeviceEventClassID = '110' AND SourceProcessName = '\Microsoft\Windows\Windows Error Reporting\QueueReporting'
- Launching wermgr.exe from a non-standard directory (typically
C:\Windows\(System32|SysWOW64), depending on the system. This activity is detected by the “R150_01_Start of a utility with the name of the system process from a folder other than the standard folder” rule, available in the KUMA repository. KUMA query:
DeviceEventClassID = '4688' AND DestinationProcessName LIKE '%\wermgr.exe' AND NOT (DestinationProcessName = 'C:\Windows\System32\wermgr.exe' OR DestinationProcessName = 'C:\Windows\SysWOW64\wermgr.exe')
- Execution of a non-standard process spawned by wermgr.exe. KUMA query:
DeviceEventClassID = '4688' AND SourceProcessName LIKE '%\wermgr.exe'
Note: The provided search queries are applicable when using the default normalizer. We recommend a search depth of at least one month.
The exploitation of the MiniPlasma vulnerability using the published PoC is successfully detected by Kaspersky Next EDR Expert and Kaspersky Extended Detection and Response via the following rules:
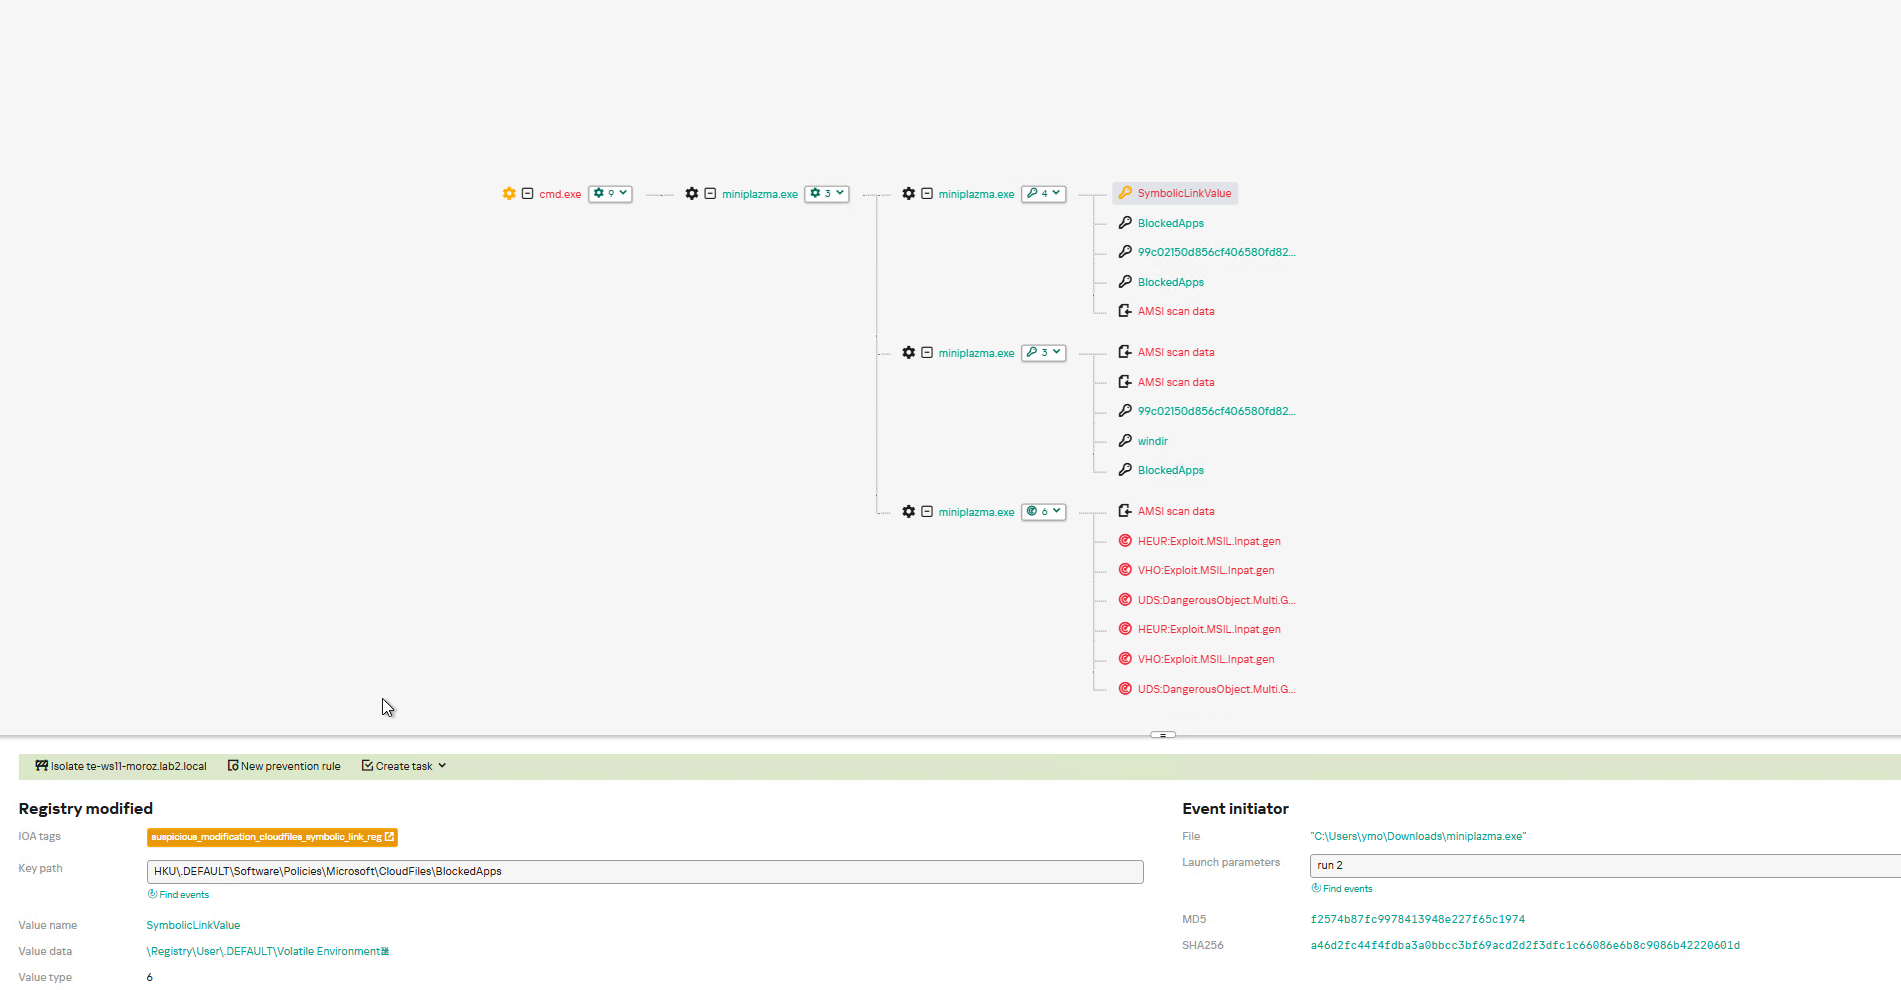
- Detection of SymbolLinks creation in the
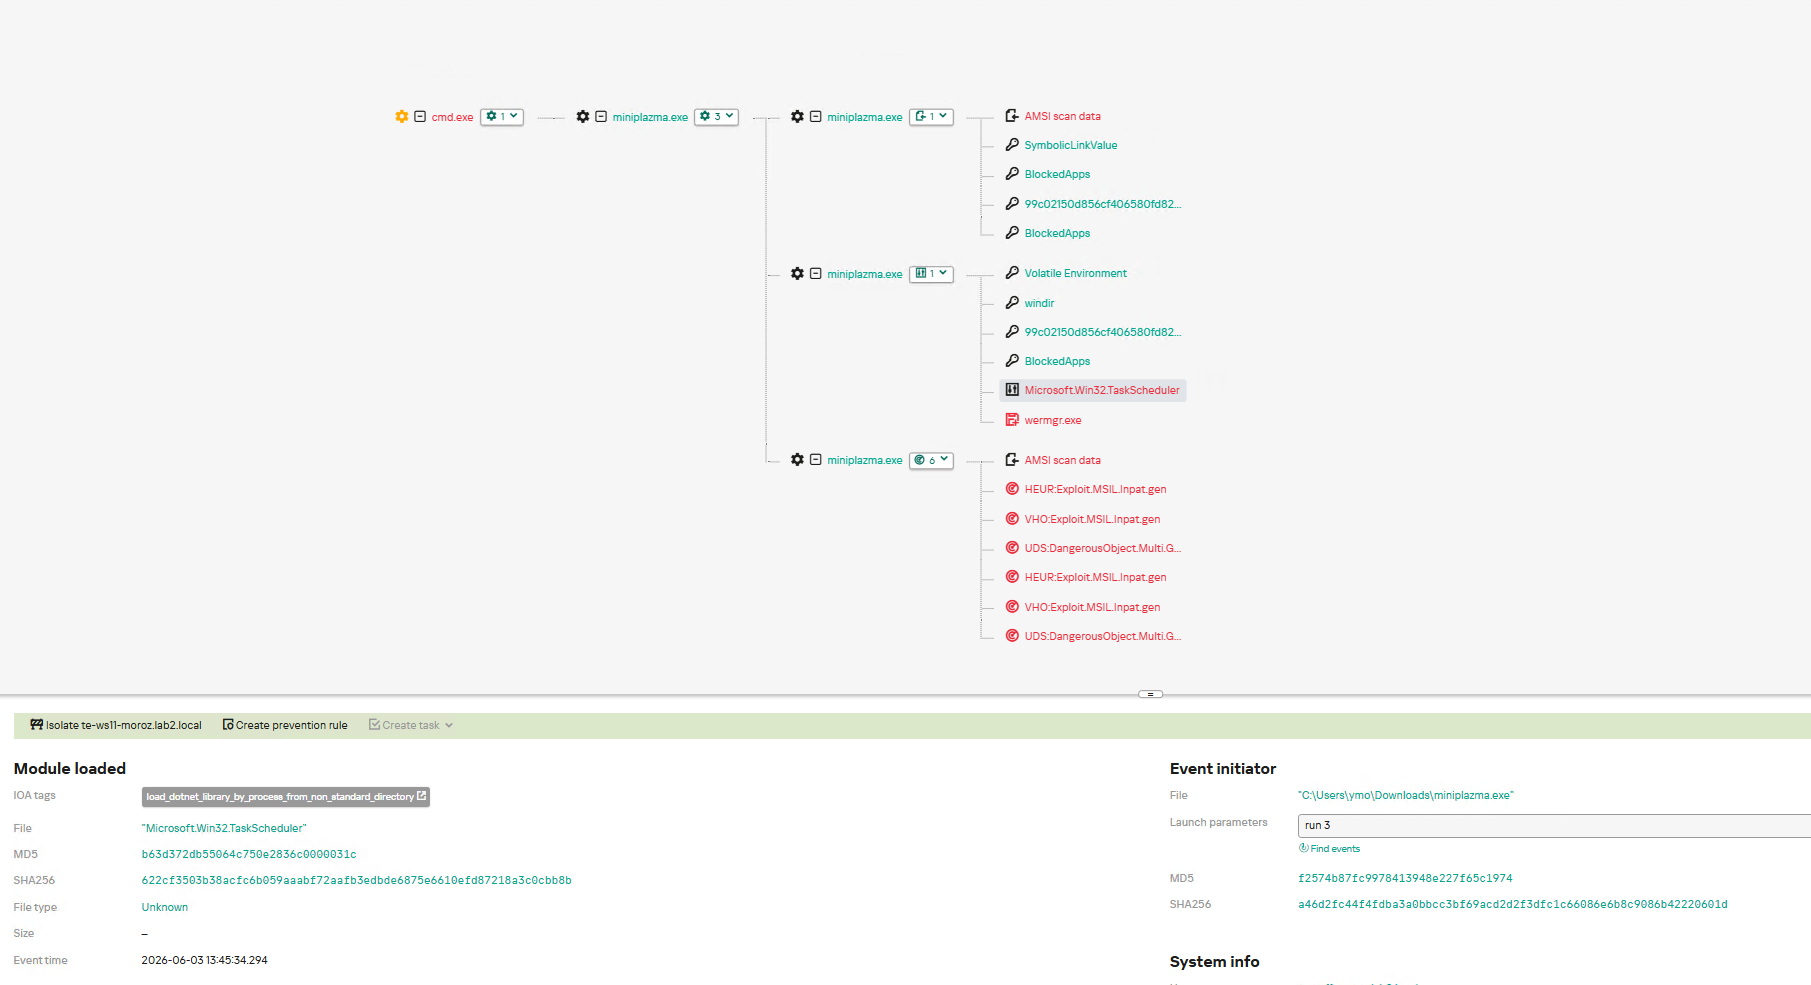
\Software\Policies\Microsoft\CloudFiles\BlockedAppskey via the suspicious_modification_cloudfiles_symbolic_link_reg rule: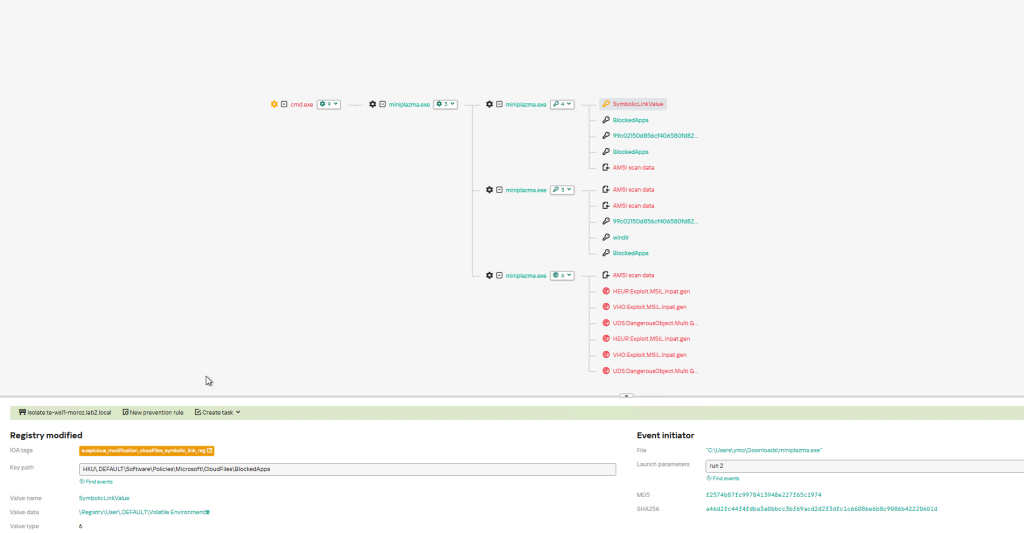
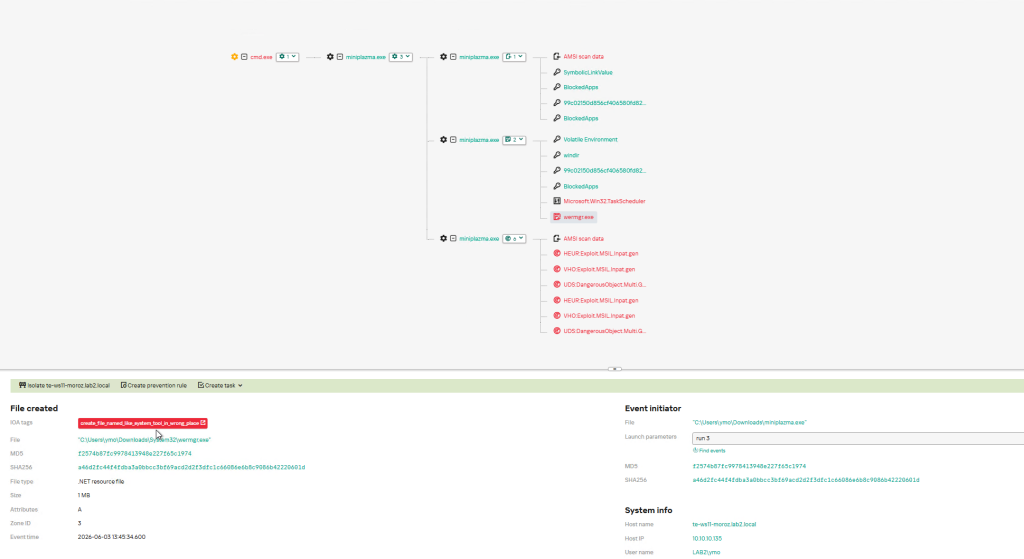
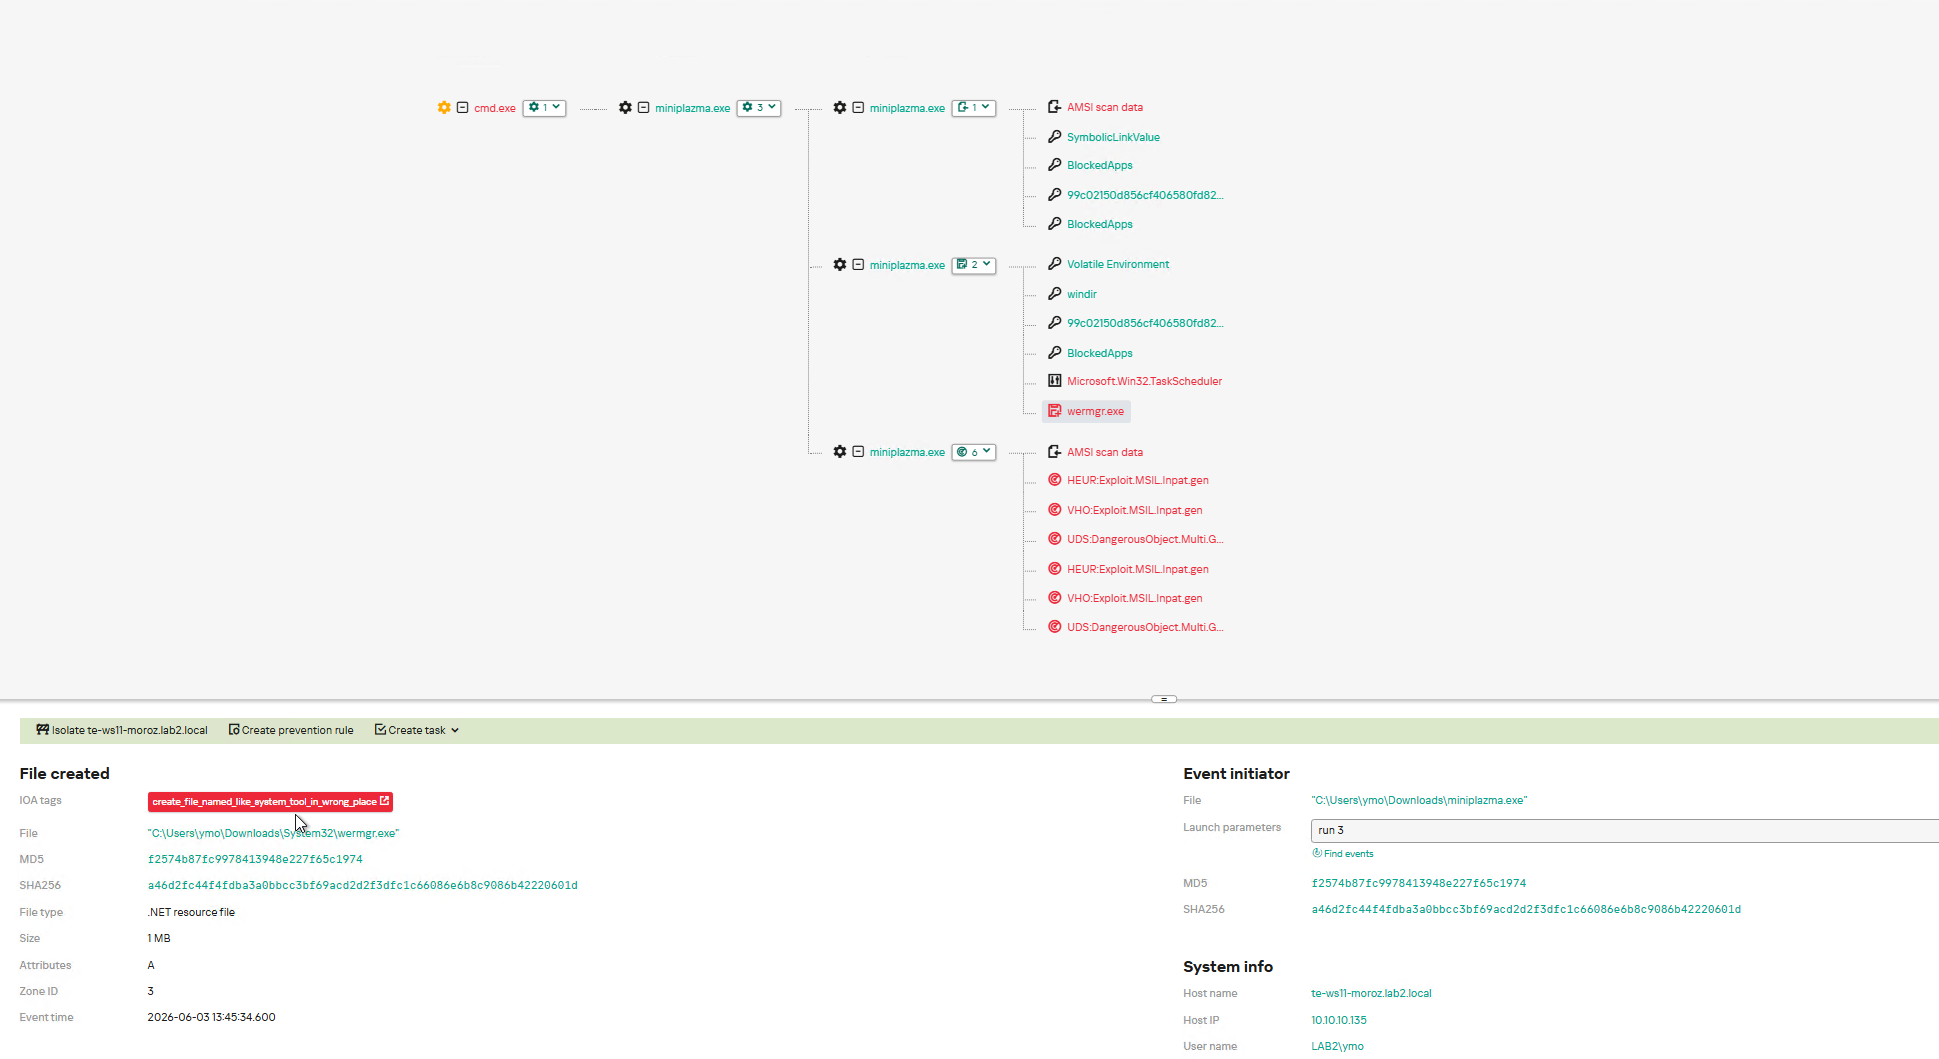
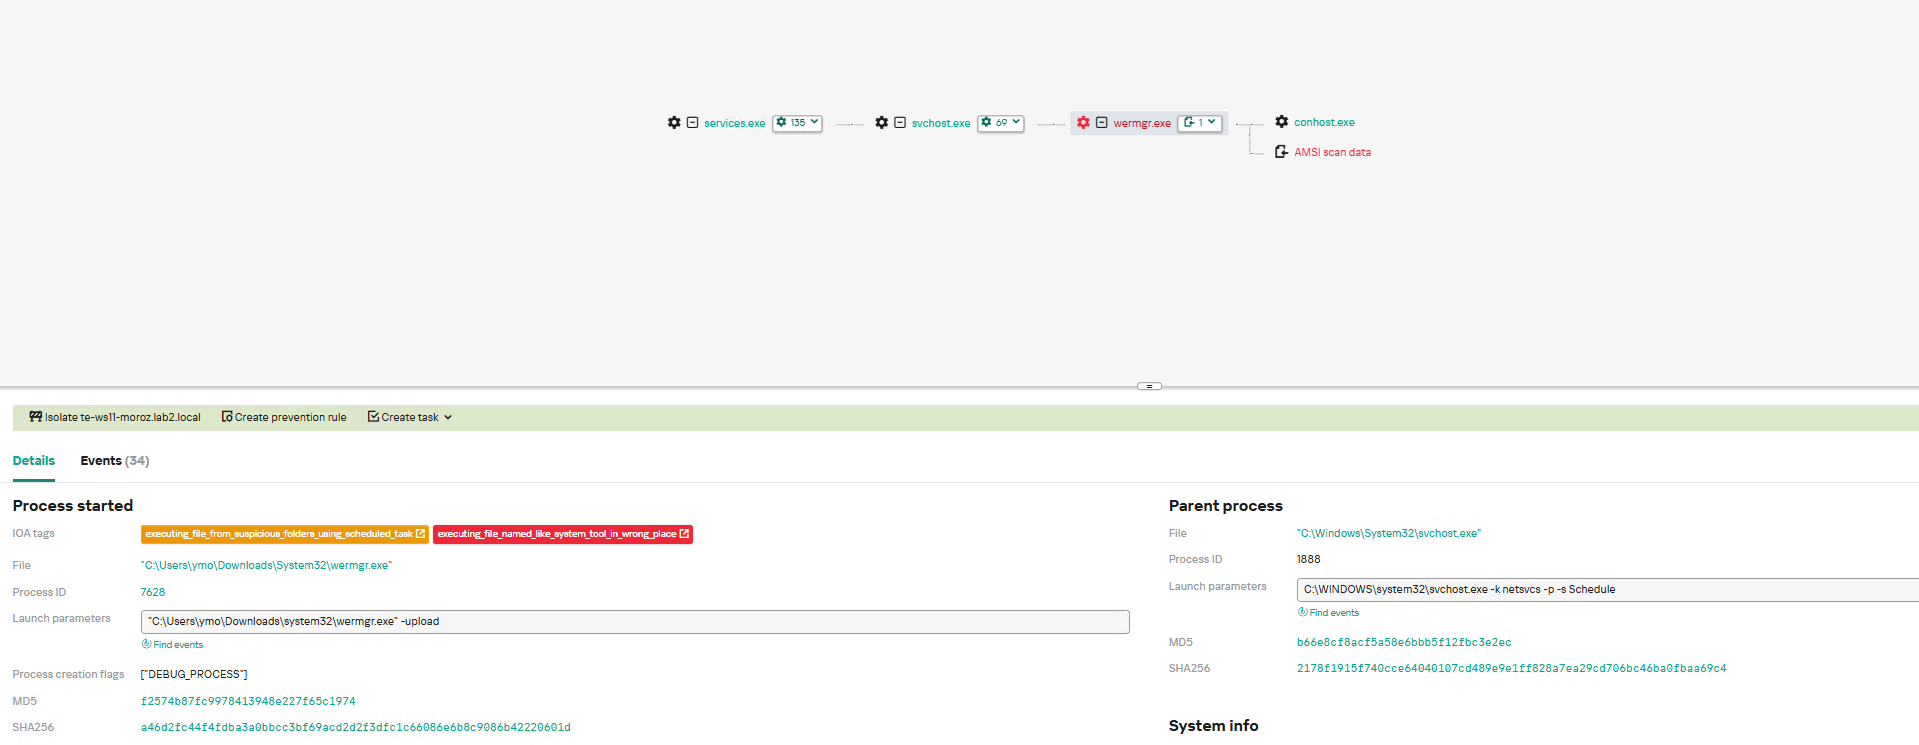
- Detection of system utilities appearing outside system directories via the create_file_named_like_system_tool_in_wrong_place rule:
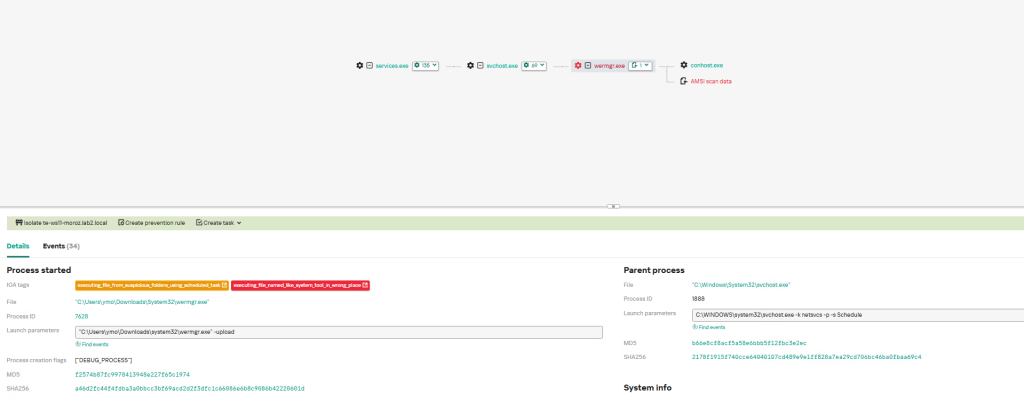
- Detection of system binary execution from non-standard directories via the executing_file_named_like_system_tool_in_wrong_place rule:
- Detection of
.NETlibrary loading from non-standard directories via the load_dotnet_library_by_process_from_non_standard_directory rule: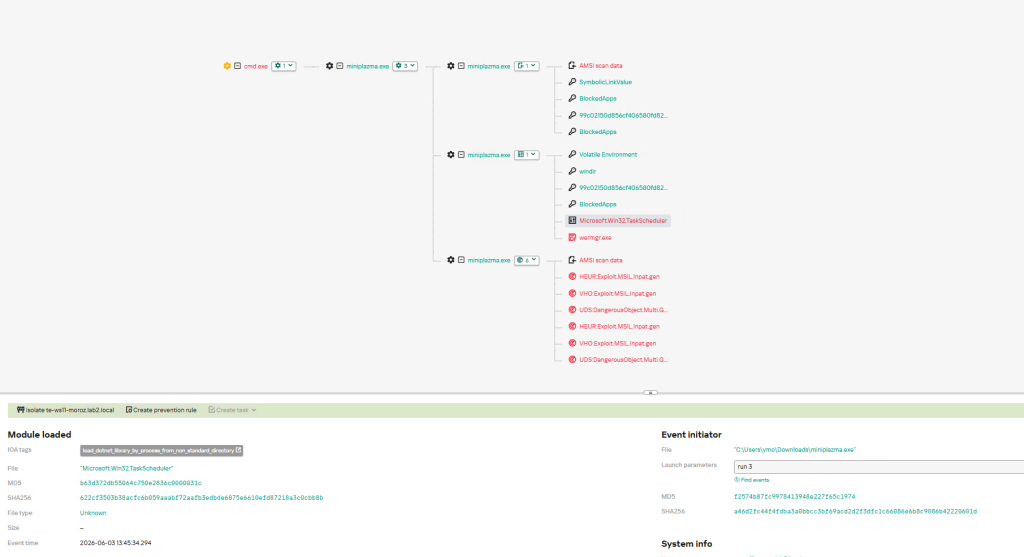
In addition to these products, Kaspersky Endpoint Security successfully detects and blocks attempts to exploit this vulnerability.
