

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

aimingoo的专栏
aimingoo的专栏
Engineering at Meta
Engineering at Meta
有赞技术团队
有赞技术团队
博客园_首页
Apple Machine Learning Research
Vercel News
Vercel News
G
Google Developers Blog
Blog — PlanetScale
Blog — PlanetScale
IT之家
IT之家
MongoDB | Blog
MongoDB | Blog
Y
Y Combinator Blog
B
Blog
The GitHub Blog
The GitHub Blog
M
MIT News - Artificial intelligence
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
Stack Overflow Blog
Stack Overflow Blog
C
Check Point Blog
Microsoft Azure Blog
D
DataBreaches.Net
I
InfoQ
Recent Announcements
阮一峰的网络日志
阮一峰的网络日志
腾讯CDC
H
Help Net Security

Let's Encrypt

The difficulty of making sure your website is broken Simplifying Certificate Renewals for Millions of Domains with ACME Renewal Information (ARI) Six-Day and IP Address Certificates Available in Certbot Shorter Certificate Lifetimes and Rate Limits DNS-PERSIST-01: A New Model for DNS-based Challenge Validation On the Importance of "Hello" and "Thanks" 6-day and IP Address Certificates are Generally Available 10 Years of Let's Encrypt Certificates Decreasing Certificate Lifetimes to 45 Days New "Generation Y" Hierarchy of Root and Intermediate Certificates Ten Years of Community Support ACME Renewal Information (ARI) Published as RFC 9773 Native ACME Support Comes to NGINX End of Life Plan for RFC 6962 Certificate Transparency Logs OCSP Service Has Reached End of Life We've Issued Our First IP Address Certificate Expiration Notification Service Has Ended Reflections on a Year of Sunlight How We Reduced the Impact of Zombie Clients Sustaining a More Secure Internet: The Power of Recurring Donations Ending TLS Client Authentication Certificate Support in 2026 How Pebble Supports ACME Client Developers Ten Years of Let's Encrypt: Announcing support from Jeff Atwood We Issued Our First Six Day Cert Encryption for Everybody Scaling Our Rate Limits to Prepare for a Billion Active Certificates Ending Support for Expiration Notification Emails Announcing Six Day and IP Address Certificate Options in 2025 Announcing Certificate Profile Selection Ending OCSP Support in 2025
Let's Encrypt Root and Intermediate Certificates
2015-06-04 · via Let's Encrypt

By Josh Aas, ISRG Executive Director ·

The keys and certificates that will underlie Let’s Encrypt have been generated. This was done during a key ceremony at a secure facility today. The following objects were created:

  • Key pair and self-signed cert for the ISRG root
  • Key pair and certificate for the ISRG root’s OCSP
  • Key pairs and certificates for two Let’s Encrypt intermediate CAs
  • CRL under the ISRG root showing that the Let’s Encrypt intermediates have not been revoked

The certificates over the public keys, of course, can be made public:

Let’s Encrypt will issue certificates to subscribers from its intermediate CAs, allowing us to keep our root CA safely offline. IdenTrust will cross-sign our intermediates. This will allow our end certificates to be accepted by all major browsers while we propagate our own root.

Under normal circumstances, certificates issued by Let’s Encrypt will come from “Let’s Encrypt Intermediate X1”. The other intermediate, “Let’s Encrypt Intermediate X2”, is associated with our disaster recovery site and will only be used should we lose the ability to issue with “Let’s Encrypt Intermediate X1”.
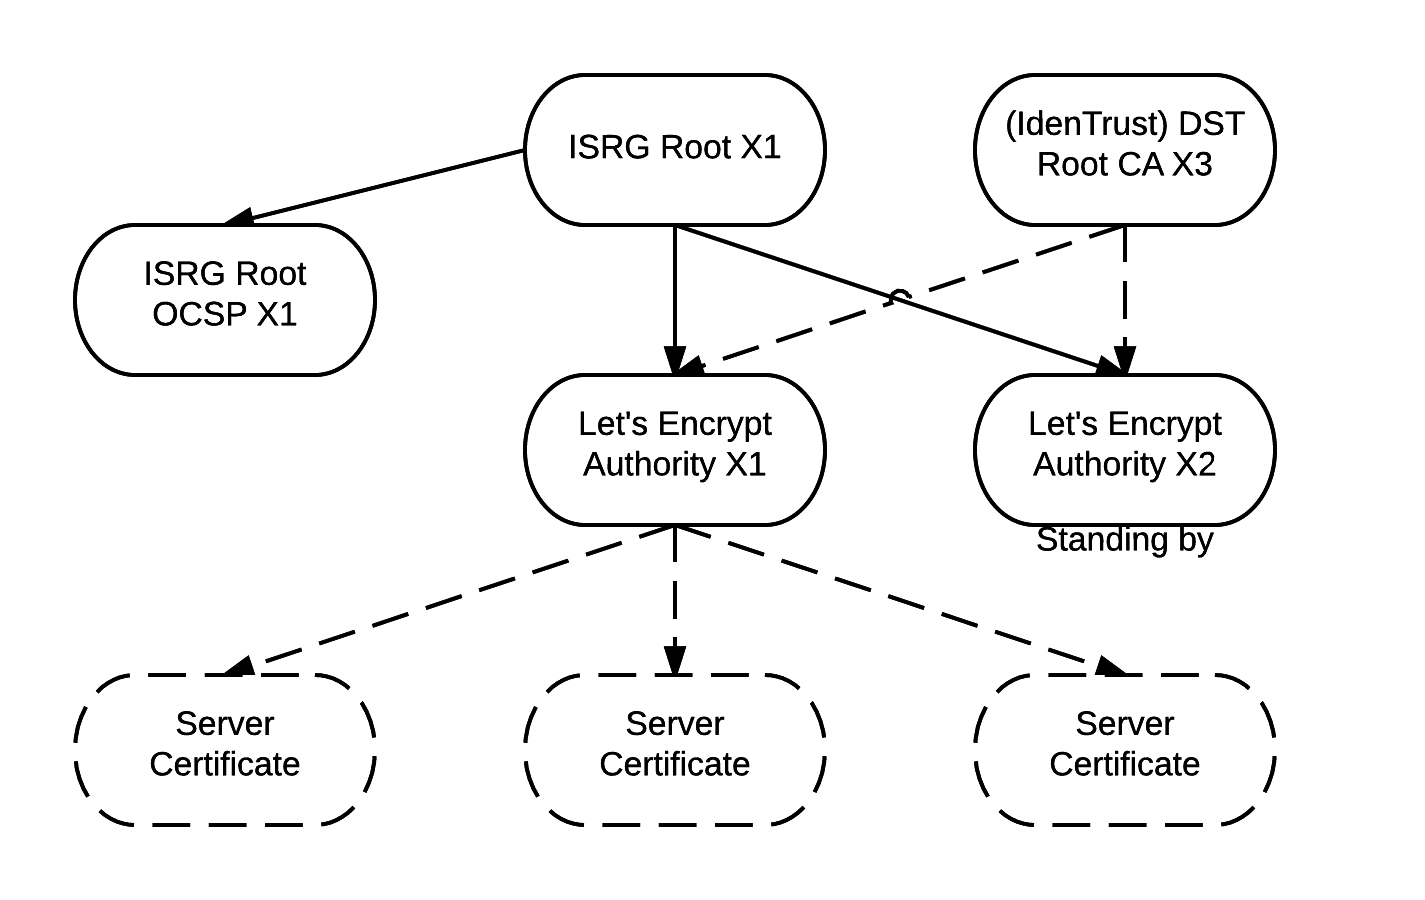
ISRG Key Diagram

The private keys for the ISRG root CA and the Let’s Encrypt intermediate CAs are stored on hardware security modules (HSMs), which provide a high degree of protection against the keys being stolen.

All ISRG keys are currently RSA keys. We are planning to generate ECDSA keys later this year.

The generation of these keys and certificates is an important step in getting Let’s Encrypt ready to issue certificates. In the next few weeks, we’ll be saying some more about our plans for going live. In the meantime, we would love for you to get involved.