











In an average week, Netlify blocks over half a billion malicious Layer 7 HTTP requests to our customer websites, with peaks totalling several times this amount.
Today Netlify is announcing our Advanced Web Security portfolio, which encompasses several of the security features that were previously available in our service. We are also introducing a new Web Application Firewall (WAF) capable of blocking OWASP-classified web attacks.
Looking back just a few years prior, composable applications mainly focused on the frontend web experience, pulling together content sources into Jamstack frameworks coupled with a lightning-quick Content Delivery Network (CDN).
Today, as more enterprises are embracing composable architecture solutions, the applications developed have become more complex and depend even more on backend systems—databases and APIs—to deliver a true enterprise-class experience to customers. These enterprise applications require greater levels of confidential data processing, compliance, and security.
Security at Netlify
Netlify is committed to providing a robust and comprehensive security framework designed to protect your web applications and dynamic websites. Our approach is to be secure by design and at scale, ensuring that security is woven into every aspect of our platform, from infrastructure to application security, and access control to compliance
1. Secure Access Control
Netlify ensures secure access control by implementing robust mechanisms that only allow authorized users to access your applications.
- Through Single Sign-On (SSO), we support both Team SSO and Organization SSO, enabling strict policy enforcement by team and organization owners to minimize security risks.
- For managing user access at scale, our SCIM Directory Sync integrates with supported identity providers, allowing seamless management of Netlify access across multiple teams directly from your identity provider.
- Additionally, role-based access control (RBAC) offers fine-grained access control by restricting developers’ access to specific sites within a team.
- We also make available a Security Scorecard to ensure your organization is configured to meet best practices.
2. Compliance and Certifications
Netlify is dedicated to meeting the complex security and compliance needs of enterprises. Netlify adheres to industry standards and frameworks such as SOC 2 Type 2, SOC 27001, PCI DSS, GDPR, and CCPA, and employs a variety of anti-fraud-and-abuse controls.
For the latest compliance information, visit Netlify’s trust center.
3. Advanced Web Security
This is the latest addition to our list of security features to protect your site from threats and unauthorized access. Netlify Advanced Web Security encompasses the following enterprise security features:
- World-class DDoS mitigation protections
- A user-customizable Web Application Firewall
- Configurable rate limiting
- Firewall Traffic Rules to block traffic based on IP address or geographic location
- Access to Log Drains for full visibility over user traffic
Netlify’s Web Application Firewall
To keep our customers safe, Netlify applies a variety of protections and filters globally to block a variety of common attacks on websites. These protections include tests for protocol and method enforcement, detection of path attacks, and the validation of request headers, user agents, and URIs, among other filters. These rules are in addition to our global IP bans, which block known malicious traffic, and the blocking of traffic associated with Distributed Denial of service (DDoS) attacks.
In an average week, Netlify blocks over half a billion malicious Layer 7 HTTP requests to our customer websites, with peaks totalling several times this amount.
This attack-blocking functionality is baked into our core service and is not customizable by users. Starting today, customers can apply and configure firewall rules compatible with the OWASP Core Rule Set (OWASP CRS), curated by Netlify to address the type of attack traffic we see targeting composable site architectures.
The OWASP CRS is one of the most respected sets of WAF rules available. It is specifically designed to detect some of the most exploited modern web attack signatures, including those in the OWASP Top 10.
The Netlify WAF also supports a passive mode, which coupled with log drains, enables site developers to observe the rules triggering on-site traffic, so ruleset tuning can be performed. Similar to the functionality of our custom rate limiting rules, our WAF also supports exclude paths.
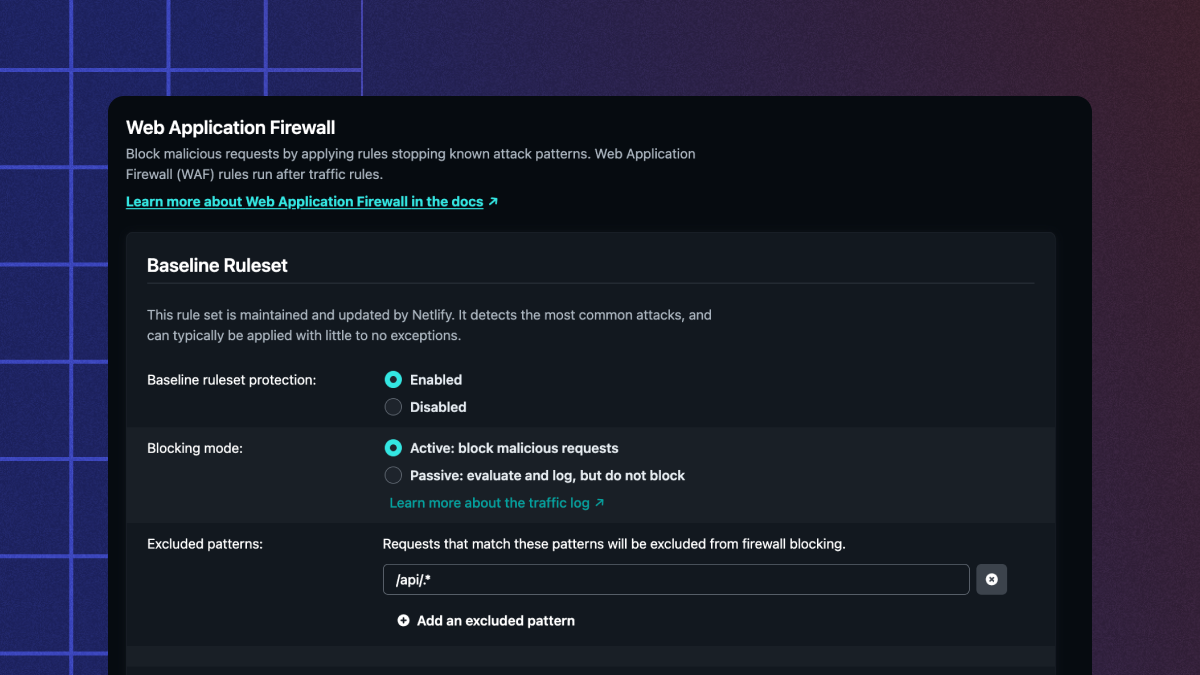
Review our WAF documentation to learn more about how to enable and configure the Netlify Web Application Firewall for your sites.
One advantage of using a composable architecture is that you can piece together a custom application stack that’s the right solution for your site. If you want to bring your own WAF to your site, our customer success engineers can help you find a reference architecture that meets your needs.
Conclusion
The suite of security tools available in our Netlify Advanced Web Security portfolio provides site developers with the necessary tools to defend against modern web attacks. This suite is now more powerful with the introduction of the user-customizable Netlify Web Application Firewall.
WAF is currently available for all enterprise customers. If you’re interested in learning more about WAF and want to evaluate how to apply Netlify’s Advanced Web Security features to your sites, please get in touch with the Netlify Sales Team.