


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

T
Tailwind CSS Blog
博客园 - Franky
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
Y
Y Combinator Blog
Hugging Face - Blog
Hugging Face - Blog
博客园 - 聂微东
L
LangChain Blog
博客园_首页
Recent Announcements
月光博客
月光博客
酷 壳 – CoolShell
酷 壳 – CoolShell
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
H
Hackread – Cybersecurity News, Data Breaches, AI and More
爱范儿
爱范儿
博客园 - 叶小钗
博客园 - 【当耐特】
The Cloudflare Blog
J
Java Code Geeks
G
Google Developers Blog
云风的 BLOG
云风的 BLOG
Blog — PlanetScale
Blog — PlanetScale
博客园 - 司徒正美
aimingoo的专栏
aimingoo的专栏
A
About on SuperTechFans

Sansec - experts in eCommerce security

GorgonAgora: 4,800+ fake storefronts skim cards across hundreds of impersonated brands Sansec adds support for Sylius 1 & 2 Critical vulnerability in Mirasvit Cache Warmer for Magento Critical FunnelKit vulnerability threatens 40,000+ WooCommerce checkouts Composer vulnerability leaks GitHub tokens, threatens PHP supply chain Over 200 PrestaShop stores expose installer, allowing full takeover ClickFix malware hits DoD cybersecurity vendor homepage SVG Onload Tag Hides Magecart Skimmer on 99 Stores Mass PolyShell attack wave hits 471 stores in one hour Novel WebRTC skimmer bypasses security controls at $100+ billion car maker PolyShell: unrestricted file upload in Magento and Adobe Commerce Digital skimmer hits global supermarket chain Building a faster YARA engine in pure Go Magento Developers Impersonated in Targeted GitHub Malware Operation Claude finds 353 zero-days on Packagist The billion-dollar security.txt problem Keylogger targets 200,000+ employees at major US bank ConnectPOS leaked Github secrets for years Critical backdoor found in MGT Varnish extension SessionReaper attacks have started, 3 in 5 stores still vulnerable SessionReaper, unauthenticated RCE in Magento & Adobe Commerce (CVE-2025-54236) Adobe patches critical Magento admin takeover via menu injection Backdoor found in popular ecommerce components Found defunct.dat on your site? You've got a problem. You have 2 weeks left to set up CSP for your store Merchants left guessing at last-minute PCI-DSS u-turn Magento Security Release APSB25-08 [Impact Analysis] Sorry, client-side security does not work Google services abused in skimming campaigns Thousands of Adobe Commerce stores hacked in competing CosmicSting campaigns
ABS-CBN next in series of high profile breaches
Sansec Forensics Team · 2018-09-18 · via Sansec - experts in eCommerce security

ABS-CBN headquarters

ABS-CBN headquarters

While Filipinos are recovering from typhoon Mangkhut, another misfortune awaits them online. We found their broadcasting giant ABS-CBN − a $740 million conglomerate & top-500 global Internet destination − to be hacked. Criminals are running a payment skimmer on ABS-CBNs online store since at least August 16th. Personal information and credit cards are intercepted while people shop for merchandise for one of the 90+ television shows. The stolen data is sent onwards to a server registered in Irkutsk, Russia. The credit cards and identities are then (presumably) sold on the black market.

ABS-CBN is the latest target in a series of high profile skimming operations. Previously, British Airways and Ticketmaster admitted massive credit card theft of their customers. The methodology found at these crime scenes is the same: browser-based interception during the checkout process. This method is quickly gaining popularity because it defeats the security of encrypted connections (https/SSL).

Filipinos are recommended to carefully check their credit card statements for unauthorized payments.

We have notified ABS-CBN of the breach, but have not received a response.

Technical details

Sansec discovered the fraud campaign with newly released malware detection heuristics. The (obfuscated) malware is located at store.abs-cbn.com/js/lib/ccard.js (archive.org). This specific file has not been modified since four weeks, suggesting the malware was injected on or before August 16th.

$ curl -v https://store.abs-cbn.com/js/lib/ccard.js
< Last-Modified: Thu, 16 Aug 2018 06:24:34 GMT

The malware sends its stolen data to a payment collection server called adaptivecss[.]org.
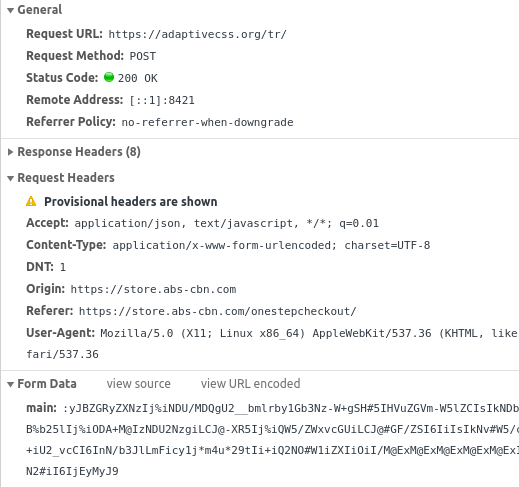
adaptivecss[.]org

This server is on the same Russian network as coffemokko.com, a different malware campaign that we discovered earlier this week:

Just discovered the curiously named "Coffe&Tea" malware campaign. CC servers at https://t.co/pS6O7mXCbm, https://t.co/7i8JqZcNXf, https://t.co/yCiImbSyfY. They have open dirs so you can list the fake payment popups per victim. Do you recognize any of them? pic.twitter.com/TFIr4qrHjm

— Willem de Groot (@gwillem) September 13, 2018

Read more