






Sansec researchers discovered that ConnectPOS, a popular Point of Sale solution, had been exposing a GitHub Personal Access Token (PAT) in their public installation instructions for over four years. The token had full repo access rights, meaning anyone who found it could push malicious code to ConnectPOS repositories.
ConnectPOS publishes installation guides on their website. In September 2021, when they migrated from GitLab deploy tokens to GitHub PAT authentication, they included an access token in their public documentation to allow customers to download modules. However, the token was configured with full repo scope instead of read-only access, granting anyone who found it complete control over the repositories. This token remained exposed until we reported it on January 6th, 2026.
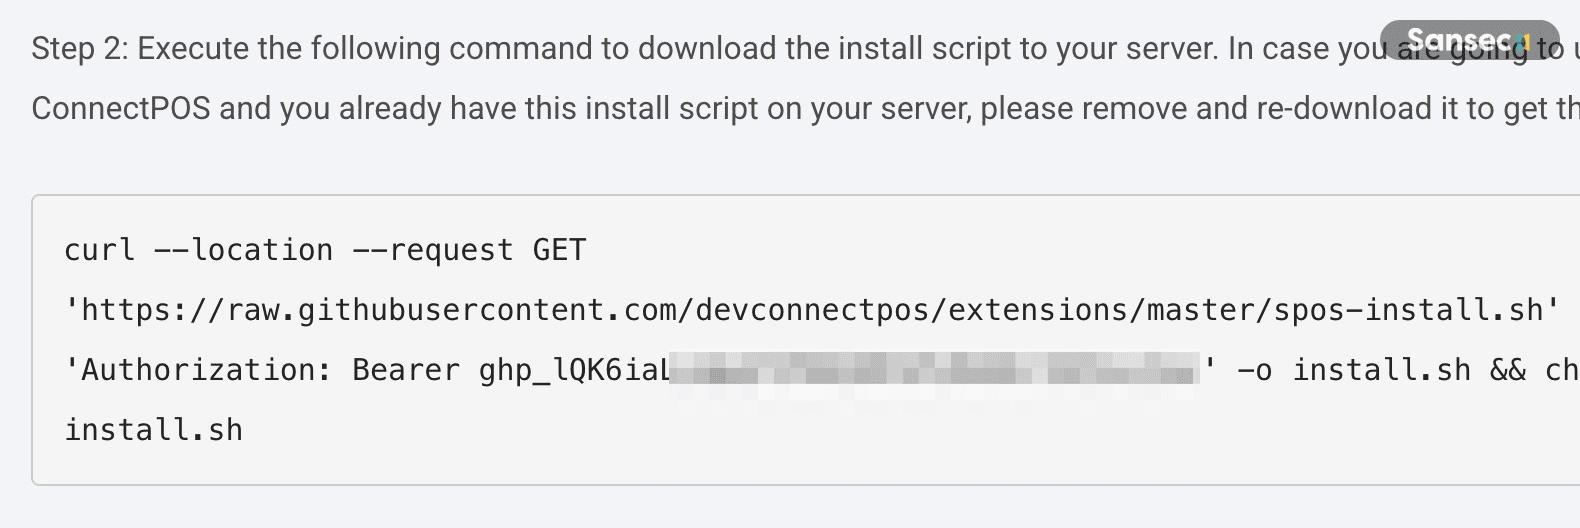
The token granted full administrative access to 59 repositories, covering everything from payment processing to inventory management:
devconnectpos/connectpos-module-aw-giftcard
devconnectpos/connectpos-module-boostmyshop
devconnectpos/connectpos-module-catalog
devconnectpos/connectpos-module-configuration
devconnectpos/connectpos-module-core
devconnectpos/connectpos-module-customer
devconnectpos/connectpos-module-giftcard
devconnectpos/connectpos-module-giftcard-integration
devconnectpos/connectpos-module-inventory
devconnectpos/connectpos-module-marketing
devconnectpos/connectpos-module-payment
devconnectpos/connectpos-module-quotation
devconnectpos/connectpos-module-quote
devconnectpos/connectpos-module-report
devconnectpos/connectpos-module-reward-points
devconnectpos/connectpos-module-sales
devconnectpos/connectpos-module-shipping
devconnectpos/connectpos-module-store-credit
devconnectpos/connectpos-module-store-pickup
devconnectpos/connectpos-module-webhook
devconnectpos/connectpos-package
devconnectpos/connectpos-woocommerce
devconnectpos/extensions
devconnectpos/m2-rest-api
devconnectpos/m23-rest-api
devconnectpos/module-adyen
devconnectpos/module-category
devconnectpos/module-core
devconnectpos/module-custom-sale
devconnectpos/module-customer
devconnectpos/module-customization
devconnectpos/module-discount-per-item
devconnectpos/module-discount-whole-order
devconnectpos/module-electronic-journal
devconnectpos/module-email
devconnectpos/module-eway
devconnectpos/module-integrate
devconnectpos/module-payment
devconnectpos/module-payment-express
devconnectpos/module-performance
devconnectpos/module-product
devconnectpos/module-pwa
devconnectpos/module-pwa-banner
devconnectpos/module-pwa-keyword
devconnectpos/module-pwa-qrcode
devconnectpos/module-refund-without-receipt
devconnectpos/module-report
devconnectpos/module-sales
devconnectpos/module-setting
devconnectpos/module-shell
devconnectpos/module-shift
devconnectpos/module-shipping
devconnectpos/module-store
devconnectpos/module-stripe
devconnectpos/module-tax
devconnectpos/module-tls
devconnectpos/module-wishlist
devconnectpos/module-xretail
devconnectpos/module-xretail23
With this access, an attacker could have:
Sansec did not download any private repositories so we cannot tell whether any of the modules have been tampered with. Given that an attacker can easily hide their malicious injection, for example by spoofing a legitimate ConnectPOS employee, a full audit of the code bases is required to assert trustworthiness.
GitHub has a secret scanning feature that automatically detects exposed credentials. This feature is enabled by default for public repositories but requires a paid plan for private repositories. Since ConnectPOS uses private repositories, we suspect they did not have this feature enabled.
The token is now revoked. That's the good news. The bad news? We don't know if anyone else found it during those four years. If you're running ConnectPOS, assume the worst and verify you're clean:
| Date | Event |
|---|---|
| September 27, 2021 | Token added to ConnectPOS installation documentation |
| January 6, 2026 | Sansec reports the exposure to ConnectPOS |
| January 6, 2026 | ConnectPOS revokes the token |
| January 12, 2026 | Sansec publishes this advisory |
We commend ConnectPOS for their swift response in revoking the token within hours of our report. However, given the 4+ year exposure window, a thorough security audit of the affected repositories and downstream installations is warranted.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。