惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Engineering at Meta
Engineering at Meta
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
腾讯CDC
宝玉的分享
宝玉的分享
量子位
Recent Announcements
Martin Fowler
Martin Fowler
J
Java Code Geeks
V
Visual Studio Blog
阮一峰的网络日志
阮一峰的网络日志
Blog — PlanetScale
Blog — PlanetScale
大猫的无限游戏
大猫的无限游戏
博客园 - 叶小钗
S
SegmentFault 最新的问题
B
Blog
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
博客园 - 【当耐特】
小众软件
小众软件
The Cloudflare Blog
Y
Y Combinator Blog
I
InfoQ
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
GbyAI
GbyAI
IT之家
IT之家

Cybersecurity Dive - Latest News

Dozens of Red Hat npm packages targeted in supply chain attack Turning tension into collaboration: How CIOs and CISOs can lead together Anthropic shares Mythos with 150 more organizations, including critical infrastructure operators Without strong governance, companies put credit ratings at risk in AI era CISA adds critical Palo Alto Networks firewall flaw to KEV as company, researchers warn of exploitation How Canva scaled to 260+M users while elevating security and productivity Top 4 data security best practices for the AI-enabled enterprise CISA urges security teams to check for software development compromises How CISOs can manage sovereign-cloud security risks IBM’s new $5B initiative will help enterprises rapidly patch open-source vulnerabilities Enterprise data is creeping its way into shadow AI tools Coordinated operation takes down Glassworm botnet Leading AI models are more vulnerable to malicious prompts than vendors claim Iranian government, not hacktivist group, breached LA Metro system, security firm says FBI warns about PhaaS platform used to access Microsoft 365 environments Iran-linked hackers target key US, allied sectors with sophisticated spear-phishing messages New York regulator calls for additional cyber mitigation amid heightened threat environment CISA asks cybersecurity community to alert it to vulnerability exploitation Grafana Labs links GitHub environment breach to TanStack npm supply chain attack 7-Eleven hit by data breach Microsoft disrupts cybercrime operation that hid behind legitimate software Compromised coding tool helped hackers breach thousands of GitHub repositories Telecom sector launches its own private ISAC Patch bypass allows hackers to exploit prior flaw in SonicWall SSL-VPN Grafana Labs says hacker gained access to codebase through leaked token How a government contest launched a revolution in AI-based bug hunting Attackers exploit critical flaw in Cisco Catalyst SD-WAN Controller MSPs need AI to fight AI-fueled cyberthreats: Guardz More money is going to physical security, but it’s often CISOs that oversee it: EY Frontier AI models reap rapid discovery of security vulnerabilities
California water utility probes breach claim by Iran-link...
David Jones · 2026-06-17 · via Cybersecurity Dive - Latest News

An article from site logo

The group Handala said it attacked one of the nation’s largest water companies.

Published June 17, 2026

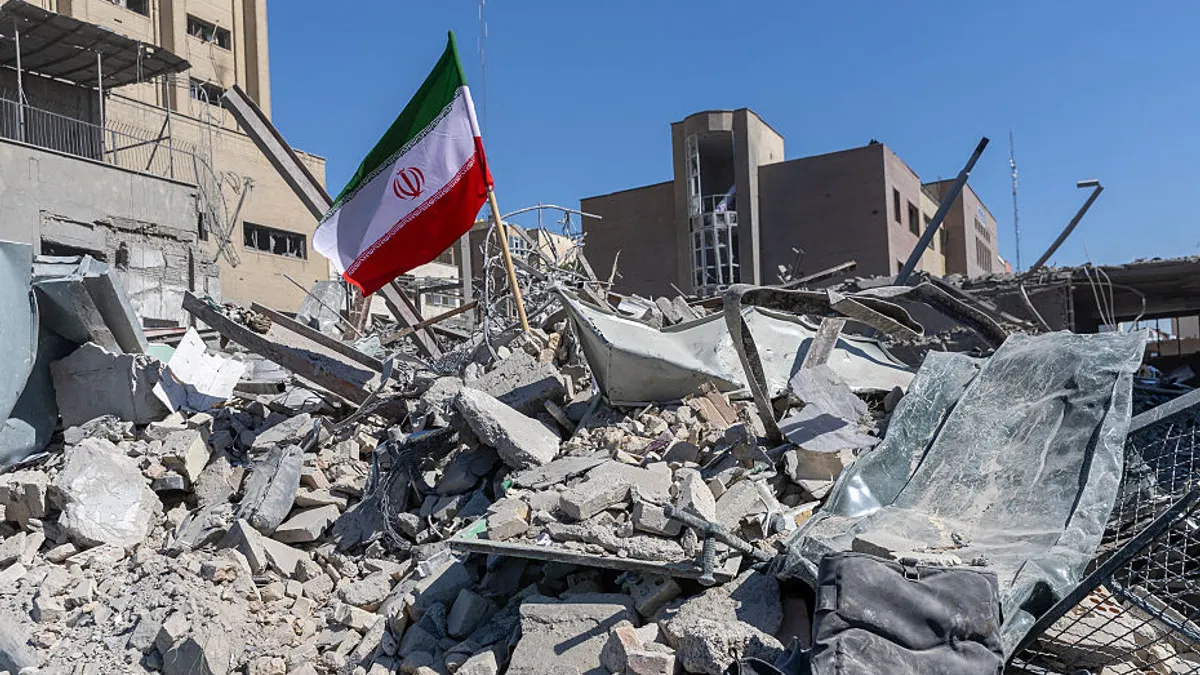
A pile of rubble with an Iranian flag stuck in it is shown.

An Iranian flag is planted on March 3, 2026, in the rubble of a police station in Tehran, Iran, damaged in airstrikes yesterday. Handala, a state-linked threat group, is claiming credit for a June 2026 attack targeting a California water utility. Majid Saeedi / Stringer via Getty Images

California Water Service said it is investigating claims by an Iran-linked threat group of a cyberattack against the water utility. 

The Iran-nexus group tracked as Handala claimed an attack against the water utility and cautioned that it deliberately avoided any attempt to disrupt the facility’s water distribution, according to Check Point Research. 

Cal Water, the largest water utility in the western U.S., confirmed that a claim was made on June 11. It said it is continuing to investigate. 

“We take cybersecurity and this claim very seriously and are working around the clock to investigate,” a spokesperson told Cybersecurity Dive via email.

After learning of the claim last Thursday, Cal Water officials have been working with forensic investigators as well as federal and state law enforcement. Preliminary results show no operational disruptions to water systems or customer billing, the spokesperson said. 

The group Handala claims the attack was retaliation for recent U.S. military operations in Sirik, Iran, according to Check Point Research. The group also claims it deliberately chose not to disrupt water services at the utility. 

The group posted several screenshots that appear to show customer relationship management and billing systems, global navigation satellite systems, access to customer information and several internal credentials.

Check Point Research said if the posted information is confirmed, it would indicate the hackers gained access to the utility’s information technology systems and not the operational technology systems that could control water distribution.  

The disclosure came just days after a Utah-based water utility said it had recovered from a March attack on its facilities. Sage Energy Partners last week said it had remediated systems at its Sage Water Resources facility, which operates a salt-water disposal facility in Duchesne, Utah. 

The company said an investigation found that a sophisticated nation-state threat actor compromised the programmable logic controllers automation system at the facility. Sage officials said the attack was consistent with a wider campaign targeting critical infrastructure across the U.S.

As previously reported, the Cybersecurity and Infrastructure Security Agency and the FBI previously issued an advisory warning of a threat to water and energy facilities by state-linked hackers. The agencies confirmed that multiple sites had been attacked, leading to disruption and financial impacts. 

Handala is considered one of the most notorious threat actors linked to Iran. The group claimed credit for a March attack against medical device maker Stryker.

Federal officials seized domains linked to Handala after the group used various websites to publicize attacks and target political dissidents.