惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

B
Blog RSS Feed
博客园 - 叶小钗
F
Fortinet All Blogs
GbyAI
GbyAI
Martin Fowler
Martin Fowler
博客园 - 聂微东
I
InfoQ
B
Blog
IT之家
IT之家
美团技术团队
L
LangChain Blog
小众软件
小众软件
C
Check Point Blog
MongoDB | Blog
MongoDB | Blog
Cyber Security Advisories - MS-ISAC
V
V2EX
Last Week in AI
Last Week in AI
A
About on SuperTechFans
博客园 - Franky
P
Proofpoint News Feed
罗磊的独立博客
月光博客
月光博客
V
Visual Studio Blog
MyScale Blog
MyScale Blog

Cybersecurity Dive - Latest News

Dozens of Red Hat npm packages targeted in supply chain attack Turning tension into collaboration: How CIOs and CISOs can lead together Anthropic shares Mythos with 150 more organizations, including critical infrastructure operators Without strong governance, companies put credit ratings at risk in AI era CISA adds critical Palo Alto Networks firewall flaw to KEV as company, researchers warn of exploitation How Canva scaled to 260+M users while elevating security and productivity Top 4 data security best practices for the AI-enabled enterprise CISA urges security teams to check for software development compromises How CISOs can manage sovereign-cloud security risks IBM’s new $5B initiative will help enterprises rapidly patch open-source vulnerabilities Enterprise data is creeping its way into shadow AI tools Coordinated operation takes down Glassworm botnet Leading AI models are more vulnerable to malicious prompts than vendors claim Iranian government, not hacktivist group, breached LA Metro system, security firm says FBI warns about PhaaS platform used to access Microsoft 365 environments Iran-linked hackers target key US, allied sectors with sophisticated spear-phishing messages New York regulator calls for additional cyber mitigation amid heightened threat environment CISA asks cybersecurity community to alert it to vulnerability exploitation Grafana Labs links GitHub environment breach to TanStack npm supply chain attack 7-Eleven hit by data breach Microsoft disrupts cybercrime operation that hid behind legitimate software Compromised coding tool helped hackers breach thousands of GitHub repositories Telecom sector launches its own private ISAC Patch bypass allows hackers to exploit prior flaw in SonicWall SSL-VPN Grafana Labs says hacker gained access to codebase through leaked token How a government contest launched a revolution in AI-based bug hunting Attackers exploit critical flaw in Cisco Catalyst SD-WAN Controller MSPs need AI to fight AI-fueled cyberthreats: Guardz More money is going to physical security, but it’s often CISOs that oversee it: EY Frontier AI models reap rapid discovery of security vulnerabilities
NIST offers security guidance for water utilities using r...
Eric Geller · 2026-06-25 · via Cybersecurity Dive - Latest News

An article from site logo

Dive Brief

The technology is one of the water sector’s biggest cybersecurity weaknesses.

Published June 25, 2026

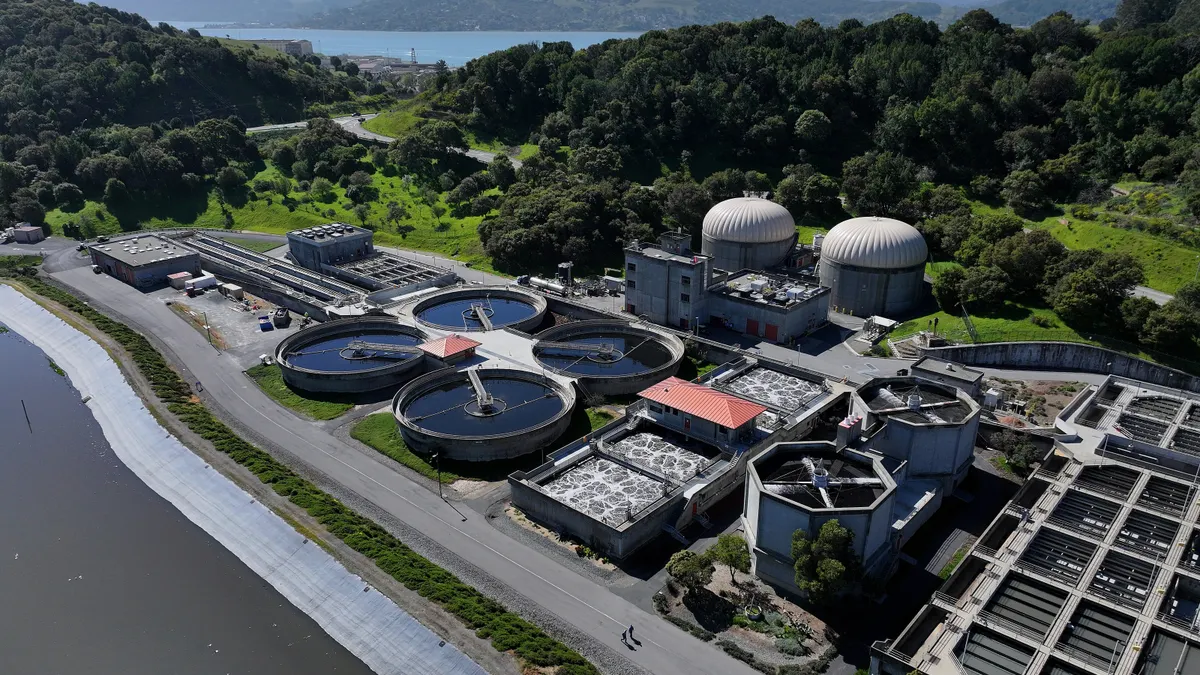
Pools of water are seen in an aerial photo of a wastewater treatment plant

In an aerial view, pools of water are visible at Central Marin Sanitation Agency wastewater treatment plant on March 20, 2024, in San Rafael, Calif. Justin Sullivan via Getty Images

Dive Brief:

  • Water utilities that use remote-access software should carefully restrict access, enforce multifactor authentication (MFA) and maintain comprehensive access logs to help them investigate possible breaches, the National Institute of Standards and Technology (NIST) said in guidance published on Wednesday.
  • The secure remote-access guidance, developed through NIST’s National Cybersecurity Center of Excellence (NCCoE), lists security considerations and describes how water utilities can implement remote access through either on-premises or cloud environments.
  • Remote-access software is one of the water sector’s biggest cybersecurity weaknesses, enabling several Iran-linked cyberattack campaigns against U.S. water systems.

Dive Insight:

NCCoE experts included several example architectures in their guidance document. One illustrates how to set up role-based access controls through the remote-access software TDI ConsoleWorks. Another demonstrates how to use Cisco Duo’s MFA service with the StrongDM access-management platform. A third describes how to use Q-Net Security products to encrypt communications between network devices.

“The ability to provide secure remote access to the water systems is crucial to the efficient operation of today’s [water systems],” the document says. “Each utility should tailor their cybersecurity practices to address the unique needs of its own organization. The goal is to assist the [water] utilities in ensuring the security and availability of remote access capability so that operations can continue uninterrupted, despite current and evolving threats.”

One of the document’s most important sections is a list of security considerations for utilities that want to use remote access. Recommendations include employing least-privilege principles, regularly updating remote-access software to the latest version, carefully inventorying remotely accessible systems (which can help organizations quickly locate and disconnect vulnerable devices) and configuring networks with zero-trust architecture, including packet inspection and demilitarized zones.

NIST recommends organizations first consider alternatives to traditional remote access that carry less risk, such as one-way remote-alarming systems that notify employees of the need to take action. “Some facilities may choose to operate on-site only,” the document says, “requiring employees and contractors to come on-site to perform all operational tasks.”

Water utilities face some of the biggest cybersecurity threats, both because they are among the least-protected infrastructure and because their vital services make them high-value targets for nation-state threat actors. Iran-linked hackers have targeted U.S. critical infrastructure with destructive malware during the war in the Middle East, and China’s Volt Typhoon campaign has breached numerous infrastructure operators over the past several years.

As the threats have grown, the federal government has expanded its scrutiny of water systems’ cybersecurity postures, and volunteer security professionals have deployed across the country to help operators make improvements. But experts say the sector is still woefully unprepared to defend itself.