





An article from

The nation’s top cybersecurity official warned that business leaders, authorities need to rethink how they protect critical infrastructure from state-sponsored adversaries.
Published June 18, 2026

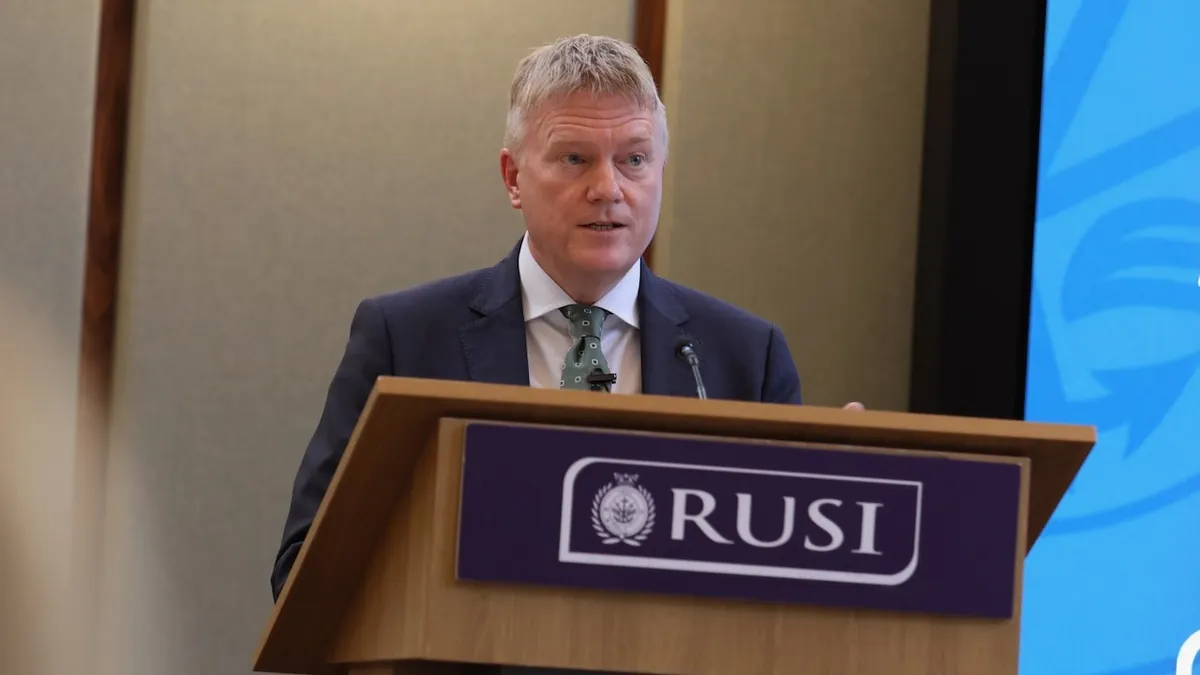
The United Kingdom’s top cybersecurity official warned that nation-state adversaries are believed to be behind the vast majority of the nation’s most serious attacks targeting critical infrastructure over the past year.
In a speech Wednesday, Richard Horne, CEO of the U.K.’s National Cyber Security Centre, said state actors were suspected in about 75% of the 200 attacks against critical sites that it responded to over a 12-month period ending in May.
Horne said the U.K. needs to rethink cybersecurity in a way that moves it from a risk that can be managed to more of a contest that needs to be fought toward victory.
“The stakes in cyber security could not be higher,” Horne said during the annual security lecture before the Royal United Services Institute. “In cyberspace we are not preparing for tomorrow’s conflicts. To some degree we are fighting them today.”
The U.K. has made significant changes in how it views cyber risk over the past year. The country went through a series of catastrophic attacks in 2025, most notably the multi-week disruption of Jaguar Land Rover.
The attack cost the U.K. economy about $2.5 billion as the automaker was forced to pause manufacturing for several weeks and send home thousands of workers from companies in JLR’s extensive supply chain.
U.K. authorities in January warned that pro-Russia groups were targeting critical infrastructure providers and local government entities over the war in Ukraine.
Cloud services and telecommunication environments must be hardened, Horne said, and steps should be taken to disrupt hackers from embedding themselves within these systems. For example, the China-linked threat actor Volt Typhoon burrowed into U.S. critical infrastructure sites throughout 2024 in preparation for potential disruptive attacks.
Horne said corporate leaders and board members needed to gain a better understanding of exposures within their own technology stacks and supply chains. These companies need to build more resilient systems so they can withstand the impact of an attack and maintain critical operations.
U.K. authorities introduced legislation to set minimum cybersecurity standards that are designed to help organizations be more capable of withstanding an attack.
The concerns raised by Horne are similar to many of the same issues facing U.S. critical infrastructure providers.
“Every critical infrastructure operator, no matter where they are located,” should carefully consider the issues raised by Horne, said Annie Fixler, director of the Center on Cyber and Technology Innovation at the Foundation for Defense of Democracies.
“Cyber has become the primary tool for nation-states to undermine rivals while maintaining plausible deniability,” Gary Bartlett, CTO at Illumio, said. “Recent conflicts, including those involving Iran and Russia, have shown how proxy groups can target adversaries and contribute to wider destabilisation efforts.”
Nick Anderson, acting director of the Cybersecurity and Infrastructure Security Agency, echoed similar concerns during an industry conference on Wednesday, noting the U.S. critical infrastructure will face similar risks of disruption.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。