惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

让小产品的独立变现更简单 - ezindie.com
月光博客
月光博客
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
T
Tailwind CSS Blog
大猫的无限游戏
大猫的无限游戏
The Cloudflare Blog
博客园_首页
Jina AI
Jina AI
WordPress大学
WordPress大学
小众软件
小众软件
阮一峰的网络日志
阮一峰的网络日志
Apple Machine Learning Research
博客园 - 三生石上(FineUI控件)
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - 叶小钗
美团技术团队
IT之家
IT之家
爱范儿
爱范儿
有赞技术团队
有赞技术团队
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
量子位
博客园 - 聂微东
人人都是产品经理
人人都是产品经理
博客园 - 【当耐特】

Cybersecurity Dive - Latest News

Dozens of Red Hat npm packages targeted in supply chain attack Turning tension into collaboration: How CIOs and CISOs can lead together Anthropic shares Mythos with 150 more organizations, including critical infrastructure operators Without strong governance, companies put credit ratings at risk in AI era CISA adds critical Palo Alto Networks firewall flaw to KEV as company, researchers warn of exploitation How Canva scaled to 260+M users while elevating security and productivity Top 4 data security best practices for the AI-enabled enterprise CISA urges security teams to check for software development compromises How CISOs can manage sovereign-cloud security risks IBM’s new $5B initiative will help enterprises rapidly patch open-source vulnerabilities Enterprise data is creeping its way into shadow AI tools Coordinated operation takes down Glassworm botnet Leading AI models are more vulnerable to malicious prompts than vendors claim Iranian government, not hacktivist group, breached LA Metro system, security firm says FBI warns about PhaaS platform used to access Microsoft 365 environments Iran-linked hackers target key US, allied sectors with sophisticated spear-phishing messages New York regulator calls for additional cyber mitigation amid heightened threat environment CISA asks cybersecurity community to alert it to vulnerability exploitation Grafana Labs links GitHub environment breach to TanStack npm supply chain attack 7-Eleven hit by data breach Microsoft disrupts cybercrime operation that hid behind legitimate software Compromised coding tool helped hackers breach thousands of GitHub repositories Telecom sector launches its own private ISAC Patch bypass allows hackers to exploit prior flaw in SonicWall SSL-VPN Grafana Labs says hacker gained access to codebase through leaked token How a government contest launched a revolution in AI-based bug hunting Attackers exploit critical flaw in Cisco Catalyst SD-WAN Controller MSPs need AI to fight AI-fueled cyberthreats: Guardz More money is going to physical security, but it’s often CISOs that oversee it: EY Frontier AI models reap rapid discovery of security vulnerabilities
IT sector faces growing threats from IP-hungry China, AI-...
Eric Geller · 2026-06-09 · via Cybersecurity Dive - Latest News

An article from site logo

Dive Brief

Businesses also need to watch out for North Korean remote IT worker schemes, according to a new CrowdStrike report.

Published June 9, 2026

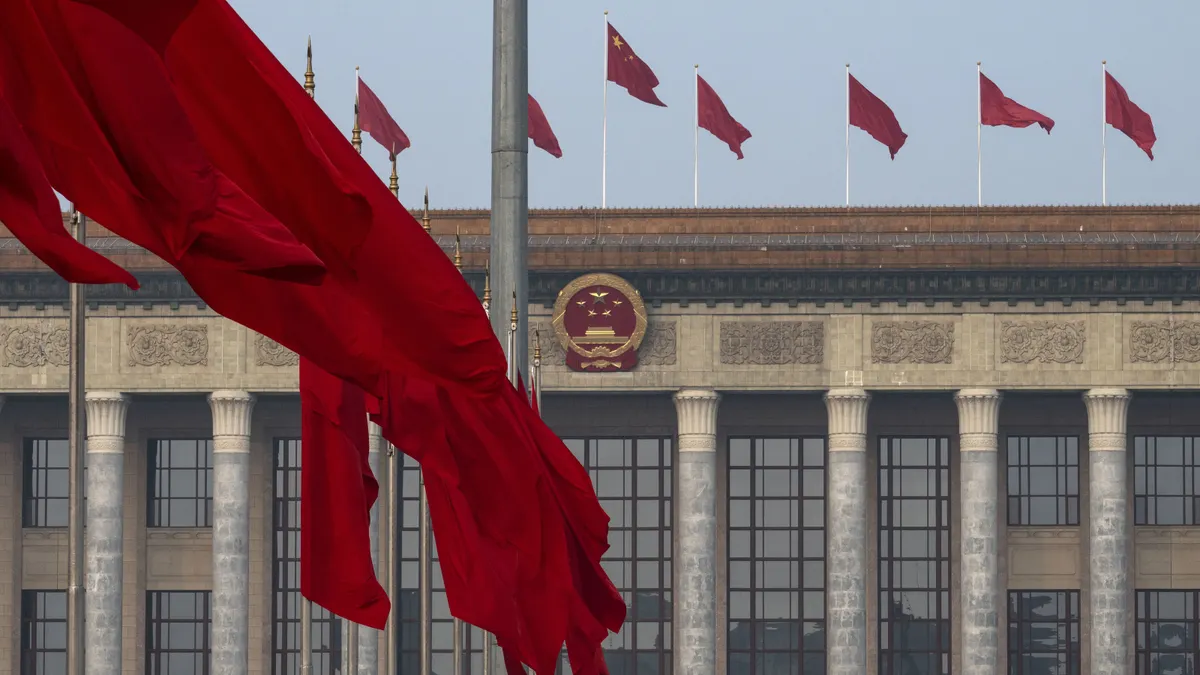
A Chinese flag flutters in front of a Chinese government building, on top of which other Chinese flags are flying

The Great Hall of the People in Beijing, China, is seen on March 10, 2025. A new report described how Beijing was avidly focused on hacking into IT firms to siphon off their intellectual property. Kevin Frayer via Getty Images

Dive Brief:

  • Chinese government-linked hackers represent the most serious threat to companies in the IT sector, CrowdStrike said Tuesday in an annual report about the IT threat landscape.
  • Between April 2025 and March 2026, cyber operatives working for Beijing targeted the technology sector more than any other, according to CrowdStrike’s report, “likely in response to Beijing’s strategic imperative to achieve technological self-sufficiency and competitive advantage in critical emerging technologies.”
  • The new report also describes threats from North Korea, cybercrime gangs and other adversaries.

Dive Insight:

CrowdStrike’s report catalogs the many threat actors that launched significant cyberattacks against the IT sector during the report’s 12-month data collection period, many of them longtime hacker groups that have menaced the sector for years.

Significant China-linked operations include Sunrise Panda’s attacks on “a Southeast Asian technology entity that provides Zimbra solutions to downstream government customers,” Murky Panda’s password-spraying campaign against Microsoft Azure customers (which CrowdStrike said affected more than 340 mostly U.S.-based organizations in a range of sectors) and Warp Panda’s exploitation of VMware vulnerabilities to deploy the Brickstorm malware.

“Technology entities in general serve as a strategic target for China-nexus adversaries,” CrowdStrike analysts wrote, “because access to such entities provides high-value intelligence collection as well as access to downstream customer environments that can enable potential supply chain compromises.”

North Korean actors were also laser-focused on the IT sector. In addition to its remote IT worker schemes, Pyongyang exploited trust relationships between open-source developers to poison widely used packages, enabling far-reaching espionage campaigns. CrowdStrike recounted how North Korean operatives tricked developers into cloning malware-infected Git repositories that enabled the hackers to penetrate macOS and Linux computers.

While China’s activities were worrisome because of their sophistication, North Korea’s were notable because of their volume, CrowdStrike said. One North Korea-linked group, Famous Chollima, was responsible for 47% of all government-linked cyberattacks on IT firms.

Cybercrime activity during the reporting period included Scattered Spider and ShinyHunters attacks, as well as the relatively new group Crimson Collective’s hack of Red Hat Consulting, which allegedly compromised 570 GB of data that included sensitive customer infrastructure and configuration information.

Cybercrime accounted for 65% of attacks on the IT sector during the reporting period, CrowdStrike said. Hacker gangs claimed to be extorting 572 technology companies on their leak websites, while dark-web forums advertised compromises of 277 technology companies, an increase of almost 30% over the previous year. (The forums advertised 4,550 compromises overall.)

AI fueled cybercriminals’ activity, as they used automated tools to generate credential-collection scripts and erase forensic evidence more quickly than defenders could preserve it. Poorly secured AI platforms have also created openings for threat actors. In the first few months of 2026, multiple criminal groups distributed malware — including a new macOS information stealer called Skrawl — using weaknesses in the AI agent OpenClaw.

CrowdStrike said IT firms in North America bore the brunt of cyberattacks during the reporting period, accounting for 45% of intrusions within the sector and 49% of extortion victims posted to data-leak websites.