惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

有赞技术团队
有赞技术团队
Cyber Security Advisories - MS-ISAC
IT之家
IT之家
博客园 - 【当耐特】
罗磊的独立博客
Stack Overflow Blog
Stack Overflow Blog
MyScale Blog
MyScale Blog
WordPress大学
WordPress大学
The GitHub Blog
The GitHub Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
Hugging Face - Blog
Hugging Face - Blog
I
InfoQ
B
Blog RSS Feed
腾讯CDC
云风的 BLOG
云风的 BLOG
N
Netflix TechBlog - Medium
Apple Machine Learning Research
GbyAI
GbyAI
雷峰网
雷峰网
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
D
DataBreaches.Net
The Cloudflare Blog
V
V2EX
S
SegmentFault 最新的问题

Cybersecurity Dive - Latest News

Dozens of Red Hat npm packages targeted in supply chain attack Turning tension into collaboration: How CIOs and CISOs can lead together Anthropic shares Mythos with 150 more organizations, including critical infrastructure operators Without strong governance, companies put credit ratings at risk in AI era CISA adds critical Palo Alto Networks firewall flaw to KEV as company, researchers warn of exploitation How Canva scaled to 260+M users while elevating security and productivity Top 4 data security best practices for the AI-enabled enterprise CISA urges security teams to check for software development compromises How CISOs can manage sovereign-cloud security risks IBM’s new $5B initiative will help enterprises rapidly patch open-source vulnerabilities Enterprise data is creeping its way into shadow AI tools Coordinated operation takes down Glassworm botnet Leading AI models are more vulnerable to malicious prompts than vendors claim Iranian government, not hacktivist group, breached LA Metro system, security firm says FBI warns about PhaaS platform used to access Microsoft 365 environments Iran-linked hackers target key US, allied sectors with sophisticated spear-phishing messages New York regulator calls for additional cyber mitigation amid heightened threat environment CISA asks cybersecurity community to alert it to vulnerability exploitation Grafana Labs links GitHub environment breach to TanStack npm supply chain attack 7-Eleven hit by data breach Microsoft disrupts cybercrime operation that hid behind legitimate software Compromised coding tool helped hackers breach thousands of GitHub repositories Telecom sector launches its own private ISAC Patch bypass allows hackers to exploit prior flaw in SonicWall SSL-VPN Grafana Labs says hacker gained access to codebase through leaked token How a government contest launched a revolution in AI-based bug hunting Attackers exploit critical flaw in Cisco Catalyst SD-WAN Controller MSPs need AI to fight AI-fueled cyberthreats: Guardz More money is going to physical security, but it’s often CISOs that oversee it: EY Frontier AI models reap rapid discovery of security vulnerabilities
AWS unveils agent security, data access tools
Paige Gross · 2026-06-26 · via Cybersecurity Dive - Latest News

An article from site logo

Dive Brief

The updates reflect Anthropic’s Mythos model and the speed at which vulnerabilities can be surfaced.

Published June 26, 2026
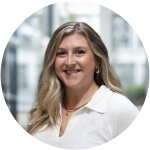
an executive speaks on stage

Swami Sivasubramanian, VP of agentic AI at AWS, speaking June 17, 2026, at the AWS Summit in New York City. The hyperscaler unveiled tools to address cybersecurity concerns as more advanced AI models change the risk landscape. Paige Gross/Cybersecurity Dive

First published on

CIO Dive

Dive Brief:

  • AWS launched agentic tools AWS Continuum, which flags and helps remediate security risks, and AWS Context, a search layer that uses a company’s data to make better informed agents, at its AWS Summit in New York City on June 17.
  • The company rolled out the tools as the rise in AI agents is rapidly changing the way enterprises operate, reshaping the cybersecurity landscape and necessitating tools that connect siloed data.
  • AWS rolled out new capabilities for AI tools Kiro, AWS DevOps Agent, AWS Transform for modernization and Amazon Bedrock AgentCore to build and deploy agents. It also updated Amazon Quick, an agentic assistant-modeled AI application, which was released as Quick Suite last year.

Dive Insight: 

Enterprises have shifted from talking about and piloting AI agents to relying on them to complete large swaths of their work, said Swami Sivasubramanian, VP of Agentic AI at AWS, during the company’s keynote on June 17

“If your teams are still waiting on you to connect the dots, if humans are still forced to be the orchestration layer, your momentum actually passes you,” Sivasubramanian said.

With this shift comes the need for companies to strengthen and tune their data and agents, which is what AWS Context aims to achieve, Sriram Devanathan, director of agentic AI and software modernization at AWS, told CIO Dive in an interview. 

The service builds a knowledge graph from a company’s existing data, including business rules and domain knowledge, that teaches agents how to navigate the stores of an organization’s knowledge and find the right answer. It acts as an agentic search layer for an organization that is connected to all agents and has built-in governance, according to AWS.

Agents, whether for security or DevOps, are helping to automate parts of a company’s software development life cycle, Devanathan told CIO Dive. At some point, they need to talk to each other, he said.  

“All of our agents, at some level, need to understand which apps are important, which apps need high priority fixes, where they run, how they run, how they are built,” he said. 

AWS Continuum is the company’s response to the release of Anthropic Mythos and Claude Fable, Chet Kapoor, VP of security services and observability at AWS, said during the keynote. The AI security service discovers security threats, informs leadership of where to act, validates solutions in a sandbox and makes recommendations for remediating security risks. 

“I call it, ‘The Mythos moment,’” Kapoor said. “It accelerated our plans significantly. Mythos set a new bar for finding vulnerabilities.”