惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

L
LangChain Blog
B
Blog RSS Feed
阮一峰的网络日志
阮一峰的网络日志
Cyber Security Advisories - MS-ISAC
H
Help Net Security
MyScale Blog
MyScale Blog
WordPress大学
WordPress大学
Microsoft Azure Blog
GbyAI
GbyAI
小众软件
小众软件
大猫的无限游戏
大猫的无限游戏
Martin Fowler
Martin Fowler
Vercel News
Vercel News
S
SegmentFault 最新的问题
M
MIT News - Artificial intelligence
Microsoft Security Blog
G
Google Developers Blog
Last Week in AI
Last Week in AI
Hugging Face - Blog
Hugging Face - Blog
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - 【当耐特】
Google DeepMind News
Engineering at Meta
Engineering at Meta
云风的 BLOG
云风的 BLOG

Cybersecurity Dive - Latest News

Dozens of Red Hat npm packages targeted in supply chain attack Turning tension into collaboration: How CIOs and CISOs can lead together Trump signs EO seeking early government access to powerful AI models Anthropic shares Mythos with 150 more organizations, including critical infrastructure operators Without strong governance, companies put credit ratings at risk in AI era CISA adds critical Palo Alto Networks firewall flaw to KEV as company, researchers warn of exploitation How Canva scaled to 260+M users while elevating security and productivity Top 4 data security best practices for the AI-enabled enterprise CISA urges security teams to check for software development compromises How CISOs can manage sovereign-cloud security risks IBM’s new $5B initiative will help enterprises rapidly patch open-source vulnerabilities Enterprise data is creeping its way into shadow AI tools Coordinated operation takes down Glassworm botnet Leading AI models are more vulnerable to malicious prompts than vendors claim Iranian government, not hacktivist group, breached LA Metro system, security firm says FBI warns about PhaaS platform used to access Microsoft 365 environments Iran-linked hackers target key US, allied sectors with sophisticated spear-phishing messages New York regulator calls for additional cyber mitigation amid heightened threat environment CISA asks cybersecurity community to alert it to vulnerability exploitation Grafana Labs links GitHub environment breach to TanStack npm supply chain attack 7-Eleven hit by data breach Microsoft disrupts cybercrime operation that hid behind legitimate software Compromised coding tool helped hackers breach thousands of GitHub repositories Telecom sector launches its own private ISAC Patch bypass allows hackers to exploit prior flaw in SonicWall SSL-VPN Grafana Labs says hacker gained access to codebase through leaked token How a government contest launched a revolution in AI-based bug hunting Attackers exploit critical flaw in Cisco Catalyst SD-WAN Controller MSPs need AI to fight AI-fueled cyberthreats: Guardz More money is going to physical security, but it’s often CISOs that oversee it: EY
OpenAI launches Daybreak to combat cyber threats
Paige Gross · 2026-05-13 · via Cybersecurity Dive - Latest News

An article from site logo

Dive Brief

The cybersecurity initiative uses AI to detect software vulnerabilities, partnering with Cloudflare, Cisco and CrowdStrike to counter threats.

Published May 13, 2026
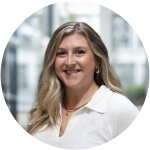
Sam Altman speaks in a conference setting

OpenAI CEO Sam Altman speaks during Snowflake Summit 2025 at Moscone Center on June 2, 2025 in San Francisco. The company announced a cybersecurity initiative called Daybreak on May 11, 2026. Justin Sullivan via Getty Images

First published on

CIO Dive

Dive Brief:

  • OpenAI on Monday launched a new cybersecurity initiative called Daybreak, which uses its large language models, Codex’s agentic capabilities and security partners to root out risk and call defense into action. The rollout is OpenAI’s answer to Anthropic’s Mythos model which debuted to limited preview last month and has highlighted weak security spots in software across various industries. 
  • Like with Anthropic’s Project Glasswing, which sought tech vendors to support Mythos, OpenAI will work with industry and government partners to deploy cyber-capable models that are meant to build autonomous cyber defense capabilities into software from the start. Cloudflare, Cisco, CrowdStrike, Oracle and Zscaler are among a group of companies already using the technology, OpenAI said. Unlike Mythos, Daybreak is publicly available, and companies can request an assessment of their security risks.
  • As AI providers compete for their share of the enterprise market with cybersecurity tools, tech leaders should experiment with all of their options, said Jeff Pollard, VP, principal analyst at Forrester, in an email to CIO Dive. “Take someone with responsibility for innovation in tech and cybersecurity and have them play with these capabilities to see what they offer,” he said.

Dive Insight:

Anthropic’s Mythos put the SaaS world on pause last month as a preview of the technology revealed major existing vulnerabilities in the world’s software infrastructure. It raises a growing concern about how AI is accessing information and how capable companies are in defending against risk. 

“What we know is that AI can help solve problems, and the lag time between finding, developing fixes and deploying fixes takes way too long,” Pollard said. “Especially when adversaries use AI to scale attacks. This is a way to use AI to help on that front.”

Daybreak is meant to work in three stages, OpenAI said. First, it prioritizes high-impact threats with AI reasoning and token usage; then, it generates and tests risks directly within an enterprise with scoped access, monitoring and review. The final stage involves sending audit-ready evidence to help enterprises track, validate and remedy the vulnerability. 

OpenAI’s Daybreak competes more directly with application security, posture management and AI-enabled application security testing capabilities, said John Watts, VP analyst at Gartner, in an email to CIO Dive.

“We believe that it will complement usage of these tools rather than fully replace them,” Watts said. “Organizations must deploy resources across the entire remediation kill chain, including patch testing, deployment and roll-back, to reduce impact to operations when patching rather than solely on [application security agent] Codex Security.”

For enterprise tech leaders, it’s time to reevaluate security tech portfolios and consider what the AI providers are offering in comparison with legacy cybersecurity vendors, Pollard said. 

He added that it’s important to remember that AI companies need people to consume their products, buy subscriptions and use tokens. 

“This is one way to accomplish that,” he said. “And the simultaneous announcements of consulting firms for enablement shows that AI companies want to do the AI, not the enablement work that comes along with it.”

OpenAI launched a standalone consulting business on Monday to provide organizations with AI adoption assistance and to send teams of forward-deployed engineers into the field and deepen its bench of AI talent via acquisitions. Last week, Anthropic launched its own enterprise AI services company with a slate of private equity companies.