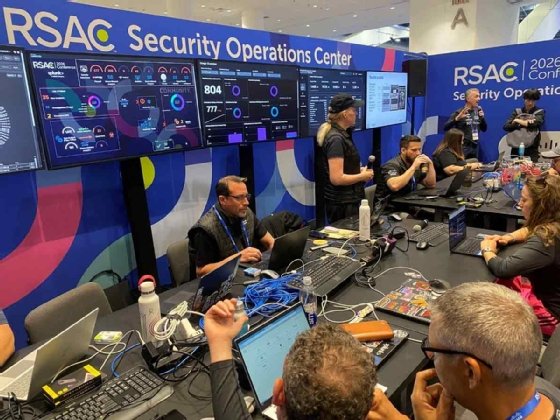
Machines whirr and whizz behind the partitioned wall in the RSAC 2026 Conference expo hall. Five side-by-side monitors flash colorful alerts, charts and statistics. A dozen analysts sit around two tables, their eyes glued to sticker-covered laptops.
It's a glimpse inside the security operations center (SOC) protecting the world's largest cybersecurity event live and in action, monitoring north-south and east-west traffic across the Moscone Center in San Francisco.
The SOC team, made up of Cisco, Splunk and Endace members, is investigating incidents on the network where nearly 44,000 attendees have gathered to learn and chat about cybersecurity and, more than likely, connect to the event's free Wi-Fi.
"We're recording everything that goes across the network. We have about 240 TB of storage here, so we'll record every packet from the start of the show, right to the end," said Cary Wright, vice president of products at Endace. "These analysts can dig in and investigate any event or incident and look at exactly what happened before, during and after it."
The analysts are on the hunt for zero days, insecurities, advanced threats and any other suspicious activity that might not trigger the security stack.
The technology
The preconfigured SOC in a box, developed for RSAC, was designed to be rolled into a venue, connected to the network operations center, and up and running in fewer than four hours.
Two Cisco Unified Computing Systems with embedded AI and GPUs provide local compute for event services and virtualization needs. A pair of Cisco Secure Firewalls with Firewall Threat Defense run in detection mode at the network edge, and Endace appliances perform always-on -- not triggered -- full packet capture and generate metadata, including Zeek logs.
Telemetry is fed into the security stack through Splunk Enterprise Security, and Splunk Attack Analyzer conducts detonation and analysis. Pivots enable analysts to rapidly move across tools and workflows.
"If a firewall detected a threat, for example, the analyst could pivot to see what network packets were related to the threat, if there was lateral movement, if any data was downloaded or exfiltrated, or if any malware was coming out of the network," Wright said.
Additional tools include Cisco XDR (extended detection and response); Cisco Secure Network Analytics; Cisco Security Cloud; Splunk Cloud Platform; Cisco Duo; Cisco ThousandEyes; Cisco Secure Malware Analytics; Splunk Attack Analyzer; Cisco Secure Access and Splunk SOAR (security orchestration, automation and response); and threat intelligence from Cisco Talos, alphaMountain, Pulsedive and StealthMole.
The dashboards
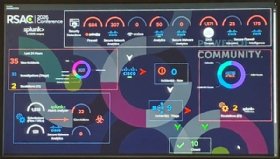
One screen displays a representation of traffic over the past three days -- a spider chart shows who was talking to whom, with the thickness of the lines indicating traffic volume.
Another screen shows traffic being analyzed by Splunk. Twenty percent of the traffic is encrypted, and the dashboard shows encryption strengths, including which TLS versions are in use.
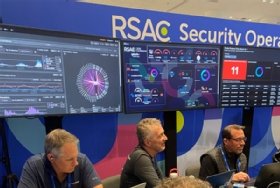
A screen flashes password counts and password events, revealing that 11 hosts on the network are broadcasting their passwords in the clear. There are a total of 217 events, meaning each host showed their password about 20 times.
During previous events, Wright explained, they'd investigate, find the relevant user and tell them that their password was insecure. This time-consuming process was recently automated, with hosts now receiving an email from RSAC informing them that their passwords were found in the clear.
RSAC attendees demonstrated better password hygiene than those at Cisco Live in Amsterdam -- Jessica Oppenheimer, director of SOC integrations at Splunk, said 400 hosts there had passwords in cleartext.
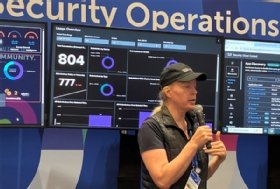
Another screen displays which AI models people are using. "Are they ones we've licensed? Ones that should be licensed? Are they using their own?" Oppenheimer said. "We can identify models on the network, and if one were to adversely affect this conference, we have the ability to block it."
AI is a big component of the SOC itself. For example, it helps tier-one analysts process data, understand threats and map data. "That's why in the past 24 hours only two of 35 alerts have been escalated up to tier-two or three analysts," she said.
SOC in a box around the globe
The SOC in a box rolled into RSAC 2026 from Cisco Live 2026 in Amsterdam, after remotely protecting the NFL Super Bowl in Santa Clara in February. It has also been used at the Olympics, Black Hat, Mobile World Congress and GovWare events. In April, it will protect the network during the NFL Draft in Pittsburgh.
The SOC in a box continuously evolves. Previous iterations of the project took incident responders three days to gain access, given the various tools from Palo Alto, Corelight, Arista Networks and Jamf, Oppenheimer explained. In response, the team created a single sign-on portal and implemented role-based access control to provide day-one access to all analysts.
For the 2028 LA Olympics, Oppenheimer said, the team is looking to add additional AI capabilities into the SOC.
Sharon Shea is executive editor of TechTarget Security.