
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

D
Docker
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - Franky
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
A
About on SuperTechFans
博客园 - 【当耐特】
Microsoft Security Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
The GitHub Blog
The GitHub Blog
雷峰网
雷峰网
博客园_首页
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
IT之家
IT之家
博客园 - 叶小钗
Google DeepMind News
aimingoo的专栏
aimingoo的专栏
博客园 - 聂微东
B
Blog RSS Feed
H
Help Net Security
Recent Announcements
阮一峰的网络日志
阮一峰的网络日志
D
DataBreaches.Net
L
LangChain Blog
Vercel News
Vercel News

Cisco Blogs

Edge opportunity for service providers: Turn infrastructure into new services MRC and SRv6: How Foundational Networking Innovations Are Enabling the Next Generation of AI Supercomputers The SMB Marketing Reset: Winning Customer Trust in a Digital-First Economy Inside the SOC: AI-powered DNS defense against ransomware Our Path Forward Securing the Federal Digital Experience with Cisco ThousandEyes for Government Cisco at ONUG Dallas 2026: Securing the AI Data Center in the Agentic Era Cisco and Red Hat are powering intelligent core to edge: Red Hat Summit insights Building the Capabilities That Win: How Cisco Partners Can Lead in the SMB & Mid-Market Era How Two Hours Felt Bigger Than My To-Do List Announcing Foundry Security Spec Ace the CCIE Collaboration Lab: Success Tips from a TAC Engineer Turned CCIE Protecting Agents with Cisco AI Defense and Google Agent Development Kit Powering an Inclusive Future: Your guide to the Purpose Pavilion at Cisco Live Las Vegas The Infrastructure Behind the Mission: SOF Week 2026 Cisco Networking App Marketplace Partners at Cisco Live 2026 Beyond the Pilot: Building the Clinical Data Fabric for the Agentic Era Benchmarking scale-out AI fabrics with Cisco N9000 + AMD Pensando™ Pollara 400 NICs Month of Developer Productivity: Build and Forget The race to autonomous transport networks: A new study Lean IT, future-ready: How to save time and simplify wireless management with AI Reading Between the Pixels: Failure Modes in Vision Language Models Biochar’s triple win: Healthier soils, improved crops, and decarbonization Designing a Proactive Customer Journey Modernize your data center operations with Cisco Nexus Dashboard Why your automation stack needs Cisco Agentic Workflows Try Cisco AI Defense Explorer Edition in this hands-on lab From Bandwidth to Intelligence: How Cisco is Powering AI-Ready Networks Spotlight on digital transformation | FY25 Purpose Report Galaxy Mode is live: A limited-time look at what your Cisco AI Assistant and AgenticOps can already do
Uplevelling Black Hat Threat Hunters
Aditya Raghavan · 2026-06-23 · via Cisco Blogs

At Black Hat, every new data source is a trade-off.

More telemetry means better visibility – but also more data for threat hunters to sift through.

From SMA to SAA: Same Need, Different Problem

Recently, Splunk Attack Analyzer (SAA) superseded Secure Malware Analytics (SMA) as the official malware threat analysis platform at Black Hat. 

With SMA, we had a simple and effective pattern: 

  • Submissions exceeding a score threshold
  • Automatically surfaced to the Threat Hunters’ incident queue on Cisco XDR

It worked well. So naturally, we wanted the same outcome with SAA.

SAA provides granular data across multiple sourcetypes, allowing for significant flexibility in how information is presented. By mapping these data streams together, we tailored our reporting to deliver a comprehensive, cohesive view of our threat landscape.

The Turning Point: Collaboration

This is where David and Lily stepped in. They built a query that:

  1. Extracts submission metadata (URL, Job ID, engines used)
  2. Uses the Job ID to retrieve high-scoring results (≥85)
  3. Joins and reshapes both datasets into a single, usable structure

This was a transformative shift. By tailoring our configuration to meet our specific requirements, we unlocked a new level of visibility. This approach delivered the deep, actionable insights necessary to optimize our workflow.

Building the Workflow

With the query ready, the focus shifted to automation.

Instead of starting from scratch, we reused existing ingestion components and adapted them for this data structure.
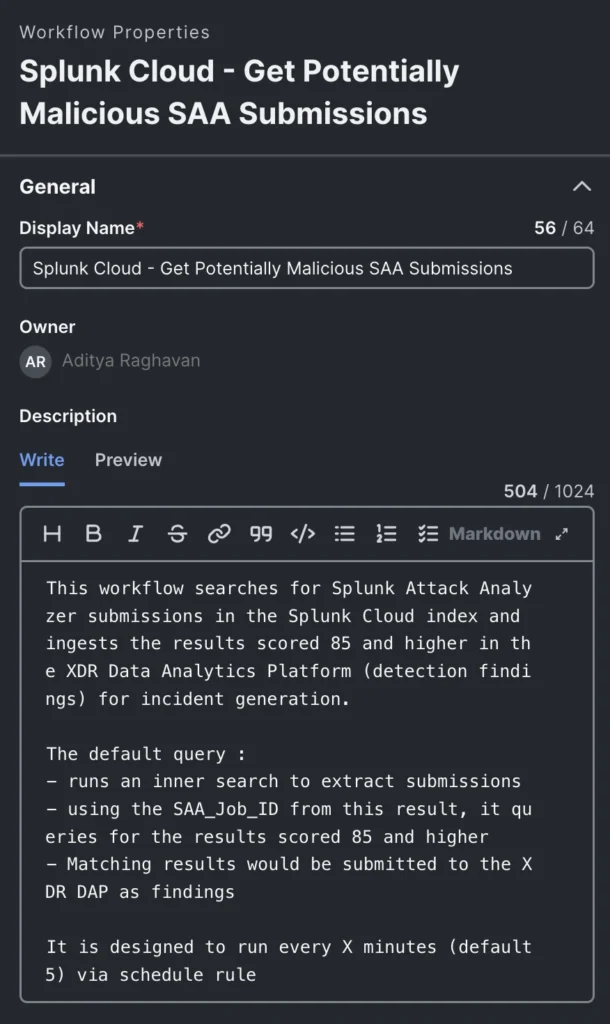
Building the workflow

Then came an important decision: Focus on what matters for detection of threats at Black Hat. 

SAA can accept any file format and URLs for analysis which means we saw many protocols being used, including:

  • HTTP 
  • FTP 
  • POP3/SMTP

But only HTTP had meaningful volume and relevance for the event.

So, we cut the rest. POP3/SMTP would get a chance next time around.

This was precision – prioritizing impact over completeness.

Enriching with Network Context and reducing noise 

A file submitted via HTTP doesn’t exist in isolation – it has network context. So, we enriched each submission with:

  • Related traffic telemetry
  • Directionality
  • Action context (allowed vs blocked)

This turned isolated results into something threat hunters could actually investigate.
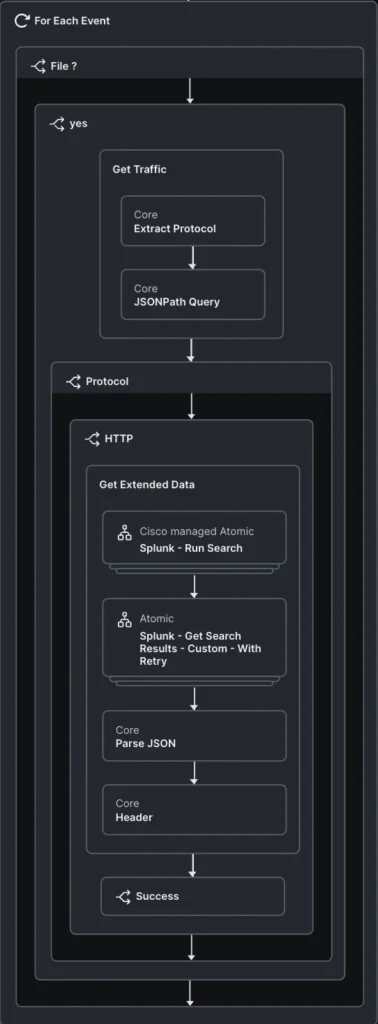
EnrichingWithNetworkContext

At this stage, we hit familiar challenges: 

  • Timestamp normalization (epoch → RFC3339)
  • Action context extraction (allowed vs blocked)
  • Traffic directionality

All necessary for proper ingestion into XDR.

One issue nearly derailed the correlation logic. Traffic originating from internal zones was routed through zScaler, resulting in:

  • Shared destination IPs
  • Multiple unrelated events bundled together

This could create false correlations – exactly the noise we were trying to avoid.

The fix? A targeted exception to filter it out.

Highly customized – but effective.

The Outcome: Better Signals for Hunters 

The workflow produced a new detection stream in Cisco XDR – powered by SAA submissions, enriched with network context.
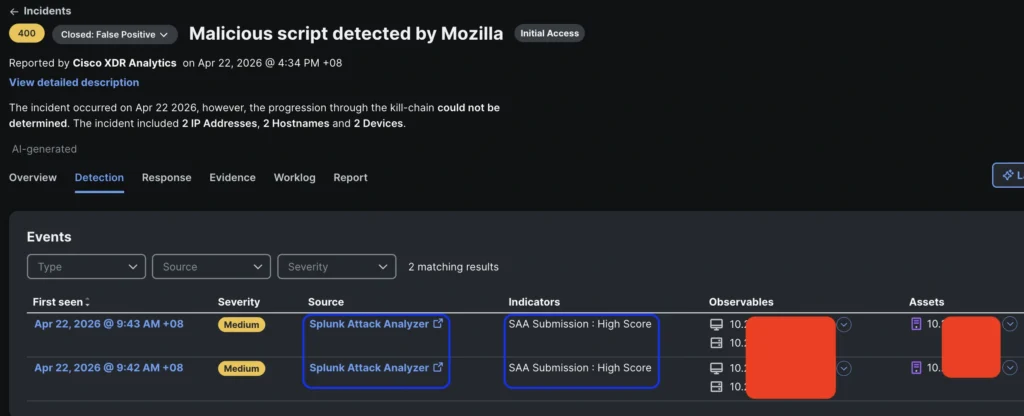
Malicious script detected by mozilla

At first glance, some alerts looked critical based on their attributes of: 

  • High scores
  • Multiple internal systems involved
  • Suspicious JavaScript obfuscation behaviour

But investigation told a different story. 

A legitimate Twitter embed. Flagged by heuristics. 

False positive. And that’s the point. 

With proper context and analysis from Attack Storyboard, the team quickly validated and dismissed it.
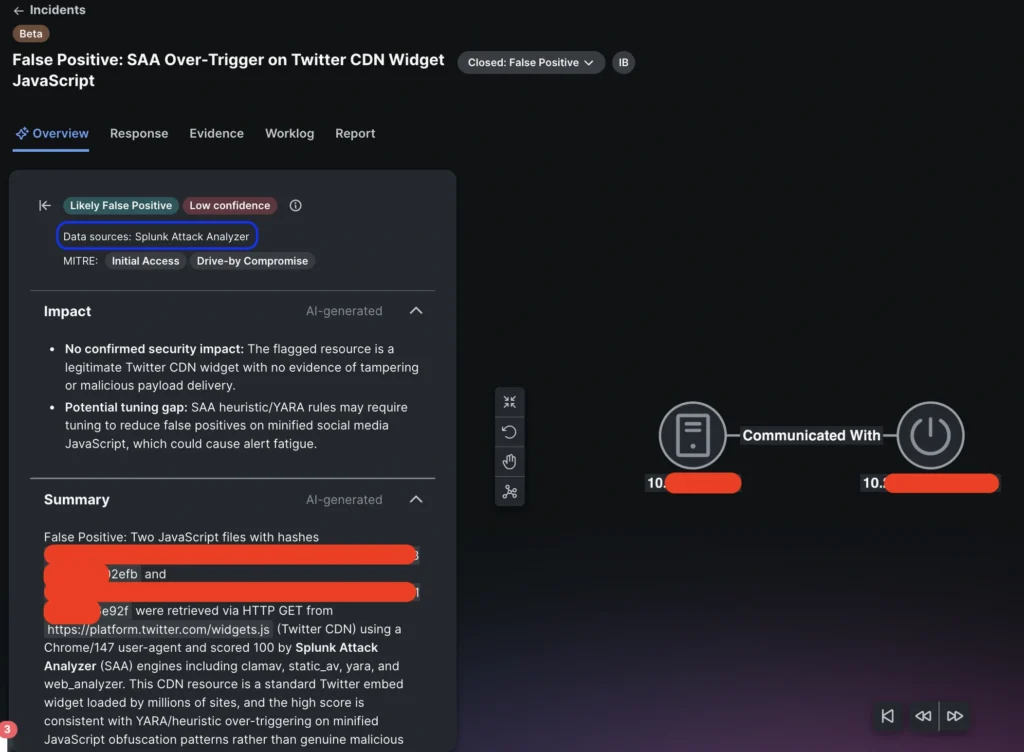
CDN Widget

And that’s the real win. This workflow wasn’t about adding another data source. 

It was about:

  • Surfacing high-risk submissions automatically
  • Providing network context for faster triage
  • Helping threat hunters dismiss noise faster

This workflow is far from perfect. It will evolve, just like everything else we build at Black Hat. 

“In the end, the best detection isn’t the highest scored one – it’s the one you can act on.” 

Check out the other blogs from our team at Black Hat Asia 2026. 

About Black Hat 

Black Hat is the cybersecurity industry’s most established and in-depth security event series. Founded in 1997, these annual, multi-day events provide attendees with the latest in cybersecurity research, development, and trends. Driven by the needs of the community, Black Hat events showcase content directly from the community through Briefings presentations, Trainings courses, Summits, and more. As the event series where all career levels and academic disciplines convene to collaborate, network, and discuss the cybersecurity topics that matter most to them, attendees can find Black Hat events in the United States, Canada, Europe, Middle East and Africa, and Asia. For more information, please visit www.Black Hat.com.


We’d love to hear what you think! Ask a question and stay connected with Cisco Security on social media.

Cisco Security Social Media

LinkedIn
Facebook
Instagram