


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

aimingoo的专栏
aimingoo的专栏
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
Blog — PlanetScale
Blog — PlanetScale
博客园 - Franky
The GitHub Blog
The GitHub Blog
F
Fortinet All Blogs
Microsoft Azure Blog
I
InfoQ
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
T
Tailwind CSS Blog
博客园 - 三生石上(FineUI控件)
Apple Machine Learning Research
D
Docker
Google DeepMind News
GbyAI
GbyAI
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
P
Proofpoint News Feed
N
Netflix TechBlog - Medium
H
Hackread – Cybersecurity News, Data Breaches, AI and More
Engineering at Meta
Engineering at Meta
H
Help Net Security
B
Blog
宝玉的分享
宝玉的分享

Cisco Blogs

Cisco Live 2026: Bringing the Future of Customer Experience to Las Vegas Edge opportunity for service providers: Turn infrastructure into new services MRC and SRv6: How Foundational Networking Innovations Are Enabling the Next Generation of AI Supercomputers The SMB Marketing Reset: Winning Customer Trust in a Digital-First Economy Inside the SOC: AI-powered DNS defense against ransomware Our Path Forward Securing the Federal Digital Experience with Cisco ThousandEyes for Government Cisco at ONUG Dallas 2026: Securing the AI Data Center in the Agentic Era Cisco and Red Hat are powering intelligent core to edge: Red Hat Summit insights Building the Capabilities That Win: How Cisco Partners Can Lead in the SMB & Mid-Market Era How Two Hours Felt Bigger Than My To-Do List Announcing Foundry Security Spec Ace the CCIE Collaboration Lab: Success Tips from a TAC Engineer Turned CCIE Protecting Agents with Cisco AI Defense and Google Agent Development Kit Powering an Inclusive Future: Your guide to the Purpose Pavilion at Cisco Live Las Vegas The Infrastructure Behind the Mission: SOF Week 2026 Cisco Networking App Marketplace Partners at Cisco Live 2026 Beyond the Pilot: Building the Clinical Data Fabric for the Agentic Era Benchmarking scale-out AI fabrics with Cisco N9000 + AMD Pensando™ Pollara 400 NICs Month of Developer Productivity: Build and Forget The race to autonomous transport networks: A new study Lean IT, future-ready: How to save time and simplify wireless management with AI Reading Between the Pixels: Failure Modes in Vision Language Models Biochar’s triple win: Healthier soils, improved crops, and decarbonization Designing a Proactive Customer Journey Modernize your data center operations with Cisco Nexus Dashboard Why your automation stack needs Cisco Agentic Workflows Try Cisco AI Defense Explorer Edition in this hands-on lab From Bandwidth to Intelligence: How Cisco is Powering AI-Ready Networks Spotlight on digital transformation | FY25 Purpose Report
Powering MWC Barcelona – Building a Unified SOC and NOC w...
2026-04-09 · via Cisco Blogs

Mobile World Congress (MWC) Barcelona is one of the most demanding environments for network and security operations. With thousands of attendees, unmanaged devices, and applications interacting in real time, operational visibility and threat detection must function flawlessly.

For the 2nd year, the Cisco team leveraged Splunk, in addition to its other security products, to deliver a unified Security Operations Center (SOC) and Network Operations Center (NOC) experience. Together, we used Splunk as the central data platform and integrating telemetry across a broad set of Cisco technologies.

What made this deployment particularly notable was not just the breadth of integrations, but the speed and flexibility with which we operationalized the environment.
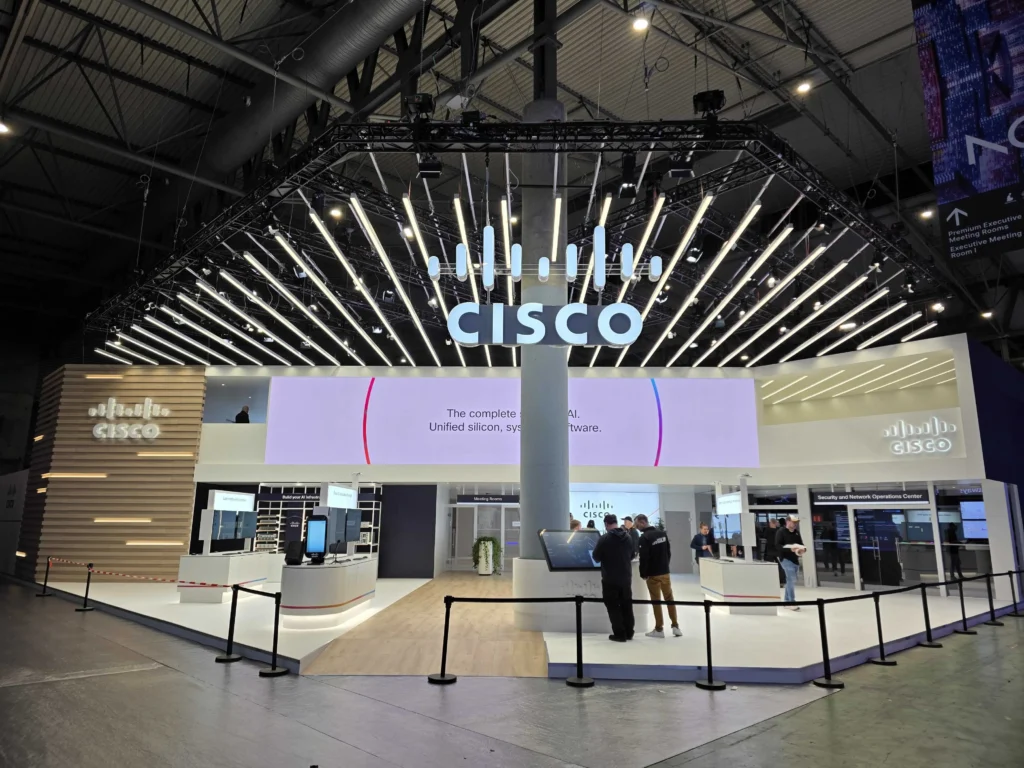
Cisco booth setup
People getting the Cisco booth in preparation for Mobile World Congress 2026

The Architecture: A Unified Operations Platform

At the core of the deployment was Splunk Cloud, acting as the single pane of glass for both SOC and NOC workflows.

We ingested data from multiple Cisco platforms, including:
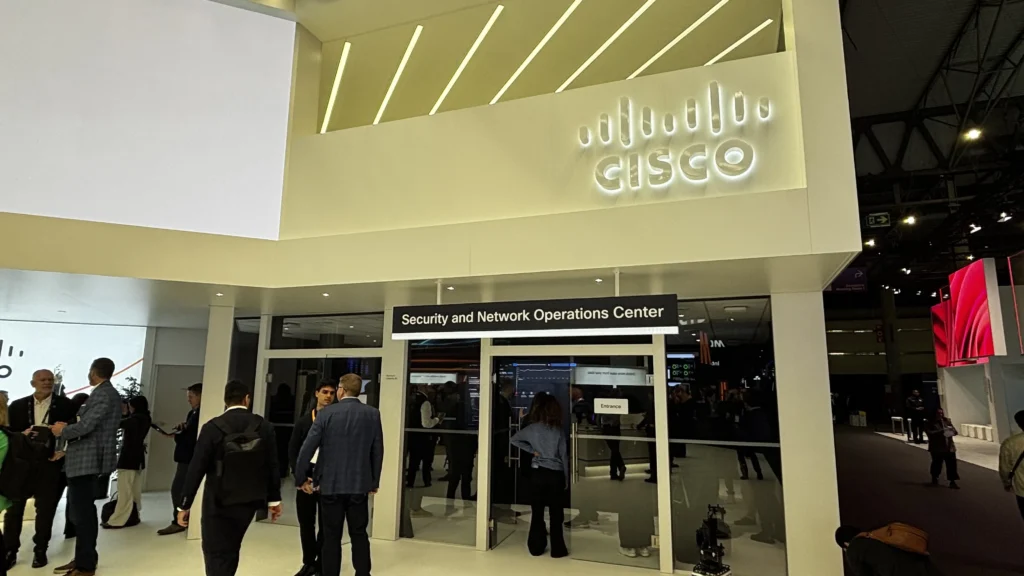
MWC 2026 NOC
The SOC and NOC area at Mobile World Congress 2026 

This architecture allowed us to converge traditionally siloed operational domains into a single analytics layer, enabling faster correlation between network events and security incidents.
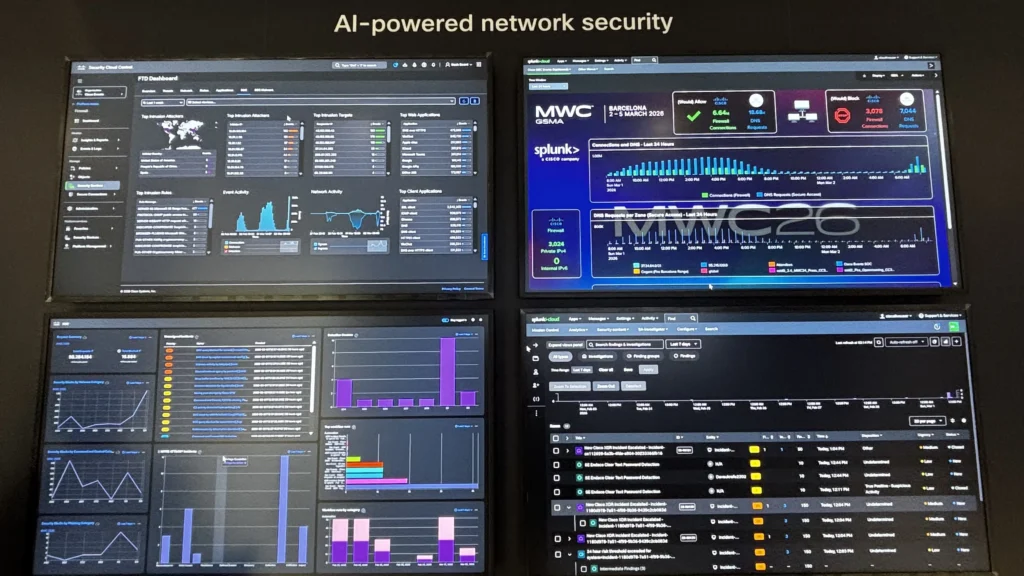
MWC 2026 SOC dashboards
Clockwise from the upper left quadrant: Firepower in Security Cloud Control, Splunk Cloud dashboard for MWC, Splunk Enterprise Security Mission Control and Cisco XDR.

Building NOC Dashboards in an Afternoon

One of the most impactful outcomes was how quickly we were able to deliver operational visibility following various requests from other teams present at the event.

Using Splunk’s data platform and visualization capabilities, we were able to build a fully functional NOC dashboard in just a few hours. The dashboard provided:

  • Real-time network usage and availability
  • Client connectivity metrics across wireless and wired environments
  • Application usage indicators

Because all telemetry was collected within Splunk, creating meaningful dashboards required minimal transformation work. This highlights a key advantage of using a unified data platform: once ingestion is solved, insights can follow quickly.
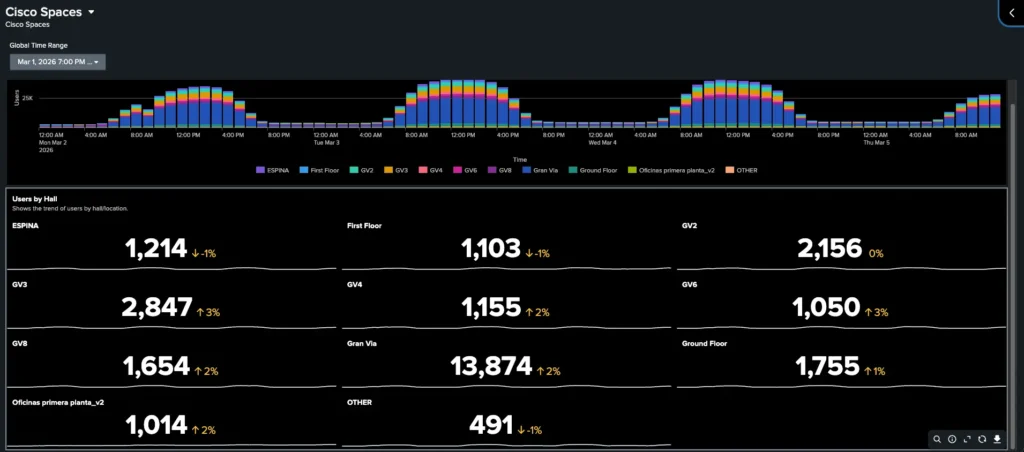
MWC 2026 Cisco space dashboard
One of the dashboards built using Splunk to track Cisco Spaces users across the venue.

Bridging SOC and NOC: From Visibility to Context

Traditionally, SOC and NOC teams operate in parallel, often using separate tools and datasets. At MWC, we intentionally broke down that barrier.

By leveraging Splunk as the common platform:

  • NOC events (e.g., latency spikes, usage trends) could be correlated with
  • SOC signals (e.g., anomalous traffic patterns, threat detections)

This convergence enabled faster root cause analysis and reduced mean time to resolution (MTTR), particularly in scenarios where performance issues or traffic anomalies had potential security implications.

A First: Deploying the Cisco 6160 Firewall in a Public Event

A standout aspect of this deployment was the use of the Cisco Secure Firewall 6160—marking its first deployment in a public event environment.

Bringing this data into Splunk required a bit of engineering:

Data Pipeline Design

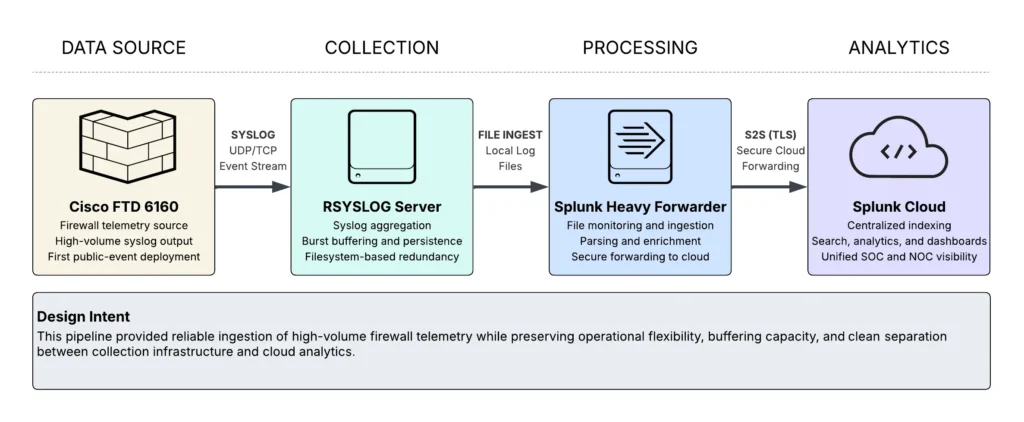
Because of the scale and performance characteristics of the firewall, we implemented a structured ingestion pipeline:

  1. RSYSLOG Server
    • Acted as the initial log aggregator source for the firewall
    • Handled high-throughput syslog ingestion from the 6160
    • Provided buffering and normalization capabilities
    • Saved data on the file system, providing another layer of redundancy
  2. Splunk Heavy Forwarder (HF)
    • Consumed logs from files produced by RSYSLOG
    • Applied parsing, filtering, and metadata enrichment
    • Forwarded processed data securely to Splunk Cloud using the S2S protocol
  3. Splunk Cloud
    • Centralized indexing and analytics
    • Enabled both SOC and NOC use cases

The following diagram illustrates the ingestion pipeline used to reliably transport high-volume firewall telemetry into Splunk Cloud:
MWC 2026 blog diagram CC
Figure: Firewall telemetry ingestion pipeline used at MWC 2026, showing the flow from Cisco FTD 6160 through RSYSLOG and Splunk Heavy Forwarder into Splunk Cloud for centralized SOC and NOC analytics

Why This Approach Worked

  • Scalability & Resiliency: RSYSLOG absorbed burst traffic without dropping events and created a local copy of log files
  • Flexibility: The Heavy Forwarder allowed us to control parsing/filtering before ingestion, should we need to
  • Cloud Integration: Clean separation between on-prem data collection and cloud analytics

This pipeline ensured reliable ingestion of high-volume firewall telemetry while maintaining performance and data integrity.

Lessons Learned

A few key takeaways from the deployment:

  • Unification accelerates operations

    Bringing SOC and NOC data into a single platform improves operations and makes new insights possible

  • Data onboarding is the hardest—and most important—step

    Once data is flowing and normalized, building dashboards and detections becomes significantly easier.

  • Edge engineering still matters in cloud-first architectures

    Components like RSYSLOG and Heavy Forwarders remain critical for handling real-world data ingestion challenges.

  • Speed is achievable with the right abstractions

    Building a production-grade NOC dashboard in hours—not days—is realistic when the platform is designed for it.

Check out the lessons learned from the Event SOCs we deploy around the world, with the white paper and latest blogs.


We’d love to hear what you think! Ask a question and stay connected with Cisco Security on social media.

Cisco Security Social Media

LinkedIn
Facebook
Instagram