


Serving tech enthusiasts for over 25 years.
TechSpot means tech analysis and advice you can trust.
Editor's take: Microsoft has increasingly turned Windows Update into a point of frustration for some users, all while cybercriminals continue to exploit weaknesses in the Windows platform to deploy more sophisticated threats. The situation becomes even more complex when additional layers of code obfuscation are introduced.
Malwarebytes recently uncovered a new malicious campaign targeting the Windows Update service. Focused on French-speaking users, the campaign uses layered obfuscation techniques to deliver multiple malicious payloads built with legitimate tools. The malware's primary goal is to steal passwords and other sensitive user data.
The attackers lure victims with a convincing imitation of a Windows Update web page. The fake site prompts users to download what appears to be an important update for Windows 11 24H2, allegedly containing critical security fixes. The download is actually a large Windows Installer package named "WindowsUpdate 1.0.0.msi."
According to Malwarebytes, the MSI package was created using the legitimate open-source WiX Toolset. When executed via the Windows shell, it installs an Electron application containing obfuscated JavaScript code. The malware conceals its true intent behind multiple layers of obfuscation, leveraging Electron, JavaScript, Visual Basic, and Python to evade security software and Windows protections.
The concealment appears to have been effective, as no major antivirus engine detected the threat during Malwarebytes' analysis. The malware includes two main infostealing payloads. The first is designed to target encryption-related functions and extract sensitive data such as passwords, payment details, and account credentials.
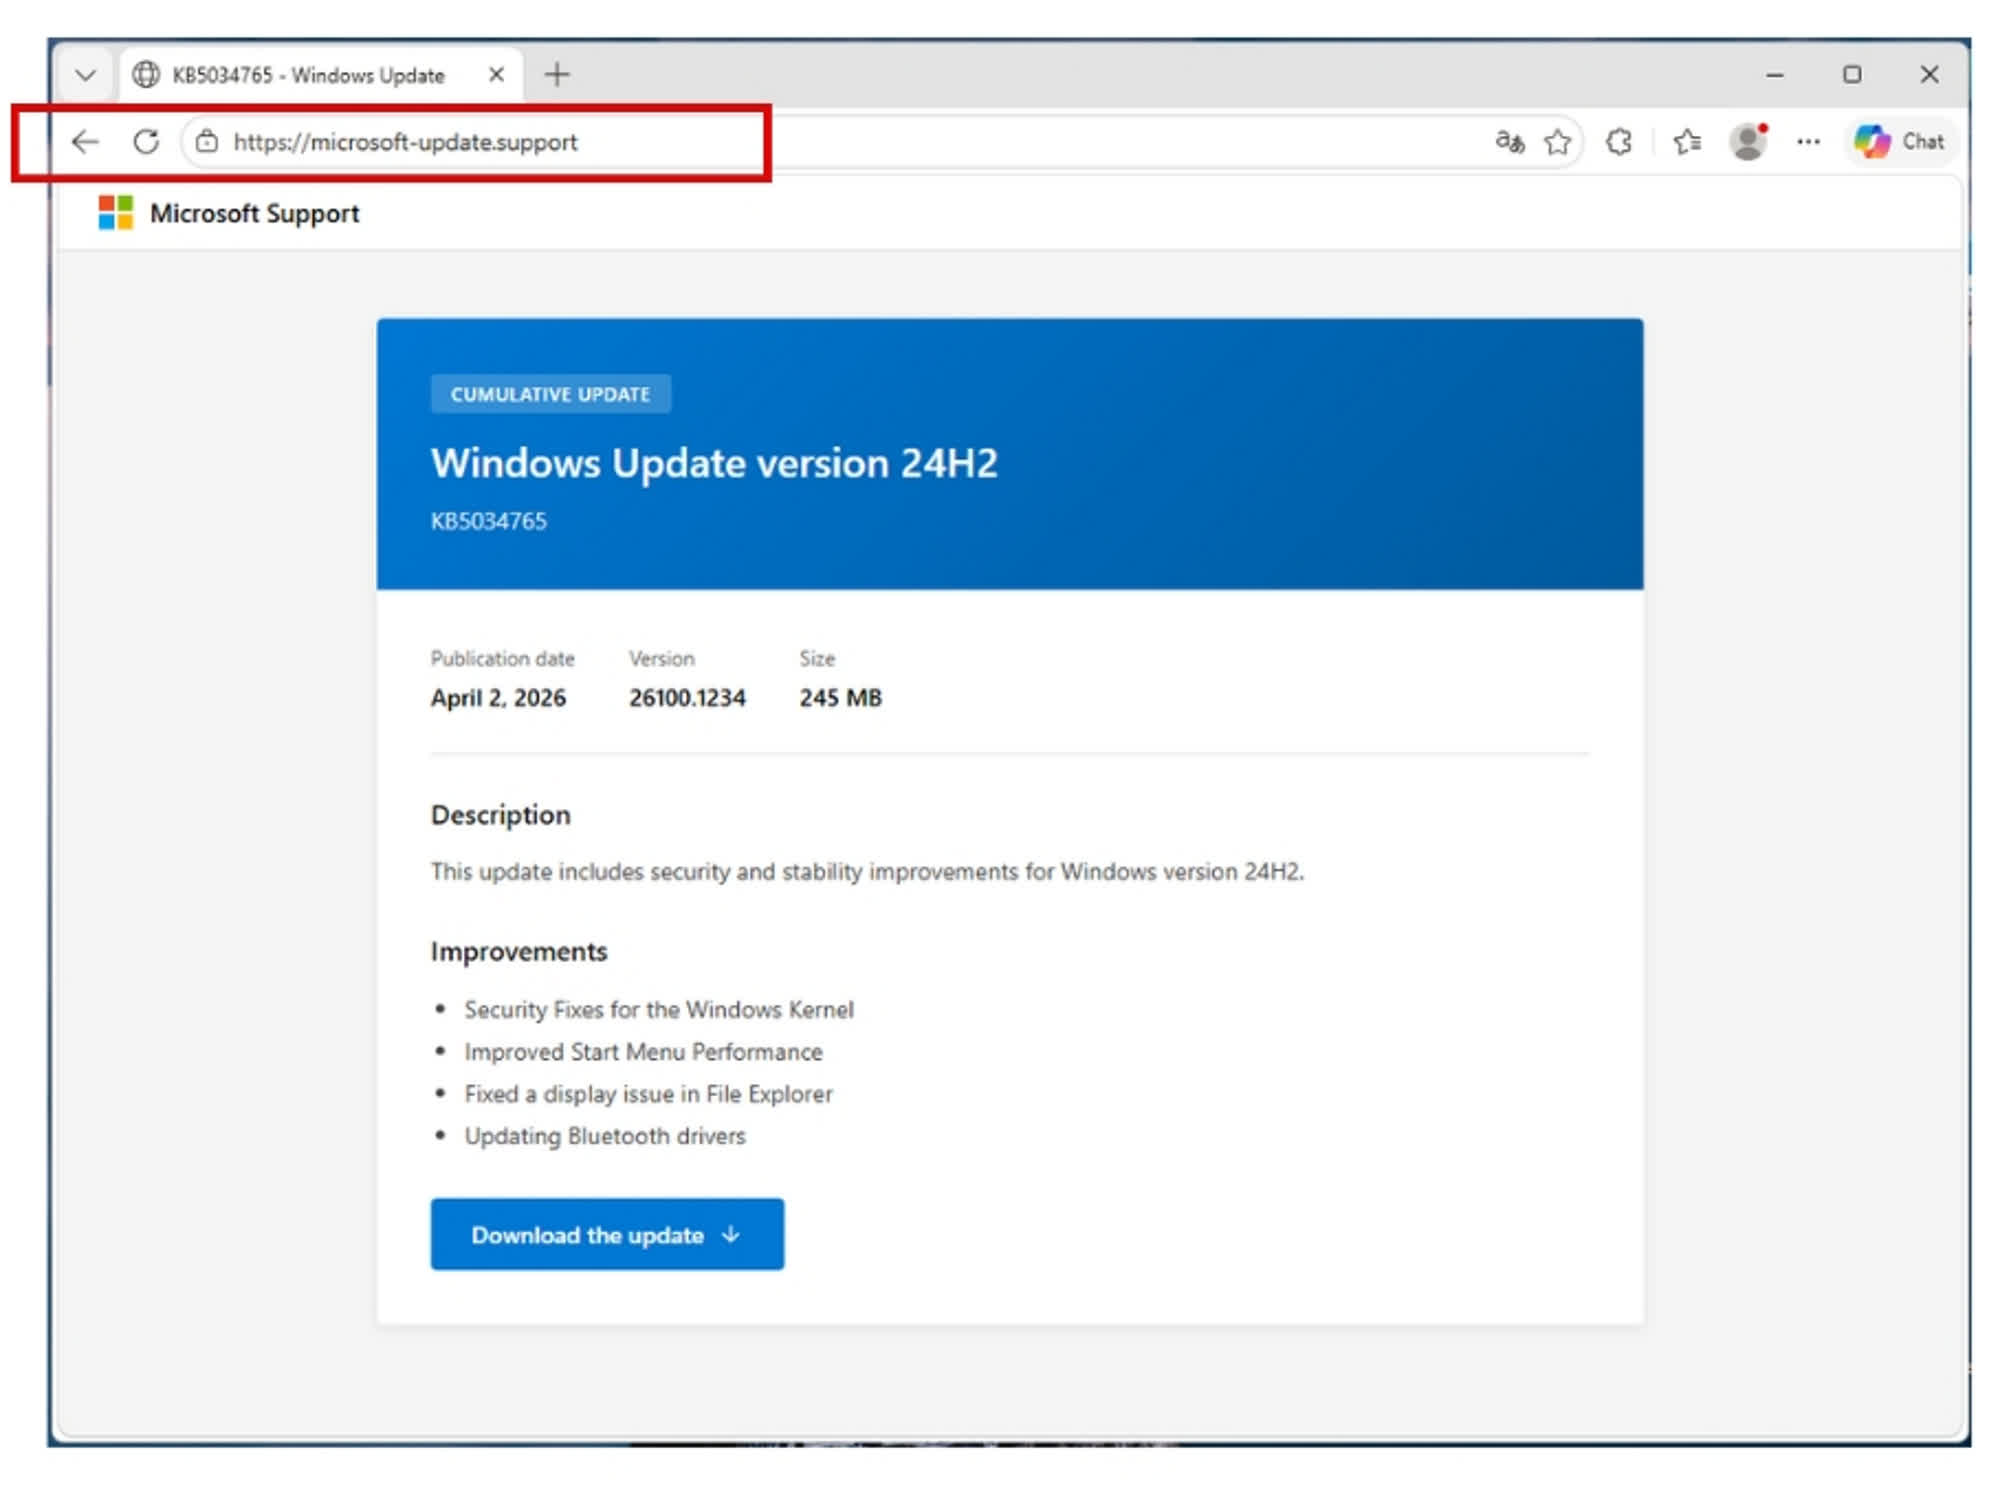
Meanwhile, the second payload targets Discord. The Discord app is built on Electron, which means the malicious code can modify parts of the application to intercept login tokens, payment data, and even two-factor authentication tokens each time the messaging app is launched.
The malware can establish persistence on a Windows system by modifying the Windows Registry and placing a "Spotify.lnk" shortcut in the user's Startup folder. It then attempts to connect to command-and-control infrastructure operated by the attackers in order to exfiltrate stolen data and receive further instructions.
Malwarebytes analysts explained that the campaign appears to specifically target French users, likely due to the availability of tens of millions of exposed personal records circulating in recent data breaches. Leveraging readily available breach data can make targeting more efficient, while also allowing the attackers to quickly adapt the campaign to other languages at a later stage.
Malwarebytes also provided guidance on how to check whether a Windows system has been infected with the infostealer. The company warned that the safest way to install Windows updates is through the operating system's Settings app or the official Microsoft Update Catalog. It also recommended enabling automatic updates, although this approach is not always considered ideal by all users given concerns about buggy or problematic updates.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。