



Seemplicity has launched AI Analysts for exposure management and response. The autonomous agents replace manual vulnerability triage by working directly within remediation workflows to conduct structured, evidence-based exploitability investigations.
The old playbook is broken. AI-generated exploits have collapsed the window between disclosure and weaponization from days to hours, and the static scores and external signals teams once trusted can no longer keep pace.
“The danger was never the alerts we could see, it was the handful of genuinely exploitable ones buried among them,” said Michael Varicak, manager of vulnerability management for Omnissa. “Seemplicity’s AI Analysts surface exactly that with the context to prove it, so we spend our time fixing what attackers could actually exploit.”
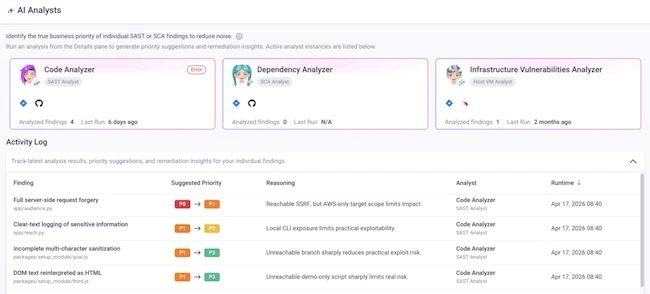
The hard part isn’t ranking findings, it’s confirming which ones an attacker could actually reach. The Seemplicity AI Analysts answer that by investigating each asset in real time, analyzing live runtime configurations, exploit prerequisites, network reachability, code and dependency usage, and compensating controls. The result is a dramatically smaller, more actionable list of what needs immediate response, backed by transparent evidence.
“Zero-day discovery at this scale pushes us out of today’s CVE disclosure process and instigates a need to reindustrialize,” said Erik Nost, senior analyst, security and risk at Forrester. “Patch Tuesday will no longer be marked on the calendar: A 30-day waiting period for patching won’t be acceptable in an environment where attackers can go from discovery to exploit in minutes.”
In preliminary deployments, the Seemplicity AI Analysts found that the majority of high-severity findings were not actually exploitable, cutting alert noise and pointing teams straight at the exposures that carry real-world risk.
“We’re not giving security teams another number to chase. We’re giving them the evidence to act,” said Ravid Circus, Chief Product Officer at Seemplicity. “A score can’t tell you whether a vulnerability is actually exploitable on your systems. Only context can. Our AI Analysts are unique by investigating the asset itself, the runtime conditions, the network exposure, and the code to prove what an attacker could really reach.”
Seemplicity AI Analysts serve three core functions:
The Host Analyst: Confirms whether a host vulnerability is truly exploitable by examining live runtime configuration, exploit prerequisites, and network reachability, then surfaces the likely owner to speed the fix.
The Code Analyst: Reads source directly from GitHub, GitLab, and other connected repositories to determine whether vulnerable code is actually reachable, then hands developers a scoped, ready-to-apply fix.
The SCA Analyst: Confirms which dependencies are genuinely used and reachable across the software supply chain, and powers SBOM-driven zero-day response before scanner signatures even exist.
Evidence over assumptions. Every verdict comes from a structured investigation of runtime context, threat intelligence, network exposure, and code, not a static risk score.
Clear chain of reasoning. Each finding carries an auditable trail of how the verdict was reached, so security and engineering teams agree on what to fix.
Built into remediation workflows. Verdicts and fixes land inside findings tables, workflow automations, and ticketing systems, with no separate validation tool or console required.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。