
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

阮一峰的网络日志
阮一峰的网络日志
博客园 - 司徒正美
D
DataBreaches.Net
宝玉的分享
宝玉的分享
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
博客园 - 【当耐特】
人人都是产品经理
人人都是产品经理
博客园 - Franky
让小产品的独立变现更简单 - ezindie.com
IT之家
IT之家
博客园 - 三生石上(FineUI控件)
J
Java Code Geeks
腾讯CDC
博客园_首页
The Cloudflare Blog
S
SegmentFault 最新的问题
C
Check Point Blog
美团技术团队
爱范儿
爱范儿
大猫的无限游戏
大猫的无限游戏
Hugging Face - Blog
Hugging Face - Blog
T
The Blog of Author Tim Ferriss
A
About on SuperTechFans
Blog — PlanetScale
Blog — PlanetScale

Help Net Security

ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
Webworm APT targets European government organizations wit...
Anamarija Po · 2026-05-20 · via Help Net Security

ESET has released an analysis of the 2025 activity of Webworm, a China-aligned APT group tracked as Space Pirates and UAT-8302. Active since at least 2022, the group initially focused on targets in Asia, but has recently expanded its operations into Europe.

ESET observed Webworm targeting government organizations in Belgium, Italy, Poland, Serbia, and Spain during 2025. The group also expanded its activity into South Africa, where researchers identified activity involving a local university.

Discord messages expose infrastructure and targets

By decrypting more than 400 Discord messages used for command-and-control (C&C) communication, ESET gained visibility into the group’s infrastructure and operations. The analysis revealed reconnaissance activity involving more than 50 unique targets.

“Through our analysis, we were fortunate enough to recover commands executed from a server that gave a view into the group’s potential initial access techniques, using an open-source vulnerability scanner as well as identifying some of its focused targets,” said Eric Howard, ESET researcher who investigated the campaign.

The recovered information led ESET to an attacker-operated GitHub repository used to host staged malware and supporting tools that could be downloaded onto victim systems.

The repository contained artifacts including the SoftEther VPN application. Researchers identified an IP address in a SoftEther configuration file that matched infrastructure previously linked to Webworm.
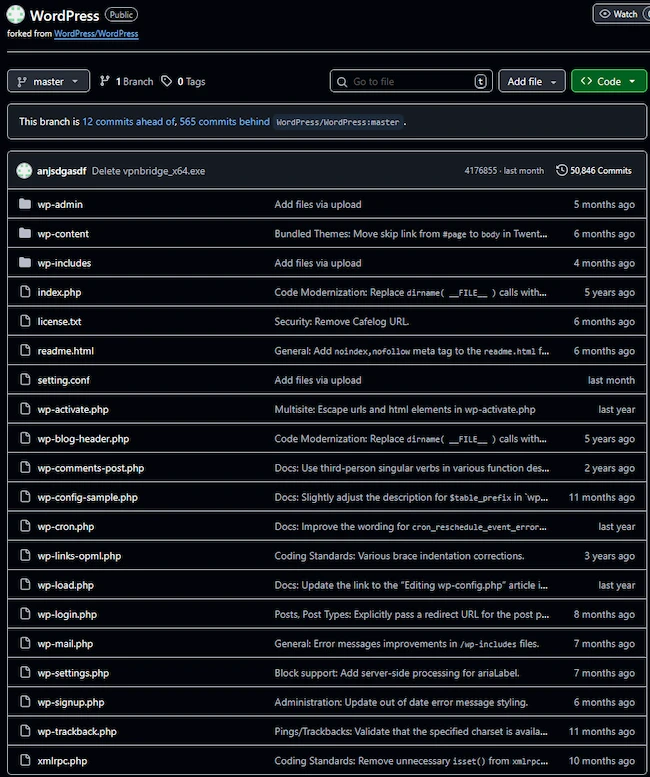
Webworm APT campaign Europe

Forked WordPress repository (Source: ESET)

New backdoors

According to ESET, the group’s latest campaigns introduced two new backdoors: EchoCreep and GraphWorm.

EchoCreep uses Discord for C&C communication, allowing attackers to upload files, send runtime reports, and receive commands.

GraphWorm relies on Microsoft Graph API and OneDrive endpoints to retrieve tasks and upload victim information.

The group expanded its use of proxy tools. Existing proxy capabilities were supplemented with custom tools including WormFrp, ChainWorm, SmuxProxy, and WormSocket. Based on the number and complexity of these tools, ESET believes Webworm may be building a larger hidden network by using compromised systems as proxy infrastructure.

During the investigation, ESET discovered that Webworm had started using WormFrp to retrieve configurations from a compromised AWS S3 bucket.

“It is apparent that through this S3 bucket, Webworm can leverage data exfiltration while an unsuspecting victim foots the bill for the service,” Howard said.

Between December 2025 and January 2026, Webworm operators uploaded 20 new files to the service, two of which had been exfiltrated from a government organization in Spain.

ESET noted that Webworm continues to stage files on GitHub and expects the group to maintain that approach in future campaigns.