


Iranian media is claiming that the US used backdoors and/or botnets to disable networking equipment during the current war, and Chinese state media is dining out on the allegations.
Reports from Iran claim hardware made by Cisco, Juniper, Fortinet, and MikroTik either rebooted or disconnected during recent attacks on Iran – despite the regime disconnecting the nation from the global internet.
The reports suggest that’s only possible because someone – probably the US – can sabotage the equipment at will.
The report linked to above hypothesizes that a hidden backdoor in firmware or bootloader allows remote attacks at a pre-determined time or can be activated by a signal from a satellite. In either scenario, the US uses the backdoor to bring down networks at the most inconvenient moment for Iran.
The thrust of the Iranian stories we’ve seen is that US-based vendors are complicit in the installation of backdoors.
Another scenario Iranian reports float is that someone has installed a botnet on networking equipment and has therefore been able to target devices from Cisco – and from MikroTik, the Latvian networking equipment vendor that emphasizes its product development takes place within the European Union.
As Iran’s internet is currently mostly closed – more on that later – it’s almost impossible to verify reports of a mass outage.
That the USA possesses the ability to conduct attacks in cyberspace is not in doubt. After the US takeover of Venezuela, president Trump and general Dan Caine, chairman of the Joint Chiefs of Staff, alluded to online action being one element of the operation. Caine also said US Cyber Command assisted with the June 2025 “Operation Midnight Hammer” attack on Iran, without elaborating on the agency’s role.
Whatever is going on, Chinese state media has seized on the Iranian reports to restate Beijing’s position that China is a pacifist in cyberspace and the US is the real cyber-villain.
China’s National Computer Virus Emergency Response Center (CVERC) regularly posts a theory that information leaked by Edward Snowden shows the US embeds backdoors in networking equipment, and that all allegations that Beijing conducts cyberattacks is therefore just a sham to shift the blame to the Middle Kingdom. CVERC has even argued that the Volt Typhoon attacks – which the Five Eyes nations agree was a Chinese attack on critical infrastructure – were a false flag operation run by US intelligence community to give it credibility when smearing China.
Chinese state media has given credence to the Iranian reports and even published the cartoon below to express Beijing’s feelings on the alleged events in Iran.
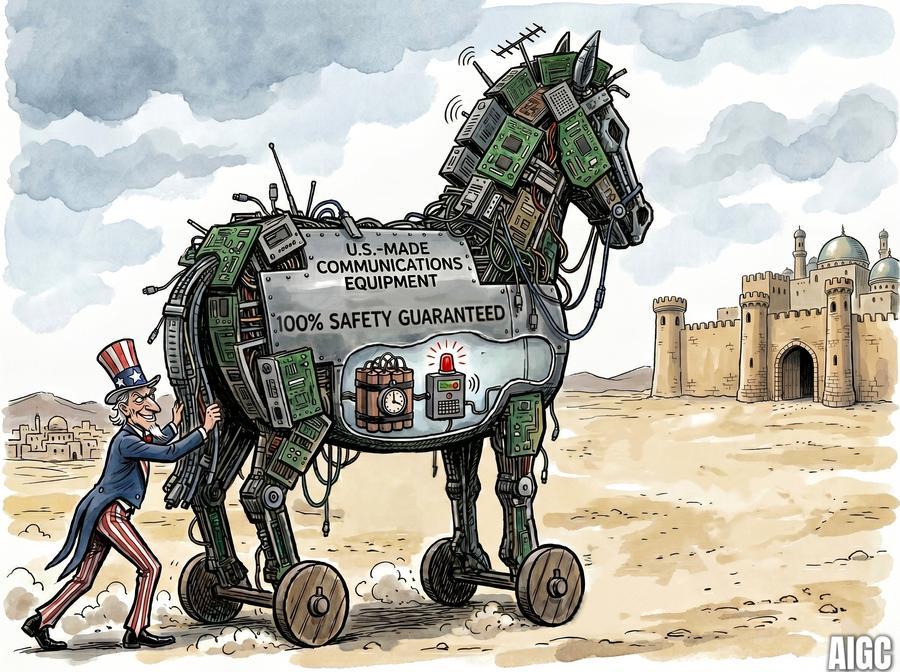
Chinese State Media cartoon - Click to enlarge
While these propaganda shenanigans play out, outage-watching outfit NetBlocks says Iran has maintained its internet blockade for 52 days, but adds “authorities continue efforts to segregate users and provide selective access to favored groups.”
That may be a reference to reports that Iran’s government has created a service called “Internet Pro” that allows some citizens to access a subset of the global internet.
Activists claim Iran’s government also issues “White SIMs” that allow unrestricted internet access to select officials. ®
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。