


Rapid7’s latest disclosure on CVE-2026-0826 should get serious attention from anyone running HP Poly VoIP phones in an enterprise setting. It’s a critical unauthenticated stack-based buffer overflow that can give a remote attacker root-level code execution on affected devices, and the bug sits in SDP parsing for ICE-enabled phones.
“Rapid7 Labs conducted a zero-day research project against an HP Poly VVX 450 Voice over Internet Protocol (VoIP) phone. This research resulted in the discovery of a critical unauthenticated stack-based buffer overflow vulnerability, CVE-2026-0826.” reads the report published by Rapid7. “A remote attacker can leverage CVE-2026-0826 to achieve unauthenticated remote code execution (RCE) with root privileges on a target device. “
When the phone processes SDP data, it can parse a candidate attribute and copy the input into a 256-byte stack buffer without checking length, which means a long enough string can overflow the stack.
“No length check is performed to ensure the incoming string length is less than 256 bytes. Therefore by providing a candidate attribute whose length is greater than 256 bytes, a stack-based buffer overflow will occur.” states the report.
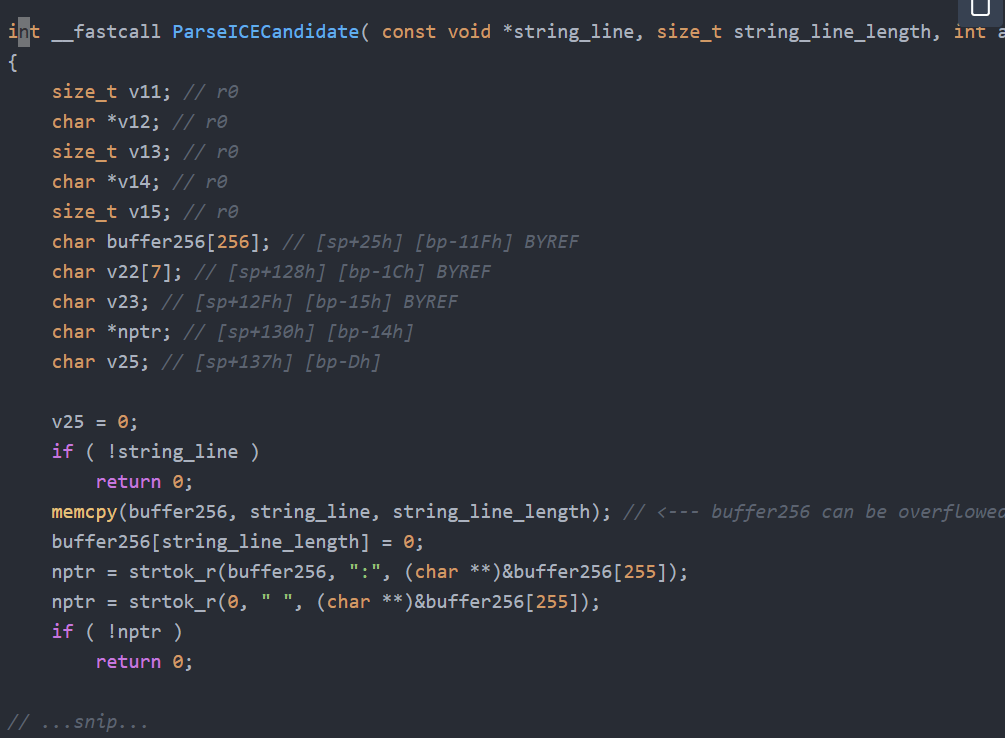
An attacker can send a specially crafted SIP INVITE request containing an oversized ICE candidate attribute, overflowing a 256-byte buffer without authentication. Testing showed the flaw allows attackers to overwrite key memory registers, including the program counter, potentially leading to remote code execution and full control of the device.
From there, the path to exploitation is straightforward enough to be dangerous: ASLR is present, NX is enabled, but ASLR does not behave as it should on the device, and shared libraries load at fixed addresses that make a ROP chain practical..
“Inspecting the polyapp binary with the checksec tool we can see that No Execute (NX) is enabled, so the stack data will not be executable.” continues the report. “As we will not be able to execute a payload directly on the stack, we can overcome this by using a Return Oriented Programming (ROP) chain to bypass the NX mitigation.”
The issue affects firmware version 6.4.7.4477 and could be exploited over the network via SIP traffic
Rapid7 confirmed the bug across the VVX line, including the VVX 150, 250, 350, and 450, plus the Trio 8800, 8500, and 8300 models. The recommended fix is simple in theory and non-negotiable in practice: disable ICE where it isn’t needed, then move all affected devices to the patched firmware releases HP published.
“HP Poly recommends that administrators disable ICE connectivity in environments where it is not required.” concludes the report. “All affected Poly Voice devices should be updated to the latest available UCS release using the Poly Lens Device Management application.”
The real risk here isn’t just that a desk phone can be popped. As Rapid7 notes, these devices sit in trusted places like conference rooms and offices, which makes them useful footholds for spying, lateral movement, and voice-based fraud; in plain terms, a compromised phone can do a lot more than ruin your day, and it won’t ask for permission first.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, HP Poly VoIP phones)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。