


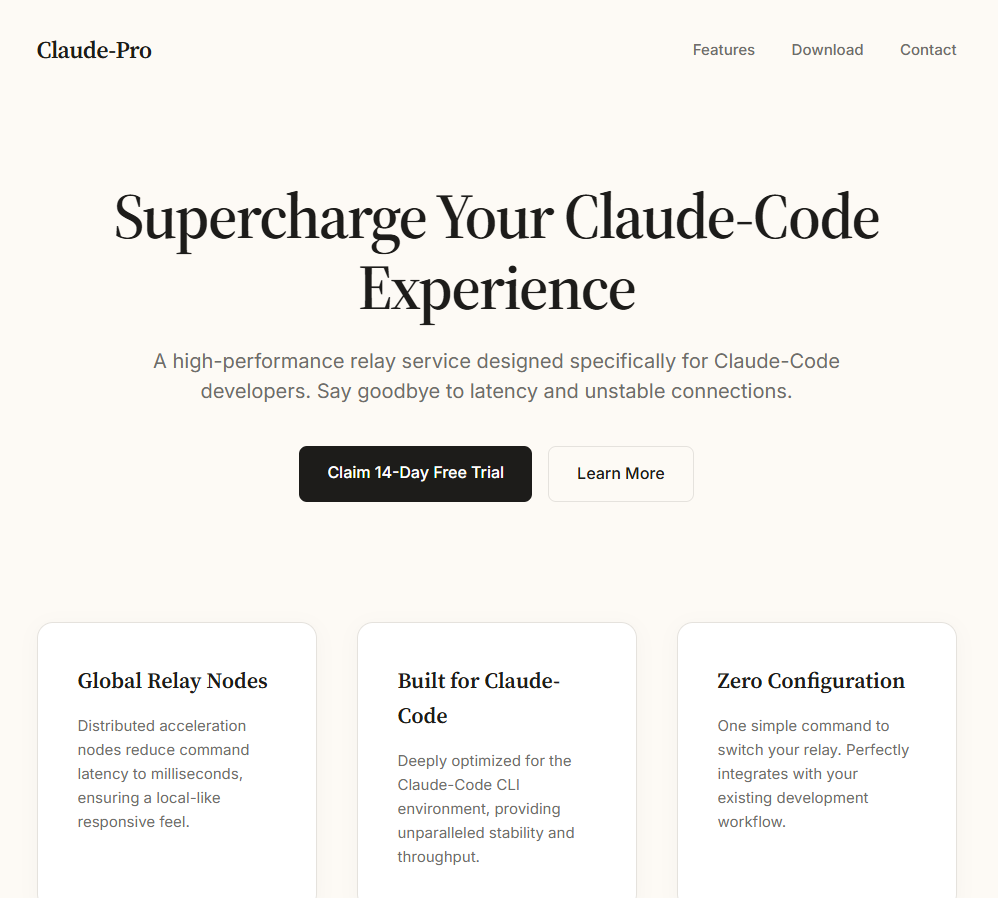
A fake website impersonating Anthropic’s Claude service was found distributing the PlugX remote access trojan, according to Malwarebytes.
The rogue site abuses the chatbot’s popularity to trick users into downloading a ZIP archive presented as a “pro version” installer. The malware uses DLL sideloading to execute and then attempts to clean up traces after infection, reducing visibility on the system.
“We discovered a fake website impersonating Anthropic’s Claude to serve a trojanized installer. The domain mimics Claude’s official site, and visitors who download the ZIP archive receive a copy of Claude that installs and runs as expected.” reads the report published by Malwarebytes. “But in the background, it deploys a PlugX malware chain that gives attackers remote access to the system.”
The malicious site delivers a ZIP with an MSI installer that mimics a legitimate Anthropic Claude setup, though with subtle flaws like a misspelled folder name. It drops a shortcut that runs a VBScript, launching the real app to avoid suspicion while silently executing malicious actions.
In the background, the script copies three files, NOVUpdate.exe, avk.dll, and an encrypted .dat file, into the Windows Startup folder and runs the executable invisibly. This abuses DLL sideloading, using a legitimate signed updater from G DATA to load a malicious DLL.
“Static analysis of the dropper script identifies these as an executable called NOVUpdate.exe, a DLL named avk.dll, and an encrypted data file called NOVUpdate.exe.dat. The script then launches NOVUpdate.exe with a hidden window (window style 0), so nothing appears on screen.” continues the report. “This is a textbook DLL sideloading attack, a technique catalogued by MITRE as T1574.002. NOVUpdate.exe is a legitimately signed G DATA antivirus updater. When it executes, it attempts to load a library called avk.dll from its own directory. Normally, this would be a genuine G DATA component, but here the attacker has substituted a malicious version. Signed sideloading hosts like this can complicate detection because the parent executable may appear benign to endpoint security tools.”

The DLL then decrypts and executes the payload stored in the .dat file.
This three-part structure, signed executable, trojanized DLL, and encrypted payload, is typical of the PlugX malware family, often used in long-running cyber espionage campaigns.
Sandbox analysis shows the malware quickly becomes active after execution. WScript.exe drops NOVUpdate.exe and avk.dll into the Startup folder, and within 22 seconds the executable connects to a remote server (8.217.190[.]58) over HTTPS, repeating the communication several times. The IP is hosted on Alibaba Cloud infrastructure, commonly abused for command-and-control. The malware also alters a TCP/IP-related registry key to modify network behavior.
To evade detection, the VBScript deploys a self-deleting mechanism that removes both the script and a temporary batch file shortly after execution, leaving only the sideloaded files and active process behind. It suppresses errors to avoid alerting the victim.
“After deploying the payload files, the VBScript writes a small batch file called ~del.vbs.bat that waits two seconds, then deletes both the original VBScript and the batch file itself. This means the dropper is gone from disk by the time a user or analyst goes looking for it.” continues the report. “The only artifacts that persist are the sideloading files in the Startup folder and the running NOVUpdate.exe process.”
This approach mirrors a technique previously documented by Lab52, using a legitimate G DATA executable, a malicious DLL, and an encrypted payload, hallmarks of PlugX. While historically linked to Chinese espionage, PlugX is now widely reused. Here, attackers combine this known method with an AI-themed lure to trick users into installing malware.
“PlugX has historically been associated with espionage operators linked to Chinese state interests. However, researchers have noted that PlugX source code has circulated in underground forums, broadening the pool of potential operators. Attribution based on tooling alone is not definitive.” concludes the report. “What is clear is that the operators behind this campaign have combined a proven sideloading technique with a timely social engineering lure—exploiting the surging popularity of AI tools to trick users into running a trojanized installer.”
The report also provides Indicators of Compromise (IOCs).
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。