
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

D
Docker
Apple Machine Learning Research
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
博客园 - 三生石上(FineUI控件)
月光博客
月光博客
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
WordPress大学
WordPress大学
Hugging Face - Blog
Hugging Face - Blog
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
M
MIT News - Artificial intelligence
腾讯CDC
B
Blog RSS Feed
H
Help Net Security
J
Java Code Geeks
有赞技术团队
有赞技术团队
Y
Y Combinator Blog
博客园_首页
Last Week in AI
Last Week in AI
博客园 - 【当耐特】
博客园 - Franky
B
Blog
MongoDB | Blog
MongoDB | Blog
博客园 - 叶小钗
Martin Fowler
Martin Fowler

Consumer Insights

Weverse data breach affects 422,584 user accounts Manchester Airports Group cyberattack exposes data of 8.7 million customers Sakura Internet hack may affect 1.36 million accounts French tax authority breach exposes data of 678,000 people and businesses Phone number leaked in the Bloctel breach? Here’s what to do. SplitVPN breach reveals 58 million hidden connection logs South Korea diplomatic academy hack exposes diplomat data Credential stuffing attack at Chick-fil-A comes with data breach notice for customers Coca-Cola halts Fairlife production across US after ransomware attack Qantas data breach started with a fake IT support call Lidl warns customers after data breach How to find out if your identity has been exposed by infostealers Texas breach exposes PII of 3 million hunting and fishing license customers Maine forced to take down data breach portal after fake notices filed with authorities Carnival breach exposes data of nearly 6 million people 7-Eleven data breach exposes data of 185,000 people UK Water Supplier Fined Nearly £1 Million After Hackers Roamed Networks for Almost 2 Years DAEMON Tools Lite breach prompts urgent update after malware-laced installer Instructure confirms breach; millions of Canvas users potentially impacted Stalkerware data leak exposes private screenshots linked to celebrities and influencers Hackers claim to have breached Udemy, stealing 1.4 million user records Rituals data breach exposes customer details Booking.com says breach exposed travelers’ data Basic-Fit data breach exposes member information across Europe Rockstar Games confirms breach after ShinyHunters leaks stolen analytics data Lapsus$ claims AstraZeneca breach exposes code and credentials Aura data breach exposes 900,000 records after phishing attack Telus Digital data breach confirmed after ShinyHunters claims 1PB theft Was Your Data Exposed in the Latest Under Armour Breach? Here’s What You Should Do Breach at Tinder, Hinge and OkCupid exposes user data
European Space Agency's cybersecurity in freefall as yet ...
Graham CLULEY · 2026-01-22 · via Consumer Insights

It has just been a few weeks since we reported on the Christmas cyber attack suffered by the European Space Agency (ESA), and the situation has already become worse.

When ESA revealed that it had been hacked over the Christmas period by a hacker known as "888" it was quick to reassure the public that the impact was "limited" to external servers containing unclassified engineering data.
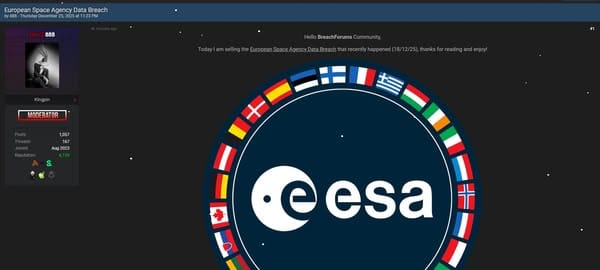
The hacker, however, claimed to have exfiltrated some 200GB of data, including source code, API and access tokens, hardcoded credentials, and SQL files. Some of the stolen documents were said to be related to the Ariel space telescope mission which aims to launch in 2029 in a mission to find out the atmospheric composition of exoplanets.

In light of the latest data breach to impact ESA, the December 2025 incident doesn't look too bad.

Because this month the Scattered Lapsus$ Hunters cybercrime group was quick to pick up where "888" had left off, exploited what they claim was an unpatched vulnerability to steal an additional 500GB of data - more than double the initial haul.

Furthermore, this latest breach reportedly involves data that might be more concerning - such as operational procedures, spacecraft and mission details, subsystems documentation, and proprietary contractor data from ESA partners including SpaceX, Airbus Group, and Thales Alenia Space.

As a consequence of this latest incident, ESA has now confirmed that a criminal investigation is underway.

Some have suggested that poor cybersecurity practices at ESA may have helped the hacking group gain unauthorised access to systems.

Cybersecurity researcher Clémence Poirier told Space.com that she frequently comes across the email credentials of ESA staff (as well as NASA) up for sale on dark web forums.

Unfortunately for ESA, it has suffered from a history of cybersecurity incidents. These have ranged from its official online merchandise store being compromised with payment card-skimming code just days before Christmas 2024, to an Anonymous-linked breach that exposed employee and subscriber passwords and other data in 2015.

The high profile of organisations that work in outer space means that they are common targets for both bug hunters and malicious hackers, with vulnerabilities being disclosed "almost every day" to BugCrowd about NASA, for instance.