


Deputy Director for Asia-Pacific and China
Bilal Mohamed
Policy Manager for India
Co-authors: Lauren Koek and Valentina Curatella, FPF APAC Interns
From July 20 to 24, 2026, the Future of Privacy Forum (FPF) participated in the inaugural Singapore Data Festival (SDF), hosted by Singapore’s Personal Data Protection Commission (PDPC) and Infocomm Media Development Authority (IMDA). Succeeding the PDPC’s annual Personal Data Protection Week, the SDF convened around 2,000 data and AI professionals, policymakers, and business leaders from all around the world.
Throughout the week, FPF convened key engagements that brought together stakeholders from industry, government, academia, and the legal sector around top-of-mind issues for the Asia-Pacific (APAC) region, including agentic and physical AI, smart wearable devices, and biometric data. This blog post takes stock of the five cross-cutting threads that emerged from FPF’s events, our invite-only Privacy Leaders’ Luncheon, our closed-door regulators’ roundtable, and contributions to the IAPP Asia Forum.
First, governance attention on AI is shifting decisively toward agentic AI, straining notice-and-consent models and pushing regulators toward objectives like accountability, safety, and meaningful human oversight. Second, AI is reshaping the breach and threat landscape, raising the stakes for security and breach notification. Third, continuous, always-on data streams from wearables and physical AI are testing the limits of existing data protection principles, especially for bystanders and biometric data. Fourth, technical and institutional capacity has become a foundational requirement for credible data protection. Fifth, scalable, interoperable cross-border data transfer mechanisms remain vital to the regional digital economy.
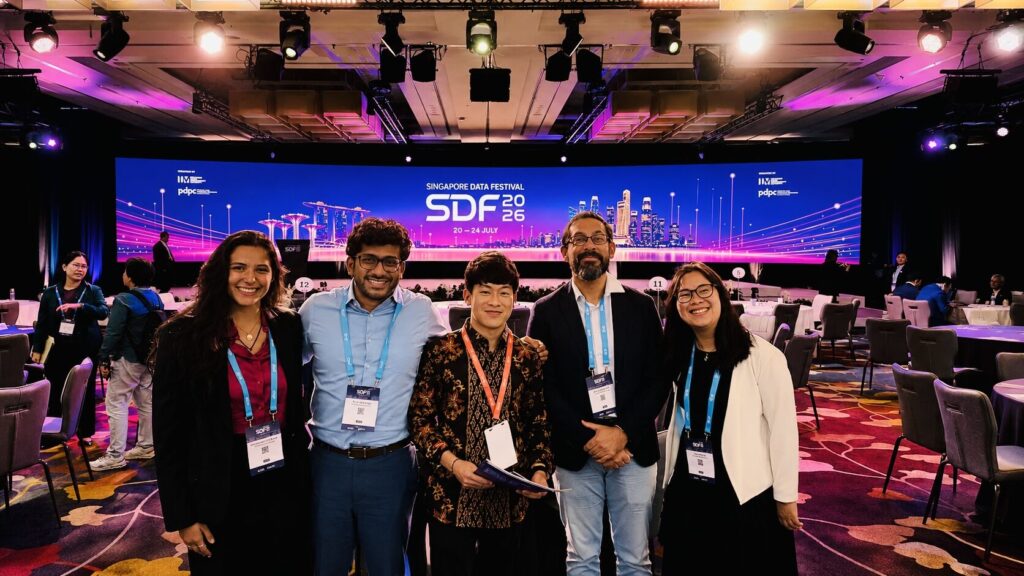
FPF at the Opening Session of the Singapore Data Festival, Monday, July 20, 2026.
Theme 1: Agentic AI is straining notice-and-consent models, pushing regulators towards ensuring accountability and meaningful oversight
In the last couple of years, the focus of global AI governance discourse has expanded from generative AI toward agentic AI systems capable of autonomous multi-step actions. This development has profound implications for the notice-and-consent model at the heart of most data protection regimes. As discussions across the week made clear, the shift is also pushing regulators toward frameworks organized around governance concepts such as bounding risk, retaining visibility over agent activity, and preserving human accountability.
The PDPC’s newly-issued guiding documents illustrate how some APAC regulators are beginning to address and provide clarity on data protection issues arising from the development and deployment of modern AI systems. On July 20, 2026, at the launch of the SDF, the PDPC published its finalized Advisory Guidelines on the Use of Personal Data in Generative AI (Advisory Guidelines). The Advisory Guidelines address how generative AI models may be trained and deployed under Singapore’s Personal Data Protection Act (PDPA).
While the guidance focuses on generative AI, it would also have a bearing on a relevant issue for agentic AI: specifically, the legal bases available for the collection and processing of personal data, and how individuals and organizations should be informed at the outset about the purpose of data collection and processing. In this regard, two points in the Advisory Guidelines are worth noting. First, the Advisory Guidelines clarify that the “Publicly Available Exception” under Singapore’s PDPA is applicable to the collection of data through web-scraping. Second, the Advisory Guidelines require explicit “AI-Specific Notifications” (rather than broad and generic language on “new product development”) where consent is sought specifically from individuals to train and develop AI models.
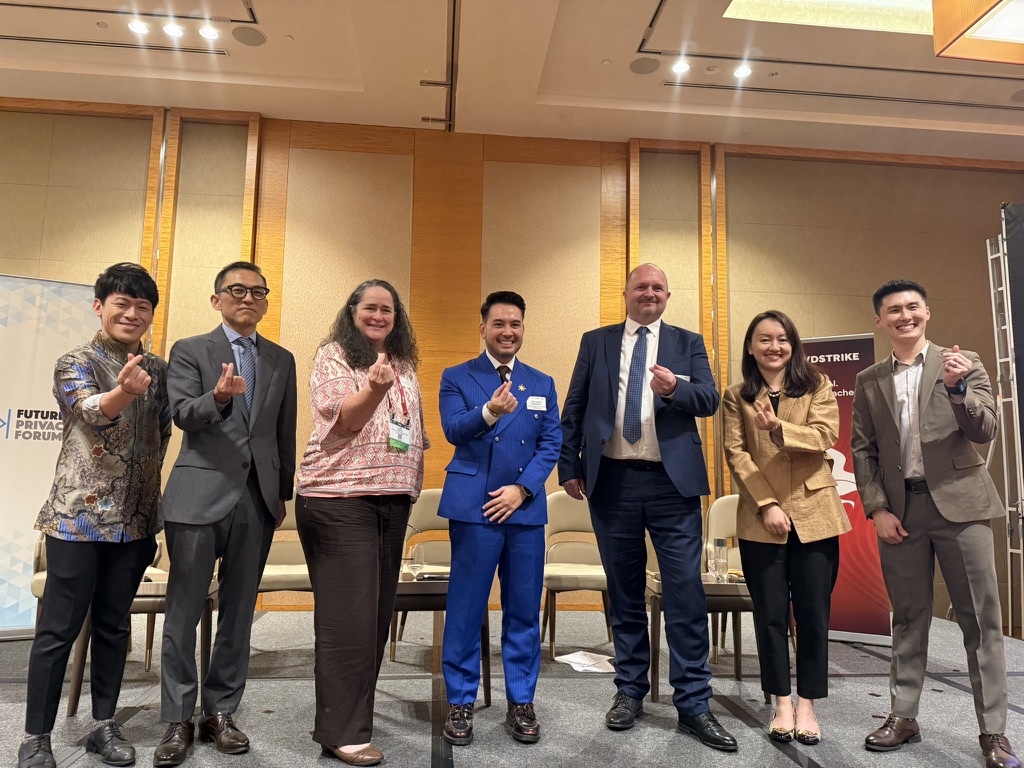
FPF and CrowdStrike’s “All-Regulators’ Panel on the Risks and Opportunities of Agentic AI,” Wednesday, July 22, 2026.
Yet, as agentic AI systems and generative AI systems with agentic functionalities become more common, regulators are recognizing that these enhanced capabilities can exacerbate data protection issues and complicate issues around responsibility allocation. Recognizing this trend, on Wednesday, July 22, 2026, FPF and CrowdStrike co-organized an “All-Regulators’ Panel on the Risks and Opportunities of Agentic AI,” moderated by Prof. Haksoo Ko (Seoul National University; FPF Senior Fellow; former Chairperson of South Korea’s Personal Information Protection Commission). Despite operating in vastly different legal, regulatory and political contexts, the regulators on the panel converged on the same objectives — achieving transparency, accountability, safety, and trust — even as they differed on the approach.
For instance, Lori Baker (Vice President, Data Protection and Regulatory Compliance, Dubai International Financial Centre (DIFC)) described how the DIFC aims to embed human oversight at every level of agentic AI deployment through internal policy prototyping. She flagged that greater clarity is needed around AI safety so that agentic AI systems can fend off attacks and avoid unintended behavior (such as a robot guard causing physical harm on the basis of a flawed visual inference).
Meanwhile, Jose Sutton Belarmino II (Deputy Privacy Commissioner, National Privacy Commission, Philippines) posited a principles-based approach towards regulating agentic systems, anchored in continuous transparency and explainability. He reasoned that legislative processes often lagged technological development. He also noted the practical difficulty of defining “meaningful” human intervention, arguing that human involvement should begin not simply at deployment, but when a company first decides to adopt an AI system.
Conversely, Alain Herrmann (Commissioner, National Commission for Data Protection of Luxembourg) outlined the European Union’s structured and risk-based approach under the GDPR and the EU AI Act, which categorizes systems by risk and mandates market surveillance. He acknowledged that applying this approach to agentic AI may present practical challenges for organizations, such as where organizations may have to comprehensively map out how an agentic AI system is processing personal data to ensure compliance. During the audience Q&A segment, Commissioner Herrmann also noted that while the EU rules may be more demanding, all EU jurisdictions share the foundational objective of ensuring accountability, safety, and trust in the development and use of agentic AI systems.
Denise Wong (Commissioner, PDPC Singapore; Assistant Chief Executive, IMDA) explained that Singapore pairs “hard-law” obligations under data protection law with iteratively updated “soft-law” guidance, such as IMDA’s Model AI Governance Framework for Agentic AI (launched in January 2026 and updated in May 2026). She emphasized that the combination of binding law and guidance allows Singapore to remain agile as guidelines are updated iteratively based on real industry feedback and use cases.
These regulatory currents were similarly mirrored – from an industry perspective – at FPF’s Privacy Leaders’ Luncheon (which convened senior practitioners from across the region to discuss top-of-mind issues around AI and data protection). Participants repeatedly emphasized visibility as the cornerstone of any internal AI governance program (that is, knowing how AI is being used across an organization, by whom, and for what), as teams contend with “shadow AI” (the use of AI tools within an organization without the organization’s explicit knowledge, approval or oversight) and organizational pressures to adopt AI. On human oversight, most participants concurred that automation should not dilute accountability. Agentic systems remain tools, and human users remain responsible for outcomes. The depth of human scrutiny, however, should be proportionate to the risks of specific contexts and use cases.
Theme 2: AI is changing the breach and threat landscape, raising the stakes for security and notification
The same capabilities driving agentic adoption are also lowering the requirements and cost of cyber threats, even as unintentional exposure grows when employees route personal data through “shadow AI” tools. In this regard, FPF also contributed to discussions at IAPP Asia Forum 2026, where these same pressures — expanding attack surfaces and rising breach volumes — featured across both sessions FPF participated in.
Josh Lee Kok Thong (Managing Director, FPF APAC) joined experts from McDermott Will & Schulte, Meta, and CrowdStrike for a session titled “The API Crisis: Securing Agentic AI in Asia’s Fastest Growing Threat Surface.” The panel explored how Application Programming Interfaces (APIs) have become an exposed control layer and a risky failure point through shadow APIs and inconsistent multi-cloud controls, and what concrete steps can strengthen API governance and secure AI-driven data flows.
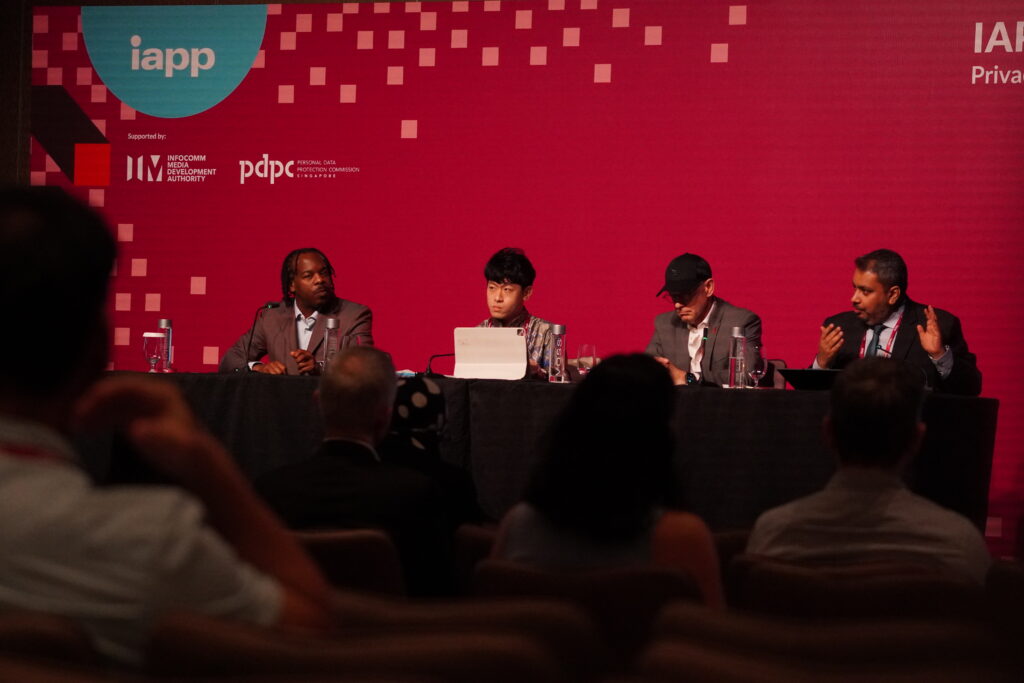
FPF’s Josh Lee Kok Thong on the IAPP panel “The API Crisis: Securing Agentic AI in Asia’s Fastest Growing Threat Surface,” Wednesday, July 22, 2026
Concerns around attack surfaces growing faster than governance measures was also a central issue in Bilal Mohamed‘s (FPF Policy Manager for India) IAPP panel on “Navigating India’s Personal Data Breach Regime in the AI Age.” This panel discussion unpacked the breach-related requirements of India’s Digital Personal Data Protection Act, 2023 (DPDPA) against a landscape in which AI is reshaping the scale, speed, and entry points of personal data breaches, making unintentional exposure more likely.
The DPDPA, unlike most data protection regimes with risk thresholds, requires data fiduciaries (equivalent to a “data controller” under the GDPR) to notify the affected individual and India’s Data Protection Board (DPB) of every breach they become aware of, regardless of severity. The panel weighed whether such an all-encompassing duty remains fit-for-purpose as the ubiquitous use of AI potentially increases the number and volume of data breaches. This issue was also thrown into relief by significant developments elsewhere, with the EU’s proposed Digital Omnibus for the GDPR looking to extend the reporting timeline and narrow breach reporting obligations to high-risk incidents only.
In this context, it was also timely that the IMDA and PDPC released an updated Guide to Data Protection Practices for ICT Systems on the first day of SDF. The updated Guide draws on lessons from recent breaches to offer organizations a practical reference for hardening systems against the kind of high-velocity AI-driven incidents envisioned by both panels.
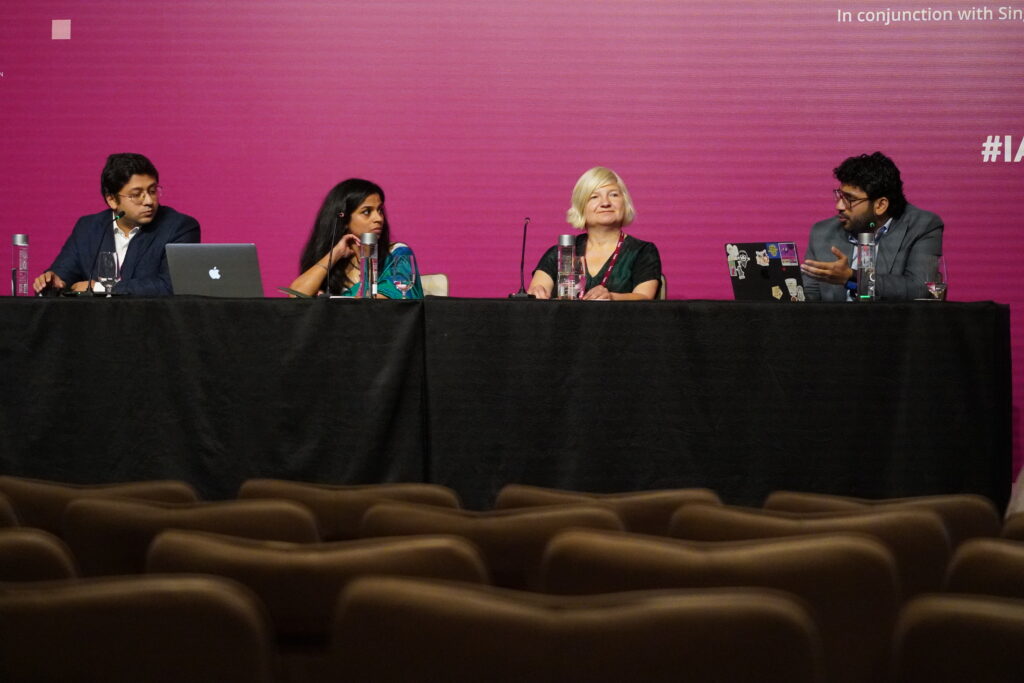
Bilal Mohamed on the IAPP panel “Navigating India’s Personal Data Breach Regime in the AI Age,” Wednesday, July 22, 2026.
Theme 3: Existing data protection principles largely cover biometrics, wearables, and physical AI, but bystander privacy remains unresolved
The challenges and complexities of stretching the boundaries of data protection law to cover emerging technologies carried over into discussions around wearable technologies and physical AI. On Tuesday, July 21, 2026, FPF, together with Rajah & Tann (R&T) and the Singapore Academy of Law (SAL), convened an event on “Biometric Data, Wearables and Physical AI: Frontier Legal, Regulatory and Policy Issues.” The discussion, moderated by FPF’s Deputy Director for APAC Dominic Paulger, featured Zee Kin Yeong (Chief Executive, SAL; FPF Global Senior Fellow), Steve Tan (Partner, R&T), Stephy Kwan (APAC Advocacy, Privacy and Data Policy Manager, Meta), and William Malcolm (Executive Director, Regulatory Risk and Innovation, UK Information Commissioner’s Office). The central question of this discussion was: how far can the technology-neutral principles of data protection law (most of them traceable to the Fair Information Practice Principles and the 1980 OECD Guidelines on the Protection of Privacy and Transborder Flows of Personal Data) stretch to cover devices their original drafters may never have imagined?
Speakers laid out how wearables and physical AI raise hard questions about what a system can perceive, infer, and — for embodied AI — physically do. In addition, the mode of data collection is changing from episodic to being continuous and always-on. Coupled with the fact that there may be little to no interaction between the technology and the people around it, this can leave bystanders with little notice that their personal data is being processed.
In this regard, there was a consensus among the panelists that existing principles remain broad enough to reach these technologies, although greater clarity is needed in three areas.
During the panel, there was also a discussion on the pitfalls and promises of biometric technologies. Because real-world biometric systems rely on probabilistic templates, they are vulnerable to degradation and spoofing. This risk is compounded when an erroneous inference is used to trigger a physical action, such as unlocking a door or dispensing medication. Nonetheless, panelists also brought up examples of how wearable devices can be genuinely life-saving, pointing therefore towards the need for nuanced and balanced policymaking in this space.
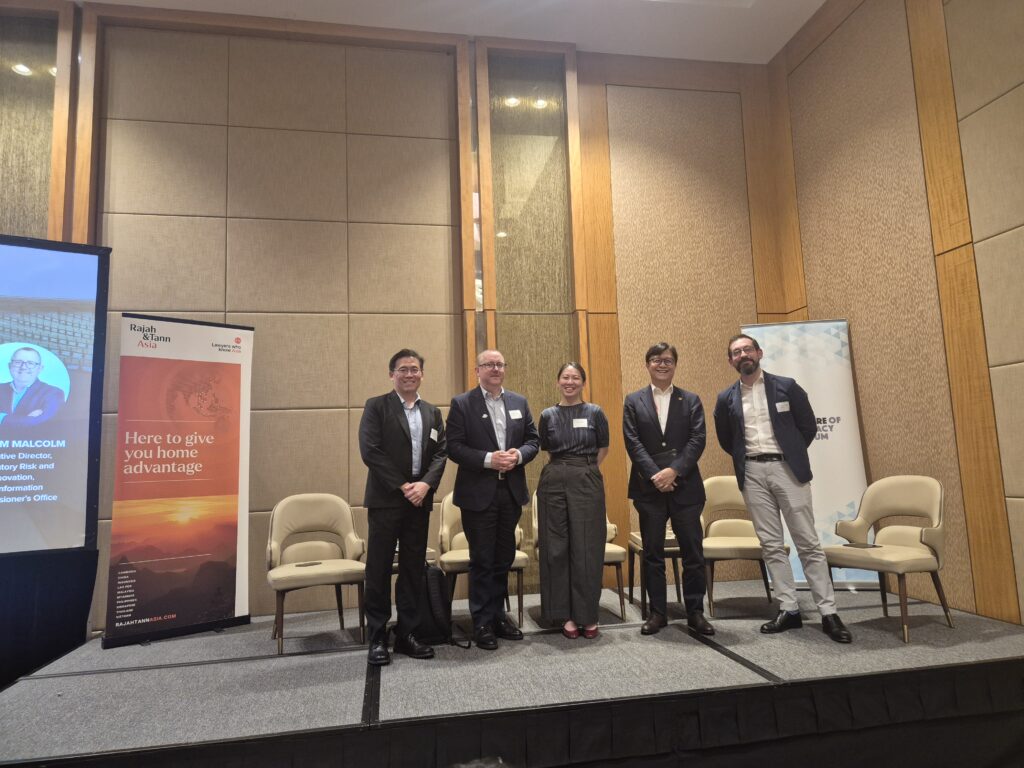
FPF, Rajah & Tann, and the Singapore Academy of Law’s joint event on “Biometric Data, Wearables and Physical AI: Frontier Legal, Regulatory and Policy Issues,” Tuesday, July 21, 2026.
Theme 4: Technical and institutional capacity is foundational to credible data protection amidst a fast-evolving technological landscape
Underlying all of the discussions above is a more fundamental question: how can regulators in general and data protection authorities (DPAs) in particular keep pace with the relentless advance of technology, while building operational capacity and fulfilling their mandate of enforcing data protection law? On Thursday, July 23, 2026, FPF hosted “Foundations and Frontiers: A Regulators’ Roundtable on Institutional Excellence in the Asia-Pacific,” a closed-door session for experienced and emerging DPAs from across the region. In keeping with the Chatham House Rule, the takeaways below are shared without attribution to individual participants.
One key takeaway is that in building institutional capacity, DPAs can look both to adjacent fields and to adjacent stakeholders. In this regard, the first session of the roundtable addressed how regulators can develop early capabilities, allocate scarce resources, and build technical capacity without disrupting day-to-day operations. For instance, in seeking to build fresh expertise in an emerging DPA, the authority could look to recruit specialized technical skills from adjacent fields like digital forensics and IT. As specialized data protection practitioners are inherently in short supply in any emerging data protection ecosystem, experts from these adjacent fields can allow DPAs to quickly gain technical capabilities and apply regulations credibly. In addition, emerging DPAs can consider fostering robust “communities of practice” by convening DPOs and practitioners across industries to provide the DPA with valuable multi-stakeholder perspectives in refining policies and approaches.
In this context, a live and relevant example might be seen in the form of India’s emerging Data Protection Board (DPB). As the IAPP panel on India’s breach notification regime (see above) highlighted, India’s DPB is in the process of being established. It is therefore interesting to follow how the DPB will leverage expertise from various sectors and domains in India to build its capacity, while addressing what an “AI-native,” digital-by-design approach to data breach management (see Rule 20 of the DPDP Rules) might look like.
Another key takeaway is that innovation and robust data protection are in fact not mutually exclusive, and that the oft-cited trade-off between both can be navigated in several ways. In the final session of the roundtable, discussants cautioned against defaulting to the creation of rigid checklists that appear to offer easy routes to compliance but may not be as robust in dealing with rapid technological change. Instead, regulators can aim for “conditional certainty” (that is, providing companies with confidence to pursue innovation so long as certain pre-requisites are met), such as leveraging controlled environments like regulatory sandboxes to build capacity, and encouraging pre-deployment consultations with the DPA.
Theme 5: Scalable, interoperable cross-border transfer mechanisms remain vital to the regional digital economy
In a region as diverse as the APAC region, it is no surprise that there has been a proliferation of regulatory frameworks governing the transfer of data between jurisdictions. The operative focus is therefore interoperability, and it was notable how transfer tools like the ASEAN Model Contractual Clauses (MCCs) and the Global Cross-Border Privacy Rules (CBPR) system are emerging as some of the APAC region’s most practical transfer tools – including for jurisdictions with emerging DPAs. This could be seen from another session during the FPF-hosted “Foundations and Frontiers: A Regulators’ Roundtable on Institutional Excellence in the Asia-Pacific.” Discussants noted how standardized or model contractual clauses like the ASEAN MCCs could function as flexible and non-binding “plug-and-play” tools across jurisdictions, even in jurisdictions without a formal DPA. The Global CBPR system was also highlighted as a scalable mechanism that, unlike regional instruments such as the ASEAN MCCs, is open to all jurisdictions. Its accountability-agent model effectively places a certified organization under the oversight of two authorities at once, extending a DPA’s practical reach beyond its own borders.
Relevantly, at the start of SDF, FPF also published its latest Issue Brief on “Navigating Cross-Border Data Transfers in the APAC Region: An Analysis of Developments from 2023 to 2026.” The Issue Brief tracks and maps the fragmented landscape for cross-border data transfers across 14 APAC jurisdictions. A key takeaway from the Issue Brief is that there appears to be a growing duality in the APAC region: convergence on shared safeguards and accountability standards, alongside divergence in data-localization and sovereignty-driven measures.
The focus on interoperability and international cooperation was also visible elsewhere during the SDF, such as when Singapore’s PDPC signed a Memorandum of Cooperation with Japan’s Personal Information Protection Commission to strengthen cooperation on cross-border data transfers.
If you want to learn more about FPF APAC and our engagements on the ground, do not hesitate to be in touch at [email protected] for membership inquiries or [email protected] for media inquiries.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。