


ENISA has published its third annual NIS360 report, assessing the cybersecurity maturity and criticality of all sectors covered by the NIS2 directive. The headline finding is that things are improving across the board. The more important finding is that the improvement is uneven, slow where it matters most, and being outpaced by a threat landscape that’s getting harder faster than defenses are getting better.
Banking, electricity, and telecommunications remain the most mature and most critical sectors, as they have been since the assessment began. Three sectors moved up into the high maturity band for the first time: trust services, aviation, and financial market infrastructures. Four more strengthened their position within the moderate band: gas, road, maritime, and health.

The drivers behind this progress are consistent across the board: cybersecurity legislation that organizations are actually using to unlock investment rather than just checkbox compliance, increased political attention translating into guidance and resources, and gradual improvements in information sharing and incident preparedness.
“Since the previous edition of this report, cybersecurity maturity across sectors of high criticality in the EU, has been steadily improving as organisations respond to evolving policy requirements and cyber threats they face.” reads the report published by ENISA. “Banking, electricity and telecommunications remain the most mature and critical sectors, while three sectors, trust services, aviation, and financial market infrastructures (FMIs) moved into the high maturity band. Four sectors strengthened their maturity within the moderate band: gas, road, maritime, and health.”
The risk zone is where the report gets harder to read. It includes sectors with criticality that exceeds their maturity, meaning they’re more important to society and the economy than they’re currently prepared to protect. This year, that zone includes health, railway, maritime, ICT service management, space, public administrations, and drinking and waste water.
Rail, drinking water, and waste water moved into the risk zone this year, not because they got worse, but because overall maturity improved across other sectors and the bar moved.
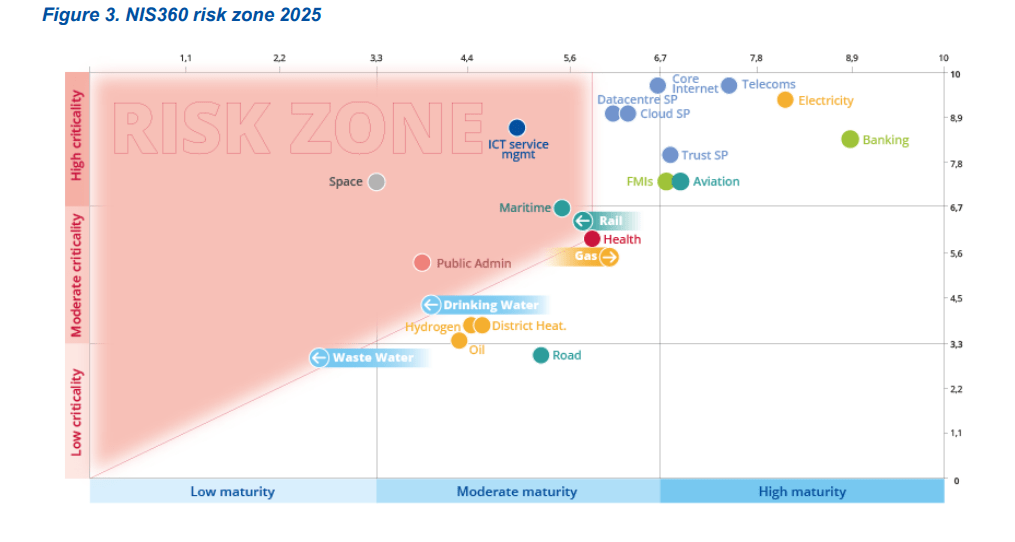
The one piece of positive news is that gas has started moving out of the risk zone, driven by better information sharing and stronger risk management implementation.
“Combining and jointly interpreting the criticality and maturity dimensions helps identify mismatches between the two and helps define the risk zone. The risk zone includes sectors with lower-thanaverage maturity and criticality that exceeds their maturity. Its composition changes over time as overall maturity improves across sectors.” continues the report. “This is one of the reasons why three sectors previously at the risk zone boundary – rail, drinking water, and waste water are now within the risk zone. The positive development is that the gas sector has started moving out of the risk zone. This shift is driven by improved information sharing, stronger collaboration, and better implementation of risk management measures that are to higher maturity.”
Health deserves particular attention because it illustrates how a sector can be getting better on paper while remaining fundamentally exposed. Pharmaceutical manufacturers are raising the overall numbers. Hospitals and healthcare providers, which are the parts of the sector most likely to be attacked and where the human consequences of a disruption are most direct, are still struggling with basic asset tracking, legacy systems, budget constraints, and cybersecurity awareness levels that most other sectors left behind years ago. One in three water sector entities surveyed has never conducted a risk assessment. In public administrations, about one third of entities have no structured process for ensuring cybersecurity expertise at management level, and about half don’t provide cybersecurity training to management at all. This is the sector that receives nearly 63% of all hacktivist attacks and is the most consistently targeted sector in Europe.
The report identifies three dynamics that are reshaping the environment across all sectors. AI is making offensive capabilities more accessible and more effective faster than it’s helping defenders, which means organizations need to detect and respond to threats at timescales that most of them aren’t currently capable of. Supply chain risk is growing because every trusted vendor relationship is also implicitly a trust relationship with everyone that vendor trusted, and the compromise of a single widely-used dependency can now cascade across entire sector landscapes in ways that weren’t possible five years ago. Geopolitical volatility is increasing the frequency and sophistication of state-aligned attacks while simultaneously creating pressure to reduce dependency on technology from outside the EU.
“With the benefits of AI thus far materialising faster for attackers than defenders, and the further proliferation and commoditisation of AI-enabled offensive capabilities being a matter of time, sectoral stakeholders are currently faced with mounting pressure when it comes to effectively adapting to the more dynamic threat environment brought forward by AI.” states ENISA.
The space sector’s situation is particularly worth noting given how much Europe is depending on it. Space underpins positioning and navigation used by financial systems for timestamping trades, telecommunications networks for synchronisation, agriculture, emergency response, border surveillance, and military communications. Its criticality score was revised upward this year to reflect this growing dependency. Its maturity score sits at the lower end of moderate, with enormous variation across entities depending on whether they fall under NIS2 scope or not. Some entities have mature, proactive security practices. Others struggle to define cybersecurity roles and responsibilities at all. There’s no dedicated EU-level forum for cybersecurity collaboration in the space sector, and information sharing remains limited. A sector that’s being positioned as a cornerstone of European strategic autonomy is also one of the least cybersecurity-mature sectors in the assessment.
The finance sector, by contrast, shows what sustained regulatory pressure and enforcement actually produces. Banking has long experience with compliance as a floor rather than a ceiling, and it shows. The FMI sector jumped a full maturity band this year, driven in substantial part by DORA implementation giving organizations a structured framework to work from and supervisory authorities the tools to hold them accountable. The lesson isn’t that more regulation automatically produces better security, but that regulation with teeth, clear requirements, and supervisory capacity actually changes behavior at scale. The contrast with ICT service management, where national authorities are often new to the sector, lack sector-specific expertise, and have limited resources, makes this point in the opposite direction.
Progress is real. It’s also not fast enough, and it’s not evenly distributed. The sectors that can least afford to be underprepared are the ones with the most ground to cover.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ENISA NIS360 2026)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。