


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

让小产品的独立变现更简单 - ezindie.com
Y
Y Combinator Blog
Blog — PlanetScale
Blog — PlanetScale
H
Hackread – Cybersecurity News, Data Breaches, AI and More
WordPress大学
WordPress大学
B
Blog RSS Feed
A
About on SuperTechFans
V
Visual Studio Blog
J
Java Code Geeks
U
Unit 42
人人都是产品经理
人人都是产品经理
Martin Fowler
Martin Fowler
Recent Announcements
M
MIT News - Artificial intelligence
IT之家
IT之家
The Cloudflare Blog
T
The Blog of Author Tim Ferriss
C
Check Point Blog
博客园 - 叶小钗
P
Proofpoint News Feed
Microsoft Security Blog
B
Blog
S
SegmentFault 最新的问题
Microsoft Azure Blog

Deno

Deno 2.8 | Deno Claw Patrol: an open-source security firewall for agents | Deno Fresh 2.3: Zero JS by default, View Transitions, and Temporal support | Deno Deno 2.7: Temporal API, Windows ARM, and npm overrides | Deno Build a dinosaur runner game with Deno, pt. 6 | Deno Build a dinosaur runner game with Deno, pt. 5 | Deno Deno Deploy is Generally Available | Deno Introducing Deno Sandbox | Deno Build a dinosaur runner game with Deno, pt. 4 | Deno Build a dinosaur runner game with Deno, pt. 3 | Deno Build a dinosaur runner game with Deno, pt. 2 | Deno React / Next.js Denial-of-Service Vulnerability: Deno Deploy users protected | Deno Deno 2.6: dx is the new npx | Deno Build a dinosaur runner game with Deno, pt. 1 | Deno React Server Functions / Next.js Vulnerability: Deno Deploy users protected | Deno My highlights from the new Deno Deploy | Deno Deno's Other Open Source Projects | Deno How Deno protects against npm exploits | Deno Help Us Raise $200k to Free JavaScript from Oracle | Deno Deno 2.5: Permissions in the config file | Deno Fresh 2.0 Graduates to Beta, Adds Vite Support | Deno Deno 2.4: deno bundle is back | Deno JavaScript™ Trademark Update | Deno What's coming to JavaScript | Deno A brief history of JavaScript | Deno Reports of Deno's Demise Have Been Greatly Exaggerated | Deno An Update on Fresh | Deno How Plaid migrated 100 services to a new database platform 5x faster with Deno | Deno Deno 2.3: Improved deno compile, local npm packages, and more | Deno Add JSR packages with pnpm and Yarn | Deno
Build a More Secure Web using npm with Deno | Deno
Andy Jiang · 2022-11-17 · via Deno

npm has made software easily accessible and usable, growing and enriching the JavaScript community. However, since Node installs and runs dependencies by granting full access to the filesystem, environment, the internet, etc., Node programs are more susceptible to supply chain attacks.

Supply chain attacks are nothing new. But given that the npm registry is the largest in the world, with more and more JavaScript developers using it to build apps and websites, npm is a constant target for these dependency attacks.

Deno makes npm better and building with it is more secure, since Deno’s secure-by-default and unique sandboxed architecture help mitigates dependency based attacks.

Secure by default

Malicious npm modules have been reported to steal user data from forms, perform shell injection attacks, and install malware onto your machine. These attacks are more likely in Node because Node apps (and its dependencies) all have unfettered access to everything—the filesystem, the internet, environment variables, etc.

Below is a demo of a particularly sinister shell injection attack using bin script confusion:
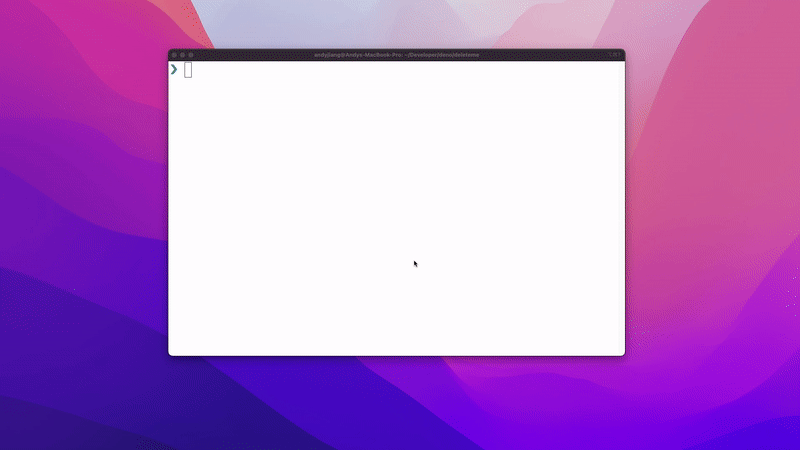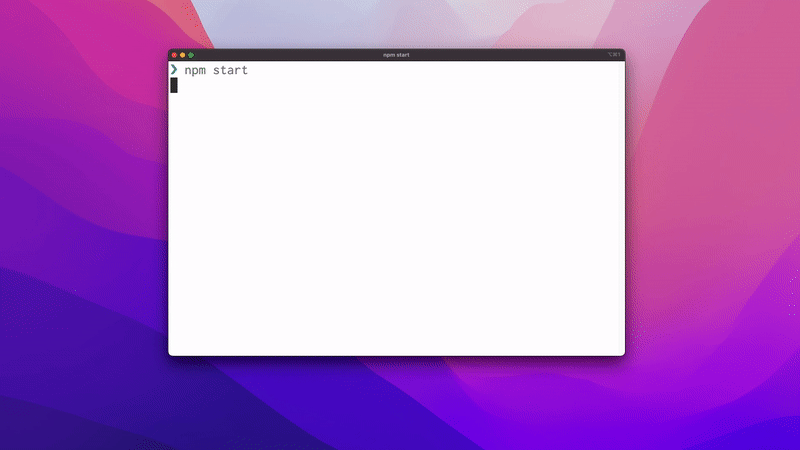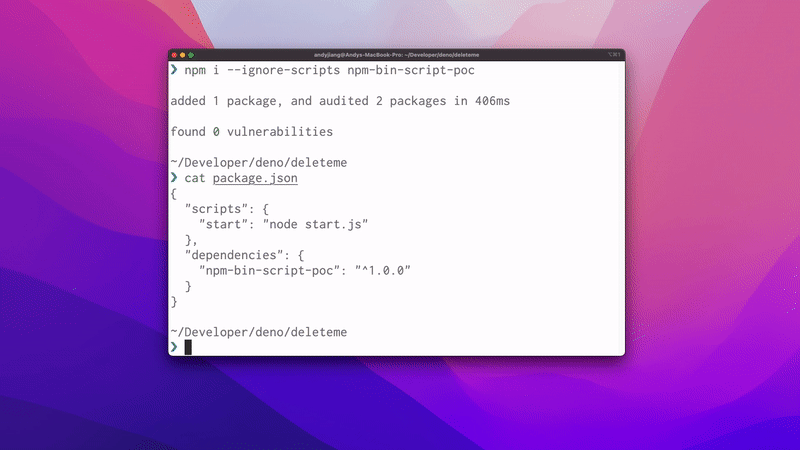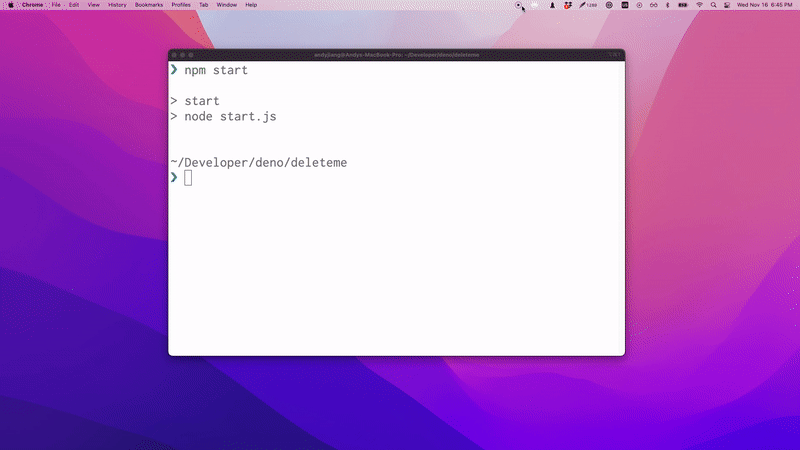
a demo of a bin injection attack in node
A bin injection attack in Node. Originally reported by Socket.dev

Deno runs code in a sandbox and uses an “opt-in” permission model. That means unless you specifically enable it, a program run with Deno has no file, network, or environment access. Access requires permissions granted through command line flags or a runtime permission prompt:
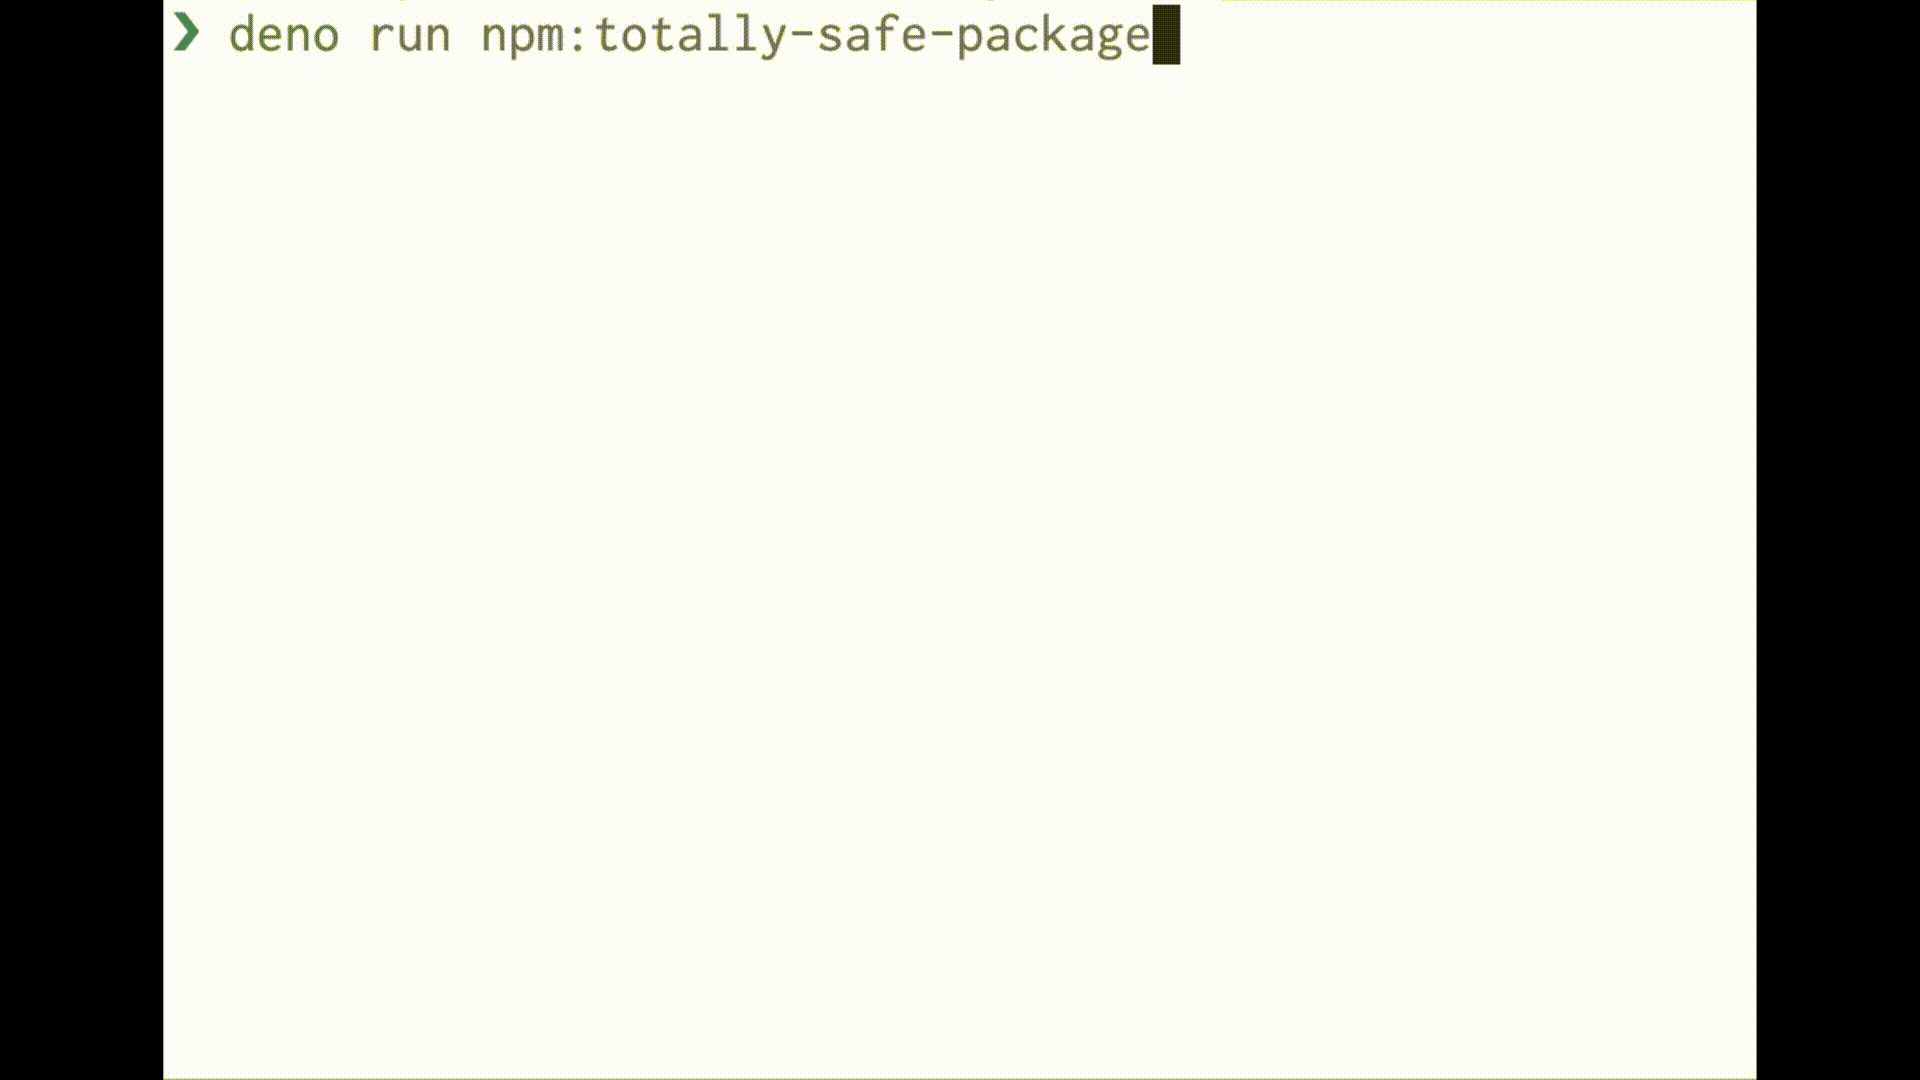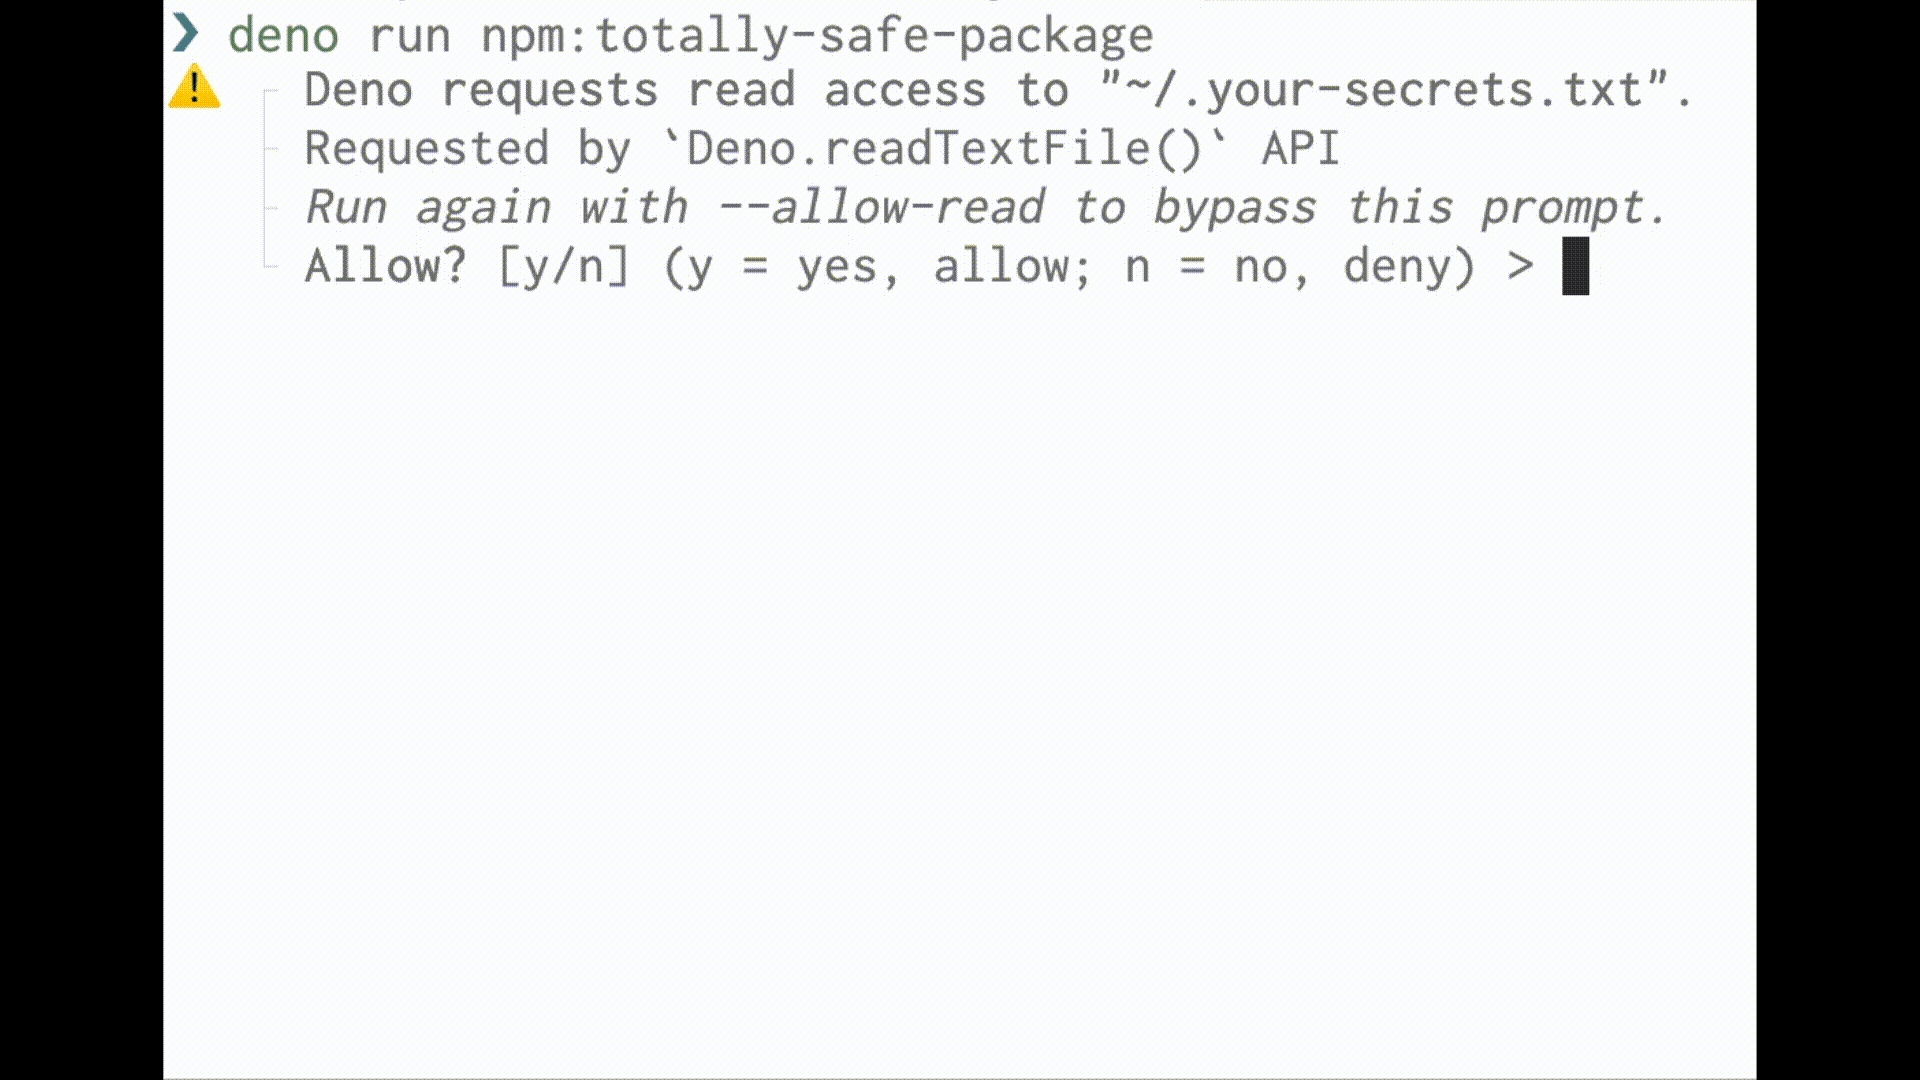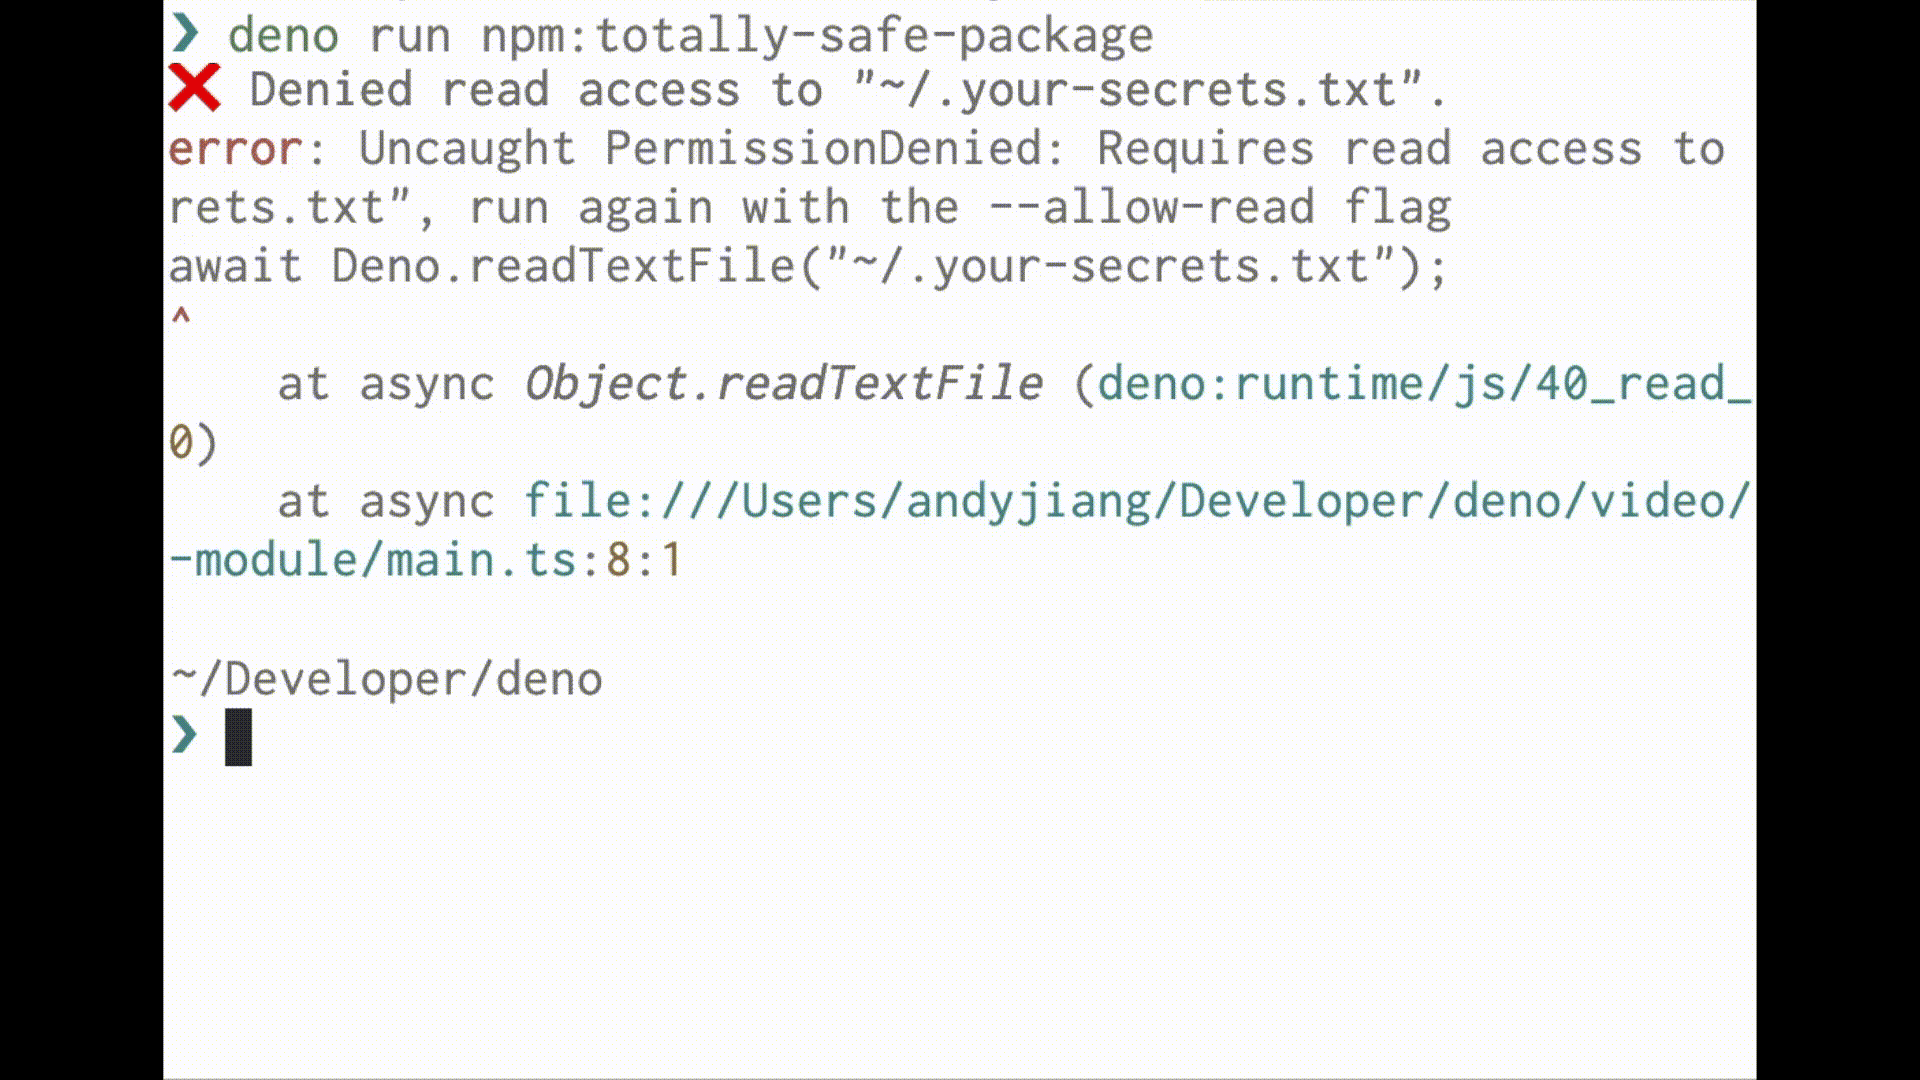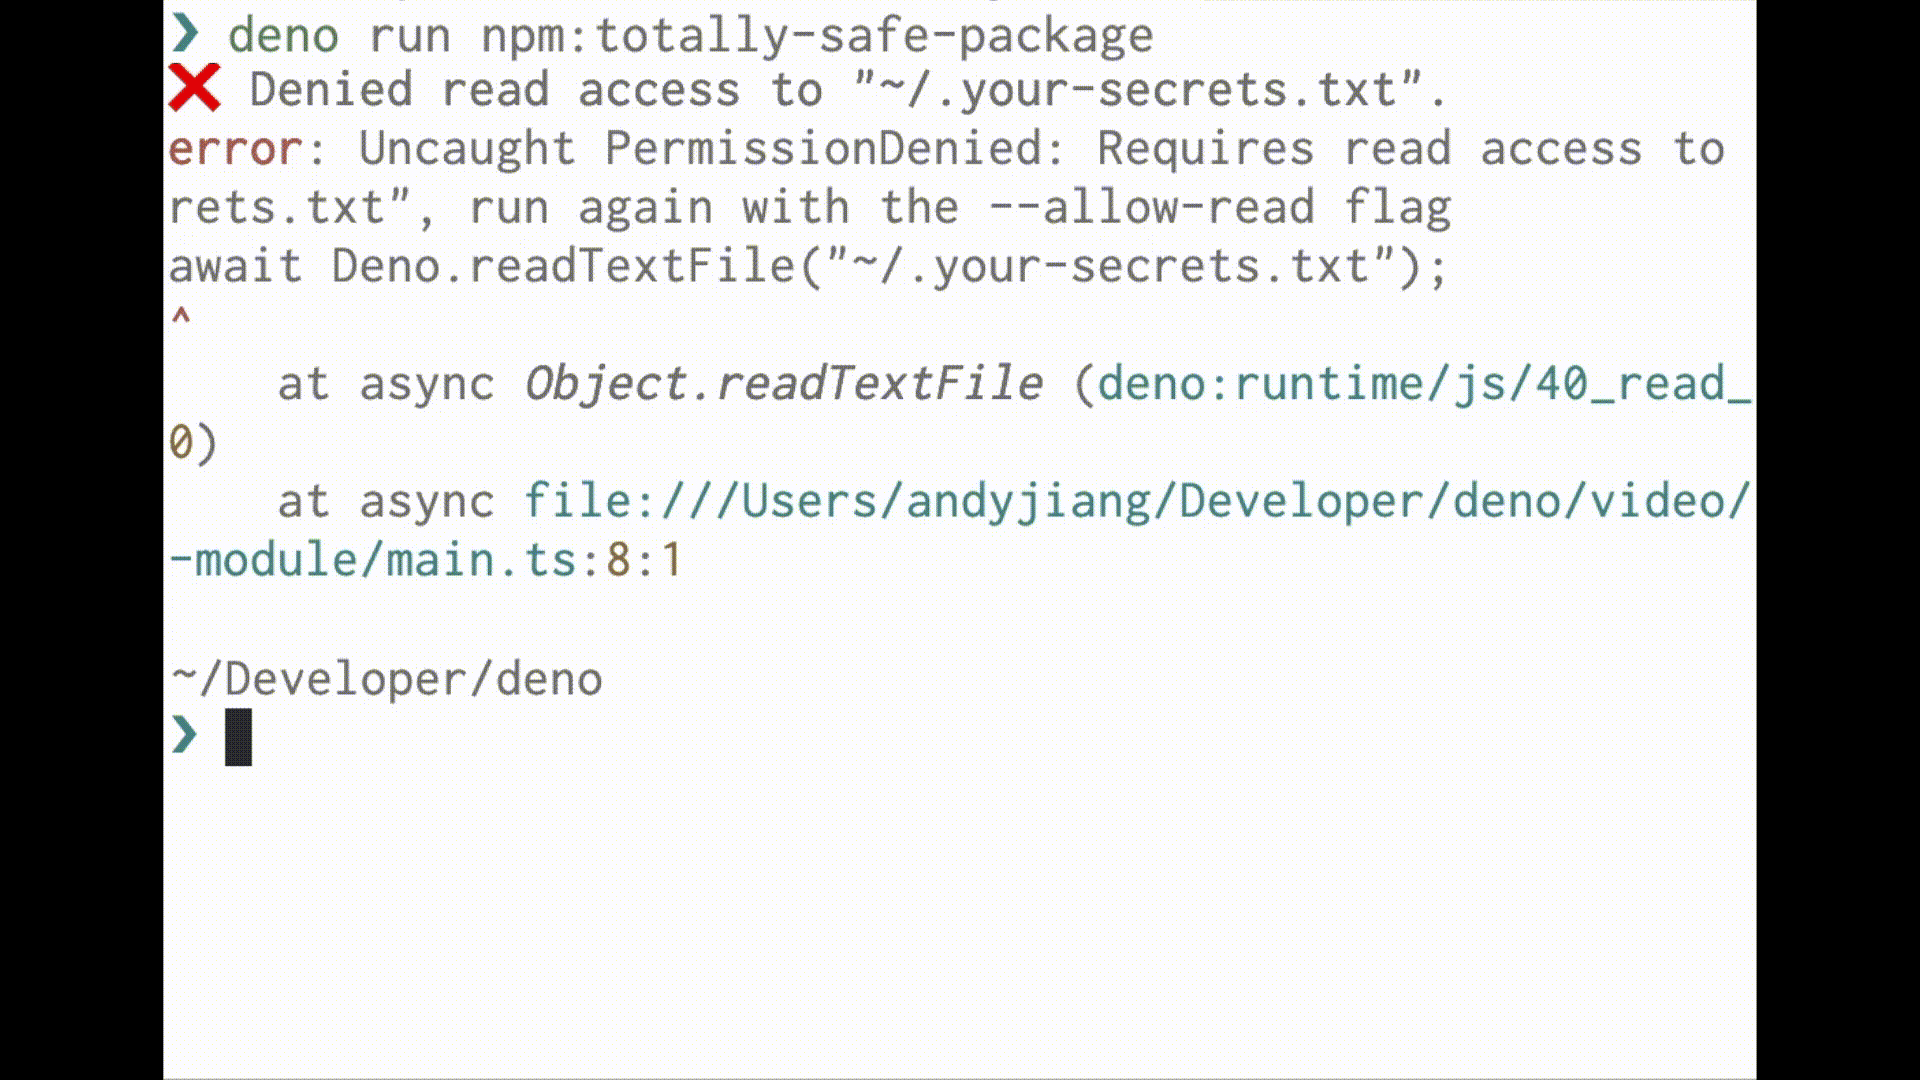
gif of deno asking the user for permissions

For a full list of permissions, see here.

When you run a script with Deno, you are aware of what access it needs.

Sandboxed Architecture

Deno’s permission model succeeds since the program is executed in a sandbox, which has a narrow entrypoint with few APIs to external systems. This makes it easy to manage all the data going to and from the code.
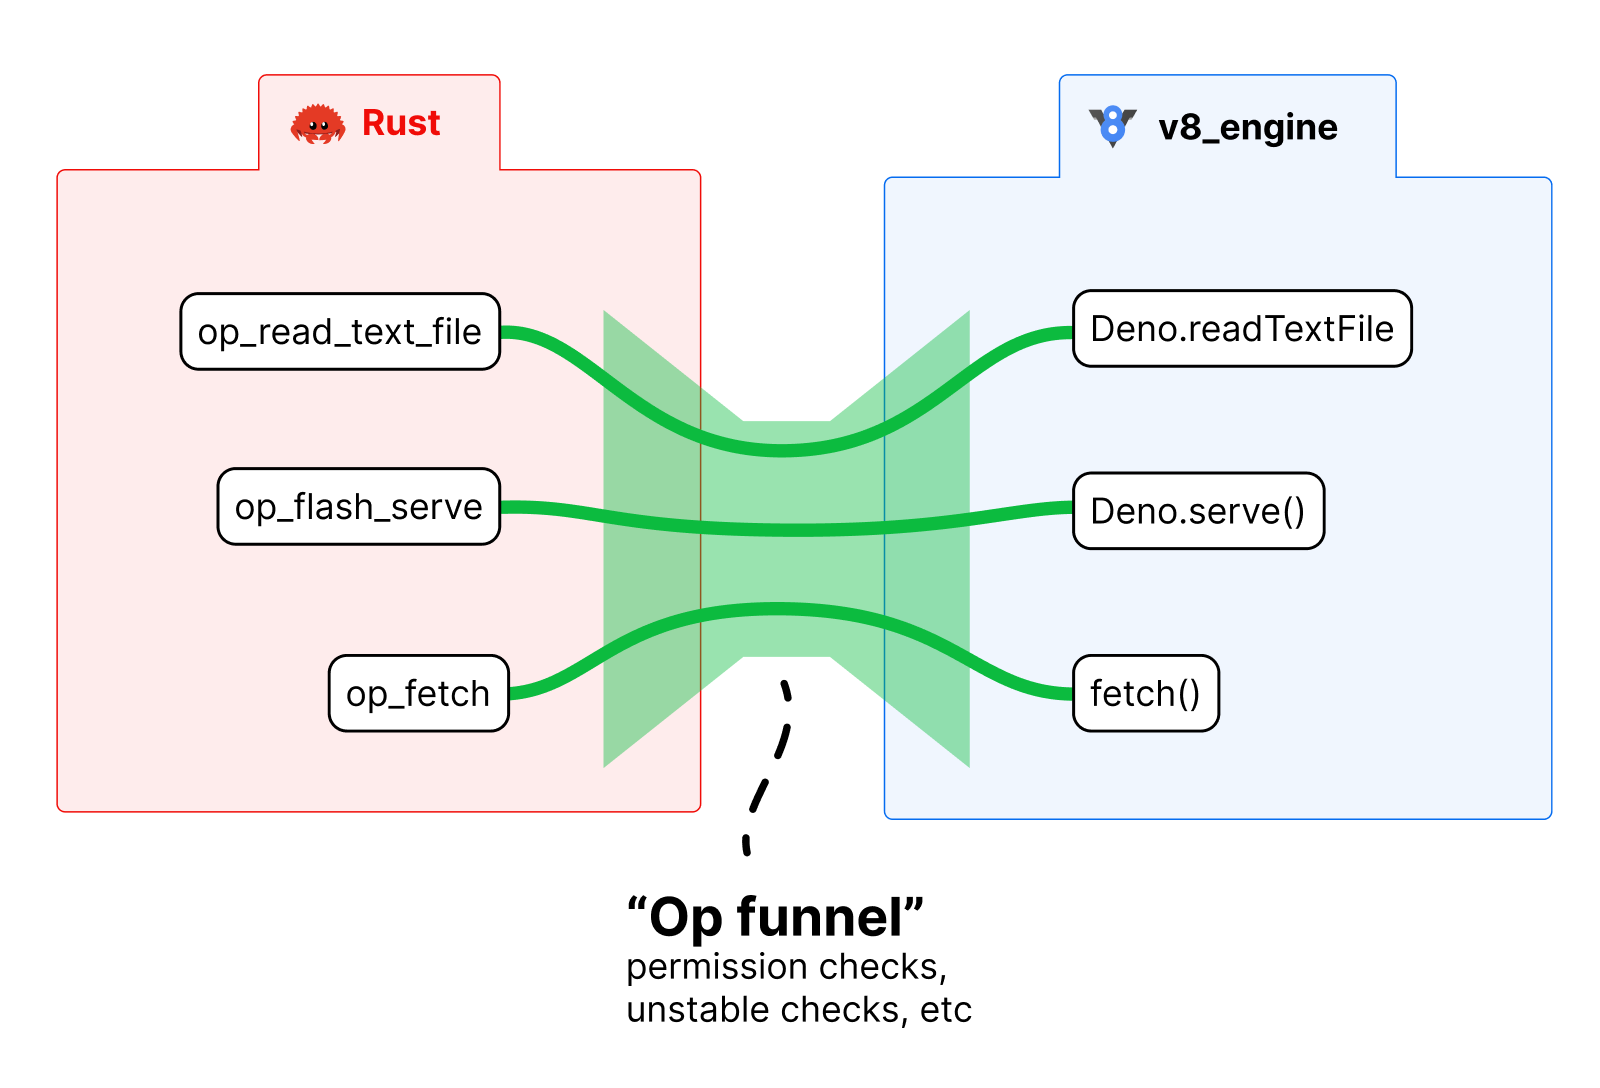
Diagram of Deno sandbox
The entry point into the V8 sandbox only has a few APIs, making it easy to audit what it needs access to.

Like a Browser

Deno’s security system is borrowed from the privacy model of modern browsers.

Whenever your browser requires access to your webcam, microphone, even geolocation API, it prompts you for permission. This means (theoretically) you are fully aware of the access the website you’re visiting has of your computer.

Deno is similar, in that it puts the control in your hands. When executing third party, untrusted code, or a random dependency, you are aware of what it needs access to.

What’s next?

Being able to browse the web safely is critical to its growth and usage. Building a more secure web with npm is easier with Deno, with its sandboxed, opt-in permissions approach helping to mitigate supply chain attacks.

What are you building with Deno? Let us know on Twitter or Discord!