
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

人人都是产品经理
人人都是产品经理
博客园_首页
IT之家
IT之家
让小产品的独立变现更简单 - ezindie.com
Vercel News
Vercel News
美团技术团队
D
Docker
WordPress大学
WordPress大学
T
Tailwind CSS Blog
酷 壳 – CoolShell
酷 壳 – CoolShell
The Cloudflare Blog
Y
Y Combinator Blog
F
Fortinet All Blogs
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
G
Google Developers Blog
爱范儿
爱范儿
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
月光博客
月光博客
MongoDB | Blog
MongoDB | Blog
S
SegmentFault 最新的问题
GbyAI
GbyAI
Hugging Face - Blog
Hugging Face - Blog
Microsoft Azure Blog
A
About on SuperTechFans

WeLiveSecurity

Supply chain dependencies: Have you checked your blind spot? Recovery scammers hit you when you’re down: Here’s how to avoid a ‘second strike’ As breakout time accelerates, prevention-first cybersecurity takes center stage Digital assets after death: Managing risks to your loved one’s digital estate This month in security with Tony Anscombe – March 2026 edition RSAC 2026 wrap-up – Week in security with Tony Anscombe A cunning predator: How Silver Fox preys on Japanese firms this tax season Virtual machines, virtually everywhere – but not all protected Cloud workload security: Mind the gaps Move fast and save things: A quick guide to recovering a hacked account EDR killers explained: Beyond the drivers Face value: What it takes to fool facial recognition Cyber fallout from the Iran war: What to have on your radar Sednit reloaded: Back in the trenches What cybersecurity actually does for your business How SMBs use threat research and MDR to build a defensive edge Protecting education: How MDR can tip the balance in favor of schools This month in security with Tony Anscombe – February 2026 edition Mobile app permissions (still) matter more than you may think Faking it on the phone: How to tell if a voice call is AI or not PromptSpy ushers in the era of Android threats using GenAI Is Poshmark safe? How to buy and sell without getting scammed Is it OK to let your children post selfies online? Naming and shaming: How ransomware groups tighten the screws on victims Taxing times: Top IRS scams to look out for in 2026 OfferUp scammers are out in force: Here’s what you should know A slippery slope: Beware of Winter Olympics scams and other cyberthreats This month in security with Tony Anscombe – January 2026 edition DynoWiper update: Technical analysis and attribution Love? Actually: Fake dating app used as lure in targeted spyware campaign in Pakistan
SnakeStealer: How it preys on personal data – and how to ...
Martina López · 2025-10-22 · via WeLiveSecurity

Malware

SnakeStealer: How it preys on personal data – and how you can protect yourself

Here’s what to know about the malware with an insatiable appetite for valuable data, so much so that it tops this year's infostealer detection charts

22 Oct 2025  •  , 3 min. read
SnakeStealer: How it preys on personal data – and how you can protect yourself

Infostealers remain one of the most persistent threats on today’s threat landscape. They’re built to quietly siphon off valuable information, typically login credentials and financial and cryptocurrency details, from compromised systems and send it to adversaries. And they do so with great success.

ESET researchers have tracked numerous campaigns recently where an infostealer was the final payload. Agent Tesla, Lumma Stealer, FormBook and HoudRAT continue to make the rounds in large numbers, but according to the ESET Threat Report H1 2025, one family surged ahead of the rest in the first half of this year: SnakeStealer.

A threat is born

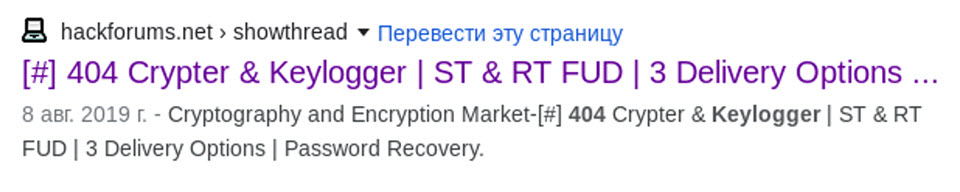
Detected by ESET products mainly as MSIL/Spy.Agent.AES, SnakeStealer first appeared in 2019. Early reports traced it to a threat originally marketed as 404 Keylogger or 404 Crypter on underground forums before it rebranded under its current name.
snake-stealer-infostealer-robo-contrasenas
Figure 1. One of the first advertisements for 404 Keylogger (source: habr.com)

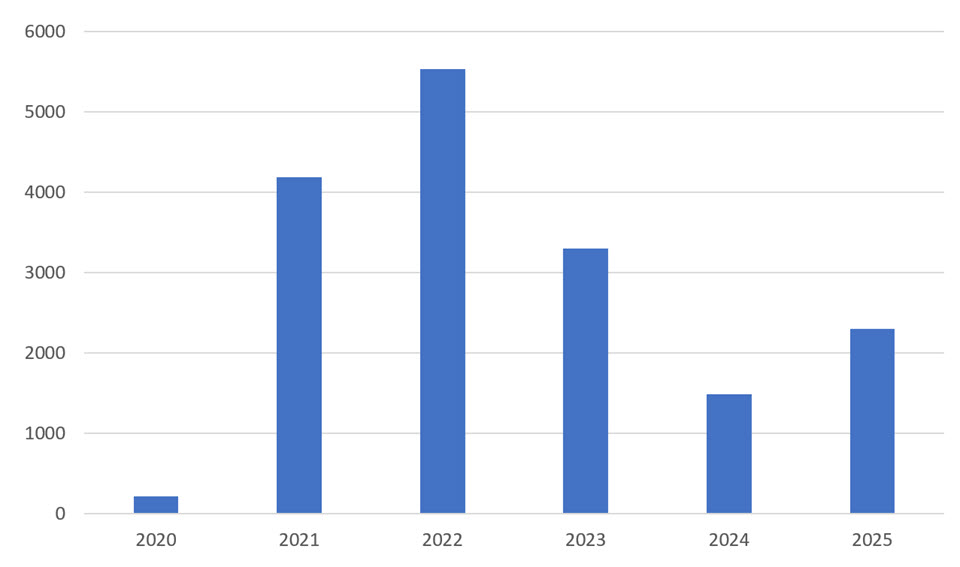
In its early variants, SnakeStealer used Discord to host its payloads, which victims unwittingly downloaded after opening a malicious email attachment. While hosting malware on legitimate cloud platforms wasn’t new, the widespread abuse of Discord soon became a hallmark tactic. SnakeStealer reached its first big wave of activity in 2020 and 2021, spreading globally without any clear regional focus.

Meanwhile, the delivery methods varied. Phishing attachments still remain the primary vector, but the payload itself may be disguised in various forms, including password-protected ZIP files, weaponized RTF, ISO and PDF files, or even bundled with other malware. Occasionally, SnakeStealer hides inside pirated software or fake apps, which speaks to the fact that not every compromise begins with a malicious email.
snake-stealer-infostealer-robo-contrasenas2
Figure 2. Hashes related to SnakeStealer, reported by year. (source: MalwareBazaar)

Malware-as-a-service: A profitable 'business model'

Like many other modern threats, SnakeStealer follows the malware-as-a-service (MaaS) model. Its operators rent or sell access to the malware, complete with technical support and updates, which makes it easy for even low-skilled attackers to launch their own campaigns.

SnakeStealer’s recent resurgence is no coincidence. After Agent Tesla began to decline and lose developer support, underground Telegram channels started recommending SnakeStealer as its successor. This endorsement, combined with the convenience of its MaaS setup and its ready-made infrastructure, propelled SnakeStealer to the top of detection charts, so much so that SnakeStealer was recently responsible for almost one-fifth of global infostealer detections as tracked by ESET telemetry.

Figure 3. SnakeStealer topping detection charts
Figure 3. SnakeStealer topping detection charts (source: ESET Threat Report H1 2025)

Key features

SnakeStealer may not break new ground, but it’s polished, reliable, and easy to deploy. It offers a full toolkit of capabilities that’s typical of professional-grade info-stealing malware, and given its modularity, attackers can switch features on or off to suit their needs.

  • Evasion: In order to stay under the radar, SnakeStealer can terminate processes associated with security and malware analysis tools and check for virtual environments.
  • Persistence: It alters Windows boot configurations to maintain access on compromised systems.
  • Credential theft: It extracts saved passwords from web browsers, databases, email and chat clients, including Discord, and Wi-Fi networks.
  • Surveillance: It captures clipboard data, takes screenshots and logs keystrokes.
  • Exfiltration: It sends stolen data via FTP, HTTP, email, or Telegram bots.

How to protect yourself

Whether you’re an individual user or a business, these steps can help reduce the risk against infostealers like SnakeStealer:

  • Be skeptical of unsolicited messages. Treat attachments and links, especially from unknown senders, as potential threats, even if they appear legitimate. Verify them with the sender through other channels.
  • Keep your system and apps updated. Patching known vulnerabilities in a timely manner reduces the risk of compromise stemming from software loopholes.
  • Enable multi-factor authentication (MFA) wherever possible. Even if your password is stolen, MFA can stop unauthorized logins.
  • If you suspect a compromise: change all passwords from a clean device, revoke open sessions, and monitor your accounts for suspicious activity.
  • Use reputable security software on all devices, desktop and mobile alike.

Final thoughts

SnakeStealer’s rise is a reminder of how quickly the cybercrime market adapts and as such reflects a larger truth about today’s threat landscape: cybercrime has industrialized. This professionalization makes it easier than ever for anyone to steal data at scale. And as one infostealer fades, another fills the gap, armed with largely the same tried-and-tested tactics. The good news is that strong cybersecurity practices will go a long way towards keeping you safe.


Let us keep you
up to date

Sign up for our newsletters