







Mobile devices have become one of the most dynamic, and most exposed, parts of the modern attack surface. They access sensitive data, connect to untrusted networks, and rely heavily on third-party applications. Yet in many organizations, mobile security still lags behind traditional endpoint protection.
Mobile device management (MDM) solutions help enforce configuration and compliance, but they were never designed to detect and respond to modern threats. As adversaries increasingly exploit mobile threat vectors, organizations need a purpose-built approach.
Aurora Mobile Threat Defense (MTD) extends Arctic Wolf’s ability to protect mobile devices, delivering comprehensive protection, visibility, and response across the full mobile attack surface.
Mobile risk is not isolated to a single control point. Instead, it spans devices, networks, applications, phishing, and especially privacy exposure; each introducing unique challenges that traditional tools cannot fully address.
Aurora MTD brings these elements together through a unified model; Device, Network, Application, and Phishing or DNAP, helping security teams to understand how risk originates, how it evolves, and where to act. Rather than managing disconnected signals, teams gain a cohesive view that is designed to accelerate faster detection and more informed decision-making.
Aurora MTD is designed to reduce friction between insight and action. The console surfaces real-time visibility across the entire mobile environment while enabling teams to quickly pivot into specific risk domains without losing context.
Security teams can move seamlessly from high-level dashboards into detailed investigations, allowing them to prioritize what matters most and respond with confidence. This streamlined experience reduces the need to stitch together data from multiple tools and instead delivers a single, operational view of mobile security.
Every mobile device introduces variability in security posture, and Aurora MTD turns that complexity into clarity.
Teams gain continuous visibility into device health, configuration, and operating system status, making it easier to identify outdated or misconfigured devices before they become vulnerabilities. Detailed device-level timelines and filtering capabilities allow teams to quickly isolate issues, investigate anomalies, and understand how risk evolves over time.
By making device posture actionable, not just visible, Aurora MTD enables organizations to shift from reactive remediation to proactive risk reduction.
Applications are one of the most common vectors for mobile compromise, but risk is often misunderstood or oversimplified. Aurora MTD addresses this by distinguishing between security risk and privacy risk, giving organizations a more nuanced understanding of their exposure.
This clarity allows teams to confidently evaluate whether an application poses a direct threat, introduces excessive data exposure, or both. Rich app intelligence, behavioral analysis, permissions visibility, and compliance insights provides the context needed to take informed action.
Instead of relying on assumptions, security teams can quickly determine which applications require mitigation, which are acceptable, and how to manage risk across the broader app ecosystem.
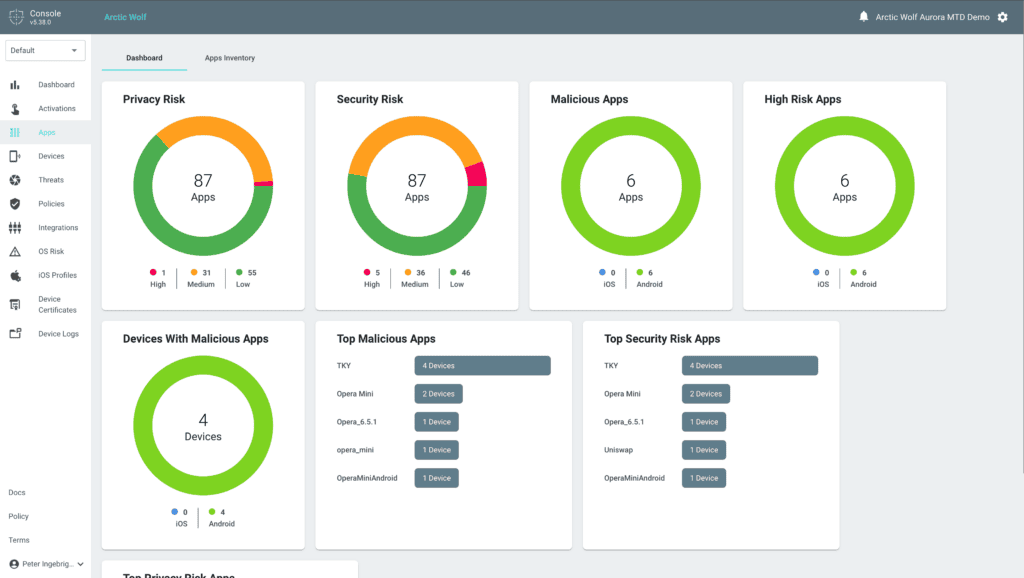
Aurora MTD Apps dashboard highlighting risk introduced by apps
Aurora MTD transforms mobile threat detection into an experience centered on clarity and context rather than alert volume.
Every alert is accompanied by meaningful insight, including device context, threat behavior, and associated network or location data. This enables teams to quickly understand not just what happened, but why it matters and how to respond.
Threat activity can be visualized over time, helping teams identify patterns, correlate events, and prioritize response efforts more effectively. This can lead to faster investigations, reduced noise, and more confident decision-making.
Aurora MTD empowers organizations to define how protection is applied through flexible, policy-driven controls.
Security teams can tailor policies to different user groups, ensuring that device behavior, network access, phishing protection, and response actions align with organizational risk tolerance. This includes the ability to enforce OS update requirements, restrict communication with known risky domains or regions, and apply advanced phishing and content filtering controls.
Beyond prevention, Aurora MTD enables automated response actions such as blocking malicious communication paths, helping stop threats before they can escalate. This combination of precision and automation ensures that protection scales without increasing operational burden.
Aurora MTD is designed to extend the value of existing mobile management tools rather than replace them.
By combining management and security capabilities, organizations gain a more complete and effective approach to protecting mobile environments.
Deploying Aurora MTD is straightforward, minimizing disruption while accelerating time to protection.
Users are guided through a simple activation process, with clear visibility into what data is collected and how it is used. Once installed, devices are quickly scanned and protected, allowing organizations to quickly extend security coverage across their mobile fleet.
End users also gain the ability to proactively evaluate risk, such as analyzing suspicious links before interacting with them, bringing an added layer of awareness directly to the endpoint.
Mobile devices are now central to how work gets done, making them a critical component of the overall security strategy. Aurora Mobile Threat Defense ensures they are treated as such by delivering:
By integrating these capabilities into the broader Aurora Platform, organizations can extend their securit
As attackers continue to exploit mobile vectors, relying on MDM alone leaves a critical gap in protection.
Aurora Mobile Threat Defense closes that gap — delivering the visibility, context, and control needed to secure today’s mobile-first workforce while aligning with the broader goal of building cyber resilience at scale.
To see Aurora Mobile Threat Defense and the benefits featured in this blog, watch the demo video:
This blog may include forward‑looking statements. These reflect our current views and are subject to change. They are not guarantees, and actual results may vary.
This blog is provided for informational purposes only. It reflects general industry perspectives and practices and is not intended to represent a guarantee, assurance, or measure of performance. Actual results, outcomes, and capabilities vary by organization, environment, and implementation.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。