
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

MongoDB | Blog
MongoDB | Blog
B
Blog RSS Feed
MyScale Blog
MyScale Blog
M
MIT News - Artificial intelligence
H
Hackread – Cybersecurity News, Data Breaches, AI and More
J
Java Code Geeks
U
Unit 42
Blog — PlanetScale
Blog — PlanetScale
L
LangChain Blog
C
Check Point Blog
WordPress大学
WordPress大学
Last Week in AI
Last Week in AI
人人都是产品经理
人人都是产品经理
T
Tailwind CSS Blog
Vercel News
Vercel News
腾讯CDC
GbyAI
GbyAI
有赞技术团队
有赞技术团队
S
SegmentFault 最新的问题
H
Help Net Security
博客园 - 三生石上(FineUI控件)
D
DataBreaches.Net
Microsoft Security Blog
小众软件
小众软件

Ethereum Foundation Blog

Checkpoint #9: Apr 2026 | Ethereum Foundation Blog How L1 and L2s can build the strongest possible Ethereum | Ethereum Foundation Blog The Promise of Ethereum: Introducing the EF Mandate | Ethereum Foundation Blog This Is Fine (Until the Grant Runs Out) | Ethereum Foundation Blog Treasury Staking Initiative | Ethereum Foundation Blog The Ethereum Foundation's Commitment to DeFi | Ethereum Foundation Blog Protocol Priorities Update for 2026 | Ethereum Foundation Blog Announcing the Platform Team at EF | Ethereum Foundation Blog Ethereum Protocol Studies 2026 | Ethereum Foundation Blog Executive Leadership Update | Ethereum Foundation Blog An update from Tomasz | Ethereum Foundation Blog Introducing the EF Academic Secretariat 2026 PhD Fellowship | Ethereum Foundation Blog Trillion Dollar Security Day at Devconnect | Ethereum Foundation Blog Allocation Update - Q4 2025 | Ethereum Foundation Blog Checkpoint #8: Jan 2026 | Ethereum Foundation Blog Devcon 8 is coming to Mumbai, India in November 2026 | Ethereum Foundation Blog Hegota Upgrade EIP Proposal Timelines | Ethereum Foundation Blog Shipping an L1 zkEVM #2: The Security Foundations | Ethereum Foundation Blog The Future of Ethereum’s State | Ethereum Foundation Blog Devconnect Argentina Recap | Ethereum Foundation Blog Allocation Update - Q3 2025 | Ethereum Foundation Blog Making Ethereum Feel Like One Chain Again | Ethereum Foundation Blog Checkpoint #7: Nov 2025 | Ethereum Foundation Blog Fusaka Mainnet Announcement | Ethereum Foundation Blog 2 weeks to Devconnect: Everything you need to know | Ethereum Foundation Blog Unveiling ESP's New Grants Program | Ethereum Foundation Blog Fusaka Update – Transaction Gas Limit Cap arrives with EIP-7825 | Ethereum Foundation Blog Fusaka Update - Information for Blob users | Ethereum Foundation Blog Announcing the 2026 EF Internship | Ethereum Foundation Blog Supporting privacy with new funding mechanisms | Ethereum Foundation Blog
blog.ethereum.org mailing list incident | Ethereum Founda...
2024-07-02 · via Ethereum Foundation Blog

On 2024-06-23, 00:19 AM UTC, a phishing email was sent out to 35,794 email addresses by updates@blog.ethereum.org with the following content
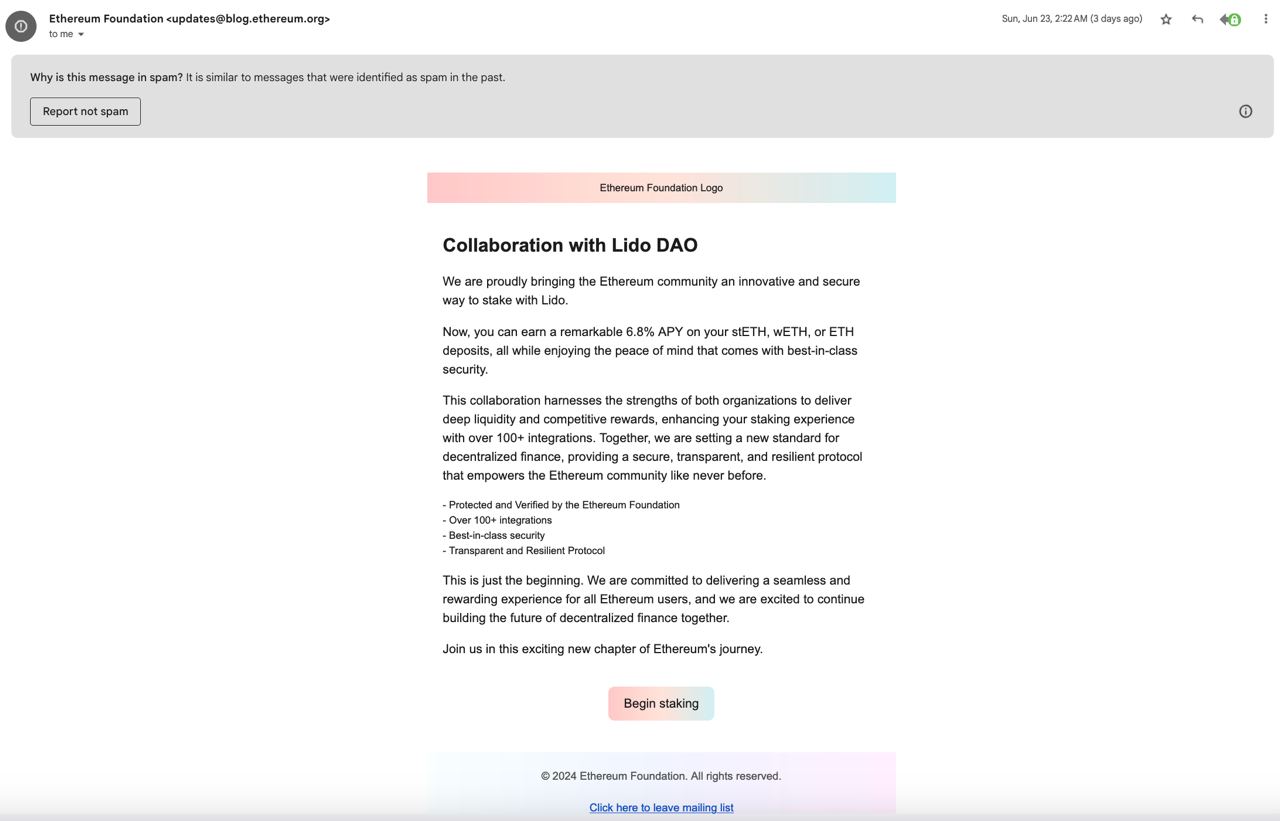
Users who clicked the link in the email were sent to a malicious website:
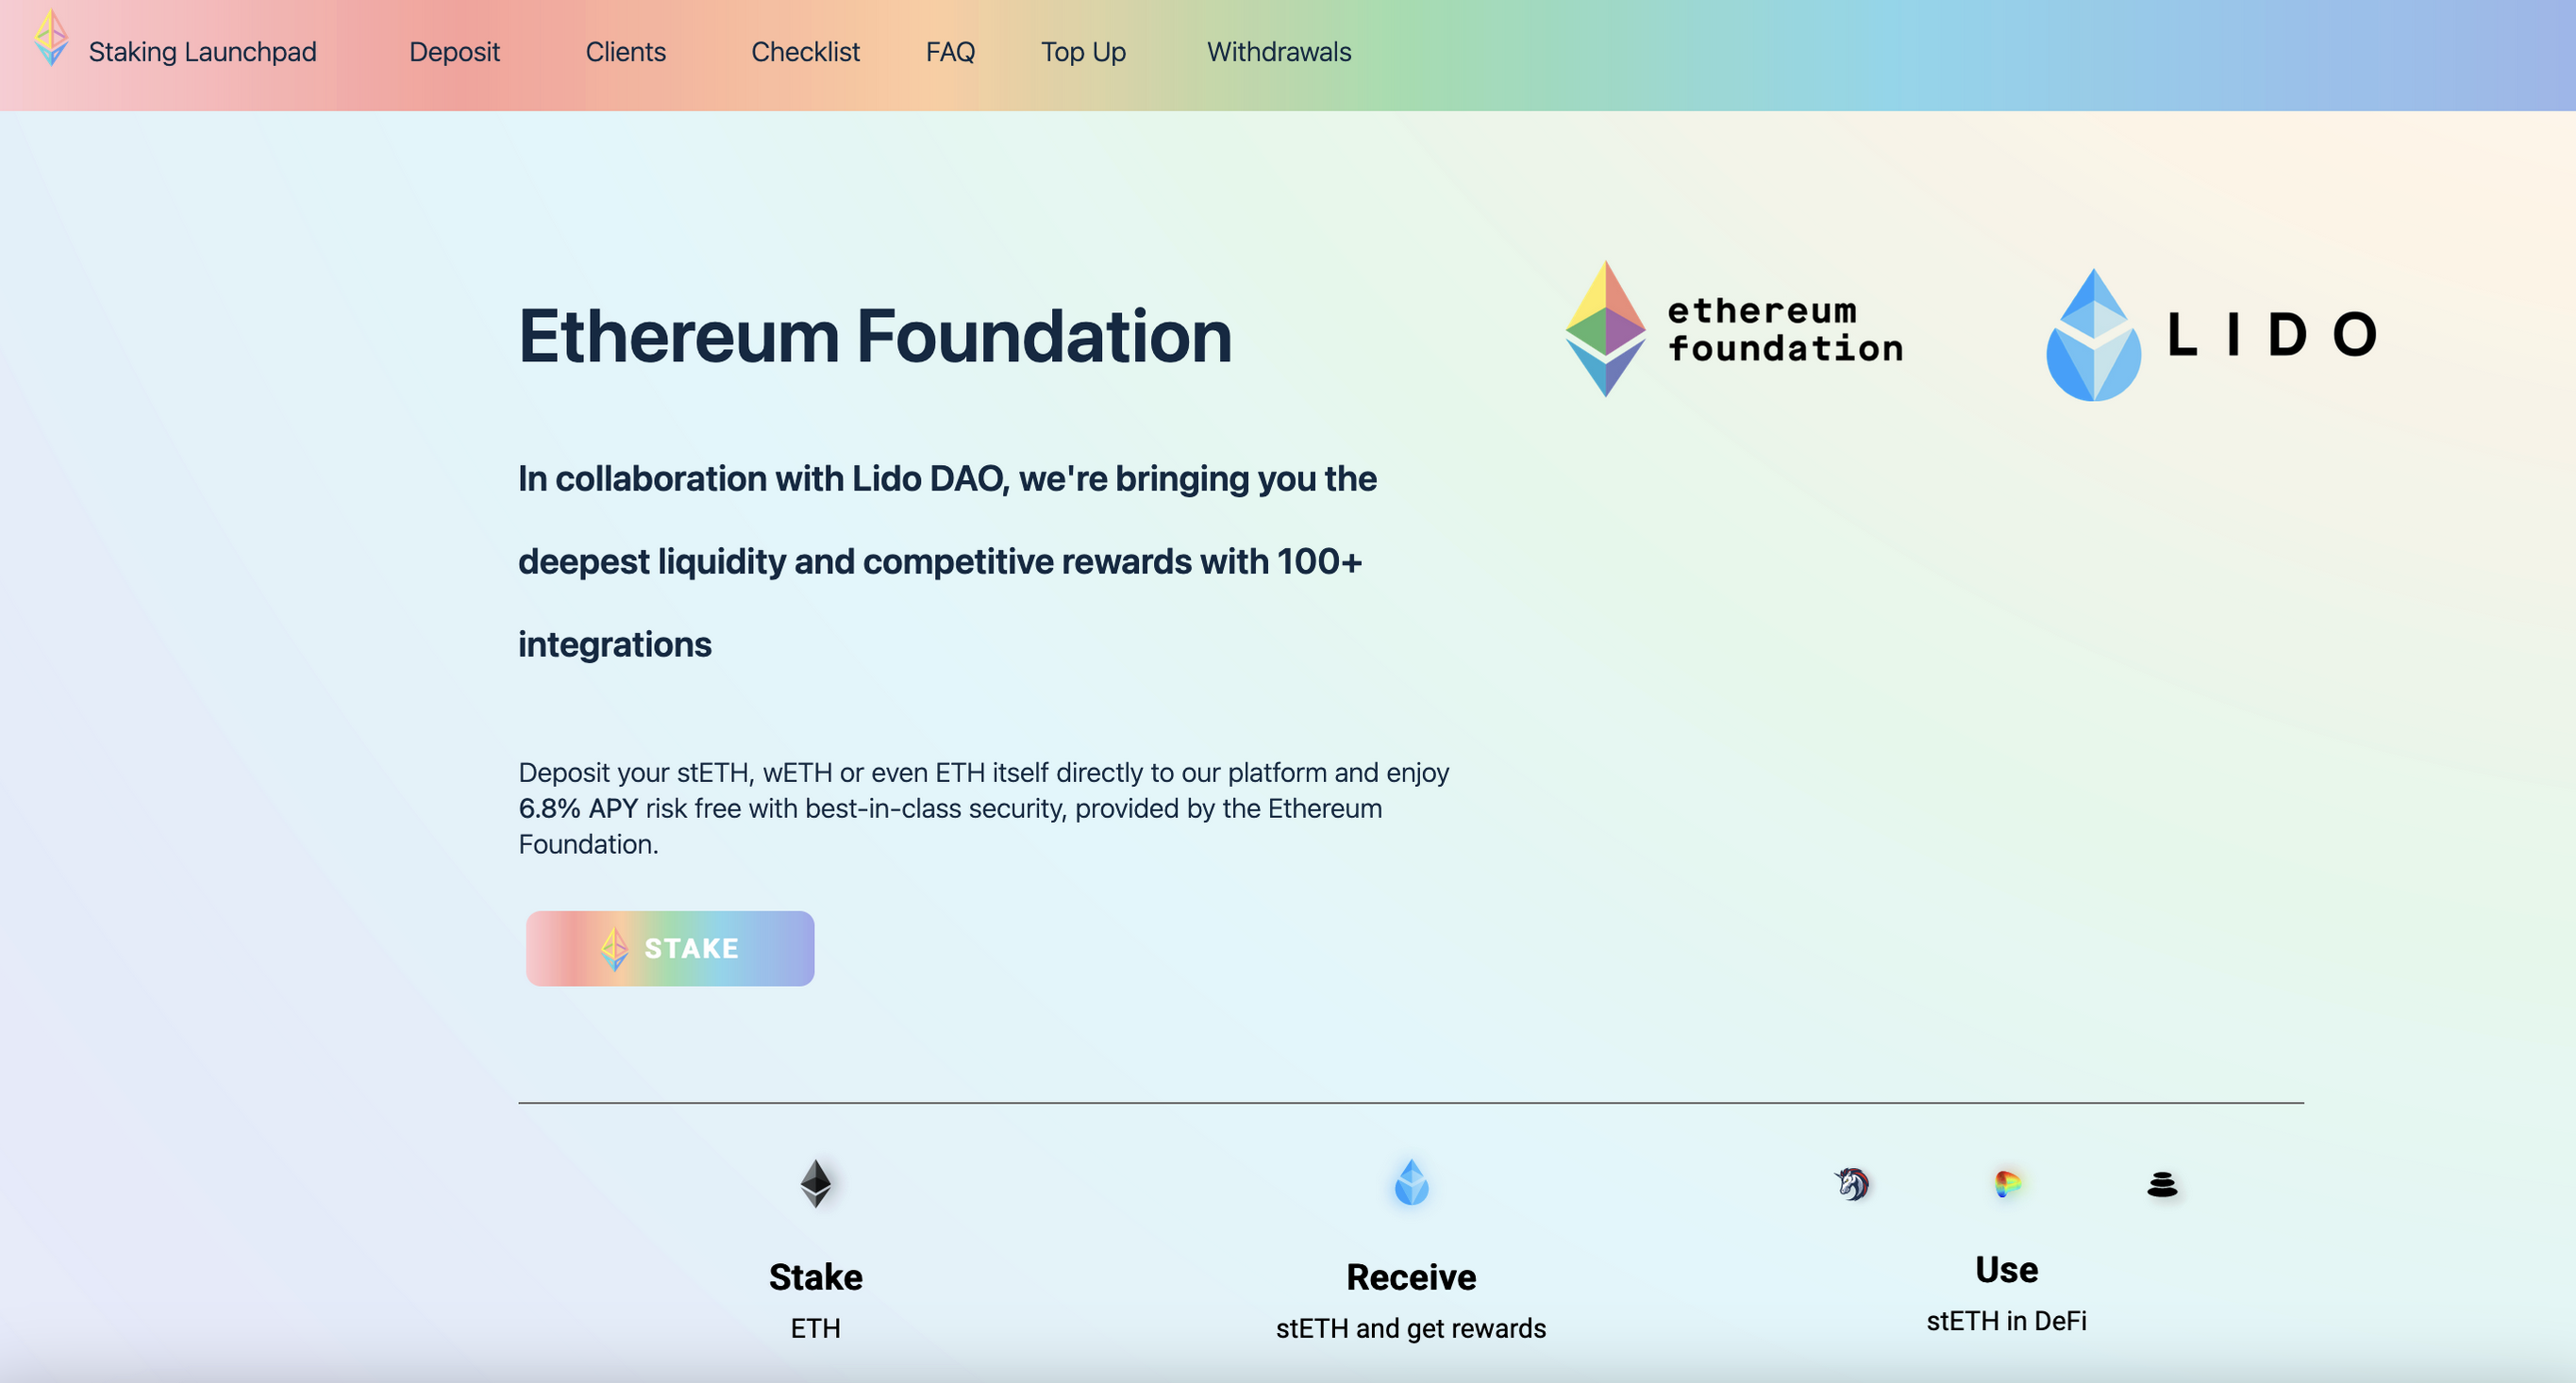
This website had a crypto drainer running in the background, and if a user initiated their wallet and signed the transaction requested by their website their wallet would have been drained.

Our internal security team immediately launched an investigation to help determine who launched the attack, what the aim of the attack was, when it happened, who was affected, and how it happened.

Some of the intial actions taken were:

  • Prevented the threat actor from sending additional emails.
  • Sent out notifications via twitter and email to not click the link in question.
  • Closed down the malicious access path the threat actor had used to obtain access into the mailing list provider.
  • Submitted the malicious link to various blacklists, and it was then blocked by majority of web3 wallet providers and cloudflare.

Our investigation into the attack showed that:

  • The threat actor imported a large email list of their own into the mailing list platform to be used for the phishing campaign.
  • The threat actor exported the blog mailing list email addresses, which was a total of 3759 email addresses.
  • When we compared the emails in the email list that the threat actor had imported, we could see that the blog mailing list contained 81 email addresses that the threat actor did not previously have knowledge of, and the rest were duplicate addresses.
  • Analyzing on-chain transactions made to the threat actor between the time they sent out the email campaign and the time the malicious domain got blocked, appear to show that no victims lost funds during this specific campaign sent by the threat actor.

As we continue working on this incident, we have taken additional measures such as migrating some mail services to other providers, to further help reduce the risk of this happening again.

We are deeply sorry that this incident occurred, and are working diligently with both our internal security team as well as external security teams to further help address and investigate this incident.

Any questions can be directed to security@ethereum.org.