





Last updated on October 16, 2025
Version 5.0.0 adds three major features for MSPs.
RDP brute-force attacks remain a top breach vector, so we built a new module that monitors and filters Remote Desktop connections.
Remote Access Protection is part of the Heimdal Firewall suite and watches every inbound RDP attempt.
By default, it blocks everything except allowlisted IP addresses.
You can add trusted IPs through the dashboard, set expiration dates if needed, and review blocked attempts in real time.
If you’re using our Microsoft 365 User Security module, RAP can check user risk scores from Azure AD before allowing access.
High-risk users trigger an extra confirmation step before their IP gets allowlisted.
The goal is simple. Let your technicians in for legitimate maintenance, keep everyone else out.
Every connection attempt gets logged so you know who tried to access which endpoint and when.
We overhauled our ransomware detection engine.
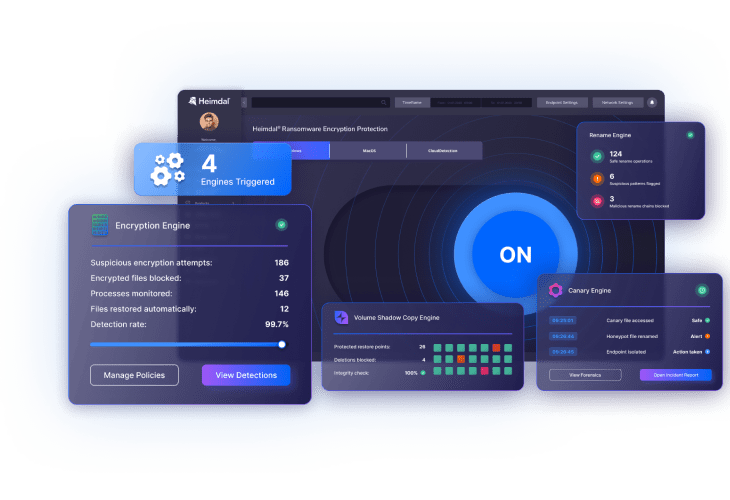
The new version (REP X or REP v2) runs at the kernel level using a new mini-filter driver and can identify and stop more than 800 ransomware variants.
It uses four different detection methods:
Encryption Engine – Monitors file encryption operations system-wide and flags unauthorized encryption attempts.
Rename Engine – Detects suspicious mass file rename activity and intercepts those changes before they propagate.
Volume Shadow Copy Engine – Guards backup restore points by blocking any attempt to delete Volume Shadow Copies.
Canary Engine – Plants decoy files in sensitive directories as tripwires. Any attempt to modify or encrypt these decoys triggers an immediate alert and defensive response.
These four engines work together. REP X is enabled by default for all new group policies and runs alongside our existing ransomware protection. You can toggle it per policy if needed.
This gives your clients stronger ransomware defense with minimal effort and no added complexity.
We completely revamped the Network OS Deployment module and now power it with iPXE.
This eliminates previous roadblocks (including Microsoft-imposed PXE limitations), so deploying Windows 11 over the network is now fully supported.
You can upload and organize ISO images in one central repository through the Heimdal dashboard. Promoting an endpoint to act as a PXE boot server now takes just a few clicks.
No more complex WDS setups.
There’s a new Reseller Repository Inheritance feature that lets MSPs share their library of OS images with all their customers automatically.
You maintain one master repository of installation images and your client organizations can pull from it, saving time and storage across the board.
Any device can network-boot via the Heimdal iPXE server and receive a fresh Windows installation.
You can remotely roll out or re-image machines across different sites without sending technicians on-site or juggling USB sticks.
Heimdal 5.0.0 RC is available now. Contact us for a demo or to learn more about the update.

Head of Content at Heimdal. A journalist by trade who cares about helping MSPs and security teams make better decisions, enjoy their work, and see real results.
CHECK OUR SUITE OF 11 CYBERSECURITY SOLUTIONS
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。